PipeViewer
 cyberark/pipeviewer
A tool that shows detailed information about named pipes in Windows
container-escapeprivilege-escalationvulnerability-analysis
cyberark/pipeviewerA tool that shows detailed information about named pipes in Windows
 ihsansencan/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182

 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
 veritas501/pipe-primitive
An exploit primitive in linux kernel inspired by DirtyPipe
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up
 bgeesaman/subpath-exploit
Writeup of CVE-2017-1002101 with sample "exploit"/escape
 chenaotian/cve-2022-0492
Detailed technical analysis and working exploit for CVE-2022-0492 Linux kernel container escape via cgroup release_agent, with step-by-step lab setup…
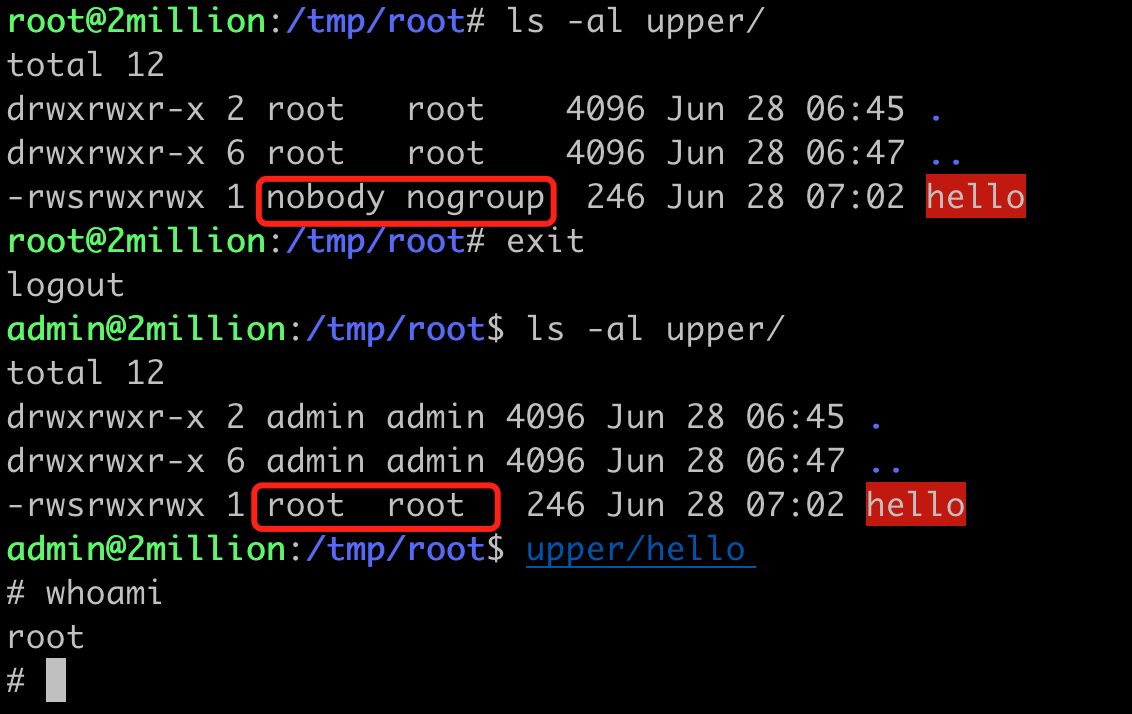 fanxiaoyao66/cve-2023-0386
非常简单的CVE-2023-0386's exp and analysis.Use c and sh.
 ricterz/pie-stack-clash-cve-2017-1000253
Demo-ing CVE-2017-1000253 in a container


 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
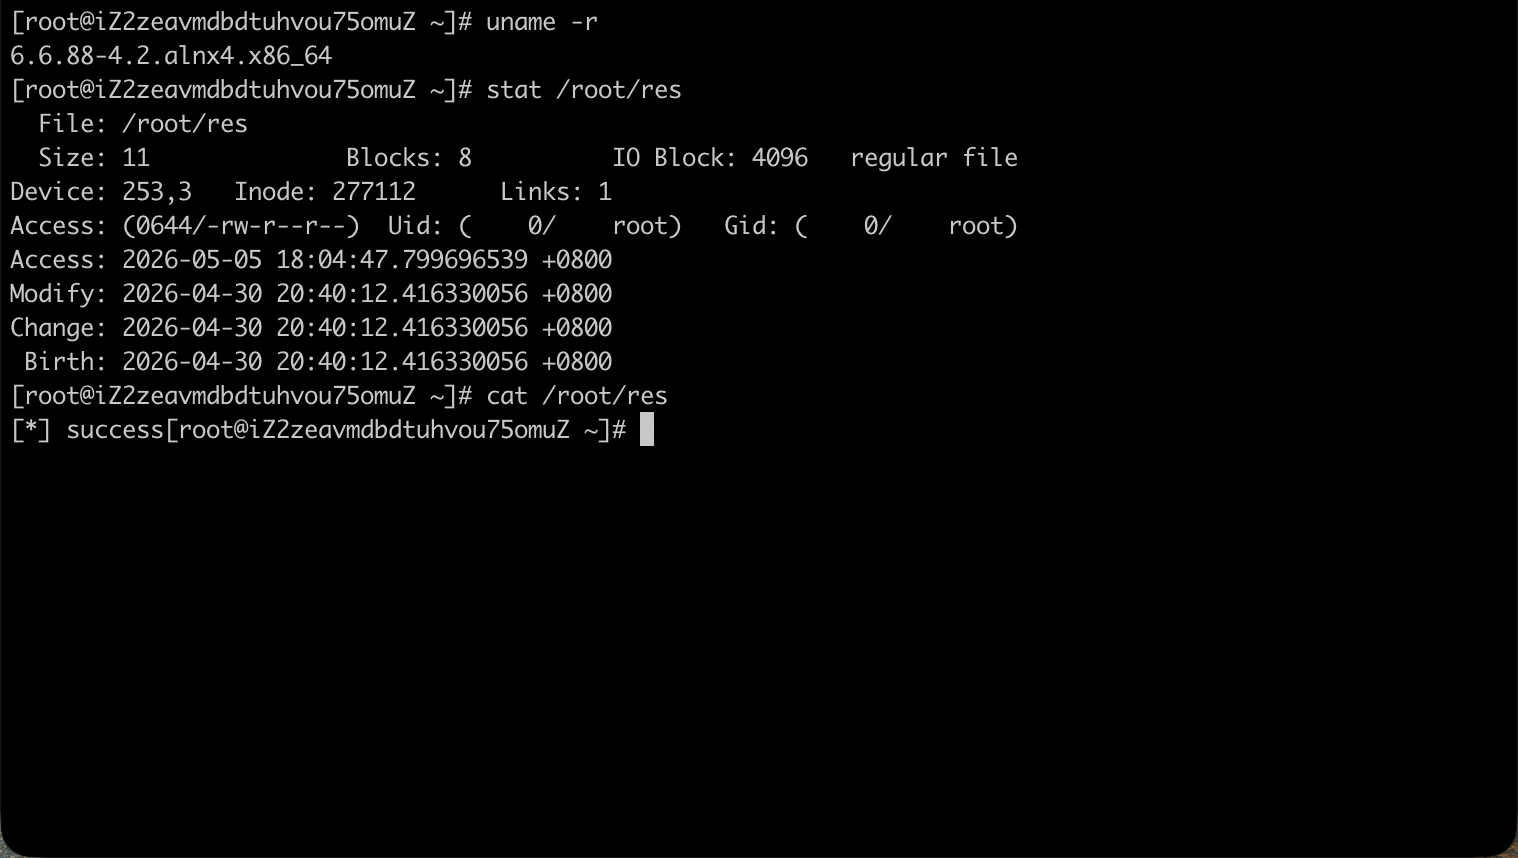
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.