Copy-Fail-CVE-2026-31431-Kubernetes-PoC

PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…

PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…

Proof-of-concept demonstrating container escape on Kubernetes via CVE-2026-31431 kernel page-cache corruption, achieving node-level code execution…

PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…

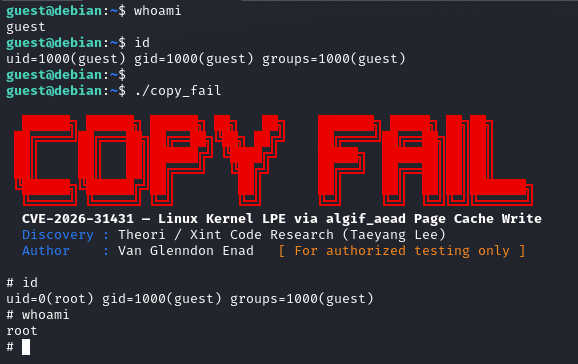
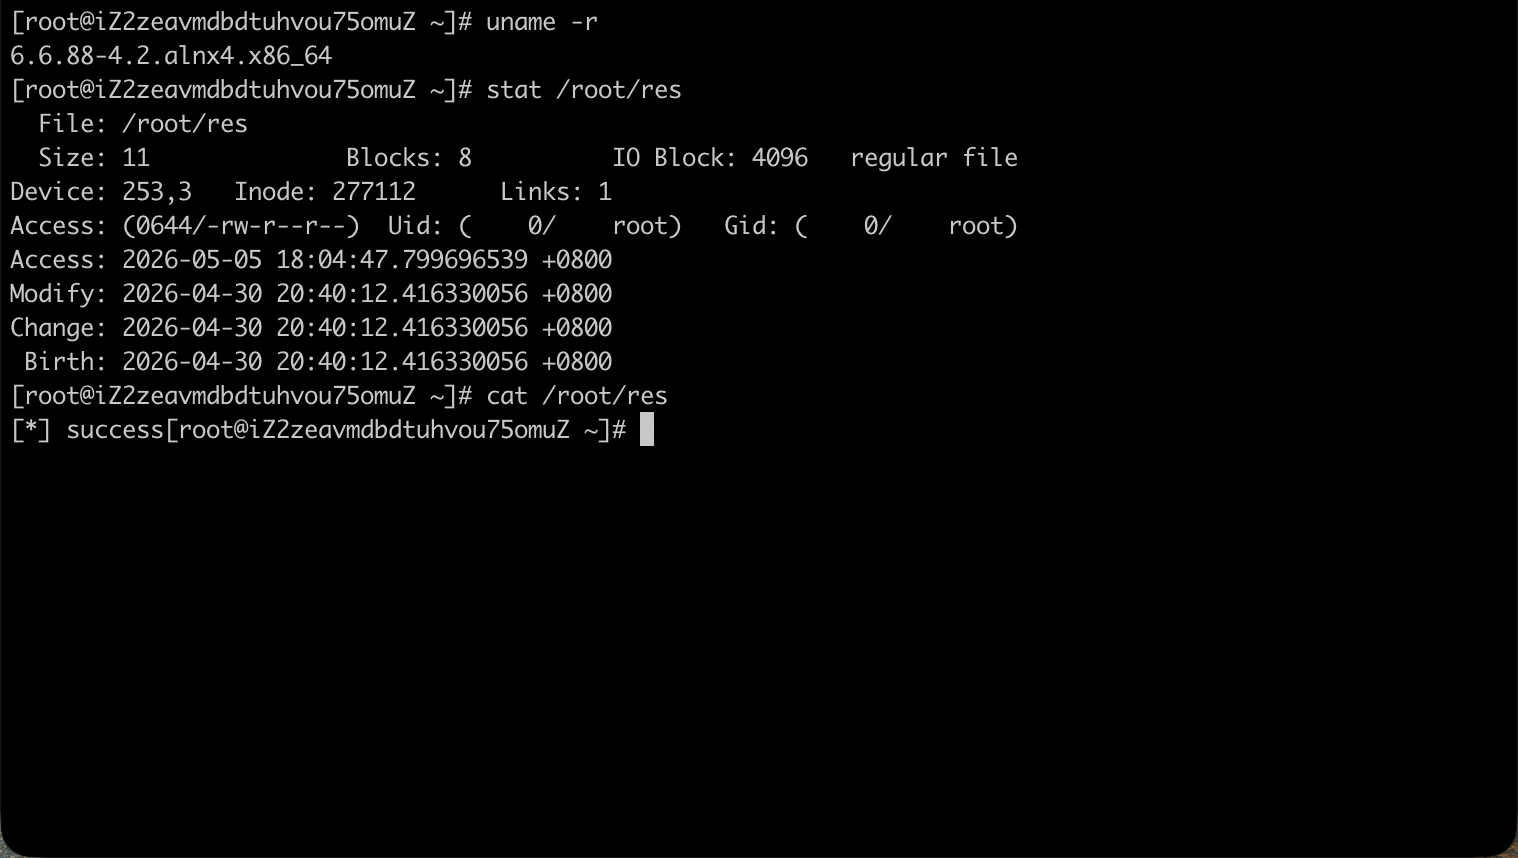
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.

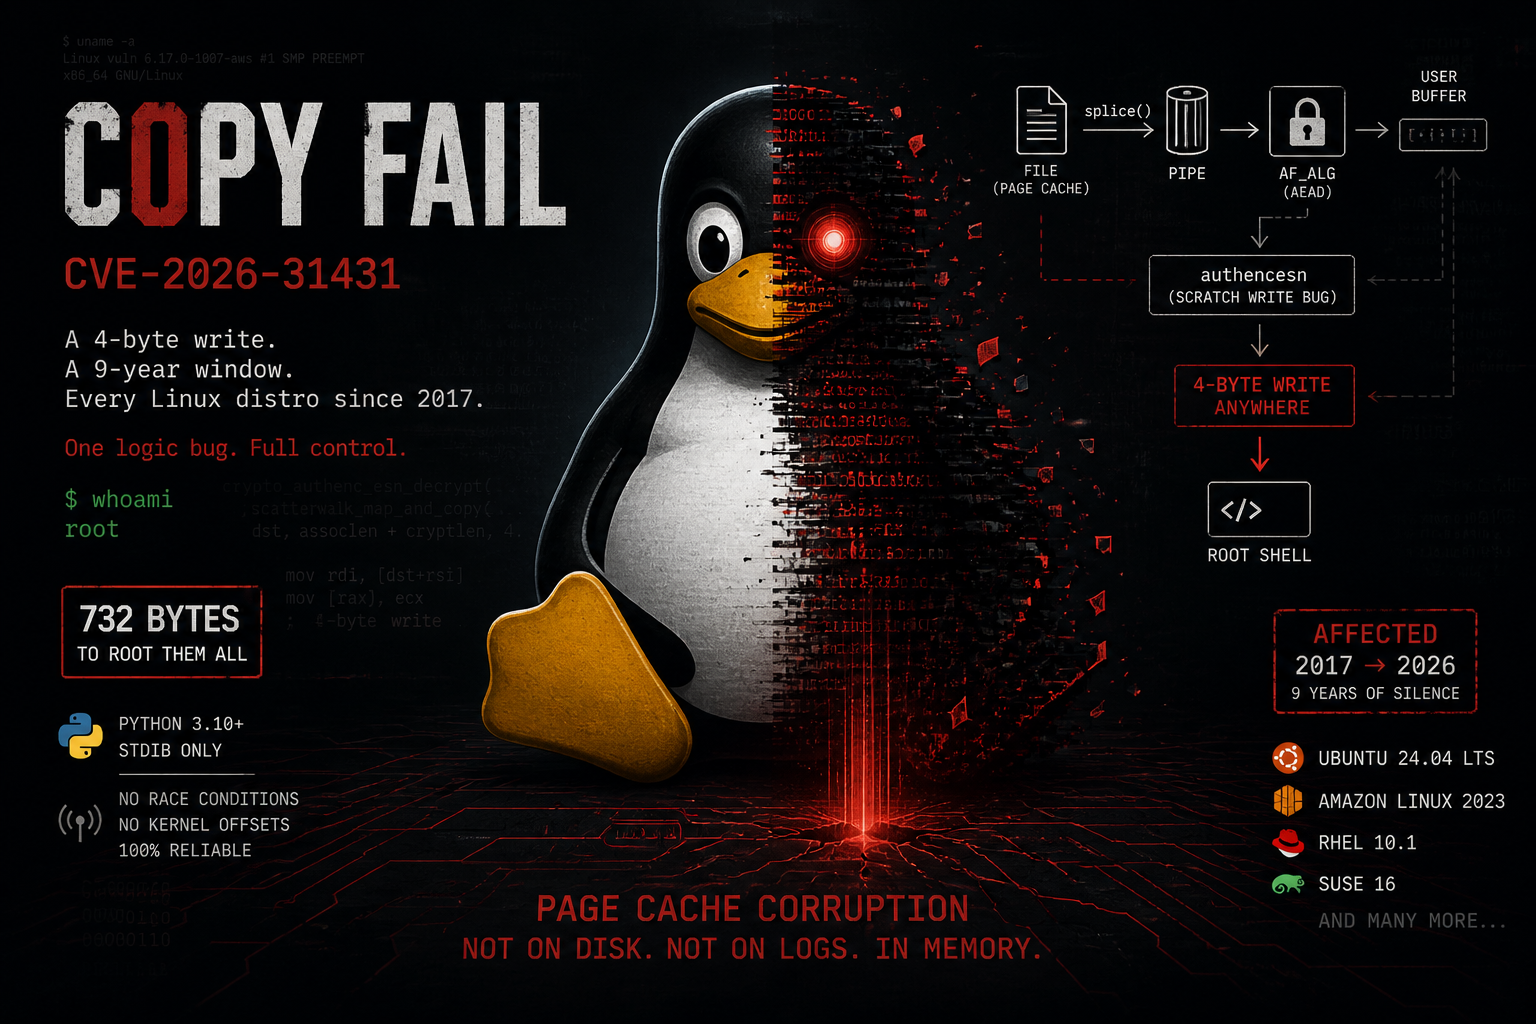
A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…

Proof of Concept of an unsafe pickle deserialization vulnerability in Socket.IO

Exploit the dirtycow vulnerability to login as root

A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…

Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…

POE code for CVE-2017-1000112 adapted to both funtion on a specific VM and Escape a Docker

Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…

Proof-of-concept exploit for CVE-2019-5736, a runc container escape that overwrites the host runc binary to achieve root code execution on the host.

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.

A Linux Host-based Intrusion Detection System based on eBPF.

Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…

Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.