

botb
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
cloud-securitycontainer-escapecontainer-security+4
brompwnie/botbA container analysis and exploitation tool for pentesters and engineers.
 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 swsmith2391/cve-2024-29510
POC code for CVE-2024-29510 and demo VulnApp
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 crusaders-of-rust/cve-2022-0185
CVE-2022-0185
 impalabs/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
 sgkdev/page_inject
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
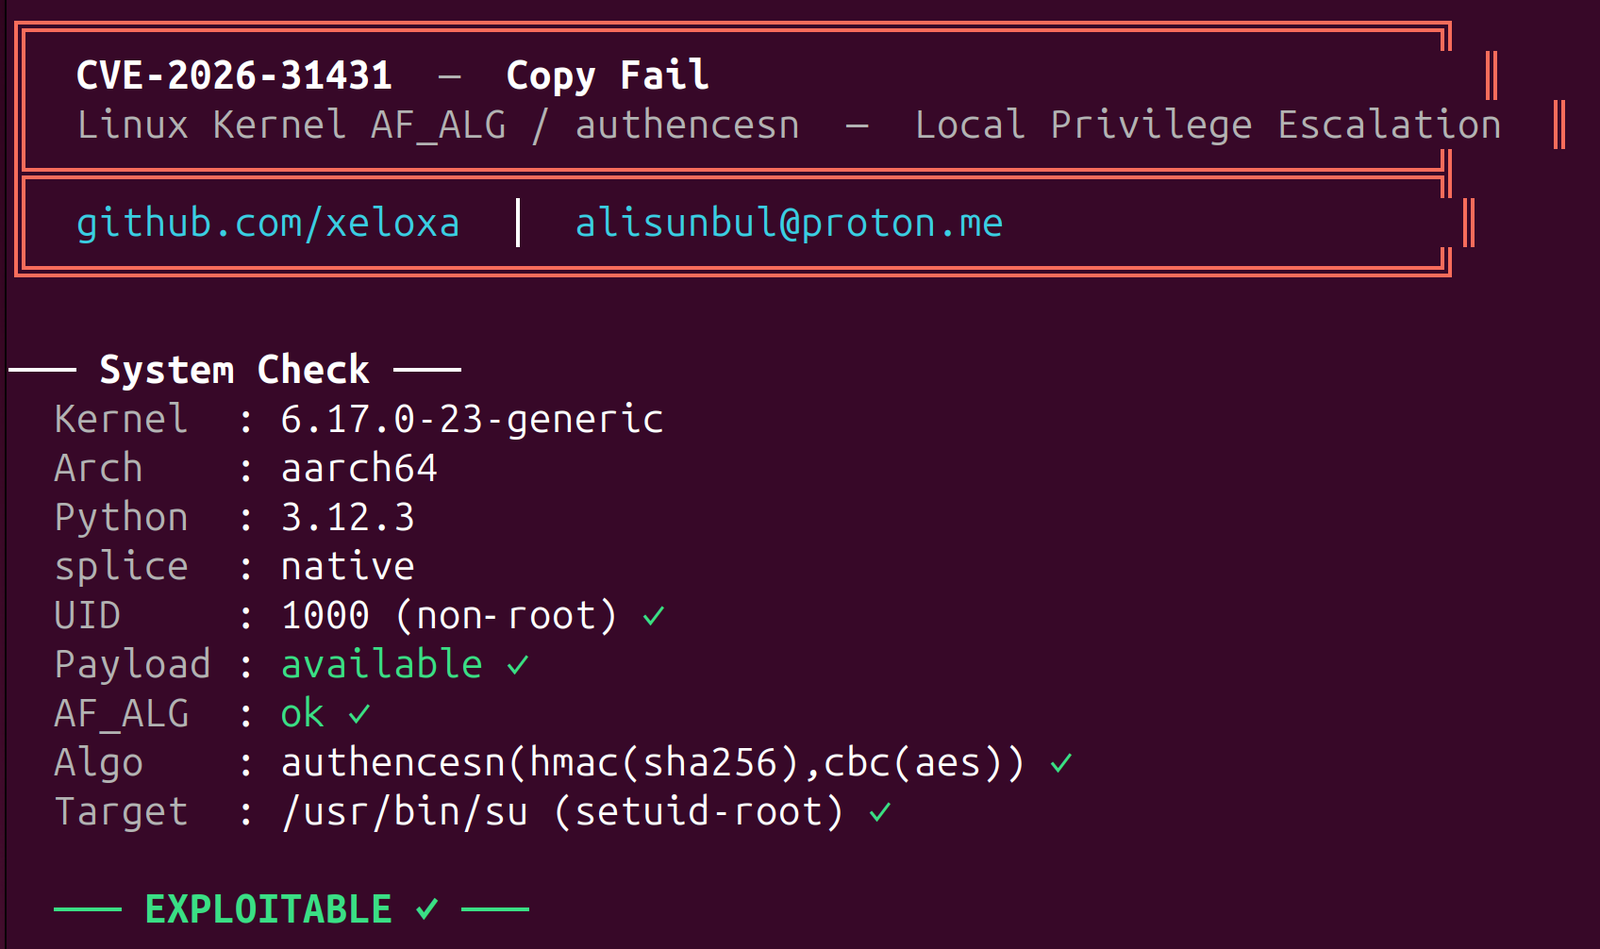 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 bridgeralderson/cve-2025-9074-poc
A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…
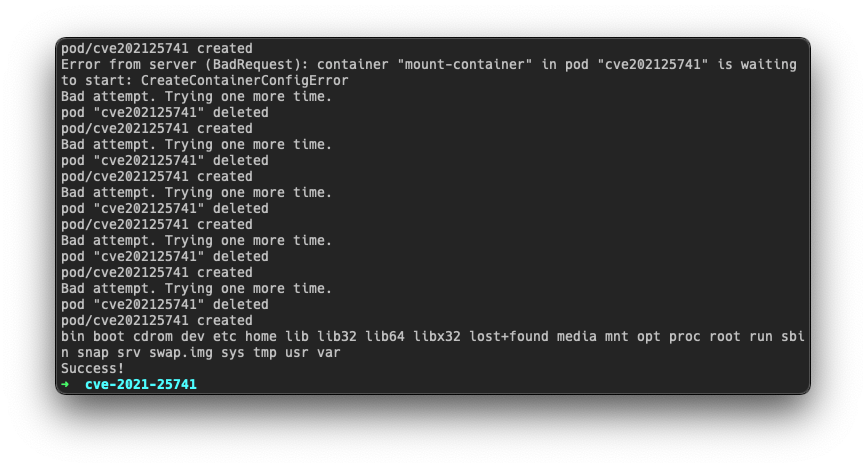 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 greyorder/cve-2021-21978
CVE-2021-21978 exp
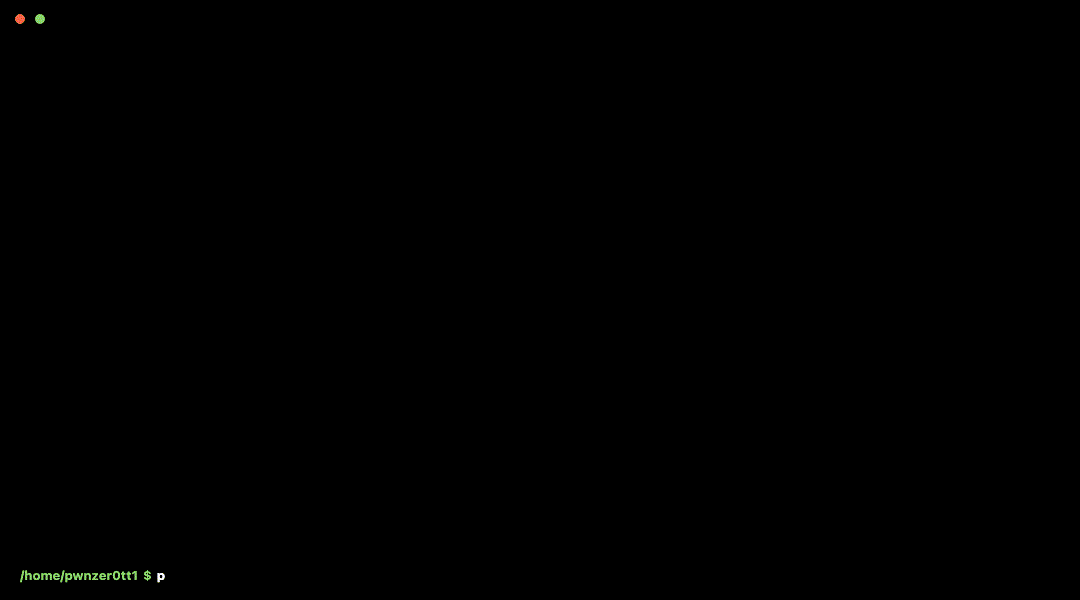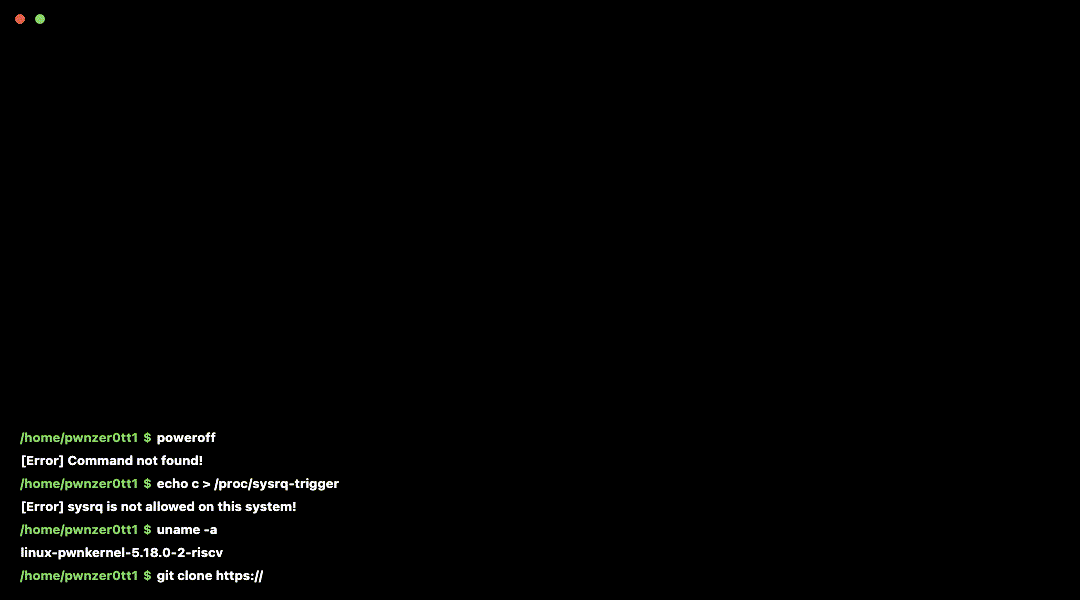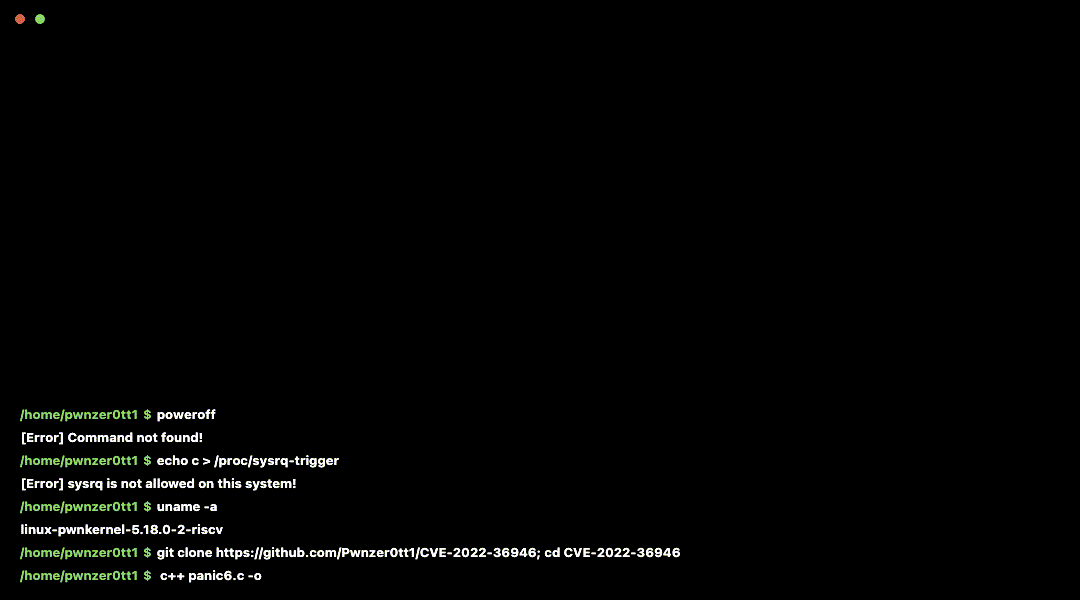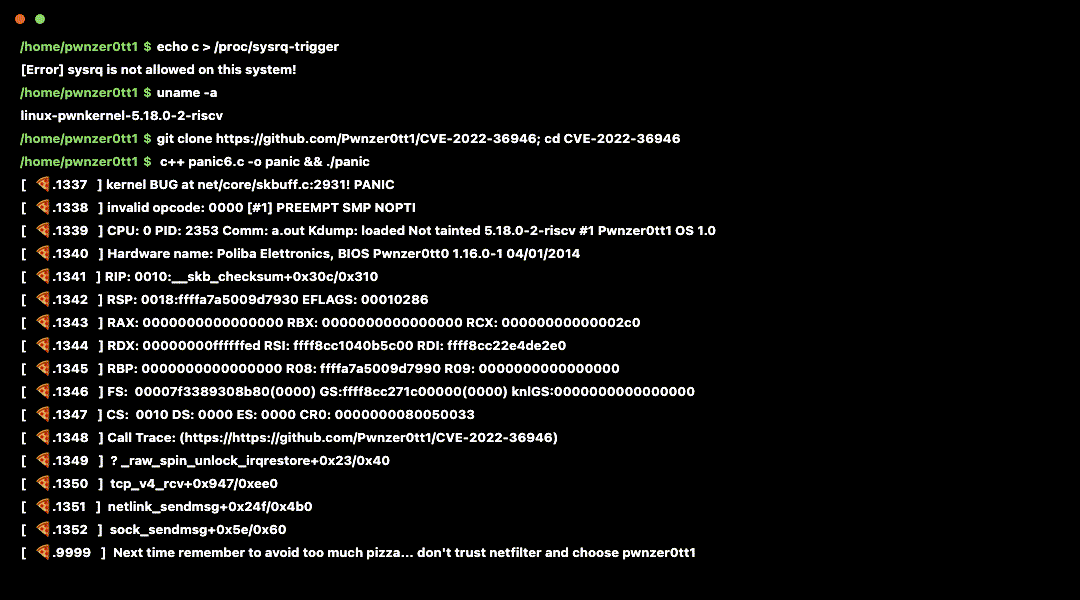 pwnzer0tt1/cve-2022-36946
CVE-2022-36946 linux kernel panic in netfilter_queue