

CVE-2017-1000112-Adpated
 ol0273st-s/cve-2017-1000112-adpated
POE code for CVE-2017-1000112 adapted to both funtion on a specific VM and Escape a Docker
binary-exploitationcontainer-escapeexploitation+2
1
ol0273st-s/cve-2017-1000112-adpatedPOE code for CVE-2017-1000112 adapted to both funtion on a specific VM and Escape a Docker
 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
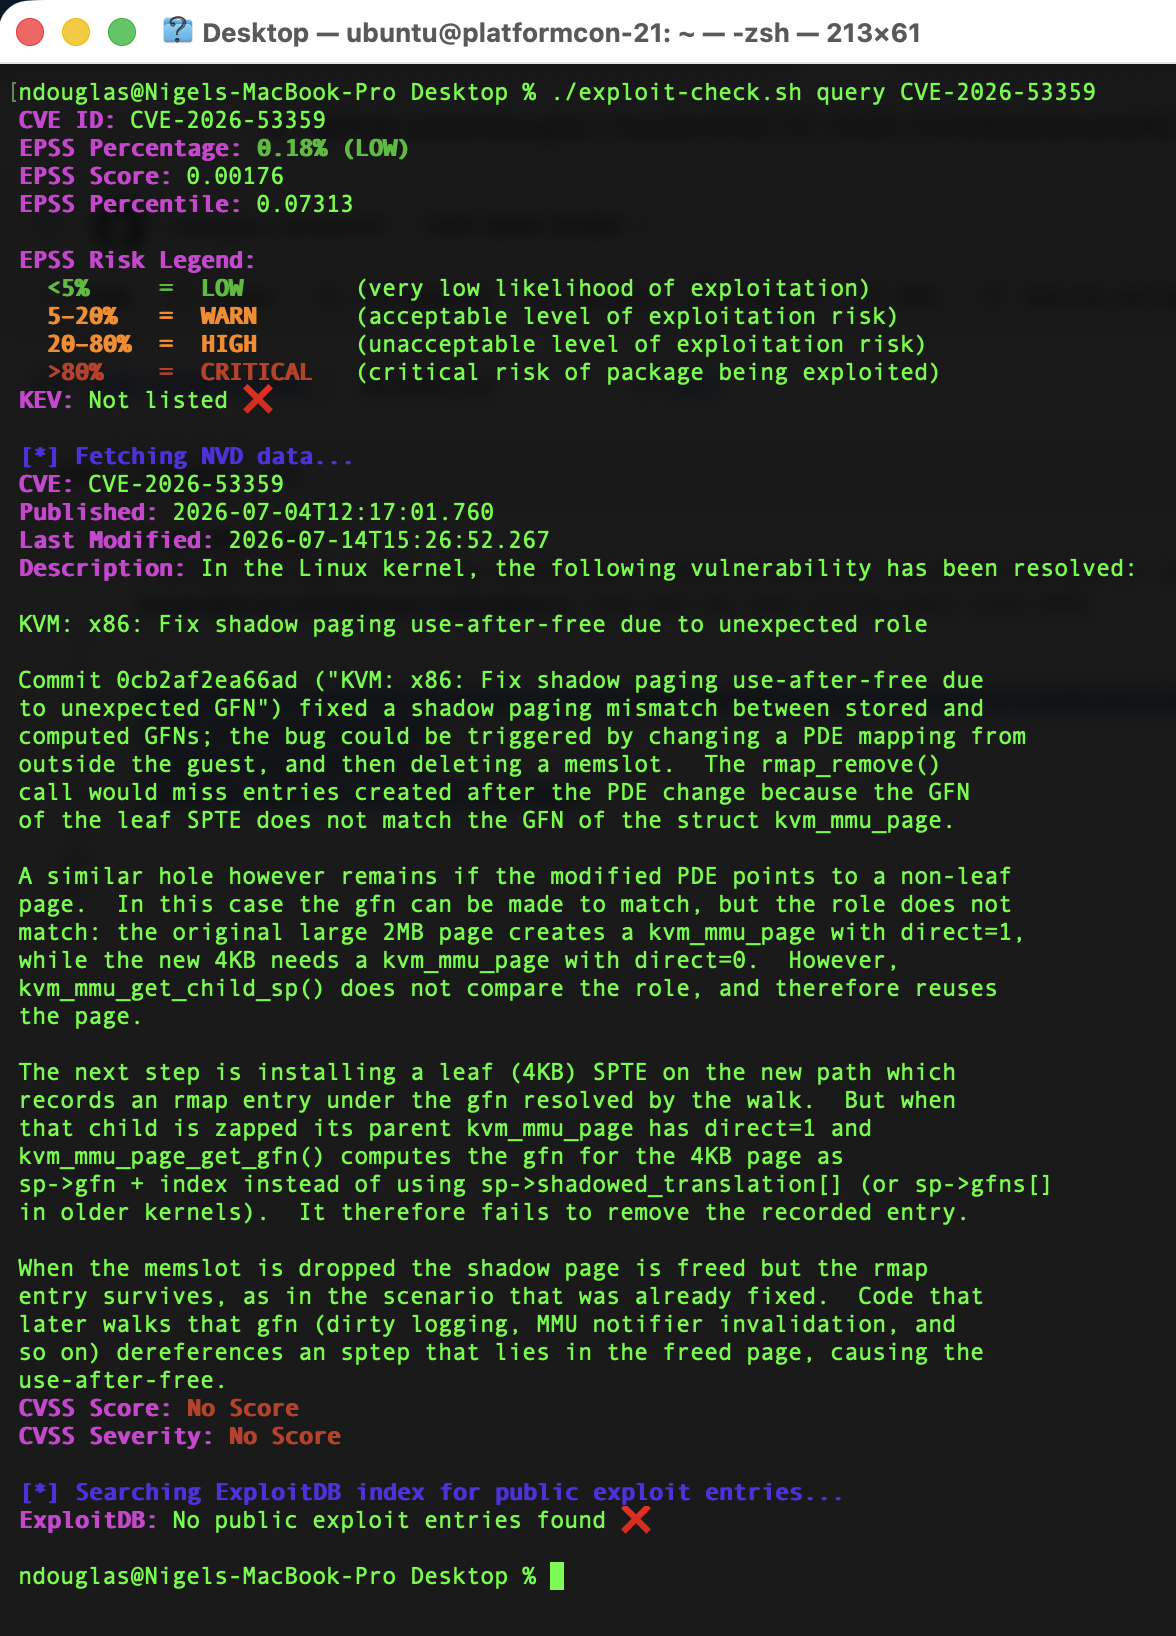 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 teawater/cve-2017-5123
Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 zaydbf/cve-2025-9074-poc
Bash-based PoC exploit for CVE-2025-9074 targeting unauthenticated Docker Engine API to achieve container escape and remote code execution via…
 billith/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, a runc container escape that overwrites the host runc binary to achieve root code execution on the host.
 starscow/copy-fail-cve-2026-31431-kubernetes-poc
Proof-of-concept demonstrating container escape on Kubernetes via CVE-2026-31431 kernel page-cache corruption, achieving node-level code execution…
 megadimenex/megahidocker
This project is exploit for some docker containers with similar to vulnerability code: CVE-2020-35191
 locus-x64/cve-2025-61765_poc
Proof of Concept of an unsafe pickle deserialization vulnerability in Socket.IO
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC
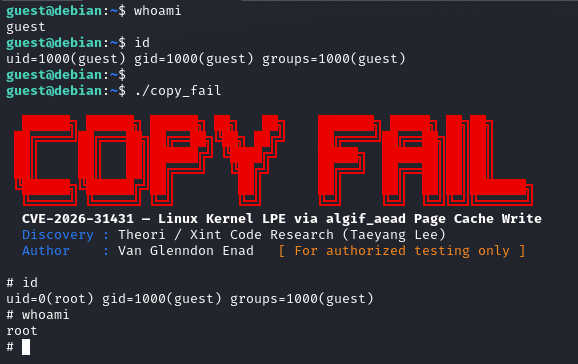 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 epsteina16/docker-escape-miner
Code sample for using exploit CVE-2019-5736 to mine bitcoin with no association to original container or user.
 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 pucagit/cve-2025-9074
PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.