
pipe-primitive
 veritas501/pipe-primitive
An exploit primitive in linux kernel inspired by DirtyPipe
binary-exploitationcontainer-escapeeducation+3
1034 years ago
veritas501/pipe-primitiveAn exploit primitive in linux kernel inspired by DirtyPipe
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 chenaotian/cve-2022-0492
Detailed technical analysis and working exploit for CVE-2022-0492 Linux kernel container escape via cgroup release_agent, with step-by-step lab setup…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 0xfuffm3/cve-2026-31431-copyfail
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…
 krish-foren6/cve-2026-31431-report-copy-fail-vulnerability-
Detailed analysis of the Copy Fail vulnerability (CVE-2026-31431) in the Linux kernel, including memory corruption mechanism, privilege escalation…
 vrtlbob/linux-kernel-vulnerabilities-cve-2026-23111
High Severity LPE vulnerability in Linux Kernel, with a CVS score of 7.8. An inverted check from user enables a process inside the container to break…
 prabeershakya/cve-2022-0185-poc
Proof-of-concept exploit for CVE-2022-0185, a Linux kernel heap buffer overflow enabling local privilege escalation and container escape via FUSE and…
 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up

 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
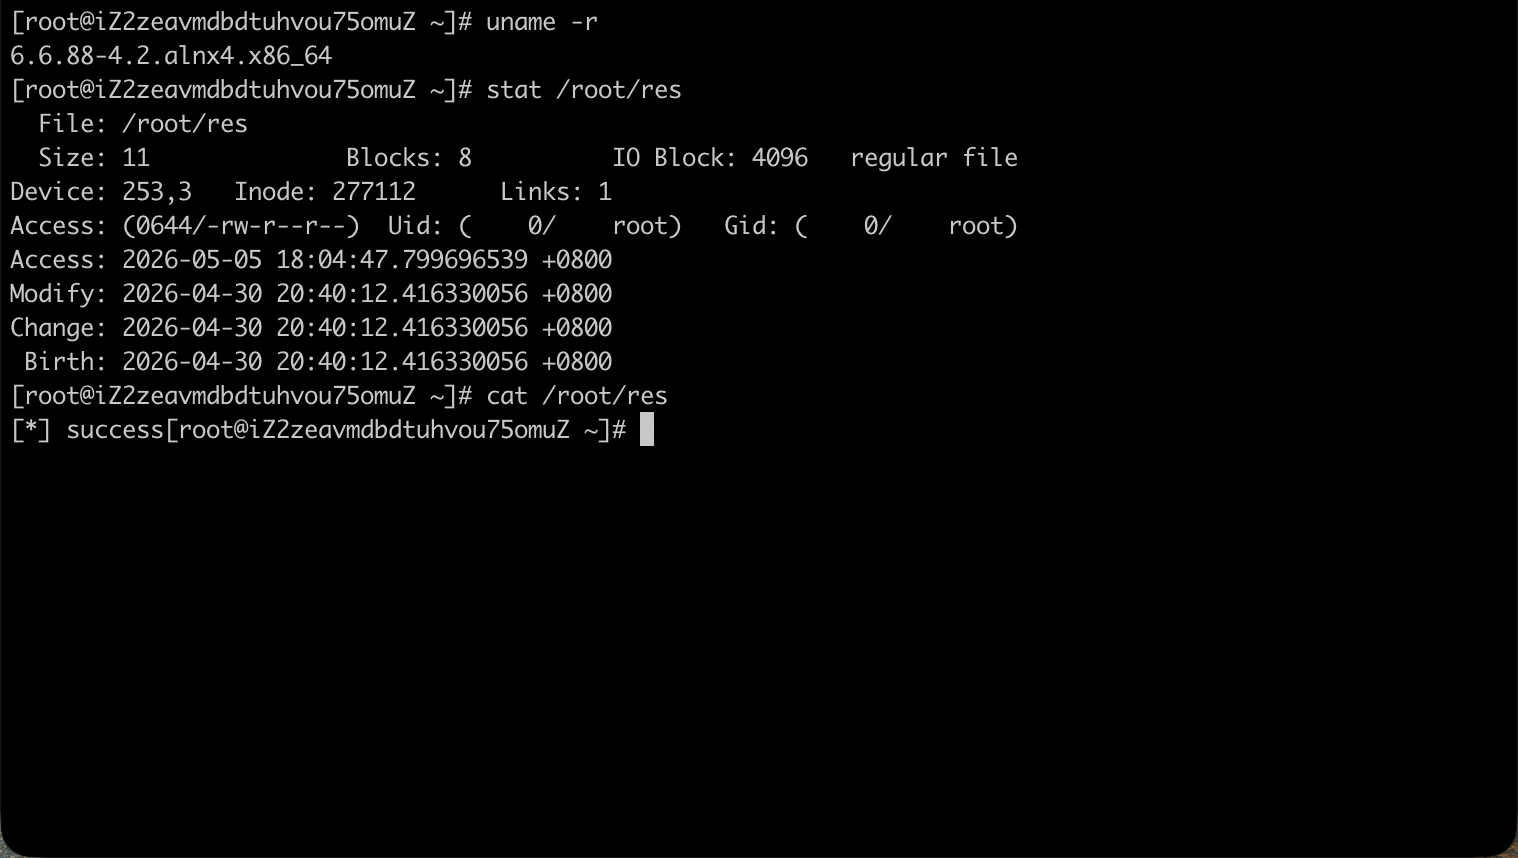 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
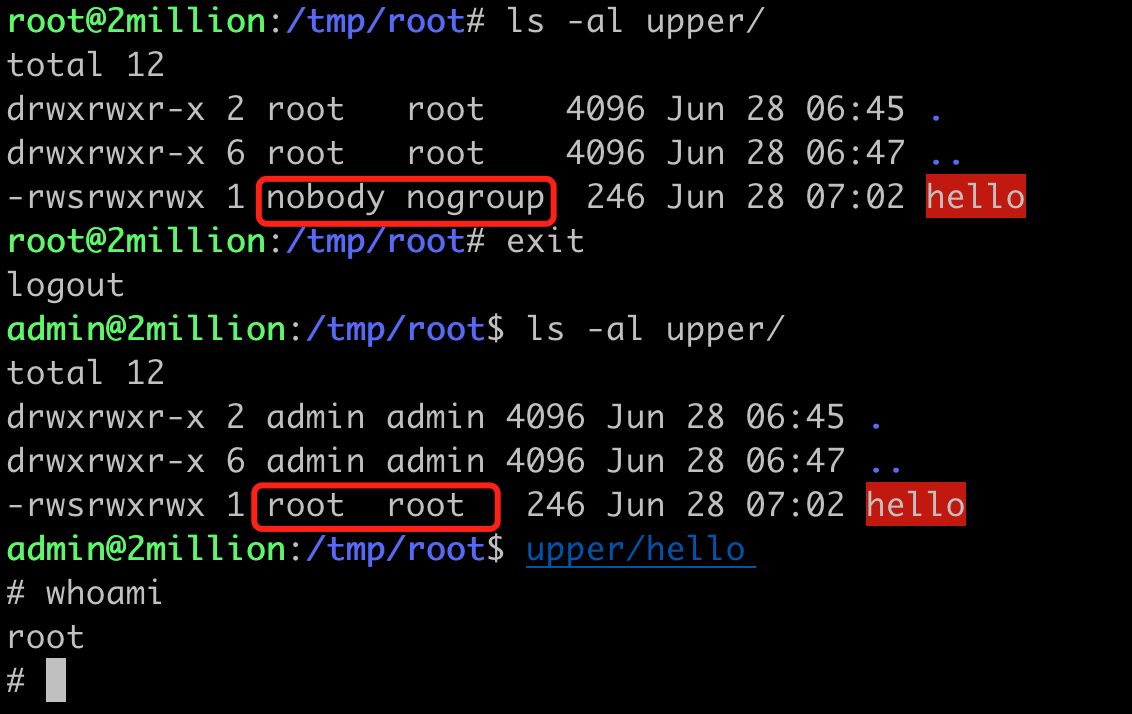 fanxiaoyao66/cve-2023-0386
非常简单的CVE-2023-0386's exp and analysis.Use c and sh.
 ricterz/pie-stack-clash-cve-2017-1000253
Demo-ing CVE-2017-1000253 in a container

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 christbowel/cve-2026-41900-poc
Proof-of-concept exploit for CVE-2026-41900, an unauthenticated remote code execution in OpenLearnX via container volume mount, enabling /tmp…