


 ricterz/pie-stack-clash-cve-2017-1000253
Demo-ing CVE-2017-1000253 in a container
 shaoshi17/cve-2025-9074-docker-exploit
一个功能强大的 Docker 远程 API 漏洞利用工具,用于 CVE-2025-9074 漏洞的安全研究和测试。
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 r0binak/cve-2024-0132
CVE-2024-0132 – Fully Weaponized NVIDIA Container Toolkit Exploit
 cdxiaodong/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626 runc container breakout via leaked file descriptors and process.cwd manipulation, enabling host…
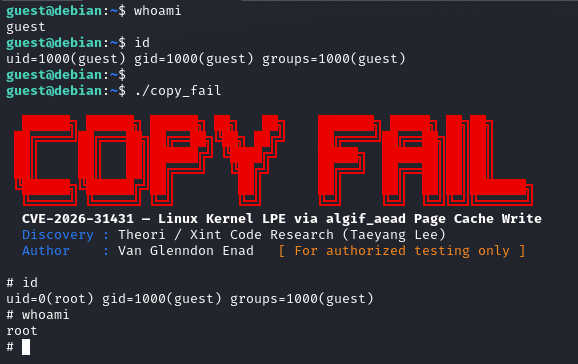 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 kianabin/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 yanxinwu946/cve-2026-46331
CVE-2026-46331 act_pedit page-cache corruption exploit, with Alpine PIE fix
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 666asd/cve-2024-23653
Proof-of-concept demonstrating CVE-2024-23653, a BuildKit container escape via a malicious Dockerfile frontend, using buildctl to inspect process…
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
 ssst0n3/kata-cve-2020-2023-poc
Proof-of-concept exploit for Kata Containers container escape (CVE-2020-2023) using mknod to modify guest filesystem and overwrite system binaries…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 alicey0719/docker-poc_cve-2024-1086
Dockerized proof-of-concept for CVE-2024-1086, a Linux kernel privilege escalation exploit that grants root access via a crafted binary.
 thekevinday/docker_lightman_exploit
Docker CVE-2022-37708