
CVE-2025-9074
 rocket-panda/cve-2025-9074
Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…
cloud-securitycontainer-escapeexploitation+3
rocket-panda/cve-2025-9074Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…
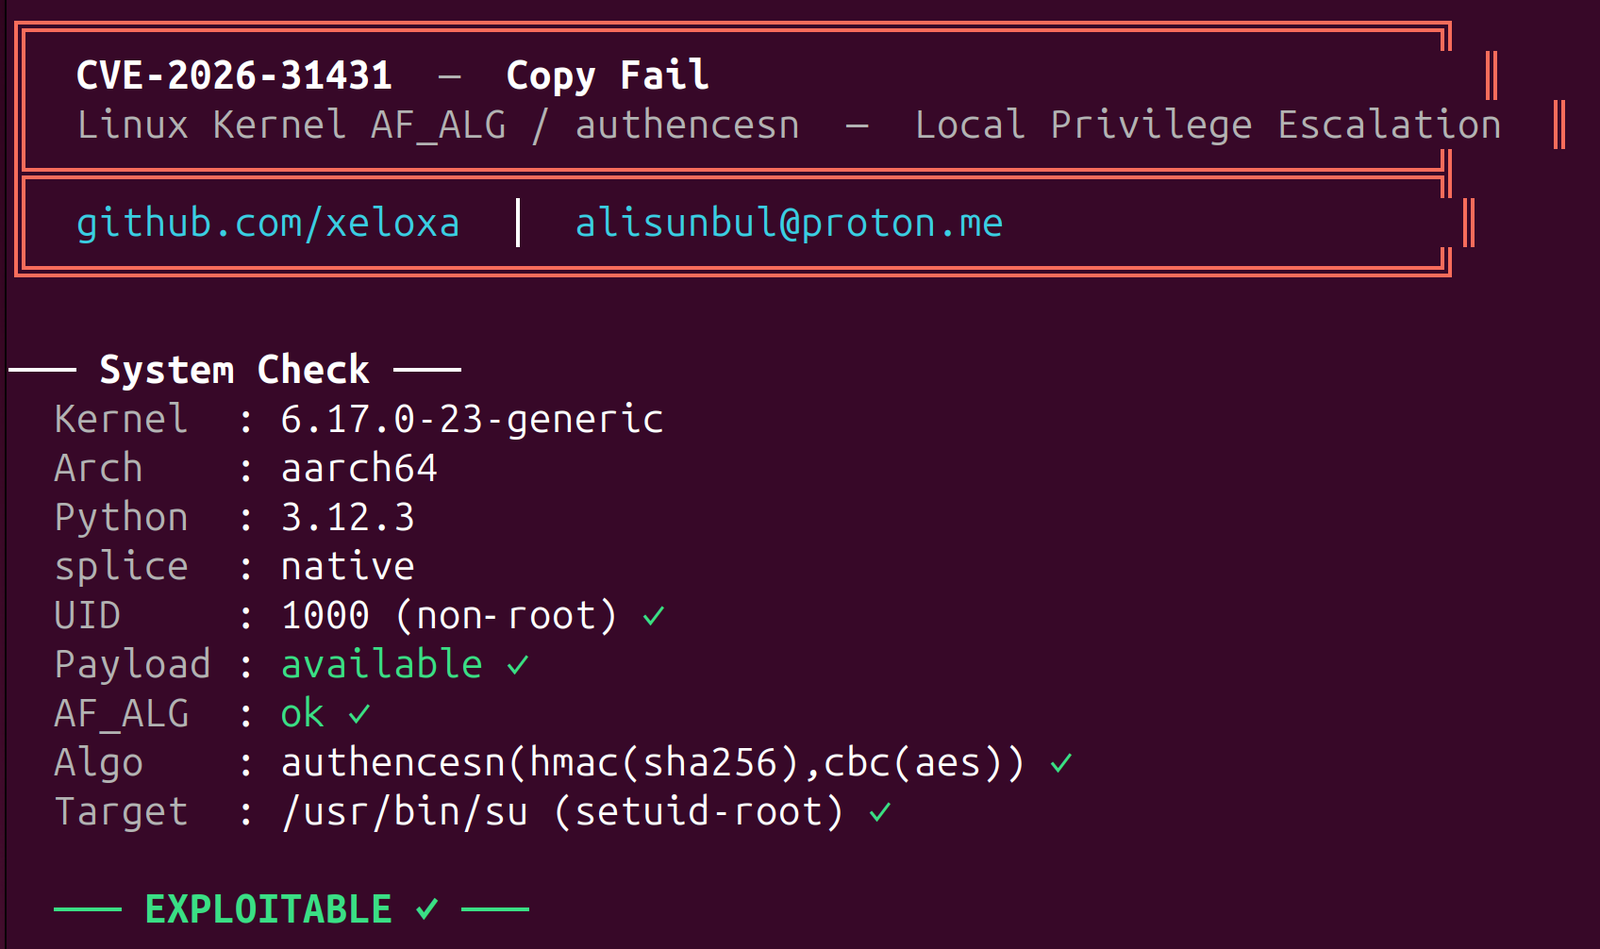 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 likekabin/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, appending a payload to the host runc binary via Docker container escape.
 bridgeralderson/cve-2025-9074-poc
A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…
 billith/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, a runc container escape that overwrites the host runc binary to achieve root code execution on the host.
 b3d3c/poc-cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, demonstrating the attack and enabling security testing.
 wenura17125/cve-2025-49131-poc
Proof-of-concept exploit for CVE-2025-49131, a sandbox escape in FastGPT allowing arbitrary file read/write, import bypass, and remote code execution…
 geropl/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runC that allows overwriting the host runC binary to gain root access…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 ssst0n3/kata-cve-2020-2023-poc
Proof-of-concept exploit for Kata Containers container escape (CVE-2020-2023) using mknod to modify guest filesystem and overwrite system binaries…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 epsteina16/docker-escape-miner
Code sample for using exploit CVE-2019-5736 to mine bitcoin with no association to original container or user.