

gvisor
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
cloud-infrastructure-securitycloud-securitycontainer-escape+4
19.8k
google/gvisorSandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 hackspeak/cve-2026-17106
PoC for Docker `docker cp` arbitrary file write, exploiting symlink and tar extraction flaws to overwrite host binaries or launch agents for…
 ssst0n3/kata-cve-2020-2023-poc
Proof-of-concept exploit for Kata Containers container escape (CVE-2020-2023) using mknod to modify guest filesystem and overwrite system binaries…
 berdav/cve-2026-41567
Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 george0papasotiriou/cve-2026-5555-container-escape-via-proc-self-fd-symlink-in-shared-volume
Proof-of-concept exploit for CVE-2026-5555, demonstrating container escape via /proc/self/fd symlink in rshared volumes to overwrite host files and…
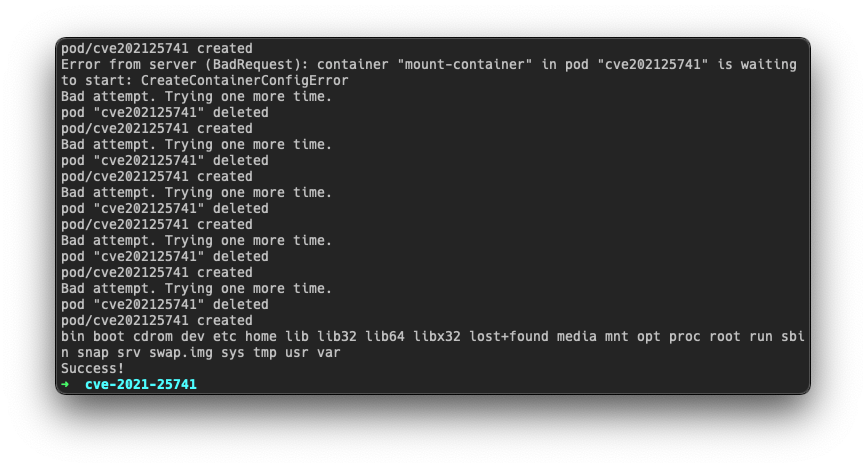 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 rocket-panda/cve-2025-9074
Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…
 cdxiaodong/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626 runc container breakout via leaked file descriptors and process.cwd manipulation, enabling host…
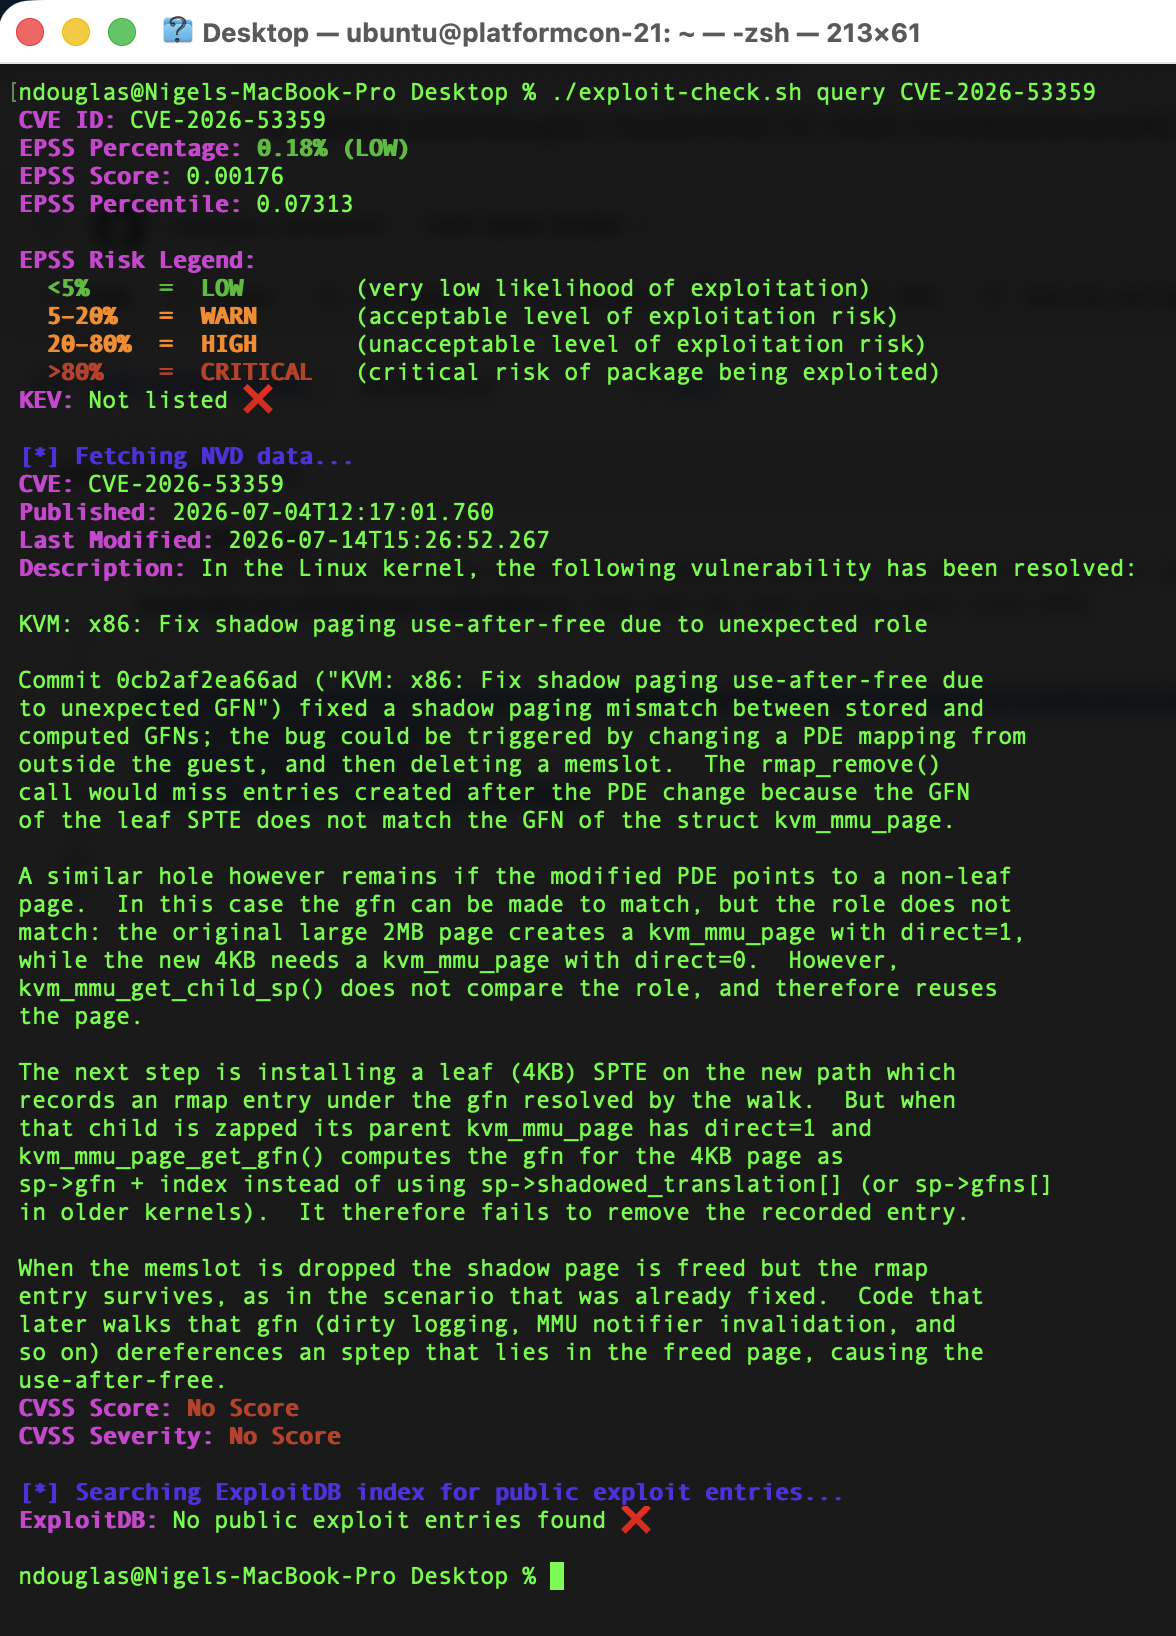 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 sastraadiwiguna-purpleeliteteaming/holistic-deconstruction-of-cve-2019-5736-
This repository provides a high-fidelity technical deconstruction and production-ready exploitation suite for CVE-2019-5736. It demonstrates how a…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 kinryulabs/rootpacket-cve-2026-31431
Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…
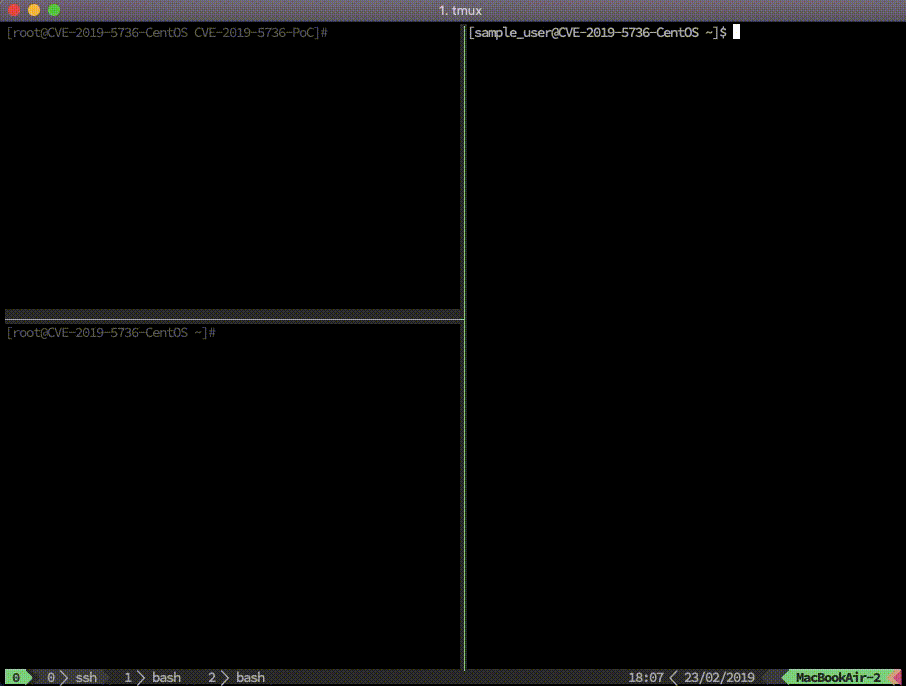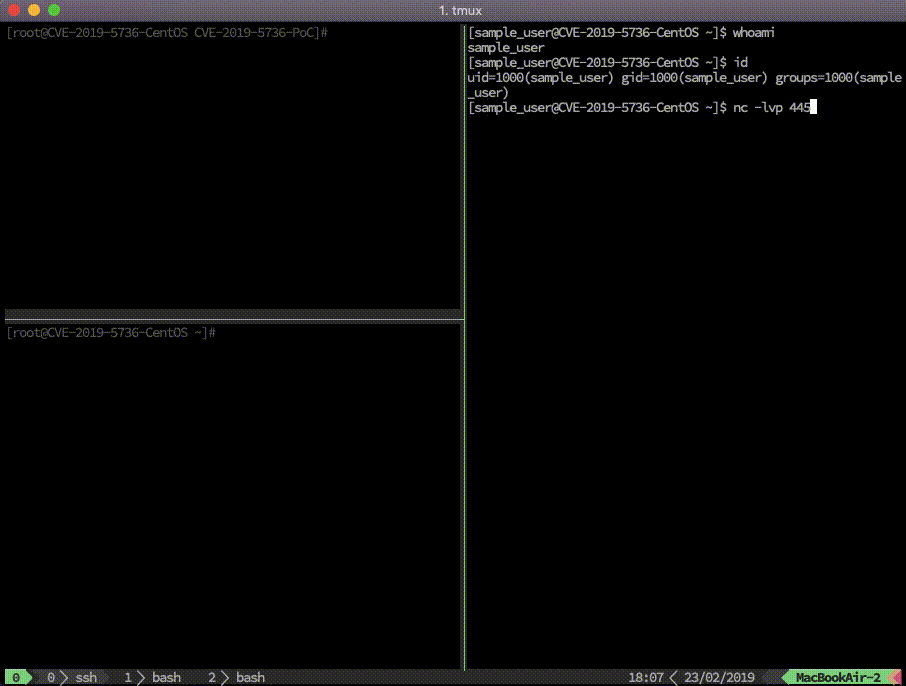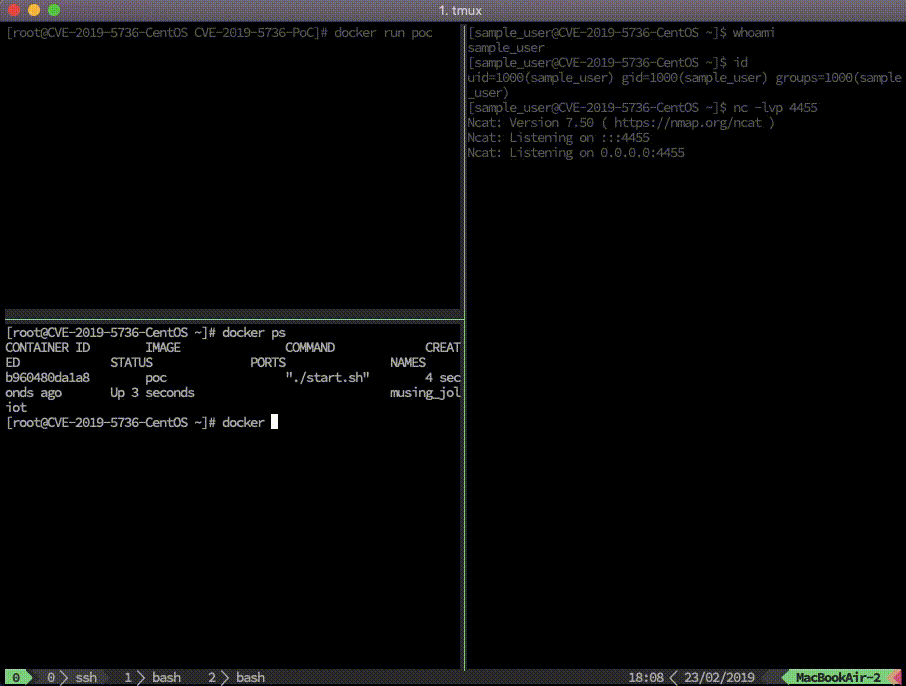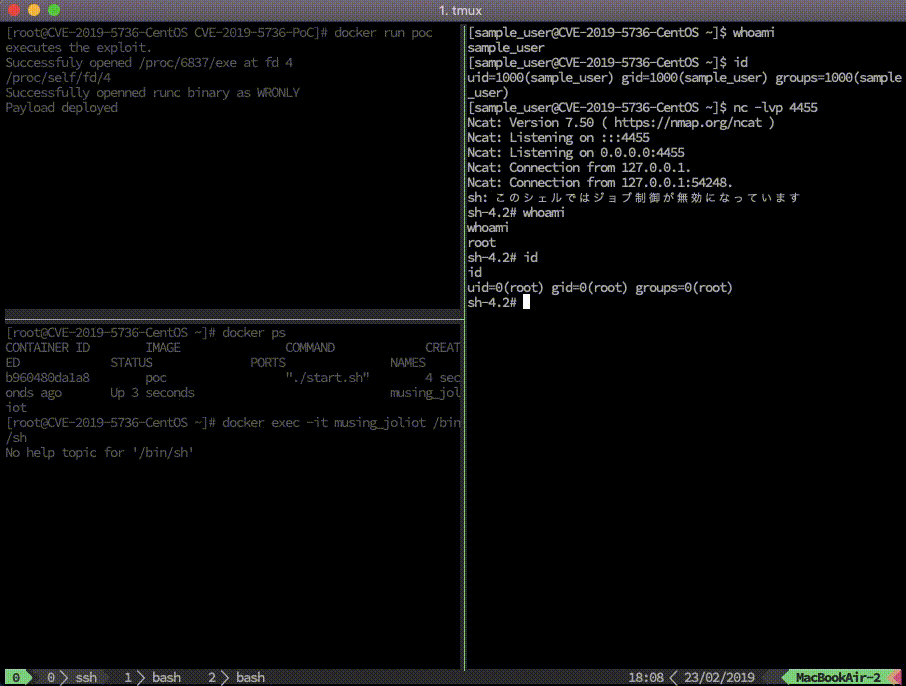 yyqs2008/cve-2019-5736-poc-2
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.
 scherepiuk/container-escape-ebpf
POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133