
Antignis
 huntandhackett/antignis
Automates Windows host-based firewall management by importing network data into a central database, creating Active Directory groups, and generating…
configuration-auditingdefensive-toolsnetwork-access-control+1
43
huntandhackett/antignisAutomates Windows host-based firewall management by importing network data into a central database, creating Active Directory groups, and generating…

 roddhjav/apparmor.d
Comprehensive set of over 1500 AppArmor profiles to confine Linux system processes, desktops, and services, with support for multiple distributions…
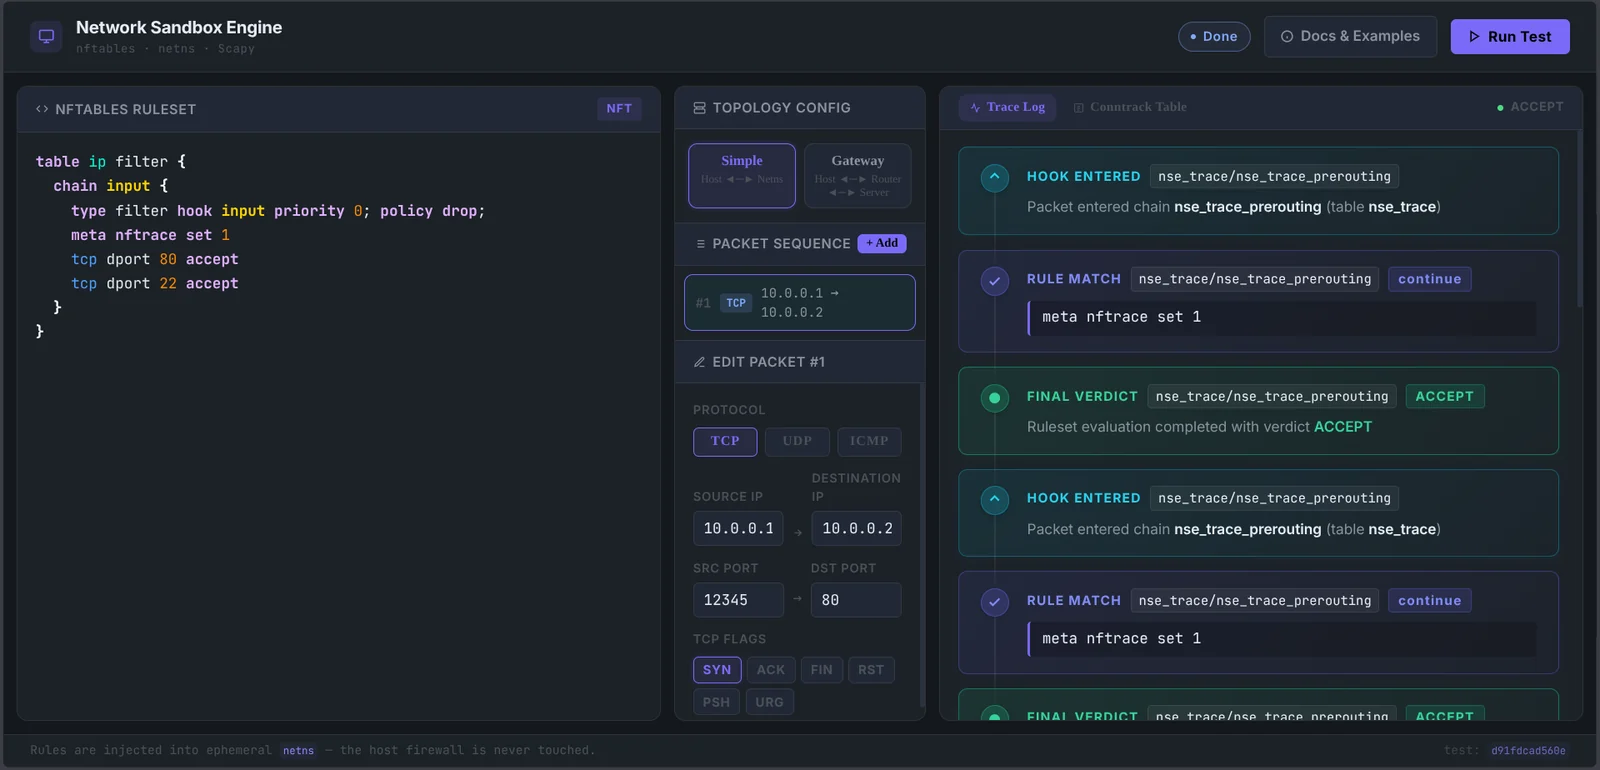 onyks-os/networksandboxengine
A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…
 hwdsl2/setup-ipsec-vpn
Automated IPsec VPN server setup with IPsec/L2TP, Cisco IPsec, and IKEv2 support. Includes helper scripts for user and certificate management, and…
 gagaltotal/cve-2026-42945-nginx-rift-toolkit
Automated toolkit for scanning, exploiting, and patching CVE-2026-42945 (critical RCE in nginx). Includes network scanner, heap spray exploit, and…
 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 ets-mse/secure-boot-cert-servicing
Standalone assessment and servicing for the Secure Boot 2011 to 2023 certificate rollover (CVE-2023-24932 / KB5025885). Assess-only by default; no…
 cain66666/openclaw-hardening-check
Offline, read-only hardening check for a self-hosted OpenClaw install — gateway exposure, auth, CVE-2026-25253. Never prints secrets, makes no…
 hargabyte/cve-scanner
Local CVE scanner for OpenClaw that checks versions against 522+ known vulnerabilities, displays recent HIGH-severity CVEs, and recommends upgrades.…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 raptoratack/copyfail-scanner-cve-2026-31431
Scans systems for CVE-2026-31431 (CopyFile vulnerability), enumerates system details, evaluates exposure, reports vulnerable status, and optionally…
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 klairmanraj/multi-vlan-enterprise-network-security-infrastructure
Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…
 isnic/prober
Automated, reproducible network security testing framework using Ansible and BATS to verify DNS, host availability, open ports, and TLS configuration…
 abdullahaligun/reachability-check
Browser-based network connectivity checker for testing firewall rules, access restrictions, and corporate policy compliance. Supports HTTP Fetch and…
 arisharazakhan-cpu/dod-blue-team-network-lab
High fidelity defensive security lab simulating a DoD aligned enterprise network with Active Directory, VLAN segmentation, STIG based hardening,…