Harden-Windows-Security

Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…

Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…

AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…

HardeningKitty and Windows Hardening Settings

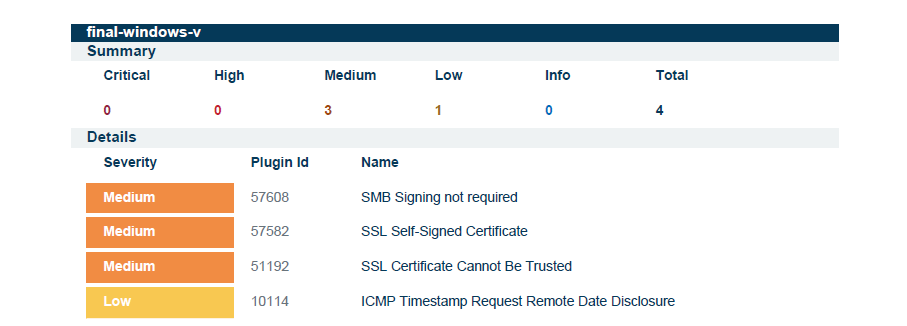
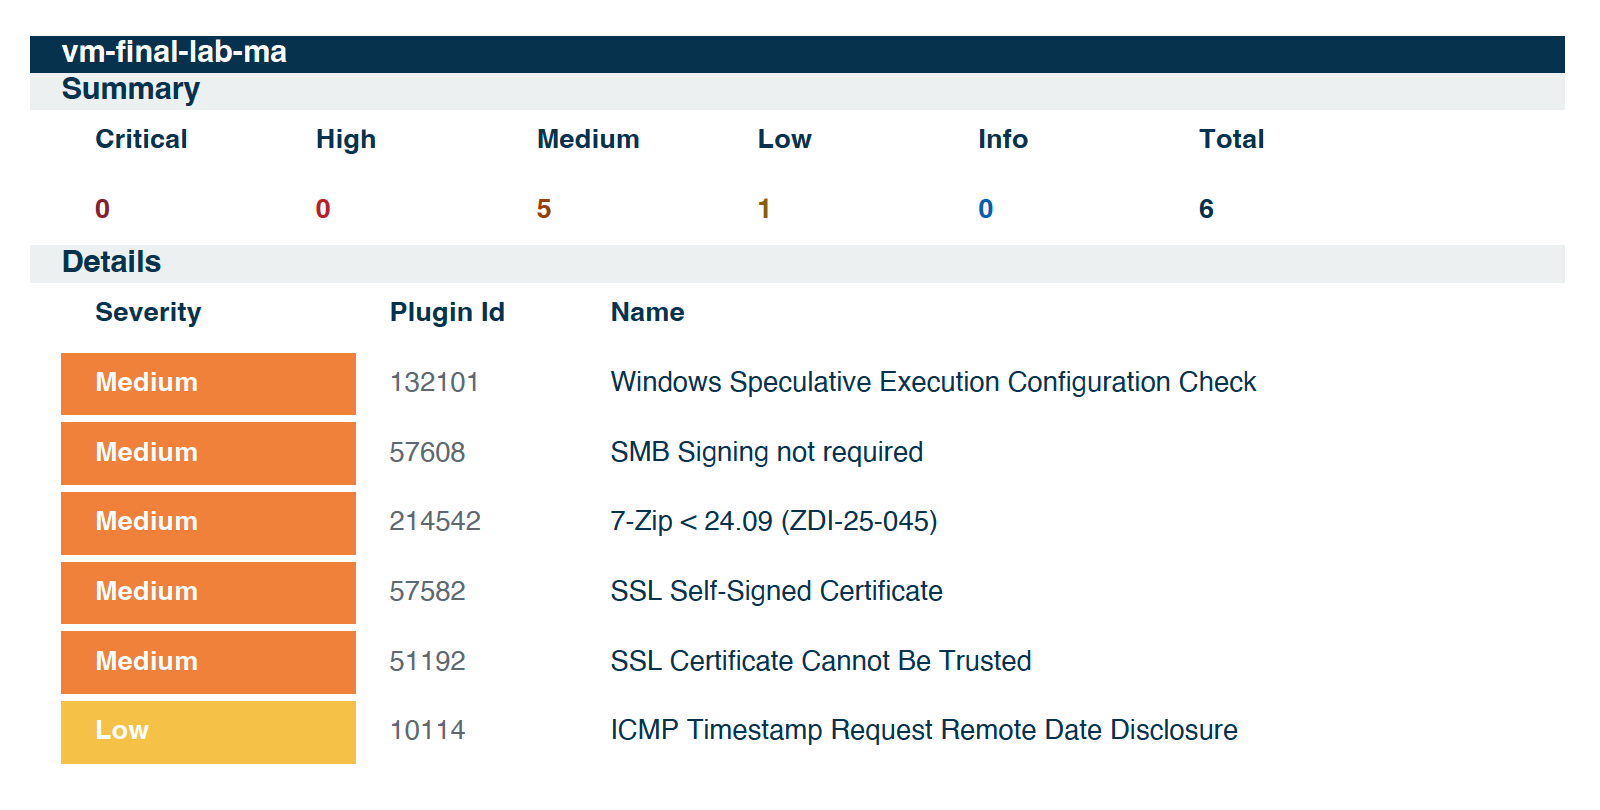
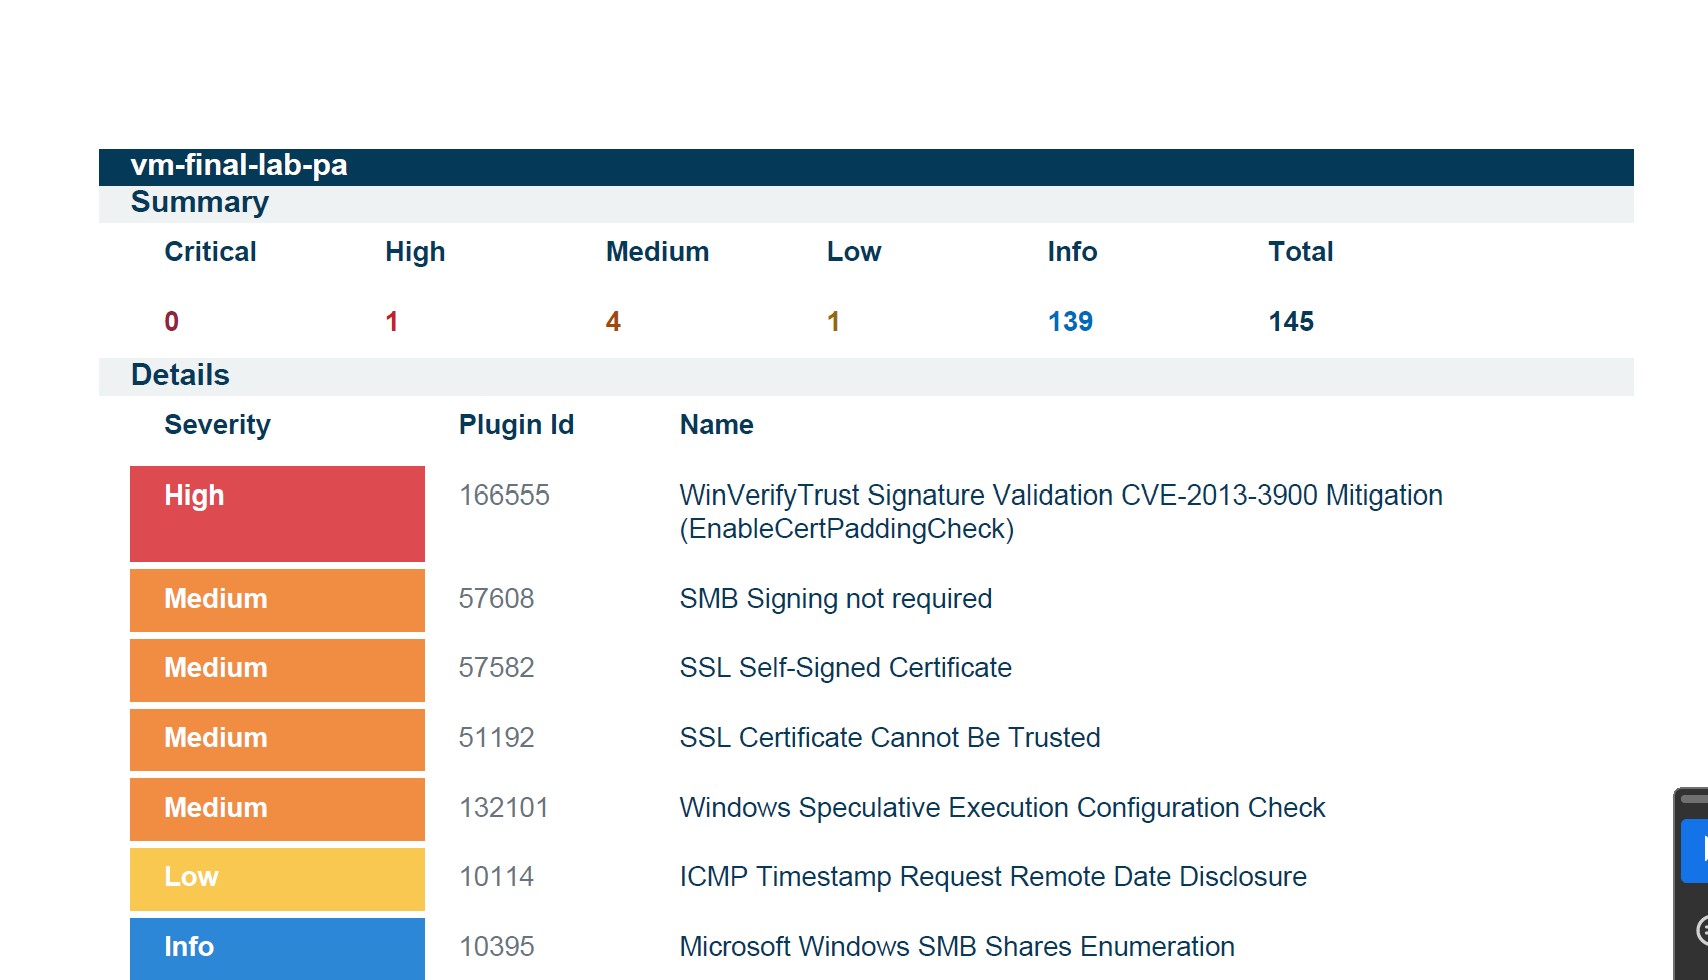
Enterprise vulnerability management on Azure — Terraform-deployed Nessus scanner, credentialed scanning, CVE-2013-3900 remediation with verified…

A small powershell script to disable print spooler service using desired state configuration

PowerShell audit script to detect missing patches for CVE-2024-38063, an IPv6 vulnerability in Windows systems, enabling rapid remediation…

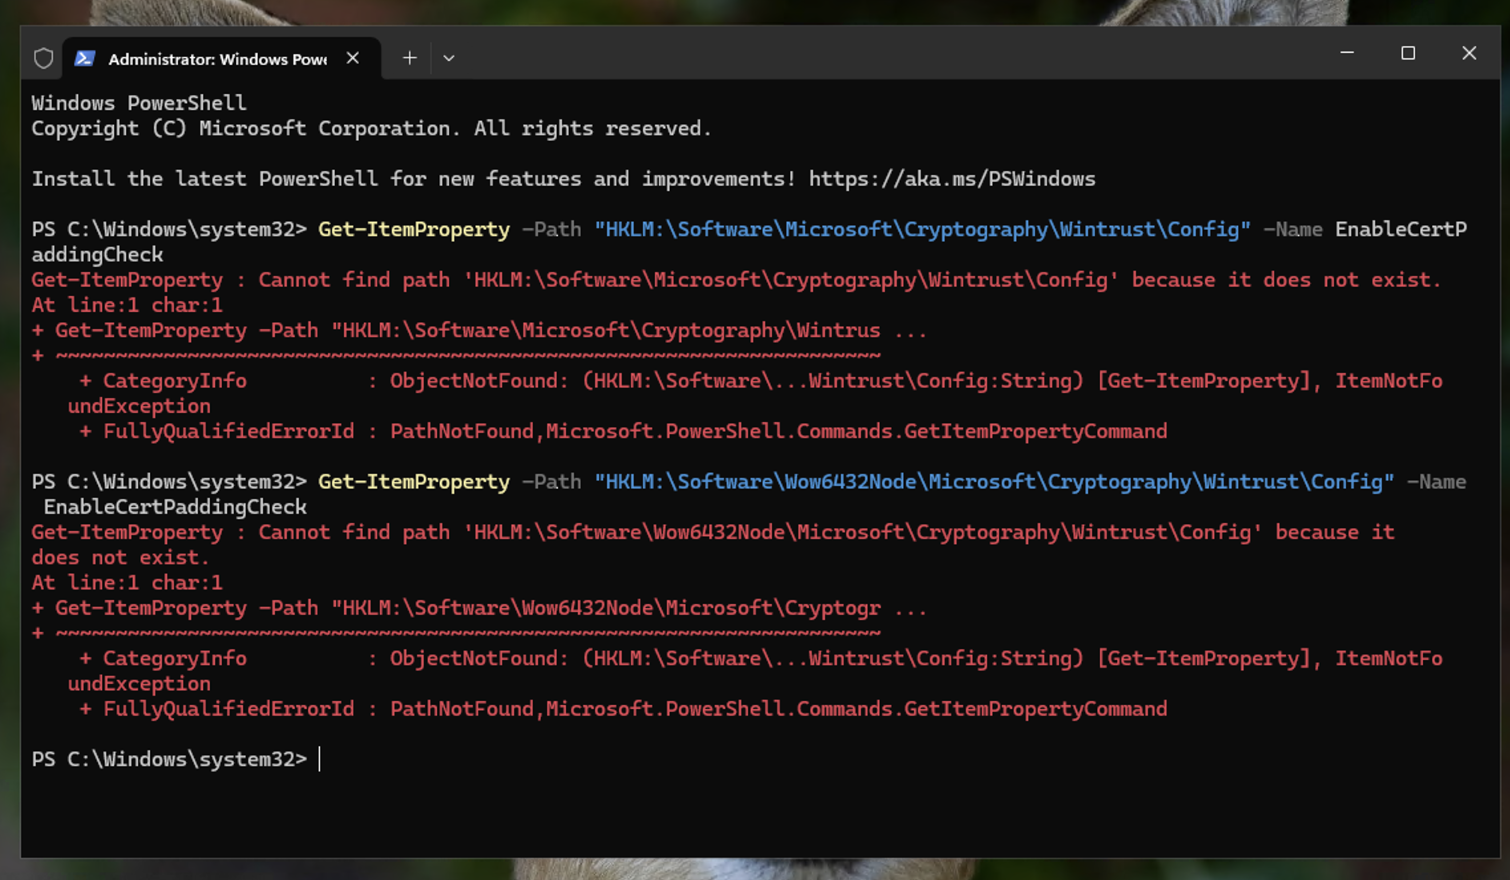
PowerShell remediation for CVE-2013-3900 (WinVerifyTrust) / Tenable Plugin 166555 using EnableCertPaddingCheck.

Fix WinVerifyTrust Signature Validation Vulnerability, CVE-2013-3900, QID-378332

C++ utility that checks Windows OS version and detects whether the patch for CVE-2018-1010 is installed using systeminfo and wmic commands.

Step-by-step remediation guide for CVE-2013-3900 WinVerifyTrust vulnerability on Windows Server 2019, including registry fix, reboot, and…

End-to-end remediation of CVE-2013-3900 using PowerShell and Tenable. Demonstrates vulnerability identification, registry hardening, and automated…

A registry-based workaround can be used to help protect an affected Windows server, and it can be implemented without requiring an administrator to…

Step-by-step remediation report for CVE-2013-3900 on Windows Server 2019 Azure VM, using Tenable/Nessus credentialed scans and registry hardening to…

Windows Elevation of Privilege Vulnerability (SeriousSAM)