PoC-RCE-CVE-2025-55182

Advanced RCE exploitation toolkit for React Server Components vulnerabilities. Features multiple pre-built payloads, Shodan integration for target…

Advanced RCE exploitation toolkit for React Server Components vulnerabilities. Features multiple pre-built payloads, Shodan integration for target…

Step-by-step guide to exploiting Samba 3.0.20 (CVE-2007-2447) using Metasploit, including Nmap scanning, payload setup, and reverse shell execution.

Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…

Python-based exploit for Apache Struts CVE-2017-5638 with single URL and batch scanning modes, vulnerability checking, and Nmap reconnaissance…

In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…

Red Team K8S Adversary Emulation Based on kubectl


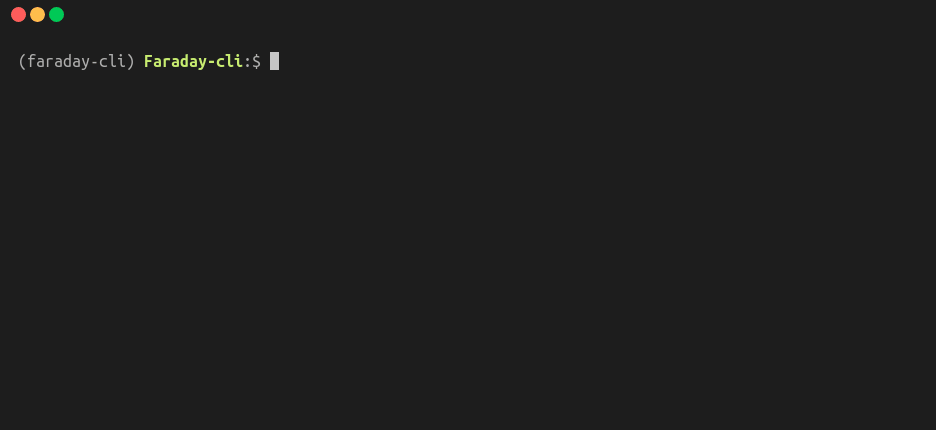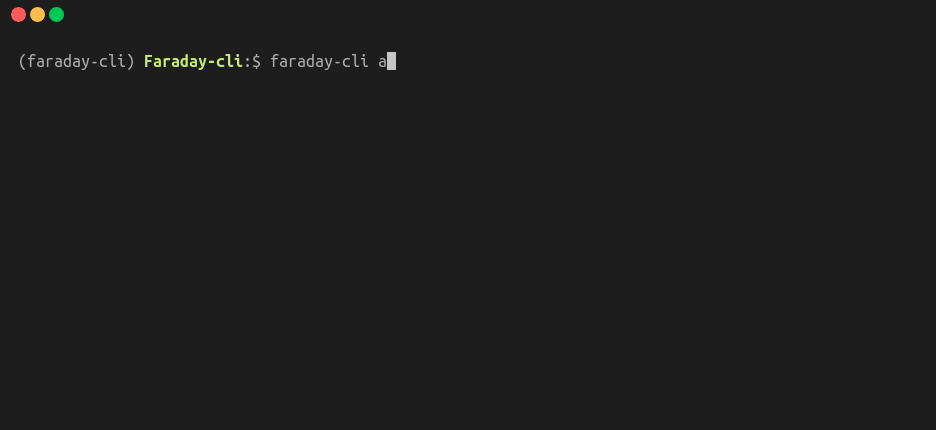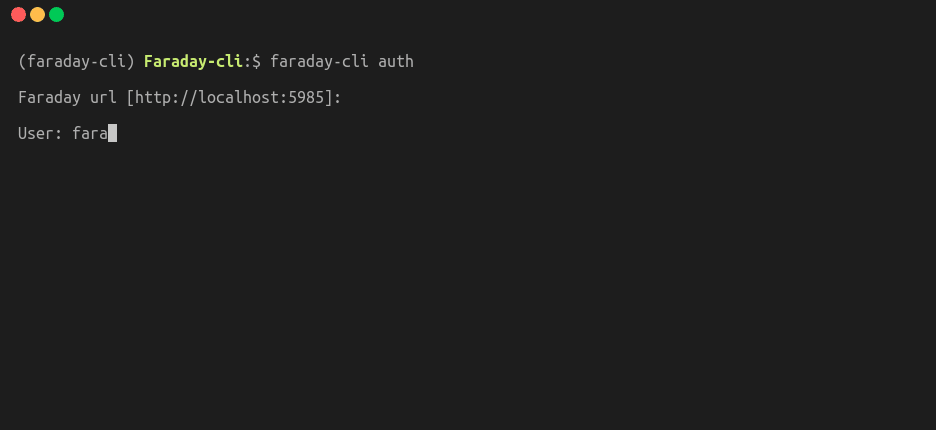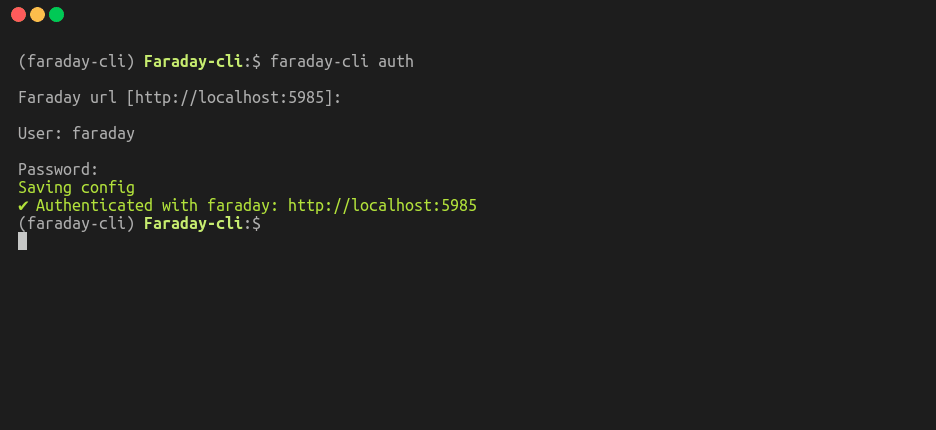
Faraday's Command Line Interface

A third-party Gopher Assassin for the Havoc Framework.

Authorized high-impact tool from CYBERDUDEBIVASH ECOSYSTEM to detect CVE-2025-64155 (FortiSIEM phMonitor Command Injection). Scans for open ports and…

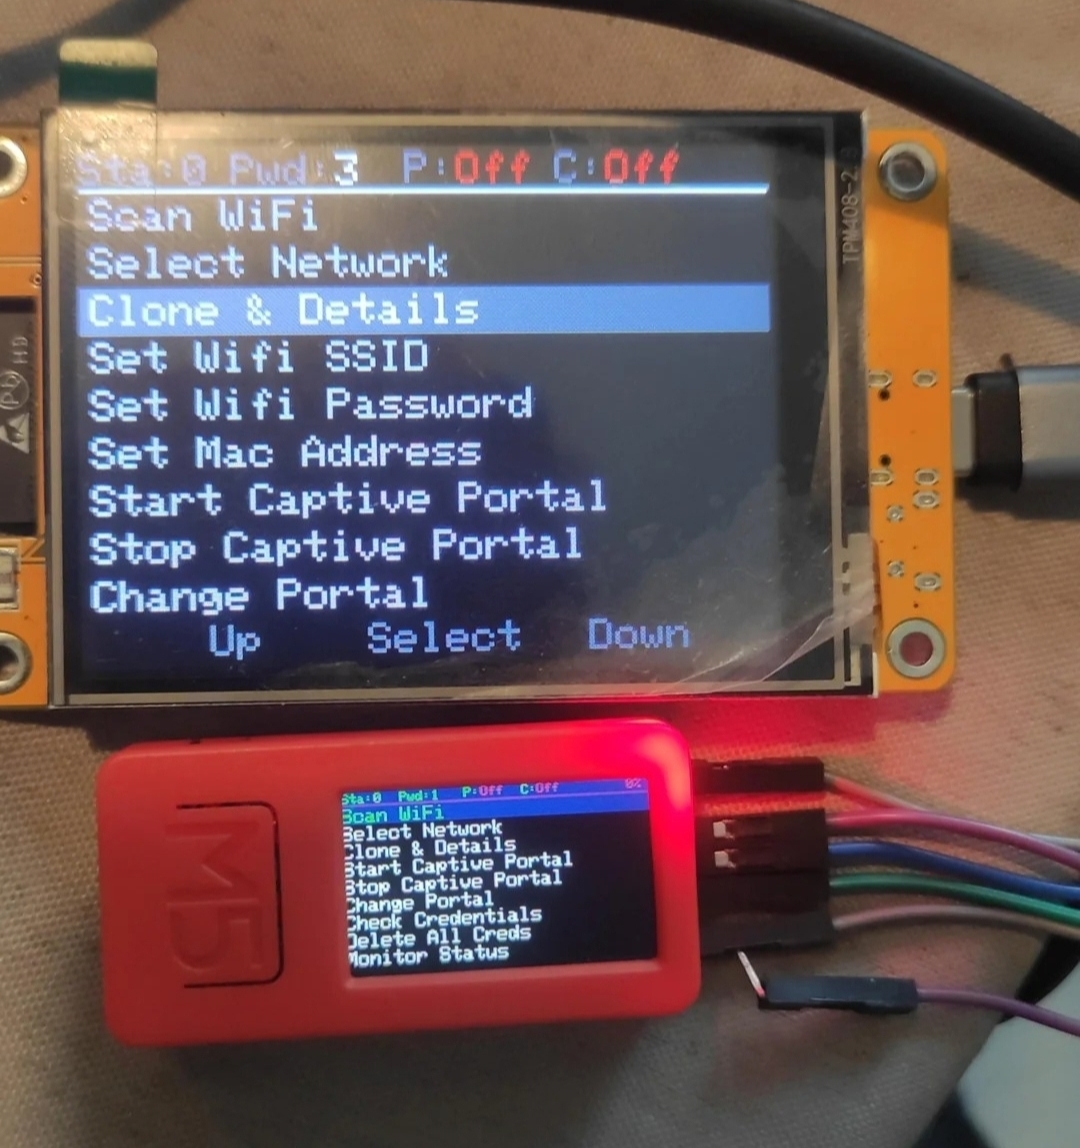
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…

Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.

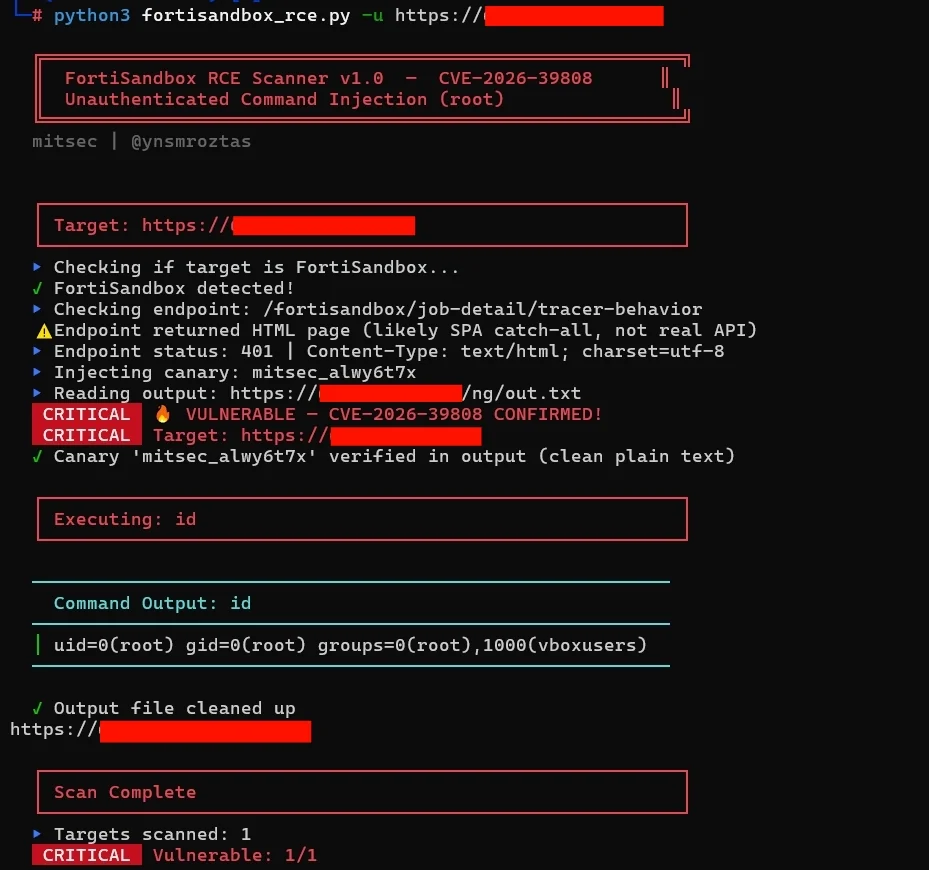
Unauthenticated RCE scanner for FortiSandbox CVE-2026-39808 with canary-based verification, command execution, and pipeline integration for mass…

Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…

Exploit tool for CVE-2024-49369 in Icinga, enabling subnet scanning, agent takeover via JSON-RPC impersonation, arbitrary command execution, and…

CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…