spring-cloud-gateway-rce

Python exploit for CVE-2022-22947 (Spring Cloud Gateway RCE) with command execution, reverse shell, and vulnerability detection via Actuator API SpEL…

Python exploit for CVE-2022-22947 (Spring Cloud Gateway RCE) with command execution, reverse shell, and vulnerability detection via Actuator API SpEL…

Proof-of-concept exploit for CVE-2022-22963 (Spring Cloud Function SpEL injection) with detection script and curl-based RCE payload generation.

Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…

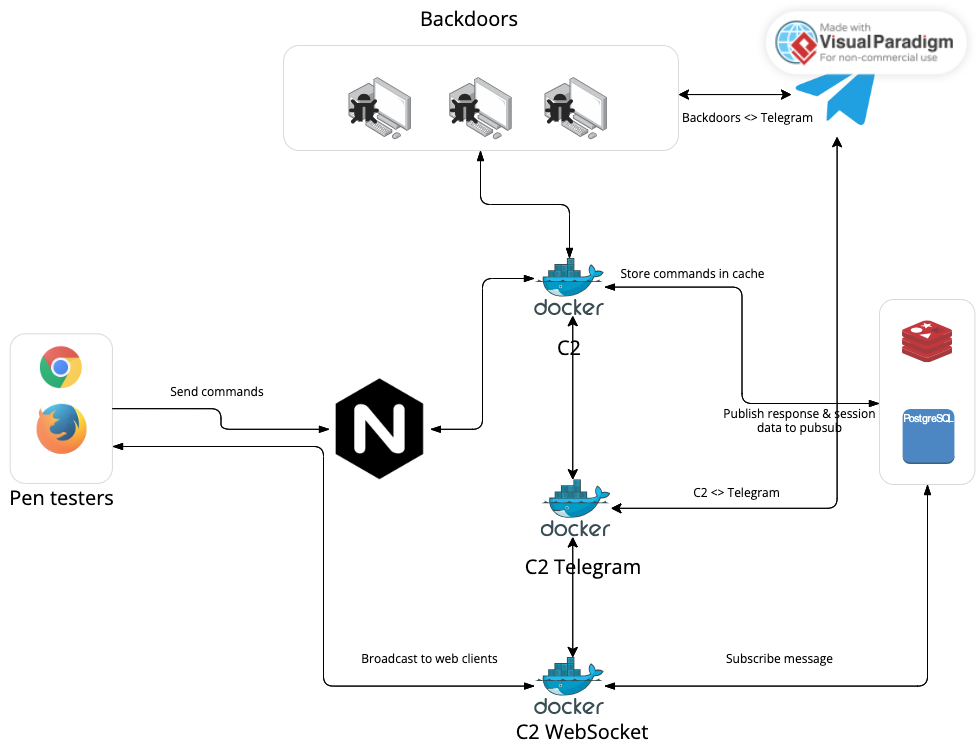
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…

KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.

Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…

Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…

Cobalt Strike External C2 Integration With Azure Servicebus, C2 traffic via Azure Servicebus

Just a repo of random Python scripts to get pentesters started with the Python language on engagements.

Collection of tools to use with Azure Applications

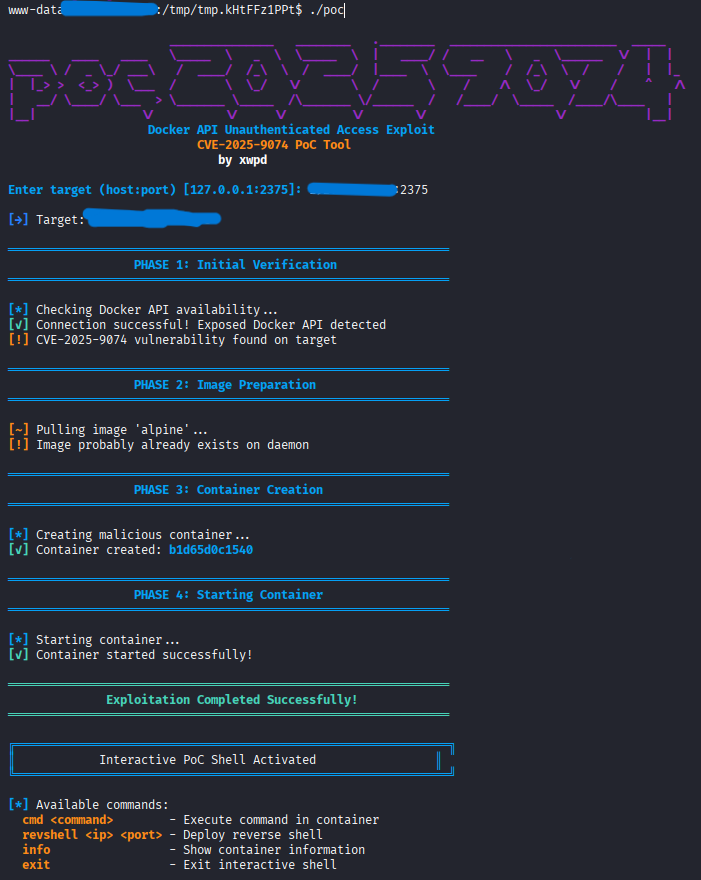
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…

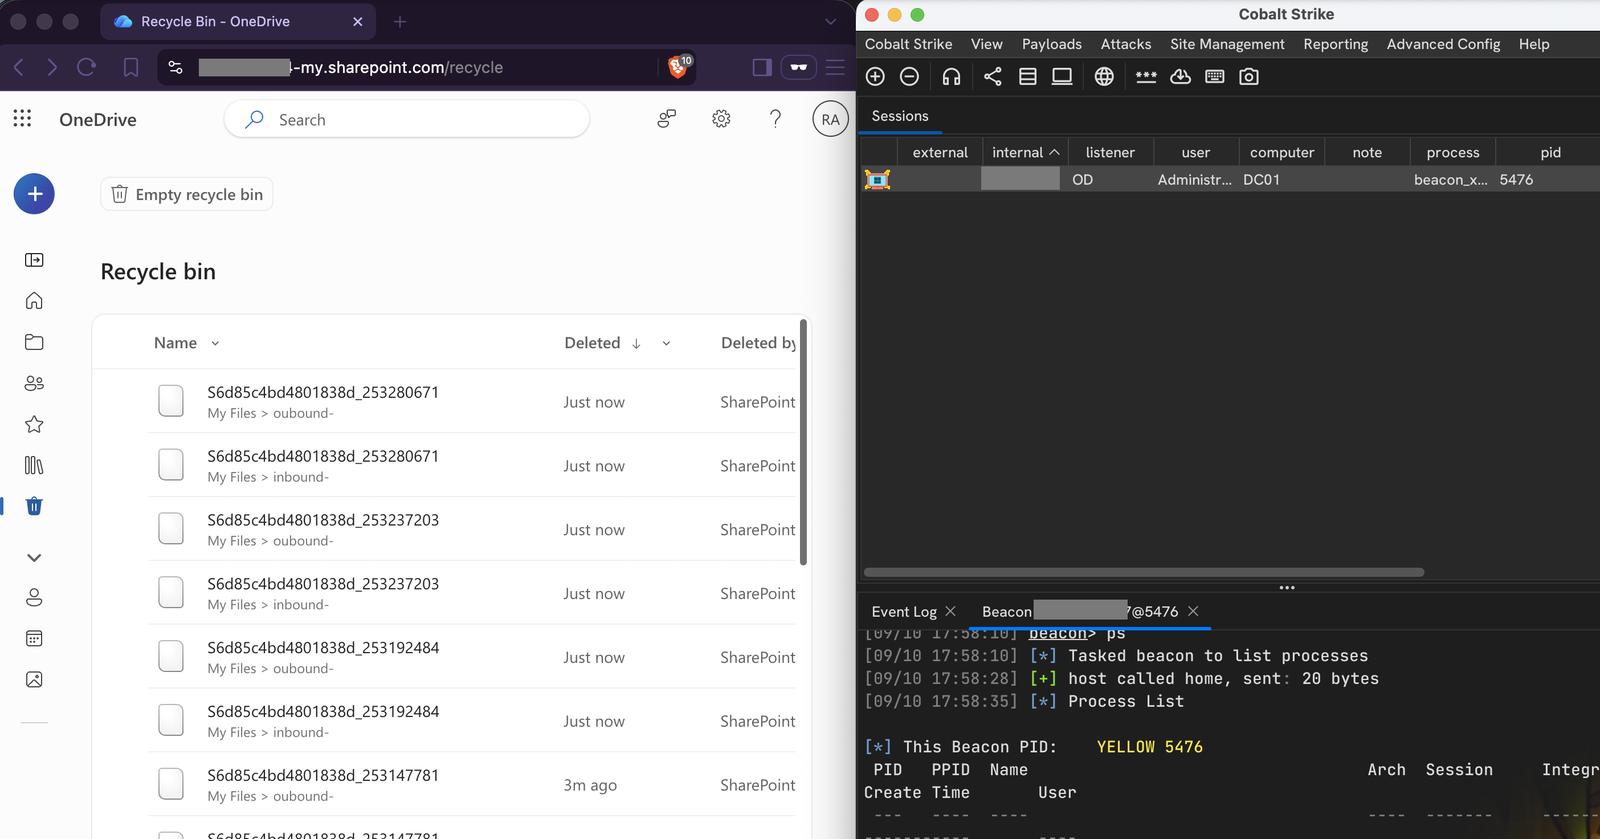
OneDrive as a covert C2 transport for Cobalt Strike

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

Ansible role to configure redirectors for red team C2

Public security advisory for CVE-2025-66209, CVE-2025-66210, CVE-2025-66211, CVE-2025-66212, and CVE-2025-66213