

WMImplant
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
command-and-controlinformation-gatheringlateral-movement+3
866
redsiege/wmimplantThis is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 tomiwa-ot/moukthar
Android remote administration tool
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
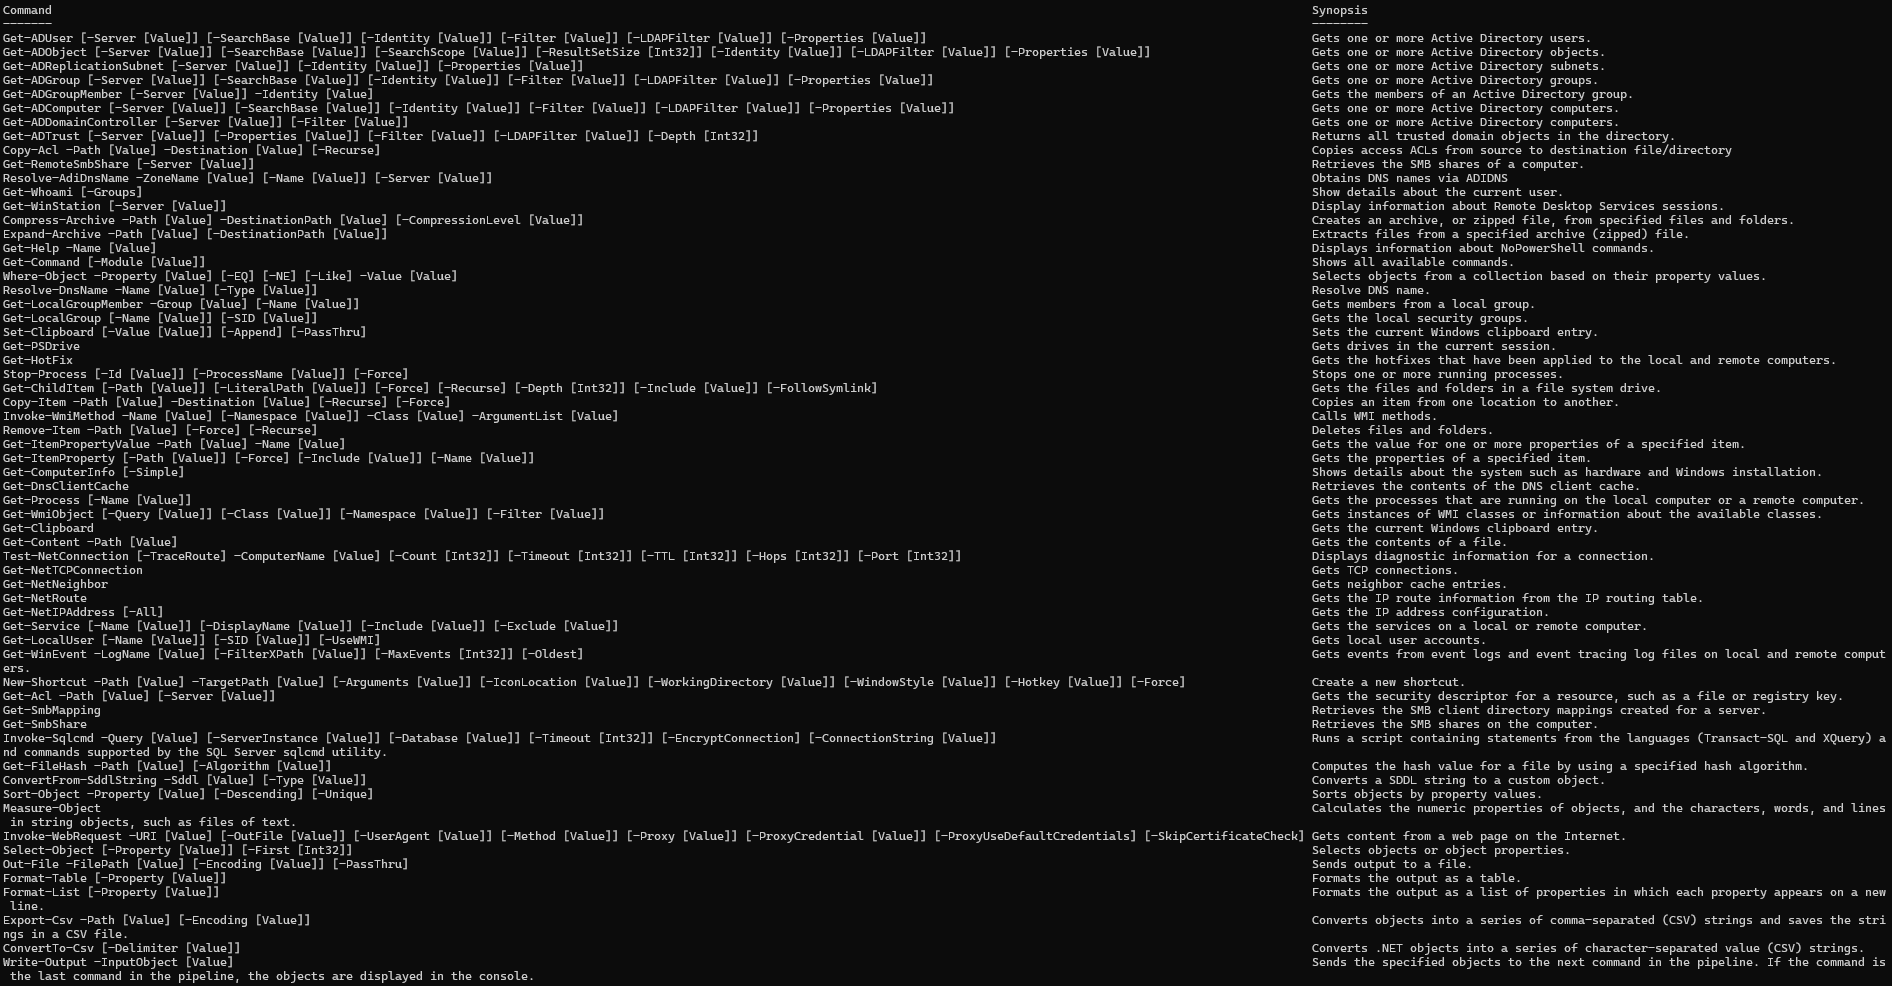 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
 redcode-labs/coldfire
Golang malware development library
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 emptymonkey/revsh
A reverse shell with terminal support, data tunneling, and advanced pivoting capabilities.
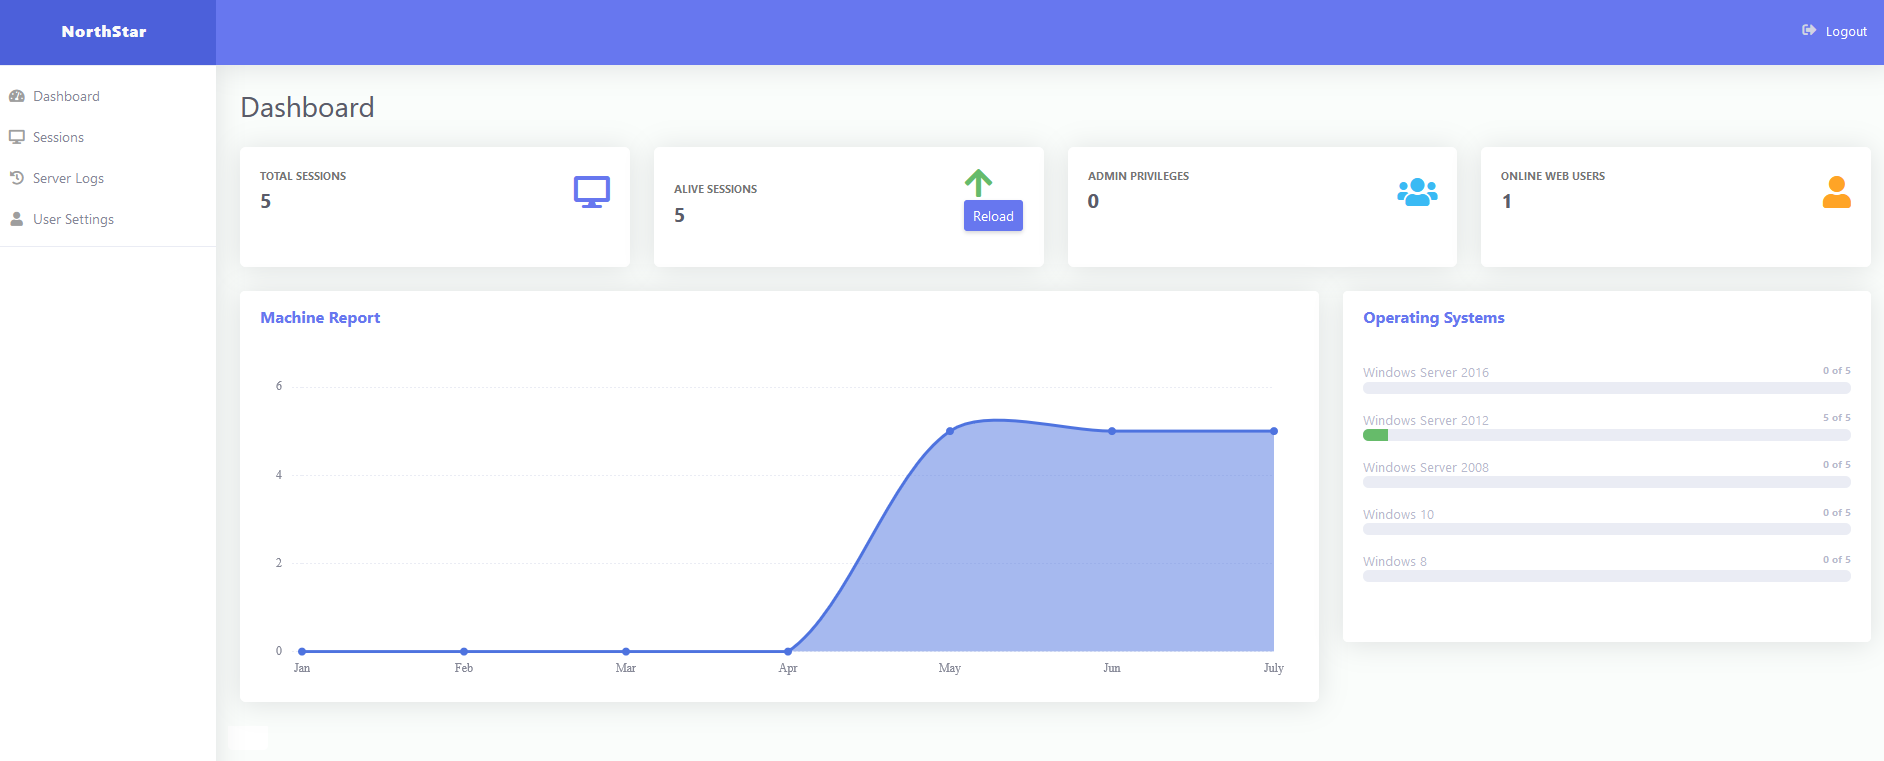 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 pjlantz/hale
Botnet command & control monitor