

PSRansom
 joelgmsec/psransom
PowerShell Ransomware Simulator with C2 Server
command-and-controleducationencryption-decryption-tools+1
509
joelgmsec/psransomPowerShell Ransomware Simulator with C2 Server
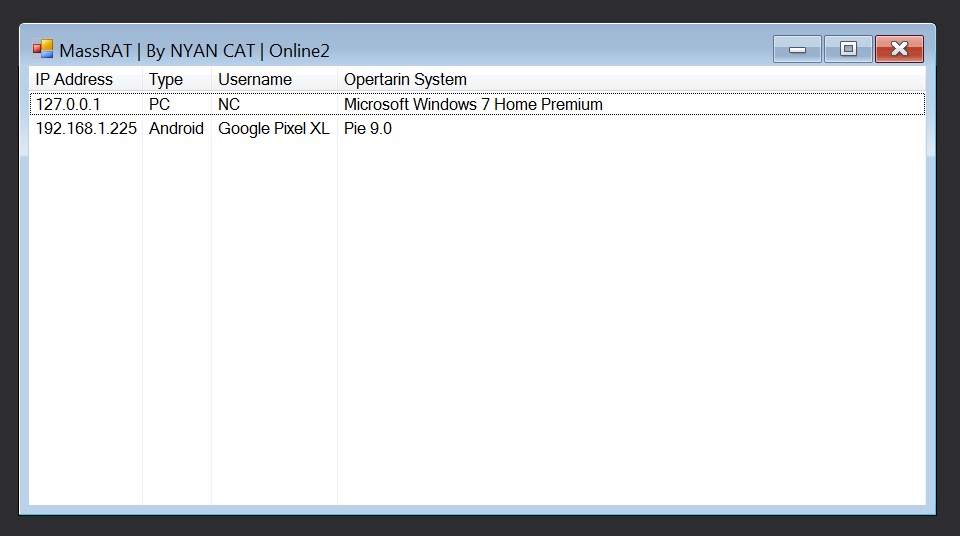 nyan-x-cat/mass-rat
Basic Multiplatform Remote Administration Tool - Xamarin

 huntoai/rdroid
[Android RAT] Remotely manage your android phone using PHP Interface
 jymcheong/autottp
Automated Tactics Techniques & Procedures
 ivan-sincek/powershell-reverse-tcp
PowerShell scripts for communicating with a remote host.
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 pyroxenites/nextjs_rce_exploit_tool
Exploit for CVE-2025-55182 & CVE-2025-66478
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
 chipik/sap_eem_cve-2020-6207
PoC for CVE-2020-6207 (Missing Authentication Check in SAP Solution Manager)
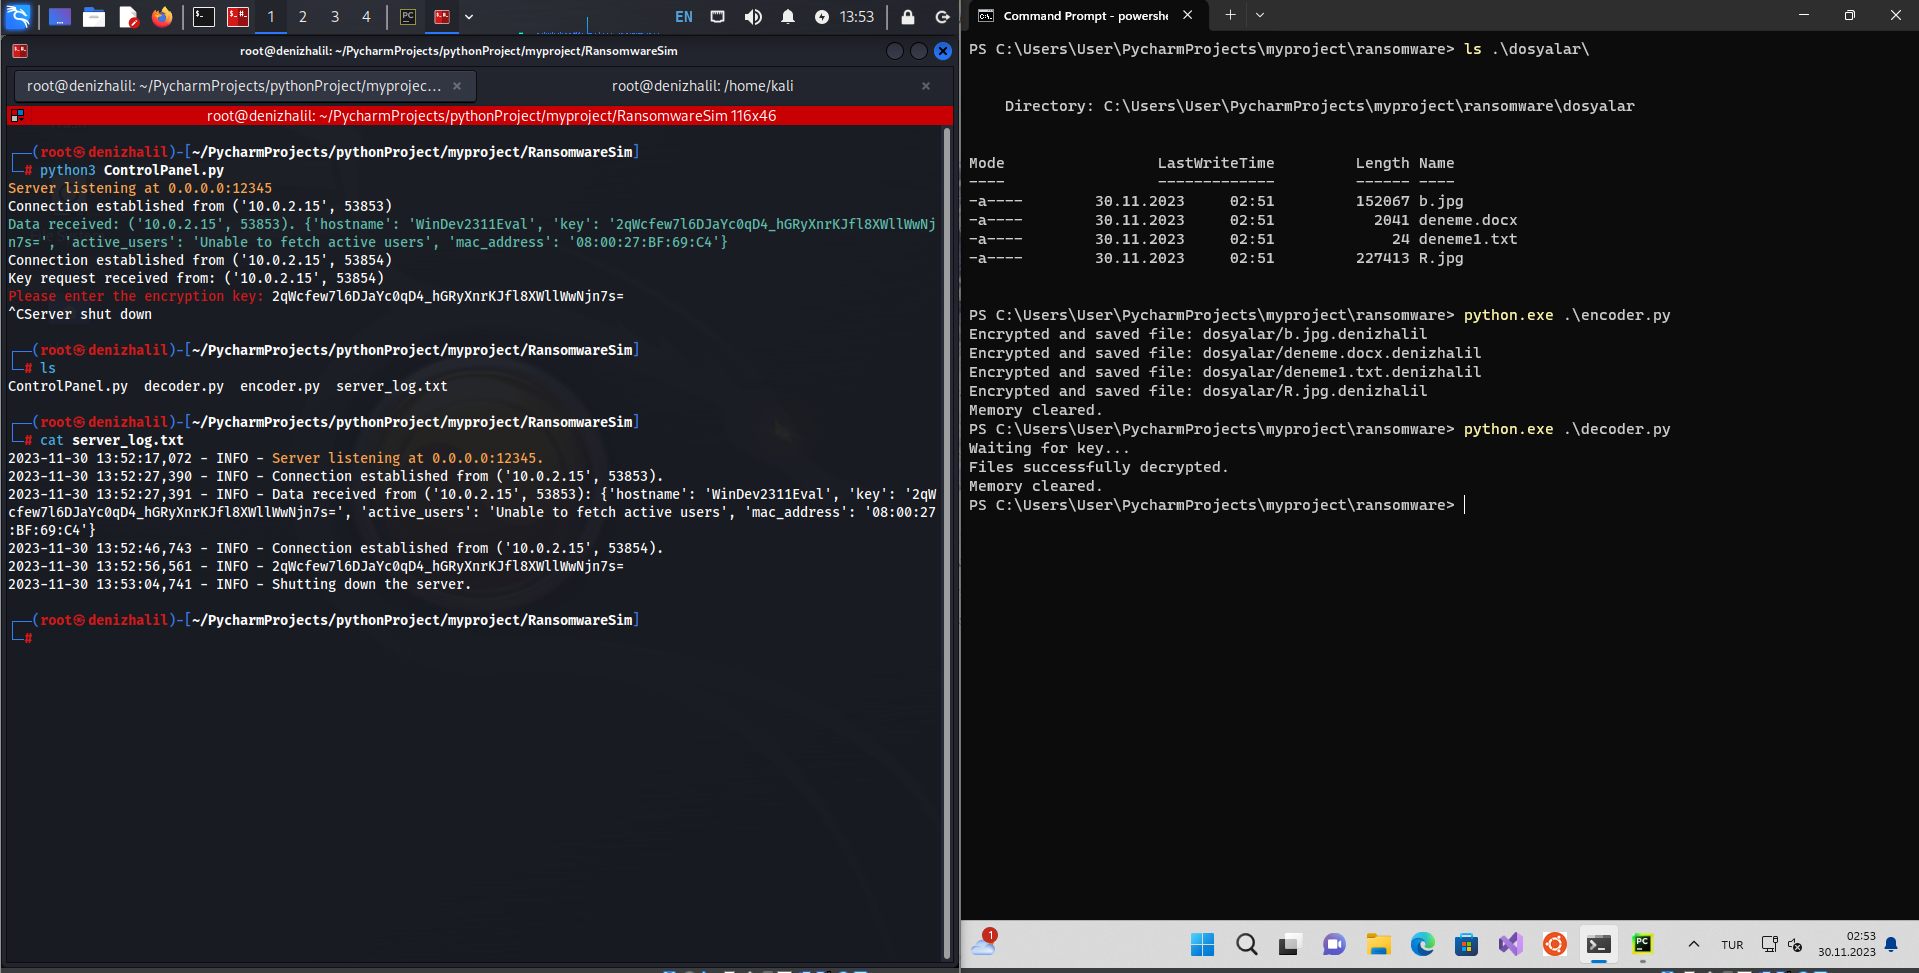 halildeniz/ransomwaresim
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.

 danielbohannon/out-fincodedcommand
POC Highlighting Obfuscation Techniques used by FIN threat actors based on cmd.exe's replace functionality and cmd.exe/powershell.exe's stdin command…
 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 stphivos/rat-shell
Windows Remote Access Trojan (RAT)