
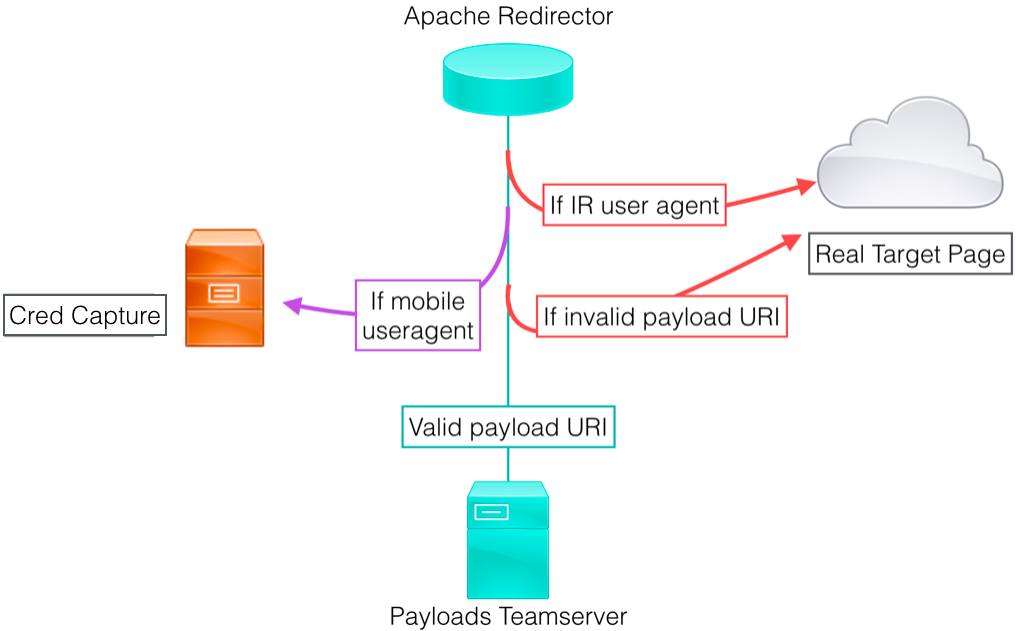
Red-Team-Infrastructure-Wiki
 bluscreenofjeff/red-team-infrastructure-wiki
Wiki to collect Red Team infrastructure hardening resources
cloud-infrastructure-securitycommand-and-controlcurated-resources+5
4.5k
bluscreenofjeff/red-team-infrastructure-wikiWiki to collect Red Team infrastructure hardening resources
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 ph4ntonn/stowaway
Multi-hop proxy tool for pentesters enabling traffic routing through multiple nodes, SOCKS5/SSH tunneling, port forwarding, remote shell, and…
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 s1n6h/pentest-harness
Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…
 postrequest/link
link is a command and control framework written in rust
 samybaiwir/dnslivery
Easy files and payloads delivery over DNS
 ttpreport/ligolo-mp
Multiplayer pivoting solution
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 leo4j/amnesiac
PowerShell-based post-exploitation framework for lateral movement in Active Directory environments. Executes in-memory with named-pipe command…
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
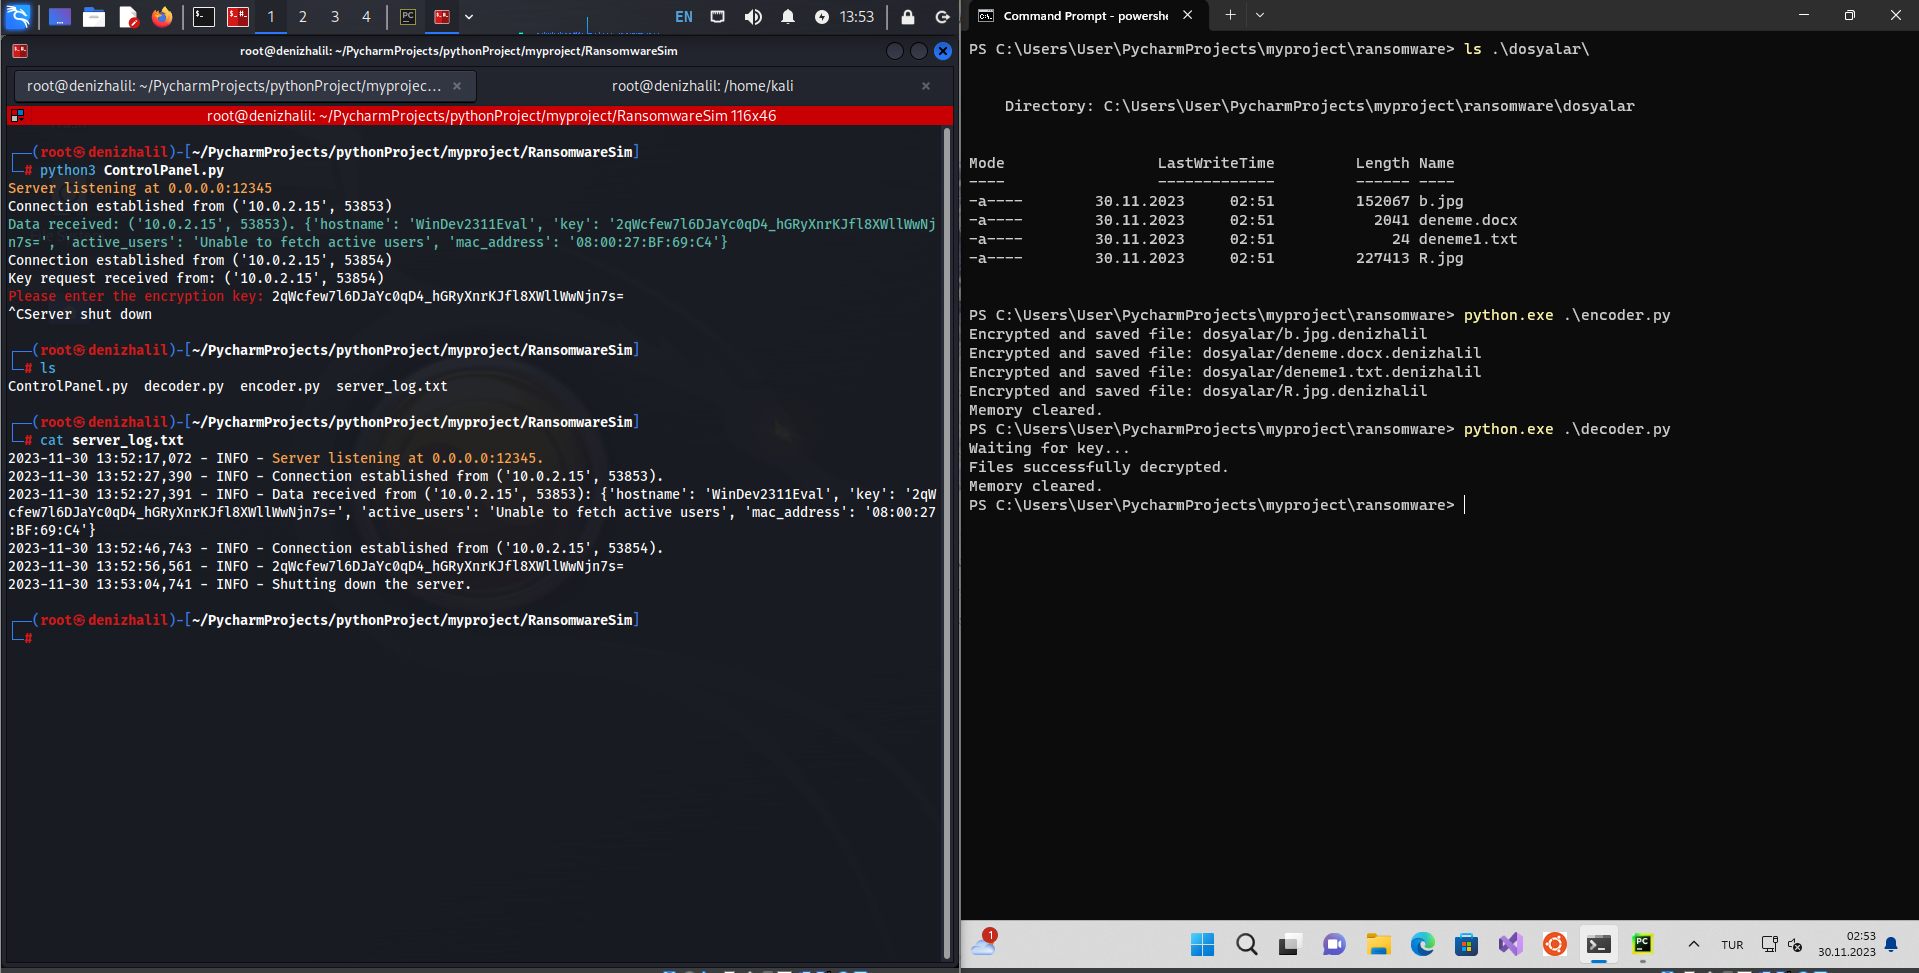 halildeniz/ransomwaresim
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)