Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
CVE-2024-51442 preview

CVE-2024-51442

GitHubmselbrede/cve-2024-51442

CVE-2024-51442 write up and example config file

binary-exploitationcommand-and-controlexploitation+2
1 year ago
CVE-2022-37706 preview

CVE-2022-37706

GitHubsanan2004/cve-2022-37706

PoC

binary-exploitationcommand-and-controlctf+6
2 years ago
CVE-2022-23935 preview

CVE-2022-23935

GitHubantisecc/cve-2022-23935

Exploit for CVE-2022-23935, a command injection vulnerability in Exiftool versions prior to 12.38, allowing arbitrary command execution via crafted…

binary-exploitationcommand-and-controlexploitation+3
3 years ago
CVE-2023-25610 preview
Archived

CVE-2023-25610

GitHubqi4l/cve-2023-25610

FortiOS 管理界面中的堆内存下溢导致远程代码执行
binary-exploitationcommand-and-controlexploitation+3
233 years ago
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
binary-exploitationcommand-and-controlids-ips-evasion+7
3397 months ago
CyberStrikeAI preview

CyberStrikeAI

GitHubed1s0nz/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

ai-securitybinary-analysiscloud-security+9
7.0k2 days ago
CyberStrikeAI preview

CyberStrikeAI

GitHubaipentest/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+8
7.0k9 days ago
unicorn preview

unicorn

GitHubtrustedsec/unicorn

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
command-and-controlexploit-frameworksids-ips-evasion+8
3.9k5 days ago
CobaltStrikeParser preview

CobaltStrikeParser

GitHubsentinel-one/cobaltstrikeparser

Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
binary-analysiscommand-and-controlmalware-analysis+1
1.1k3 years ago
JYso preview

JYso

GitHubqi4l/jyso

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

command-and-controlctfexploit-frameworks+5
1.8k3 months ago
meterssh preview

meterssh

GitHubtrustedsec/meterssh

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
command-and-controlexploitationpayload-development+4
5309 years ago
java-stager preview

java-stager

GitHubcornerpirate/java-stager

A PoC Java Stager which can download, compile, and execute a Java file in memory.
command-and-controldynamic-code-analysiseducation+7
1078 years ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
command-and-controldata-exfiltrationeducation+8
1747 months ago
BRC4-BOF-Artillery preview

BRC4-BOF-Artillery

GitHubparanoidninja/brc4-bof-artillery

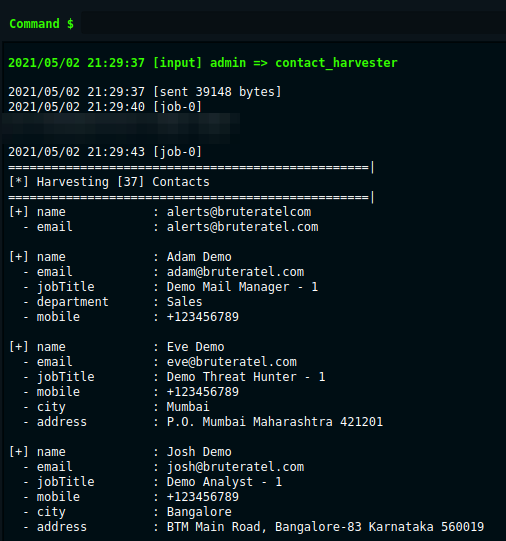
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…

command-and-controlencryption-decryption-toolshash-analysis+5
15110 months ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
672 months ago
CrabLoader preview

CrabLoader

GitHubqmadev/crabloader

Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
command-and-controlexploit-frameworkspayload-development+3
346 months ago
CVE-2023-4450-Attack preview

CVE-2023-4450-Attack

GitHubilikeoyt/cve-2023-4450-attack

Automated Java-based exploit tool for CVE-2023-4450 targeting JimuReport, featuring command execution and memory shell injection (Behinder) for…
command-and-controlexploitationpayload-development+3
212 years ago
CVE-2025-55182-golang-PoC preview

CVE-2025-55182-golang-PoC

GitHubkeklick1337/cve-2025-55182-golang-poc

Go-based proof-of-concept for CVE-2025-55182, a critical RCE in React Server Components. Features vulnerability checking, command execution, memory…

command-and-controlexploitationpayload-development+6
69 months ago
Previous1234Next