
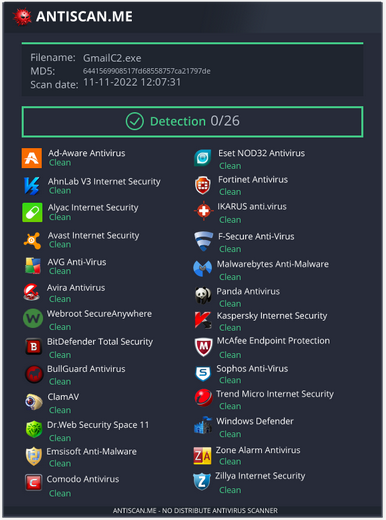
SharpGmailC2
 reveng007/sharpgmailc2
Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
command-and-controldata-exfiltrationpost-exploitation+2
264
reveng007/sharpgmailc2Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
 ziemni/cve-2007-2447-in-python
Python implementation of 'Username' map script' RCE Exploit for Samba 3.0.20 < 3.0.25rc3 (CVE-2007-2447).
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 foudadev/cve-2007-2447
Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…
 wildfootw/cve-2007-2447_samba_3.0.25rc3
Exploit for Samba 3.0.0-3.0.25rc3 'Username' map script command execution vulnerability (CVE-2007-2447), enabling remote code execution.
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
 noxlumens/cve-2022-35914_poc
Modified for GLPI Offsec Lab: call_user_func, array_map, passthru
 blackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant
CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…