

WMIHACKER
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
command-and-controlexploitationlateral-movement+2
rootclay/wmihackerA Bypass Anti-virus Software Lateral Movement Command Execution Tool
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
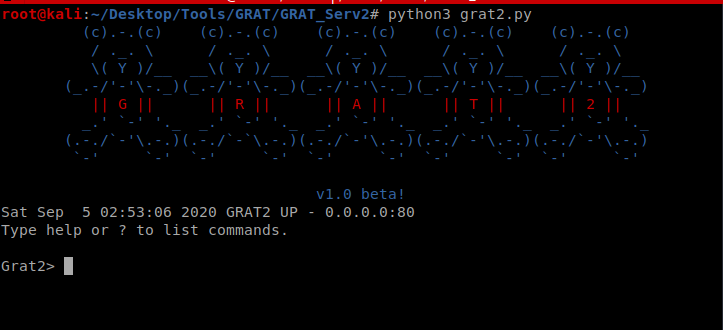 r3nhat/grat2
We developed GRAT2 Command & Control (C2) project for learning purpose.
 outflanknl/findobjects-bof
A Cobalt Strike Beacon Object File (BOF) project which uses direct system calls to enumerate processes for specific loaded modules or process handles.
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 sobri3195/pegasus-gram
Python-based keylogger and surveillance tool with Telegram C2, capturing keystrokes, screenshots, webcam, audio, clipboard, and system activity for…
 gagaltotal/cve-2026-10523-ivanti-sentry
Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…
 jbooz1/cve-2017-0213
A version of CVE-2017-0213 that I plan to use with an Empire stager
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 thecryinggame/cve-2022-39197-rce
CVE-2022-39197 RCE POC
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
 beefproject/beef
The Browser Exploitation Framework Project
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…