metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…

Autonomous Hacking Agent for Red Team

Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

Adversary Emulation Framework

Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…

a guard that blocks catastrophic agent actions

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

:hammer: A modern, cross-platform machine manager

Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.

AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…

An all-in-one hacking tool to remotely take over Android devices.

PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…

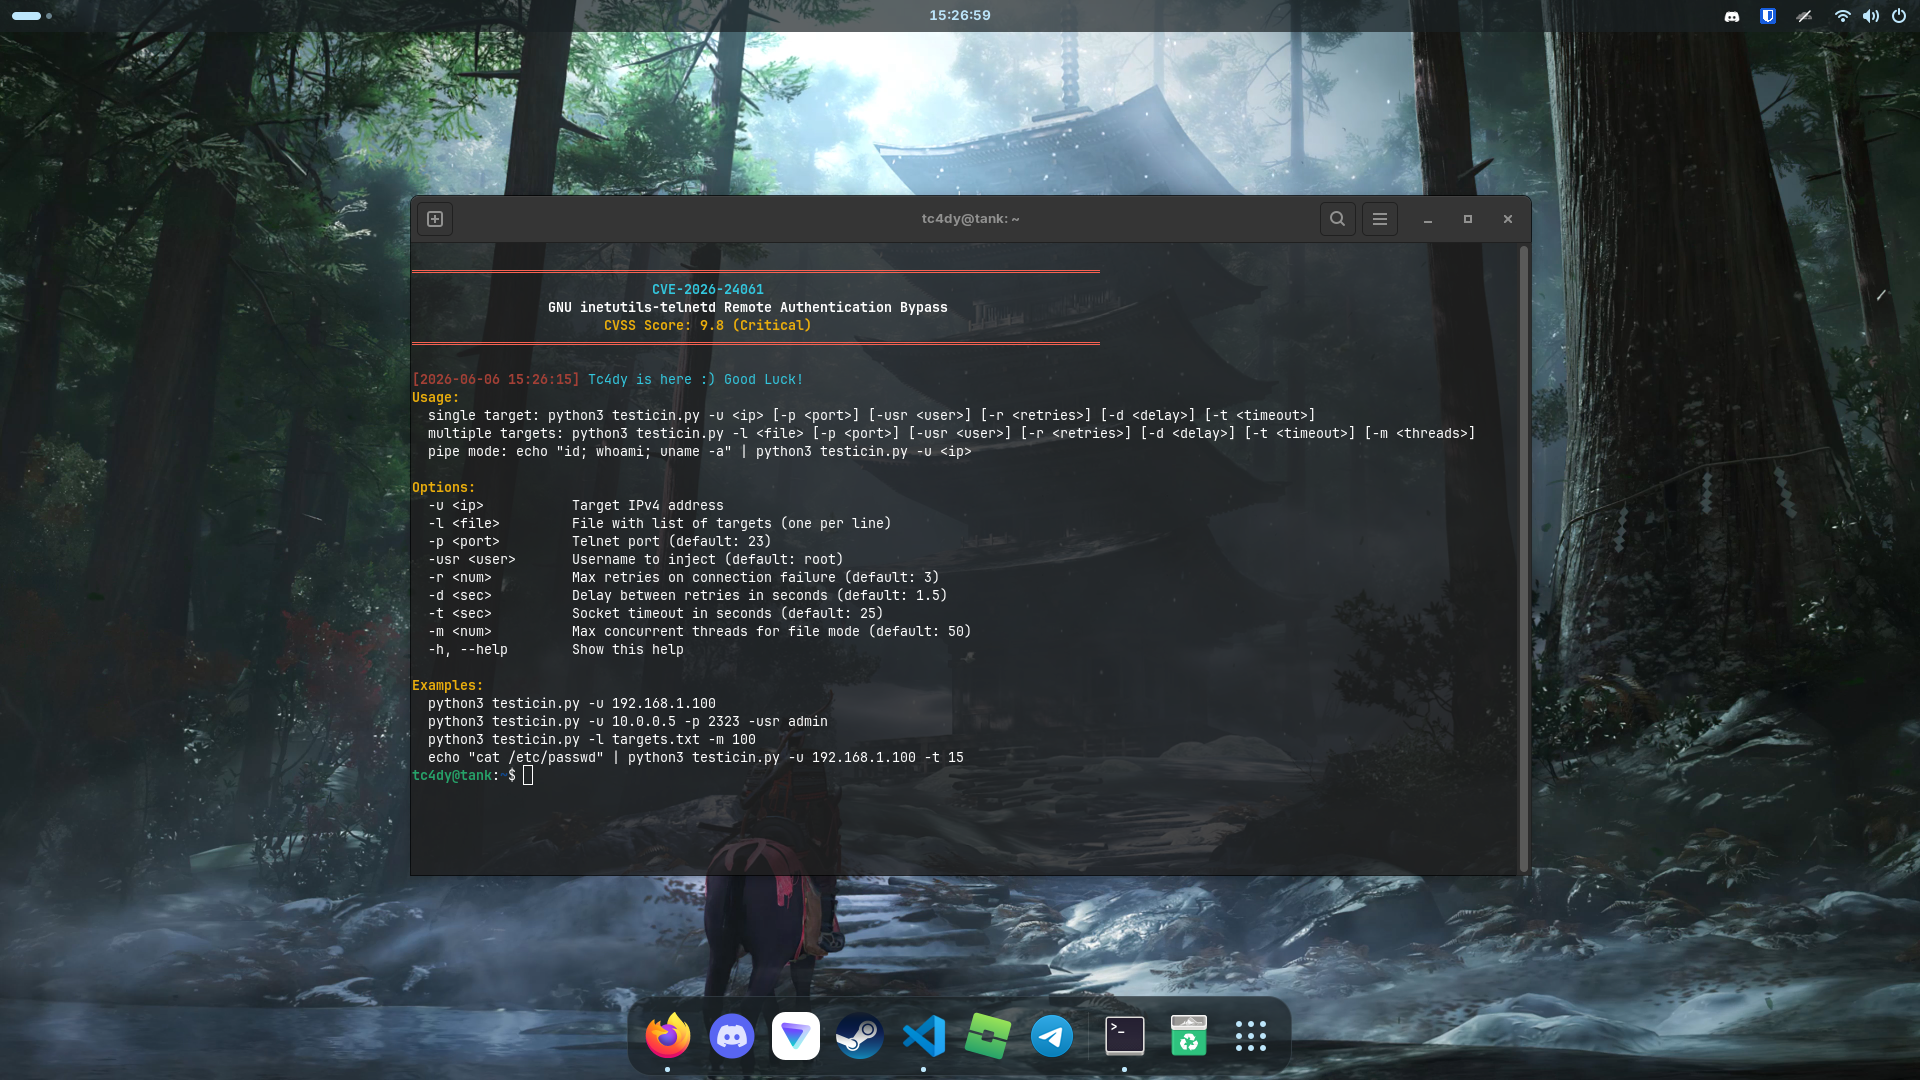
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

A collaborative web exploitation framework.

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…