CVE-2026-24061-PoC-Exploit

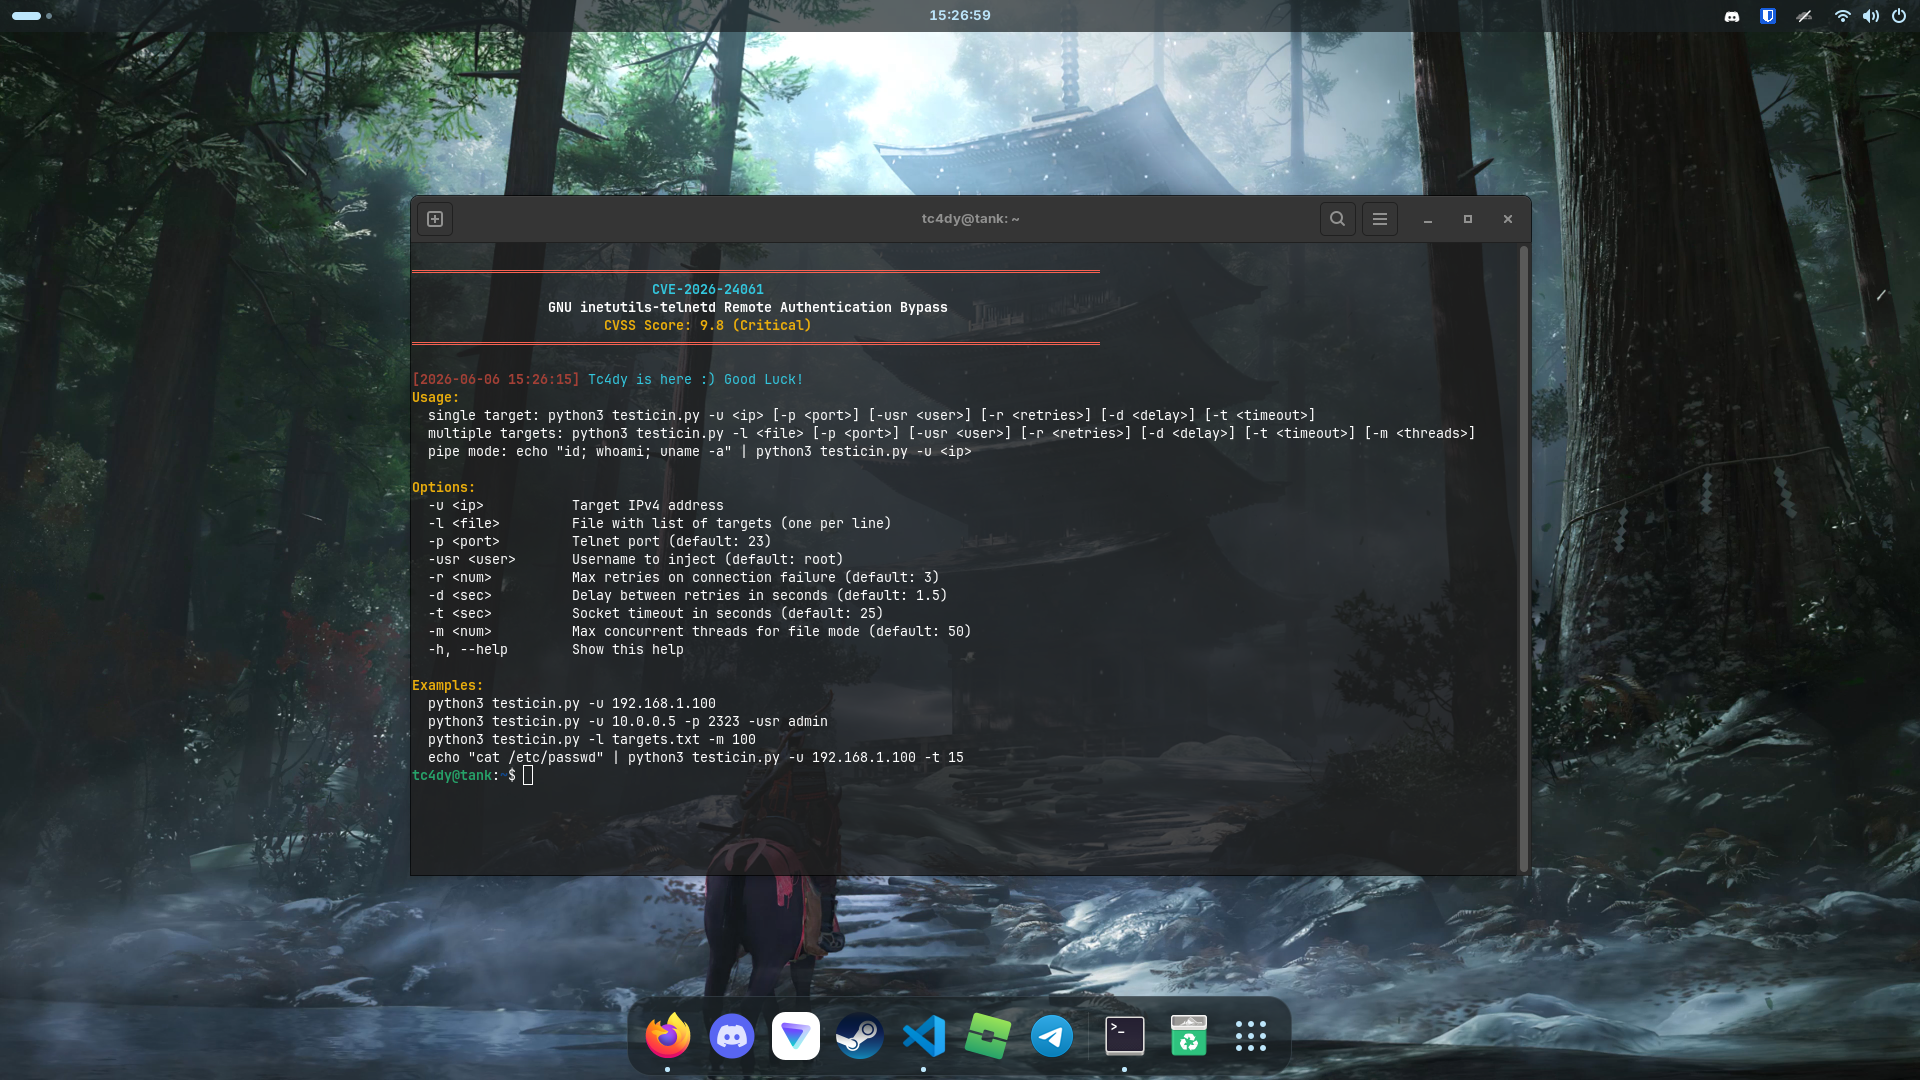
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.

PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…

Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…

CraftCMS has an RCE vulnerability via relational conditionals in the control panel

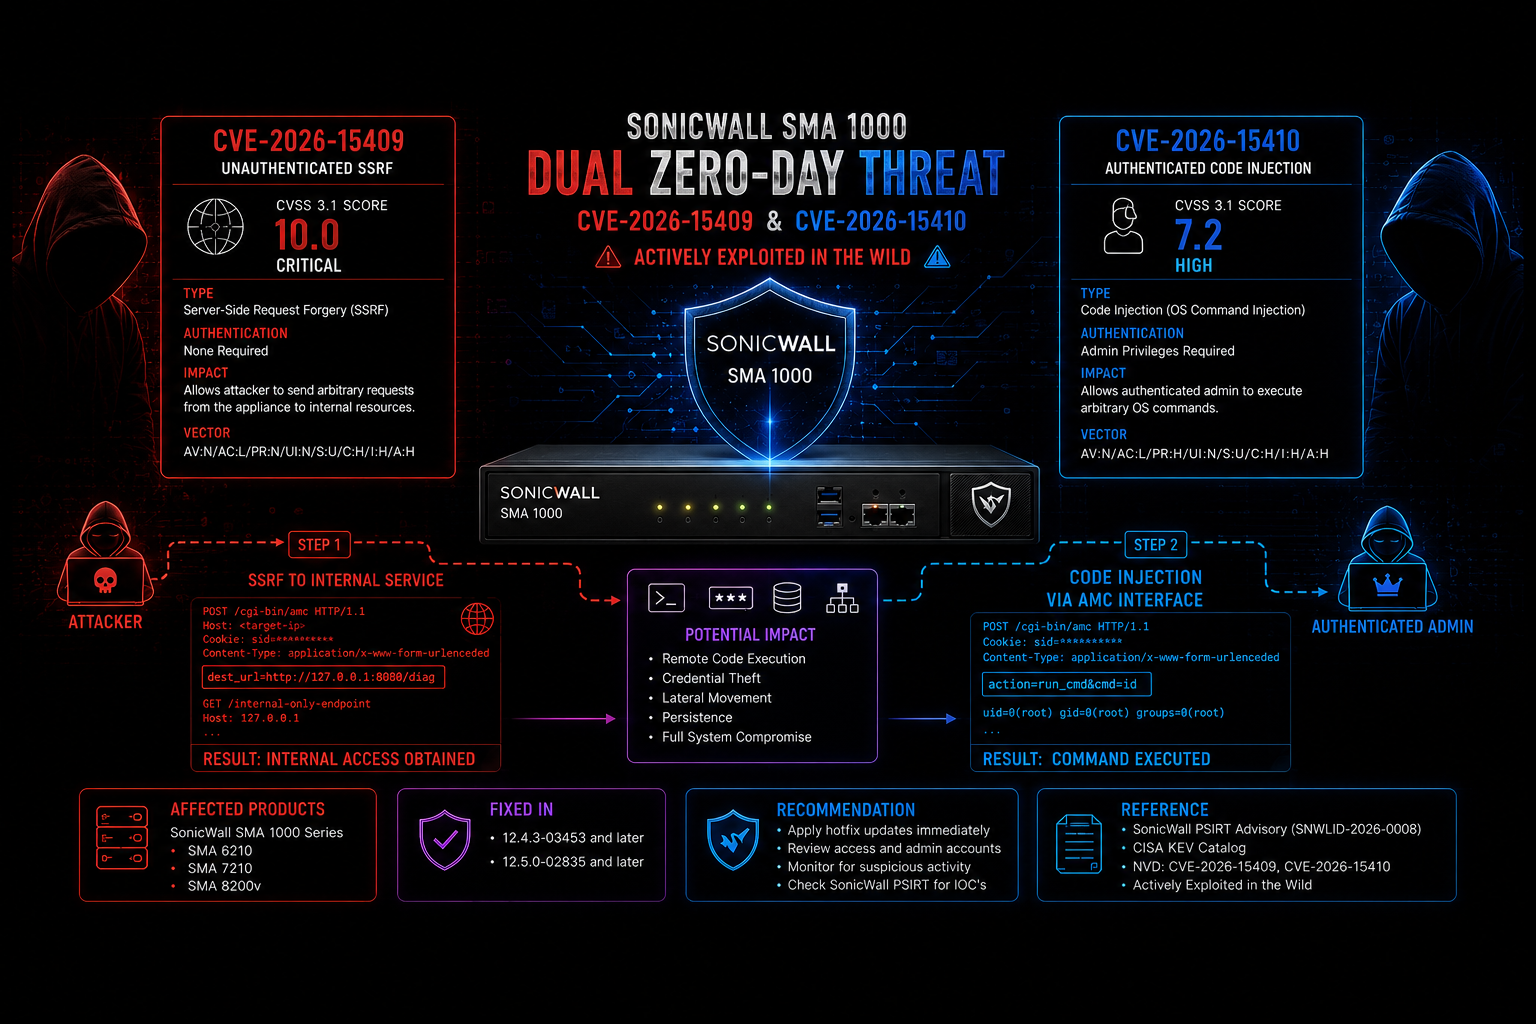
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

Malicious Register Directive Code Injection Exploit

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…

Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via…

Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…

The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.

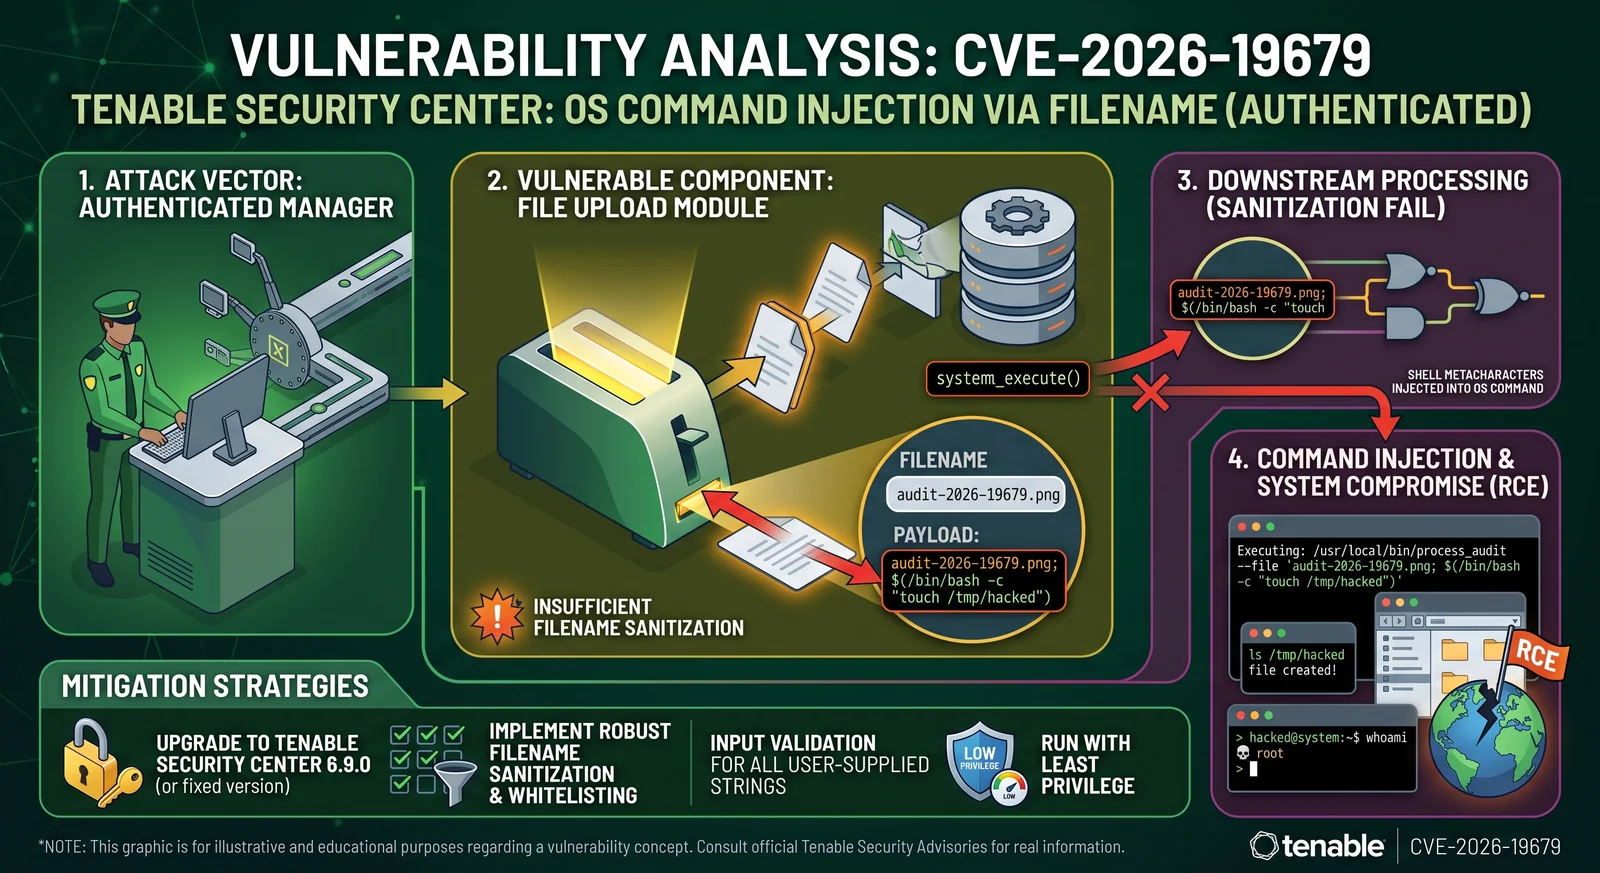
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…

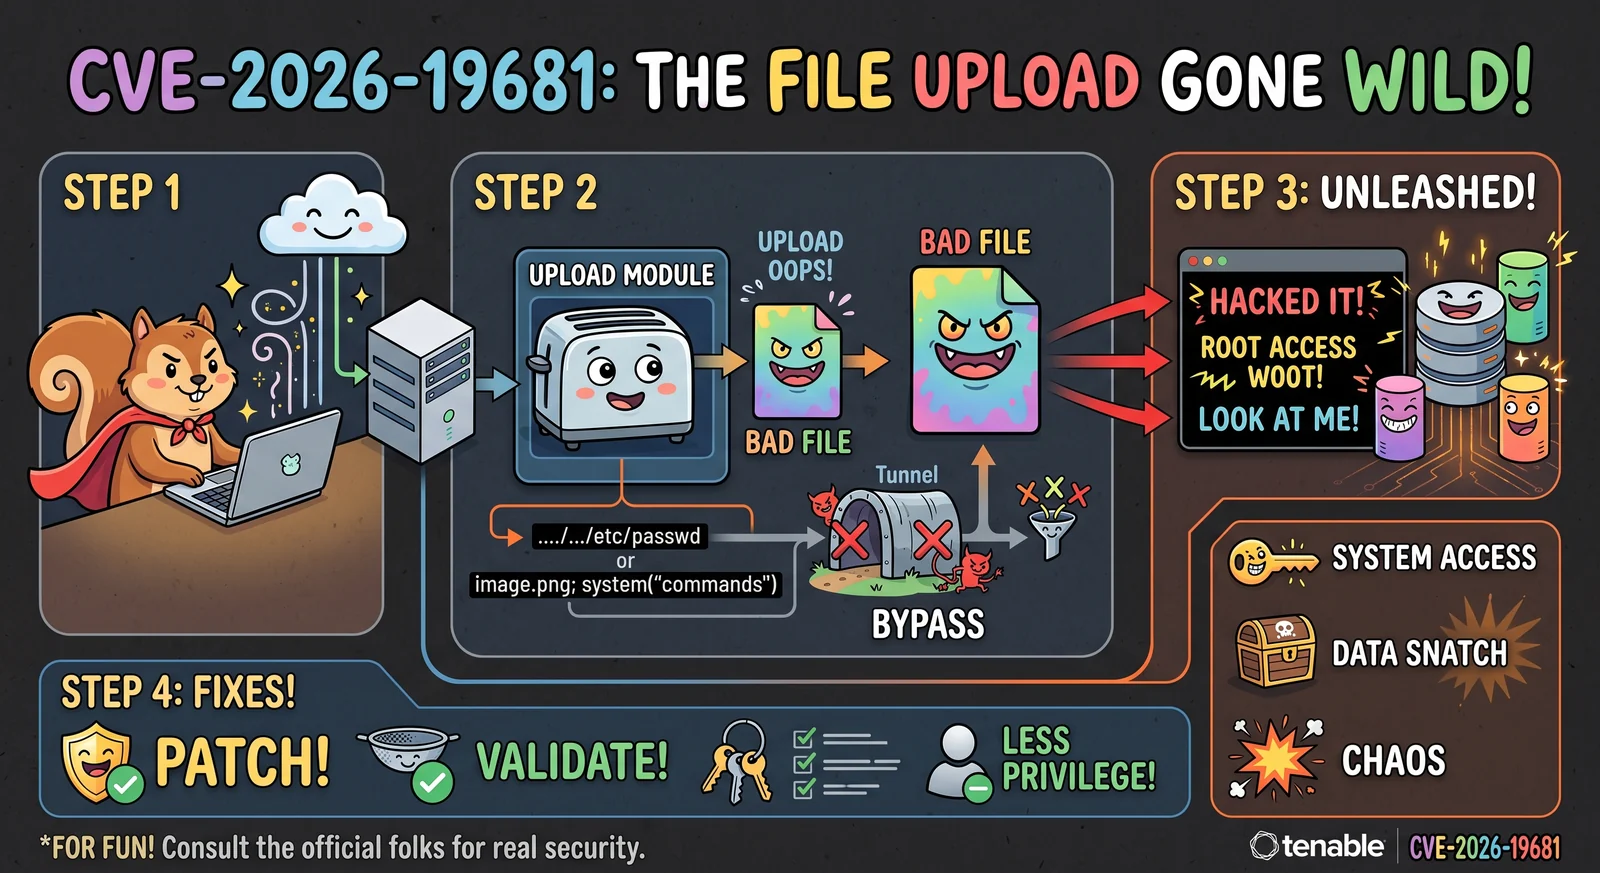
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…

POC for CVE-2026-23744 for a python revshell

CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.

IBM Langflow Unauthenticated RCE via Auto-Login Bypass

PoC exploit for CVE-2026-33017: unauthenticated remote code execution in Langflow via malicious Python Custom Component injection, with built-in…