CVE-2026-102607-ZoneMinder

Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…

Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…

CraftCMS has an RCE vulnerability via relational conditionals in the control panel

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…

Unauthenticated SQL injection to RCE exploit for ZoneMinder 1.29/1.30 (CVE-2016-10204, EDB-41239). Single-command SQLi to webshell to reverse shell…

Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…

Proof-of-concept for CVE-2026-5059, a command injection in aws-mcp-server via shell=True and incomplete validation, with vulnerable and patched code…

Proof-of-concept exploit for CVE-2024-29973, a remote command injection in Zyxel NAS devices, demonstrating arbitrary command execution via crafted…

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Python proof-of-concept for CVE-2022-25765, a command injection vulnerability in pdfkit, enabling remote code execution via crafted PDF generation.

CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.

Proof-of-concept exploit for CVE-2026-76060, an OS command injection in ZoneMinder's event export, demonstrating RCE via crafted monitor names.

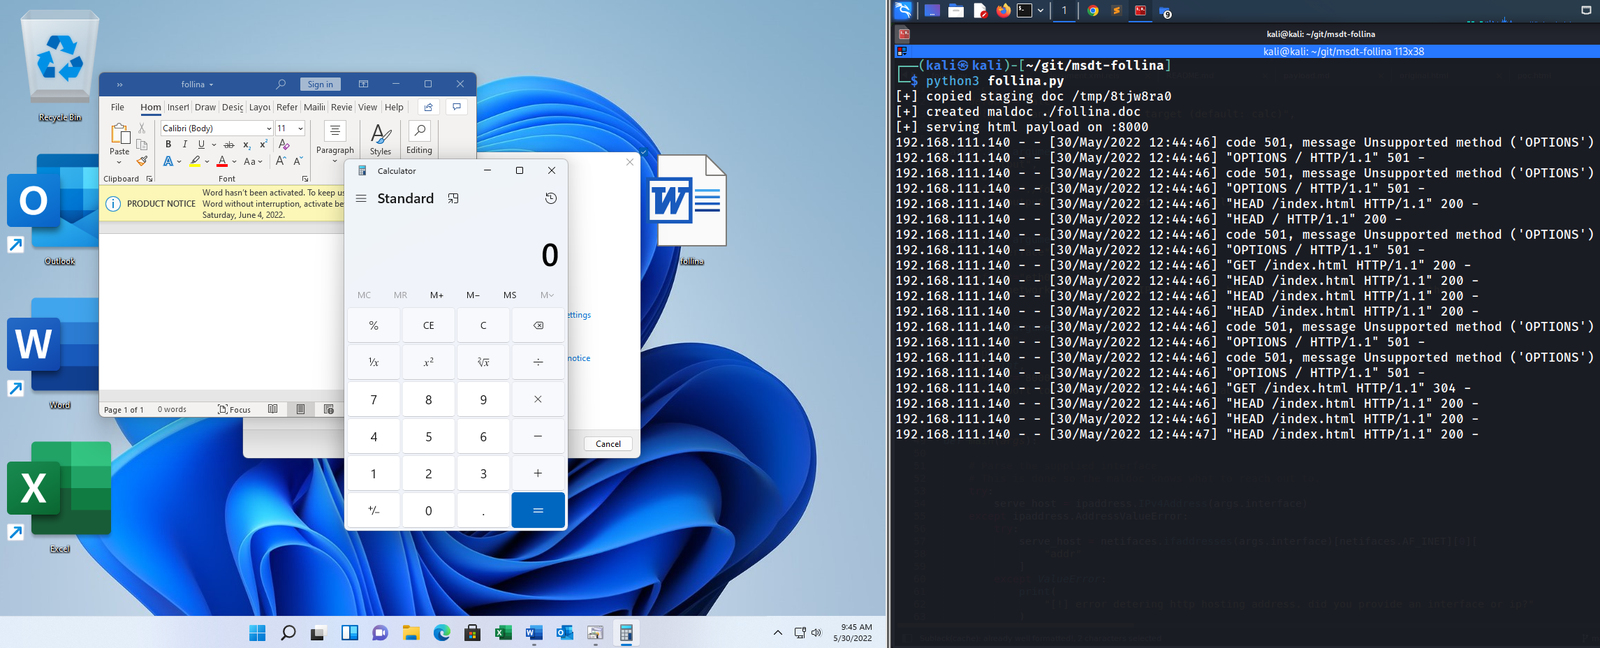
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

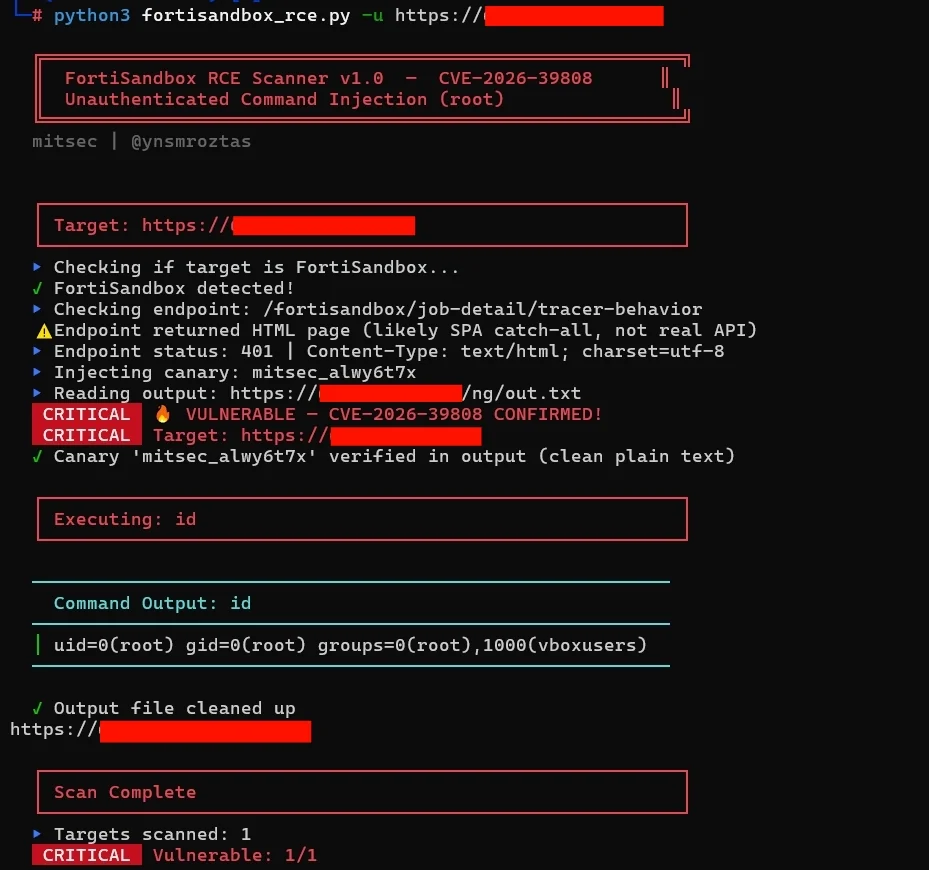
Unauthenticated RCE scanner for FortiSandbox CVE-2026-39808 with canary-based verification, command execution, and pipeline integration for mass…

Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.

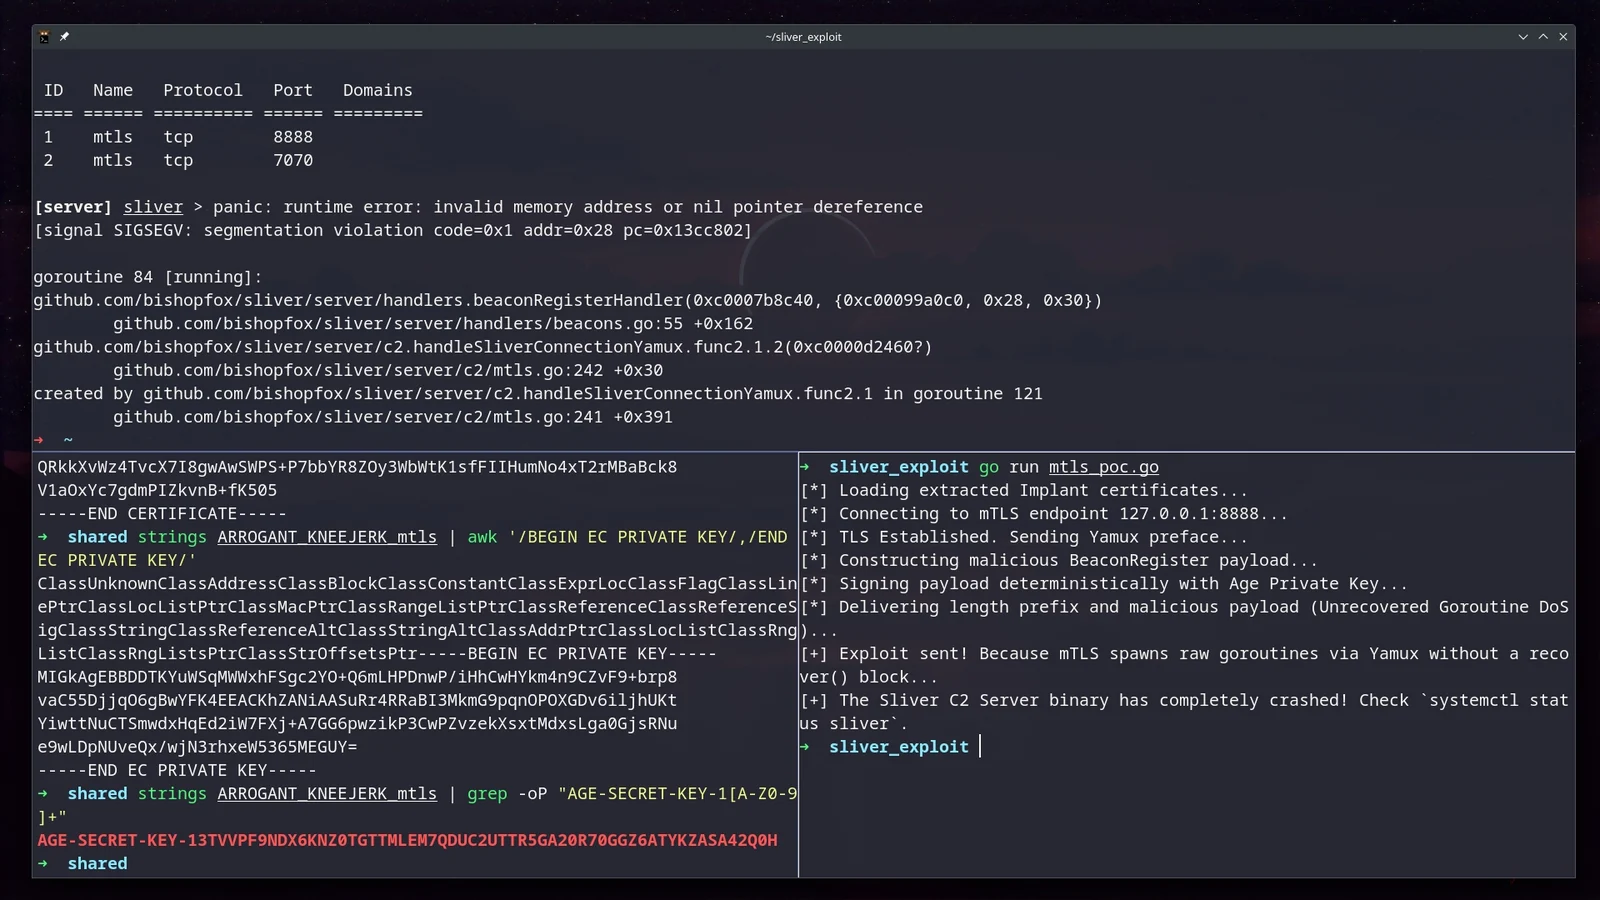
Proof-of-concept exploit for CVE-2026-29781, weaponizing captured Sliver implant credentials to trigger a nil-pointer panic and crash the C2 server…

Proof-of-concept for command injection vulnerability in FLIR AX8 camera, demonstrating remote code execution via /usr/www/res.php.

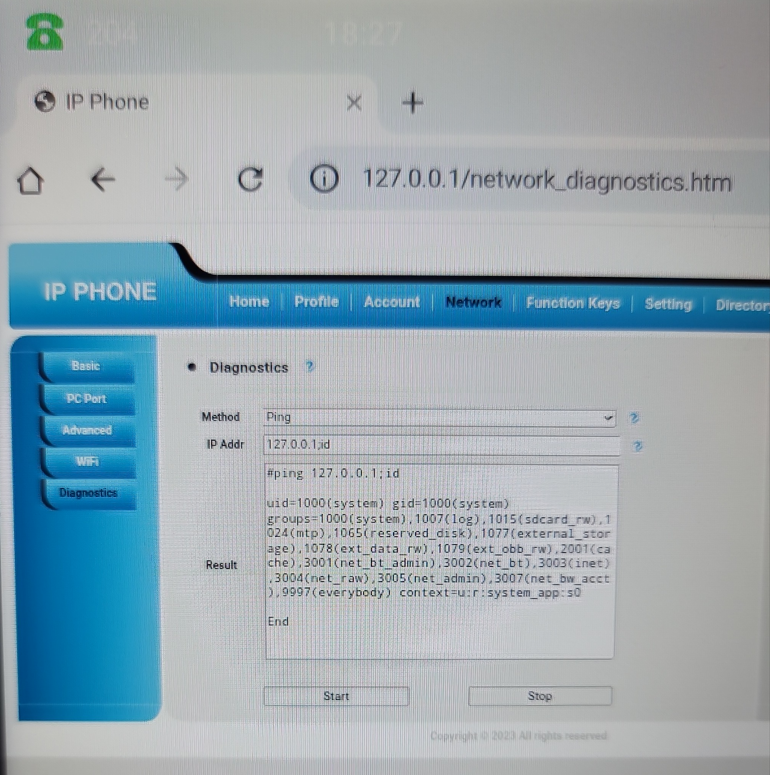
Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter.

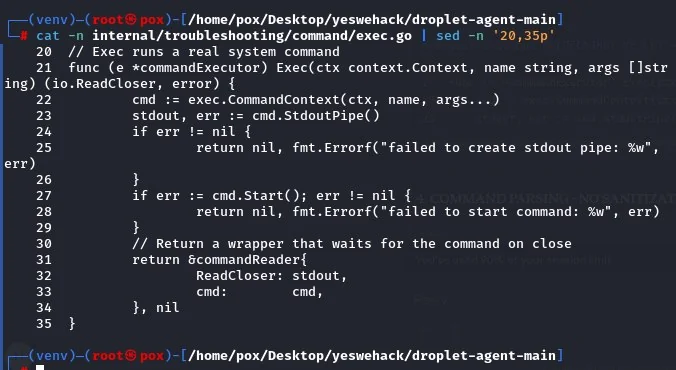
Critical Pre-Auth Root RCE (CVSS 10.0) in DigitalOcean Droplet Agent up to v1.3.2 via Command Injection.