
dig
 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
command-and-controldns-analysisinformation-gathering+3
33
xsser/digmacOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
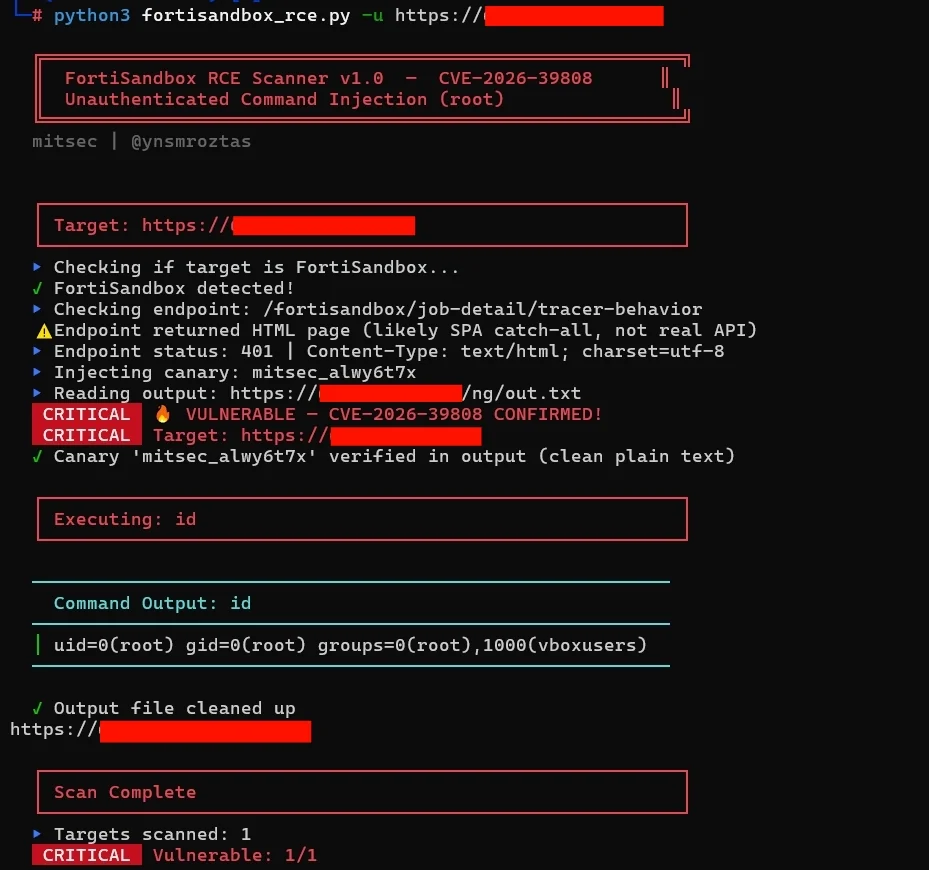 ynsmroztas/fortisandbox-rce-exploit-cve-2026-39808
Unauthenticated RCE scanner for FortiSandbox CVE-2026-39808 with canary-based verification, command execution, and pipeline integration for mass…
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
 rasta-mouse/ppenum
Simple BOF to read the protection level of a process
 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 mayyhem/maestro
Abusing Azure services over C2
 grampae/mqxss
Hooked browser communication over MQTT
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 lutfifakee-project/cve-2026-41940
cPanel/WHM CVE-2026-41940 - Mass Scanner & Exploiter
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
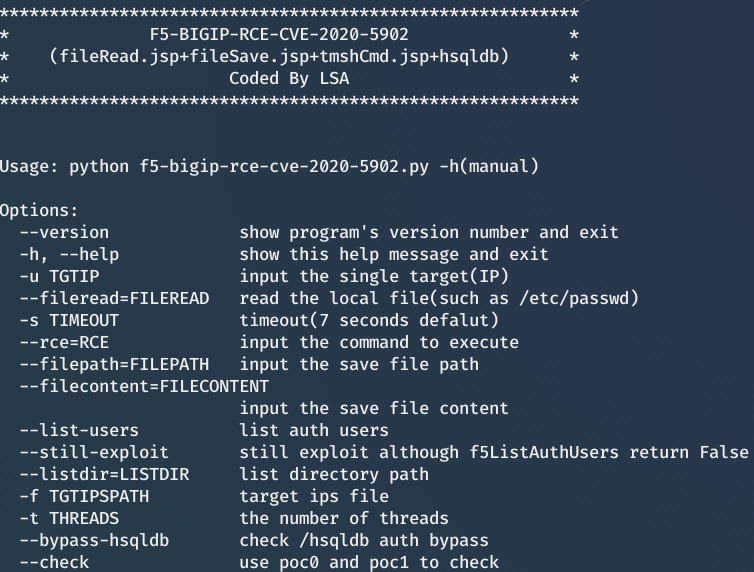 thelsa/f5-bigip-rce-cve-2020-5902
F5 BIG-IP RCE CVE-2020-5902 automatic check tool
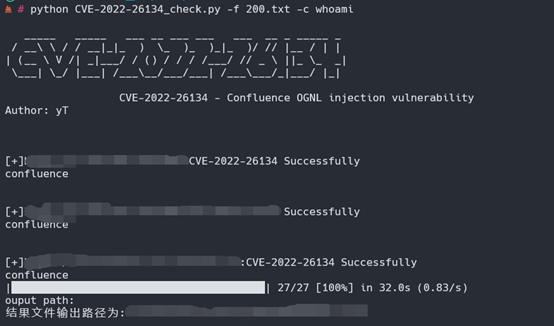 ytxzx/cve-2022-26134
Python-based exploit for CVE-2022-26134, an OGNL injection vulnerability in Confluence Server and Data Center. Supports single URL check and batch…