
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
89 results
CyberStrikeAI preview

CyberStrikeAI

GitHubed1s0nz/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
6.6k
1 day ago
PhoneSploit-Pro preview

PhoneSploit-Pro

GitHubazeemidrisi/phonesploit-pro

An all-in-one hacking tool to remotely take over Android devices.

android-securitycommand-and-controldata-exfiltration+7
6.3k8 days ago
CyberStrikeAI preview

CyberStrikeAI

GitHubaipentest/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+8
6.6k1 day ago
SliverMirage preview

SliverMirage

GitHubdaniomass/slivermirage

Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
binary-analysiscommand-and-controlexploitation+4
4226 days ago
DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis preview

DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis

GitHubkaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis

Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
command-and-controldata-exfiltrationdigital-forensics+4
439 days ago
Coldfire preview

Coldfire

GitHubredcode-labs/coldfire

Golang malware development library
command-and-controlcryptographyexploitation+5
9861 year ago
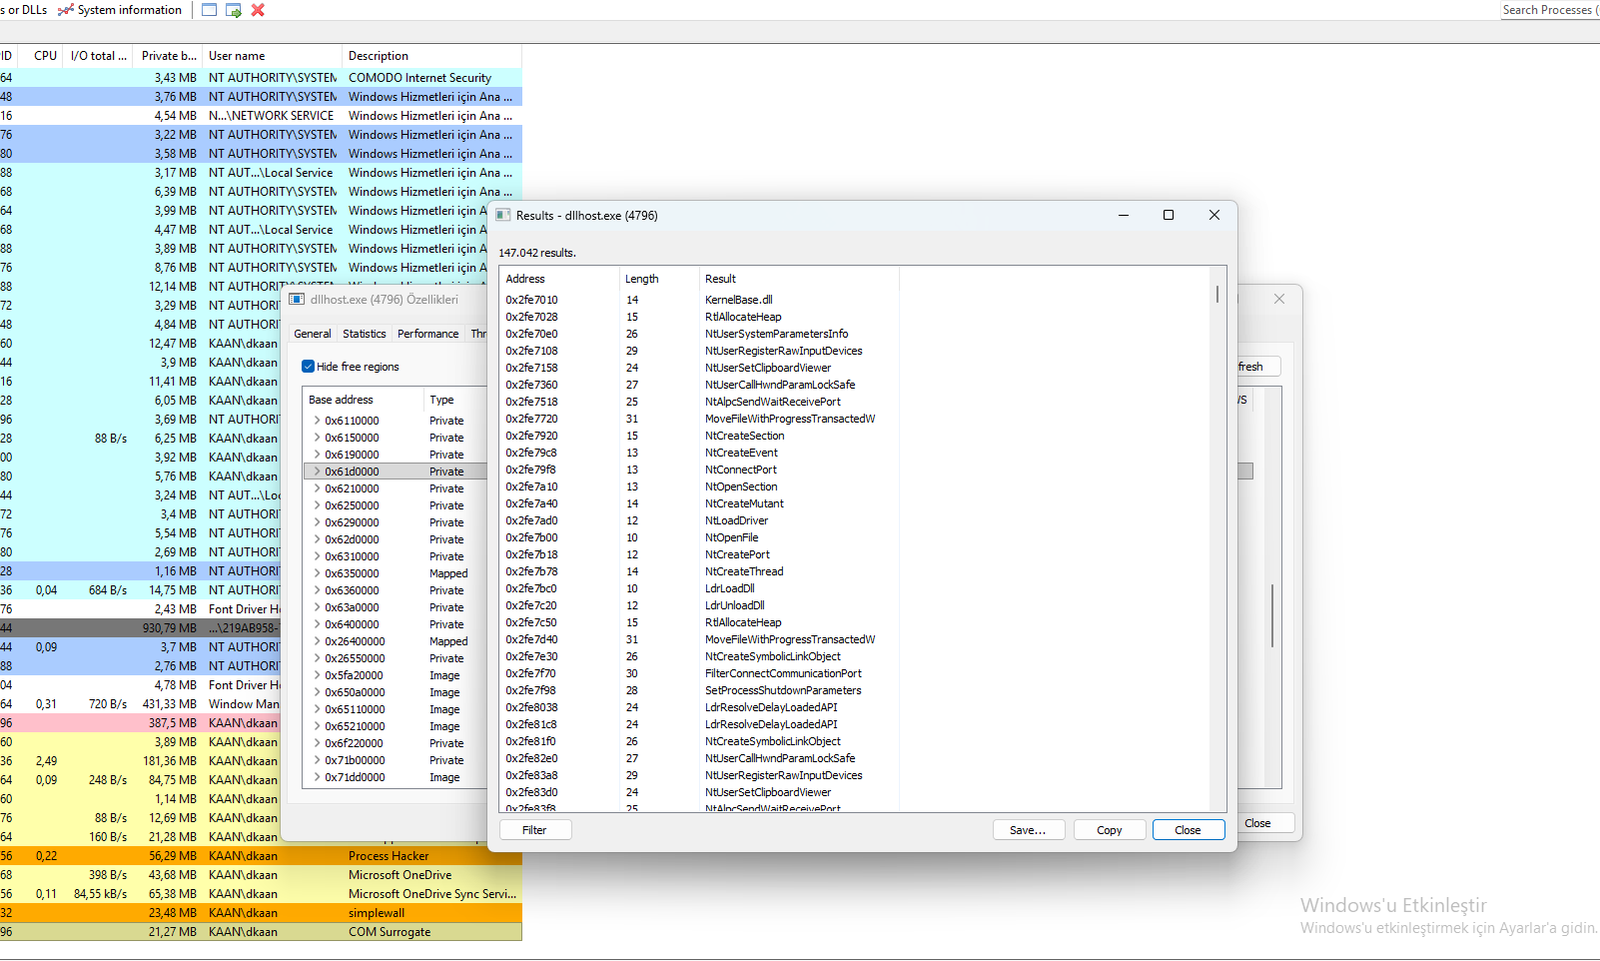
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
binary-analysiscommand-and-controldata-exfiltration+4
913 days ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

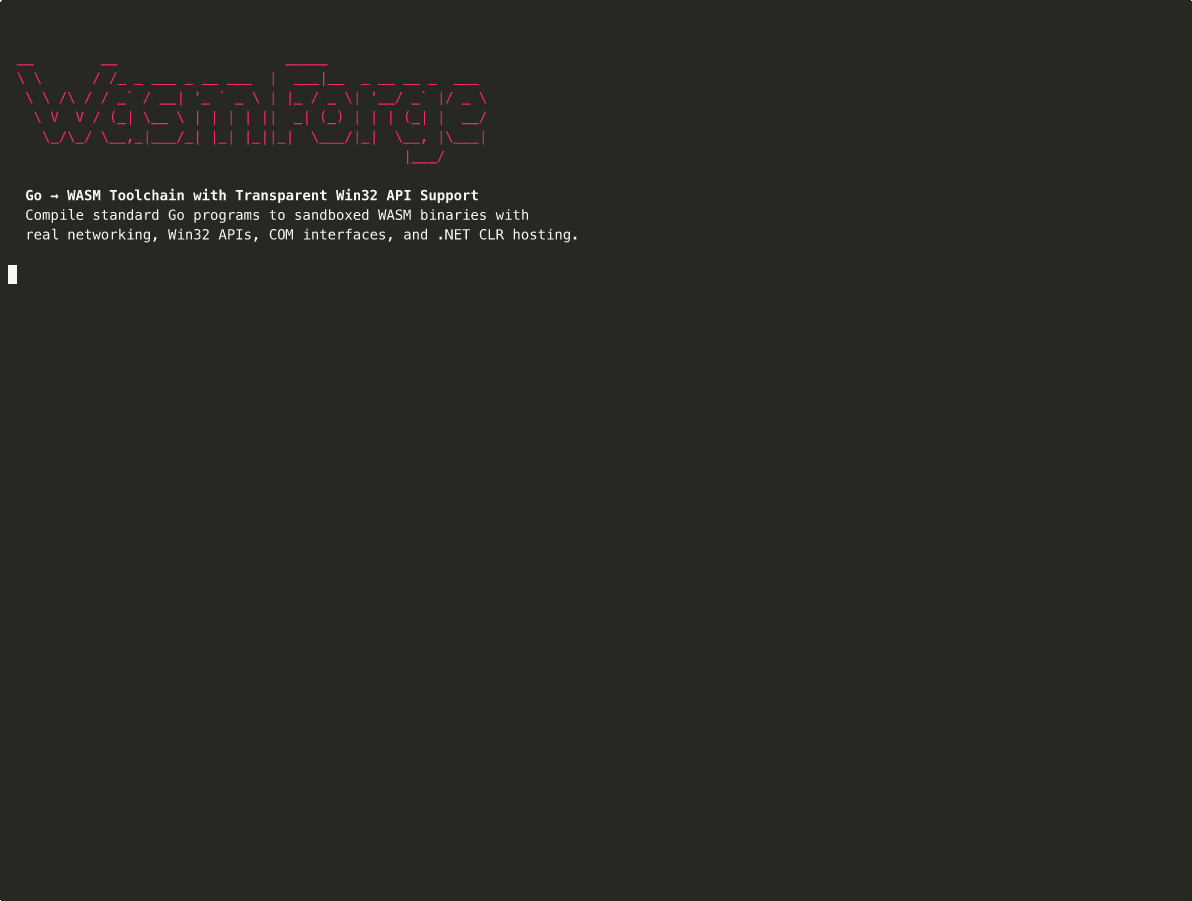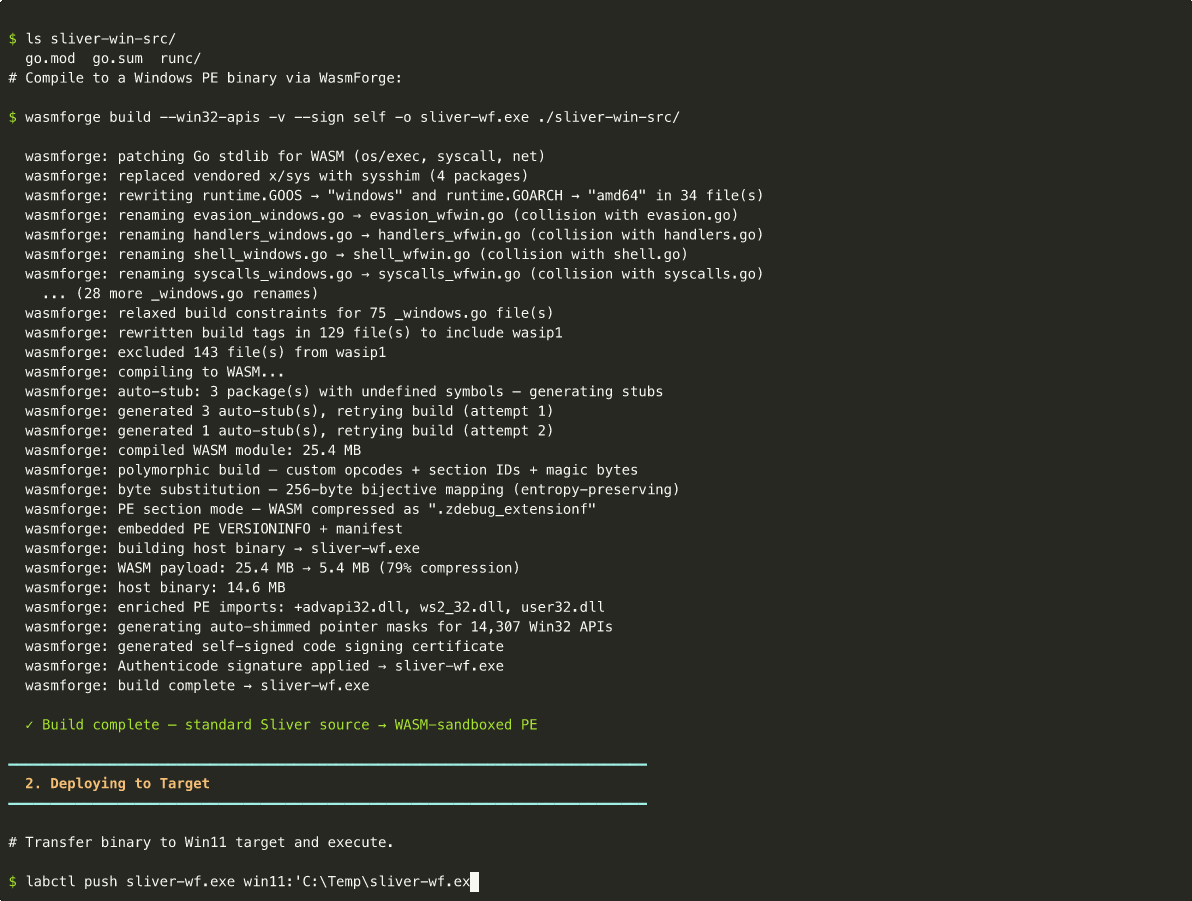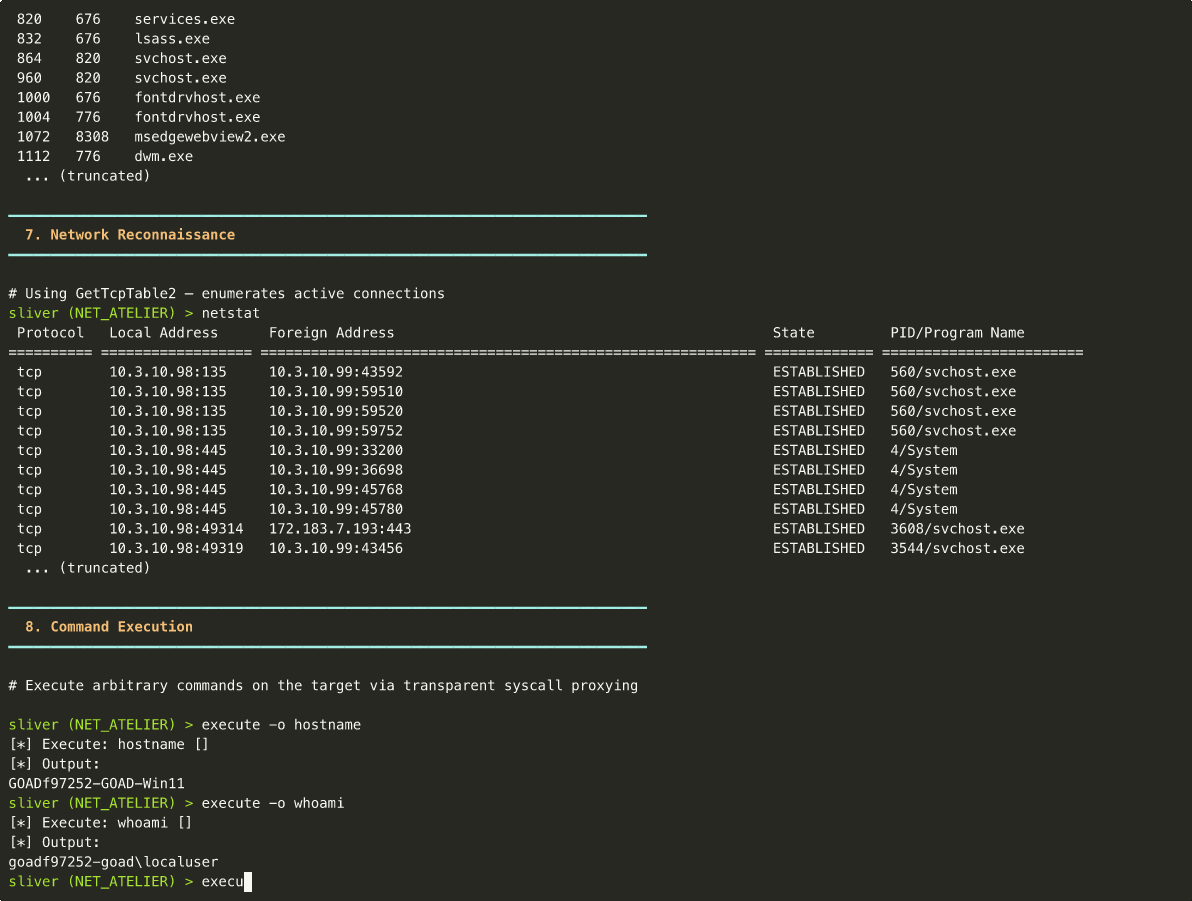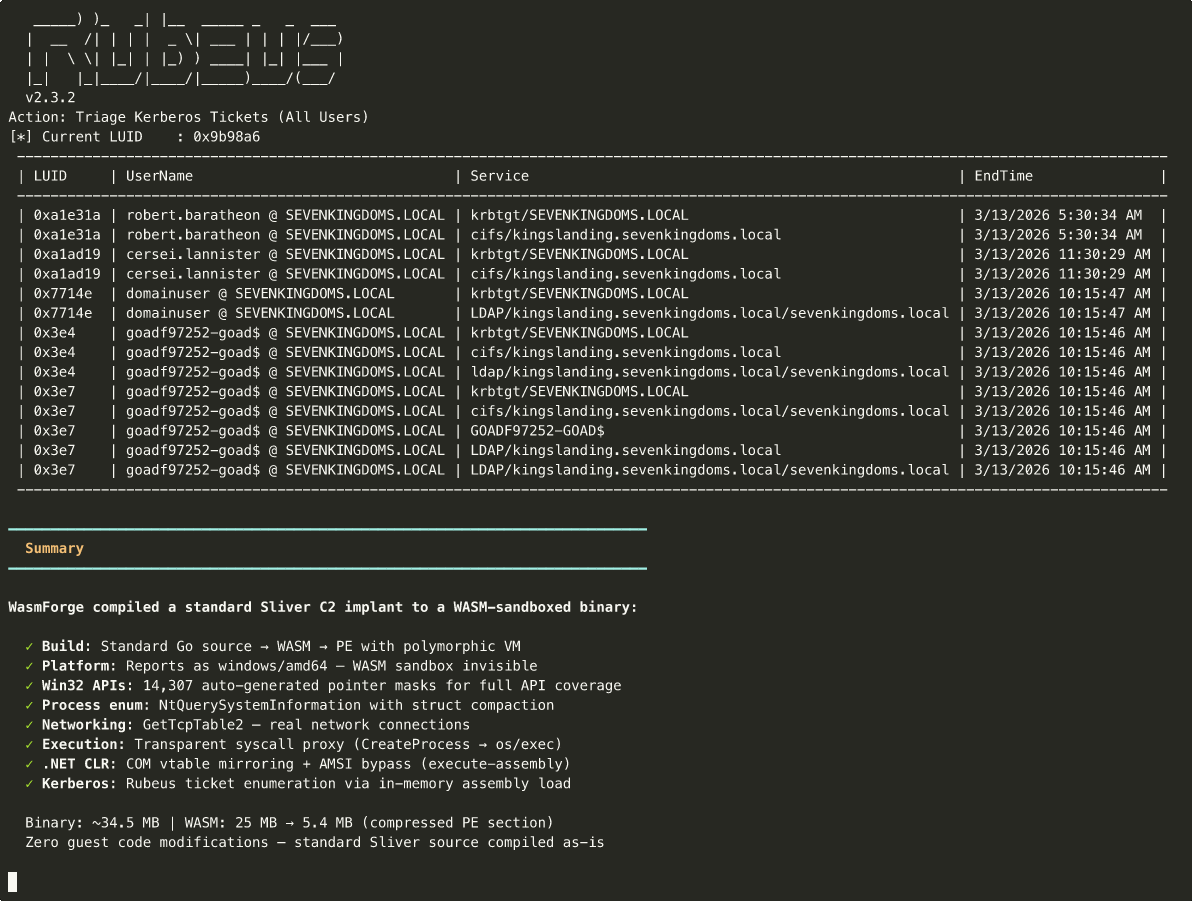
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
binary-analysiscommand-and-controlexploit-frameworks+9
1302 months ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
command-and-controlcryptographydigital-forensics+7
44 days ago
samsung-android-lpe preview

samsung-android-lpe

GitHubvikramaditya015/samsung-android-lpe

Poc for CVE-2026-20980, CVE-2026-20981, CVE-2026-20982
android-securitycommand-and-controlexploitation+5
523 months ago
AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis preview

AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis

GitHubkaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis

Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
binary-analysiscommand-and-controldata-exfiltration+2
322 days ago
frida-c2-mcp preview

frida-c2-mcp

GitHubs4dp4nd4/frida-c2-mcp

Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
android-securitycommand-and-controldynamic-analysis-sandboxing+8
646 months ago
moukthar preview

moukthar

GitHubtomiwa-ot/moukthar

Android remote administration tool

android-securitycommand-and-controldata-exfiltration+6
67910 months ago
Docx-Exploit-2021 preview

Docx-Exploit-2021

GitHublazarusreborn/docx-exploit-2021

This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444

command-and-controlexploitationmalware-analysis+3
54 years ago
XZ-Utils_CVE-2024-3094 preview

XZ-Utils_CVE-2024-3094

GitHubmrbuglf/xz-utils_cve-2024-3094

XZ-Utils工具库恶意后门植入漏洞(CVE-2024-3094)
command-and-controlexploitationincident-response+3
2 years ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

binary-analysiscommand-and-controldata-exfiltration+6
526 days ago
AndroRAT preview

AndroRAT

GitHubthe404hacking/androrat

AndroRAT | Remote Administrator Tool for Android OS Hacking

android-securitycommand-and-controlexploitation+4
1.7k8 years ago
androrat preview

androrat

GitHubwszf/androrat

androrat

android-securitycommand-and-controldata-exfiltration+6
2.0k6 years ago
Previous12345Next