metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

CraftCMS has an RCE vulnerability via relational conditionals in the control panel

CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit

This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers

Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

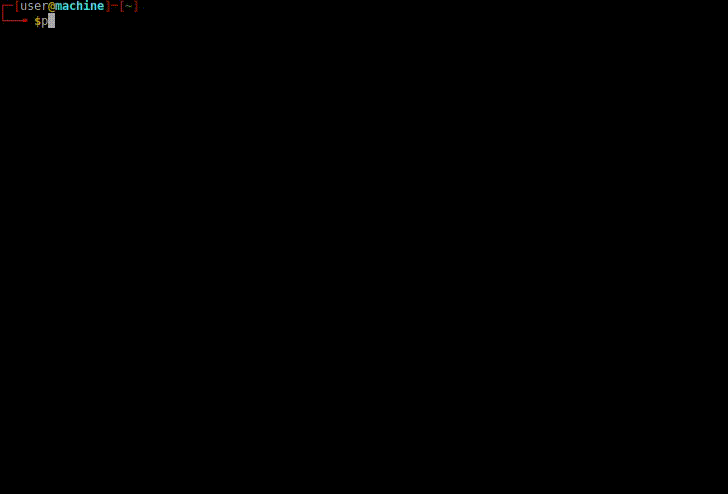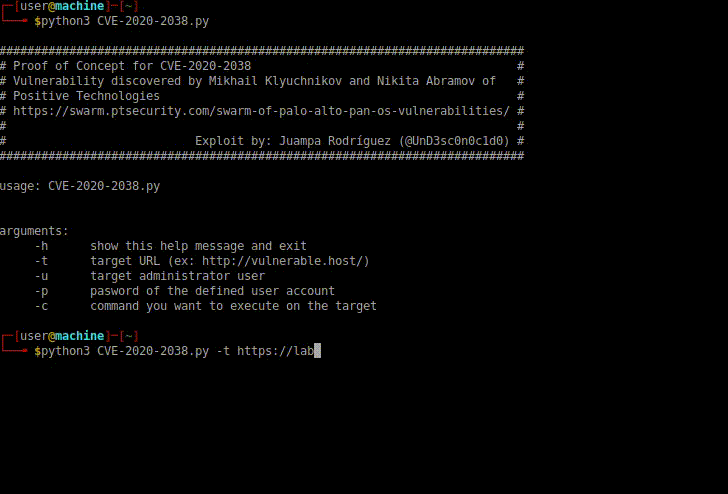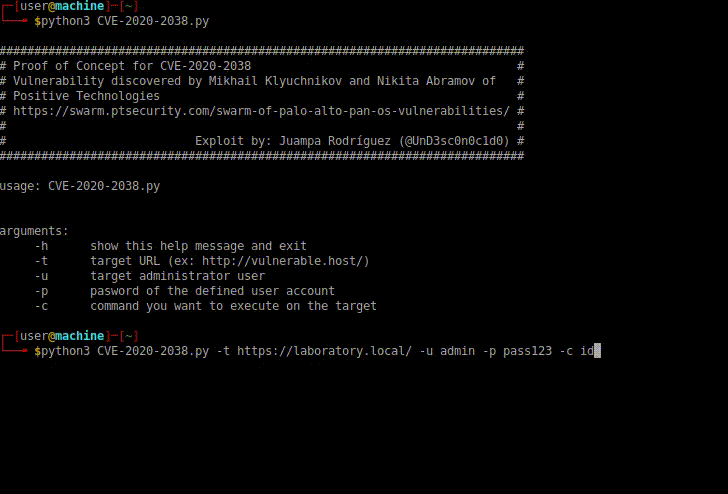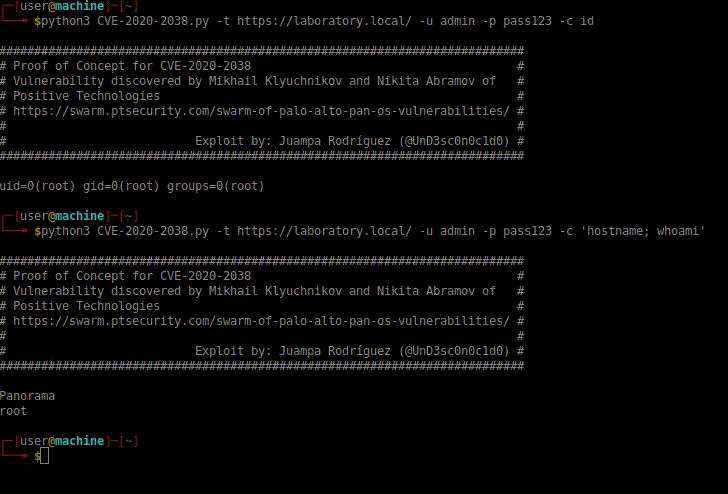
Exploit to capitalize on vulnerability CVE-2020-2038.

Security research tool for detecting and testing CVE-2025-63888 (ThinkPHP 5.0.24 File Inclusion RCE vulnerability)

Atlassian JIRA Template injection vulnerability RCE

☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…

React2Shell Exploitation Tool (CVE-2025-55182)

Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…

BIG-IP iControl REST vulnerability CVE-2022-1388 PoC

CVE-2022-39197 RCE POC

kibana < 6.6.0 未授权远程代码命令执行 (Need Timelion And Canvas),CVE-2019-7609

Proof-of-concept for CVE-2025-54100: XSS in PowerShell's Invoke-WebRequest via mshtml.HTMLDocumentClass, enabling remote code execution when curling…