
CVE-2007-4559-lab
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
binary-exploitationcode-analysisctf+6
jithinodattu/cve-2007-4559-labSelf-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 endusdksla/xwiki-cve-2025-24893
Unauthenticated remote code execution exploit for XWiki SolrSearch (CVE-2025-24893) via Groovy injection in the text parameter, with Docker-based lab…
 cyberharsh/drupalcve-2018-7602
Exploit for Drupal CVE-2018-7602 remote code execution vulnerability via double URL encoding bypass of sanitize() filter. Includes Docker-based lab…
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
 dhmosfunk/cve-2025-58098
Docker-based lab demonstrating CVE-2025-58098 argument injection vulnerability with source, vulnerable, and patched code comparisons for security…
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 tris0n/cve-2023-32571-poc
Proof-of-concept for CVE-2023-32571, demonstrating remote code execution via Dynamic Linq injection in ASP.NET applications. Includes payloads and a…
 security-phoenix-demo/mongobleed-exploit-cve-2025-14847
Exploit lab, docker and code scanner for mongobleed Vulnerability CVE-2025-14847 plus Phoenix Security Sync tools
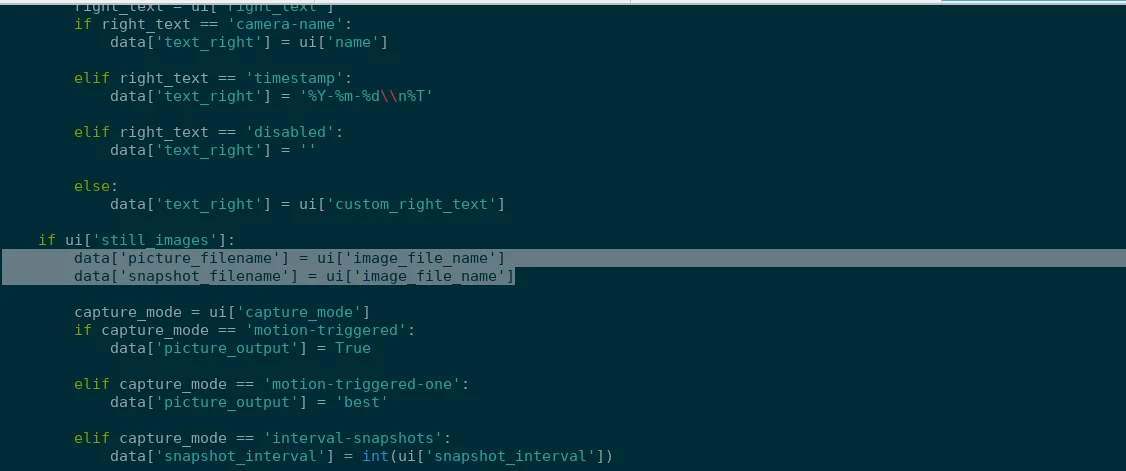 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 adamyordan/cve-2019-1003000-jenkins-rce-poc
Jenkins RCE Proof-of-Concept: SECURITY-1266 / CVE-2019-1003000 (Script Security), CVE-2019-1003001 (Pipeline: Groovy), CVE-2019-1003002 (Pipeline:…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 masahiro331/cve-2020-8277
Proof-of-concept exploit for CVE-2020-8277, a Node.js DNS resolver denial-of-service vulnerability triggered by large record responses, with…
 learner202649/cve-2026-40217-poc
The code for personally reproducing the corresponding vulnerability